AT&T Alien Labs finds new Golang malware (BotenaGo) targeting millions of routers and IoT devices with more than 30 exploits
Read: https://t.co/yQrZcDniMm
#infosec
A serious security #vulnerability has been discovered in Travis CI that exposed API keys, access tokens, and credentials, potentially putting organizations using public source code repositories to the risk of further attacks.
Read details: https://t.co/BZfQwZhtli
#infosec
FIN7 hackers are using Windows 11-themed Word documents to drop malicious payloads, including a JavaScript backdoor.
https://t.co/EGoXCdn5FI
The attack targeted a US-based point-of-sale (PoS) service provider as part of spear-phishing campaigns.
#infosec#cybersecurity
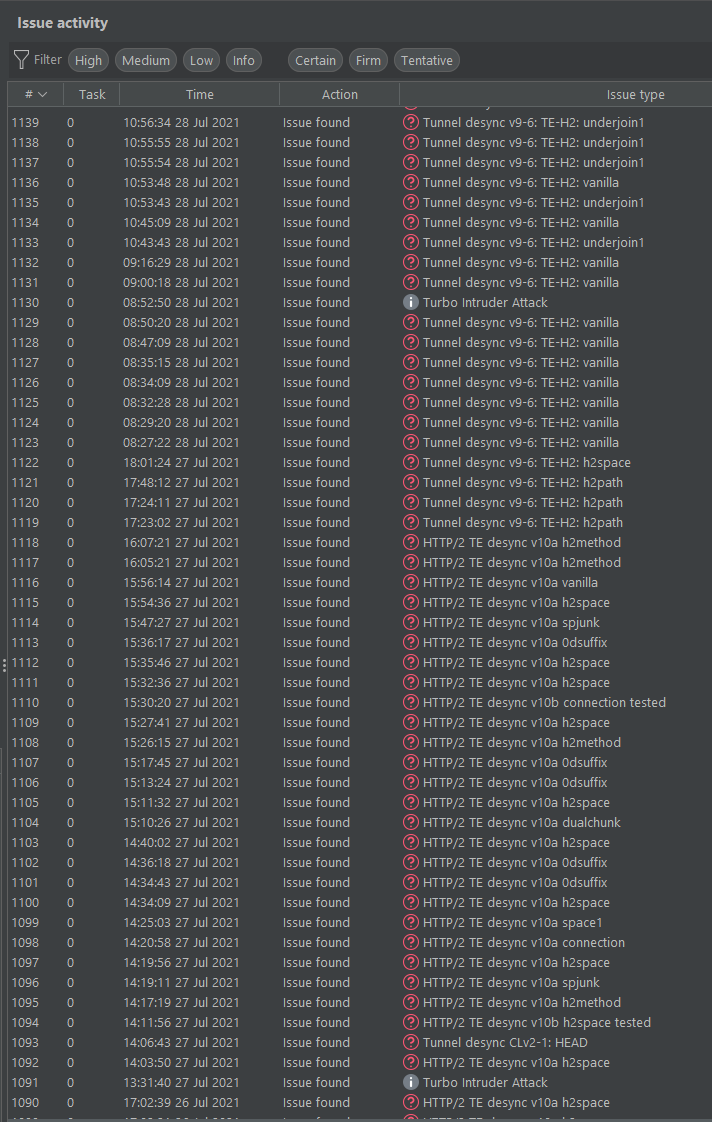
How to find a HTTP/2 playmate:
1. Install Burp 2020.8 and HTTP Request Smuggler
2. Configure scope & browse some bug-bounty sites
3. Go to proxy, hide out of scope traffic
4. Ctrl+A, right click->Extensions->pick your scan
5. Wait
https://t.co/kJWVEPcgYi
Researchers analyzed one of the largest password dumps, containing over 3.2 BILLION usernames and plain-text passwords, and discovered 1.5 MILLION records associated with emails linked to government domains around the world.
Read: https://t.co/pghLUy17L1
#infosec#cybersecurity
🔥 You may find this alarming...
A recently reported bug in #WhatsApp messenger could have enabled attackers to hack into your phone remotely and even compromise encrypted communications.
Find details and demos here https://t.co/NMbkutCwhI
#infosec#cybersecurity#hacking
WARNING: A new malware dropper distributes AlienBot Banker and MRAT #malware via #Android apps on #Google Play store, designed to let attackers gain intrusive access to victims' financial accounts as well as full control of their devices.
Read: https://t.co/PAkEt8J6f7
#infosec
UNC2546 hackers exploited Accellion FTA's 0-day vulnerabilities to steal its targets' data in the recent extortion attacks.
Read details: https://t.co/Cy2dn3Vj8v
#infosec#databreach#hacking