This month, Microsoft’s @msftsecresponse fixed 80 CVEs discovered and reported by me and the outstanding collaborators on our team, including wgg, npc0vo, and 2st. MSRC’s response and remediation were remarkably swift.
#bugbounty#cybersecurity#MSRC#security
Diffract (developed by @HototogisuTian@2st___) is an AI vulnerability research agent that goes beyond LLMs—we focus more on the nature of bugs than on AI engineering.
Q2 results:
• 37 Microsoft acknowledged CVE
• #1 on the MSRC Windows leaderboard
• #4 overall on MSRC
• Linux kernel bugs too.
We're continuing to work hard to push this further :)
https://t.co/EUjwqmGgea
#MSRC #Windows #Vulnerability
Congratulations to all the researchers recognized in the MSRC 2026 Q2 Security Researcher Leaderboard!
This quarter marks the final quarterly points-based leaderboard as we continue the evolution of our researcher recognition program. We are grateful to every researcher who partnered with us and helped strengthen the security of Microsoft products and services through their hard work and dedication.
We’d also like to recognize the top 10 researchers in this quarter’s leaderboard for their outstanding contributions. Thank you for helping protect customers around the world.
🥇Asaf Cohen (https://t.co/8WLhdz05Oq)
🥈C46F3708A45EF0041BD0A49DDAEA0E25
🥉Ron
4. Thanatos Tian (HKPolyU) & wgg & 2st with Diffract
5. haowei yan
6. fce141fd6b42fcec05c1285b15d8f999
7. Ofek Levin
8. pwn2addr
9. Kim Seung Chan (@mylostchristmas)
10. Jianyang Song
Learn more and view the full leaderboard: https://t.co/jNfv6aGNhT
Finally bought my second Claude Max 20x plan. I’m a top AI security research payer—wonder if I really have to submit another form just to get the cyber use restrictions released on a second account?
Do you use a virtual machine to browse dangerous links safely? If you use the Chrome browser inside that virtual machine, is it secure enough?
As you might have guessed, the answer is not so much.
We chained six unique CVEs from 2023 listed below.
• Chrome Renderer RCE : CVE-2023-3079
• Chrome Sandbox Escape : CVE-2023-21674
• LPE in guest OS : CVE-2023-29360
• VMware Info Leak : CVE-2023-34044
• VMware Escape : CVE-2023-20869
• LPE in host OS : CVE-2023-36802
Recently it occurred to me the fact that when I lose my status as a student, I will no longer be a "maybe-good" CTF player or a security researcher. I will still need to fill my knowledge with 7x10 hours of study and enthusiasm like I did during my sophomore year.
At first I was used to read LLVM source code a lot to find what methods, class...that I should use . Now with openai and copilot, I can focus on the algorithm design, instead of "wasting" time to read the source. AI is indeed a good helper to quickly learn prior knowledge.
Uploaded all my Offensive Security & Reverse Engineering (OSRE) course labs (docx) to my repo found below. Most of them have very detailed instructions and should be great to get you started in Software Exploitation. 1/n
#Offsec#SoftwareExploitation#RE
https://t.co/D5oBtDNOnS
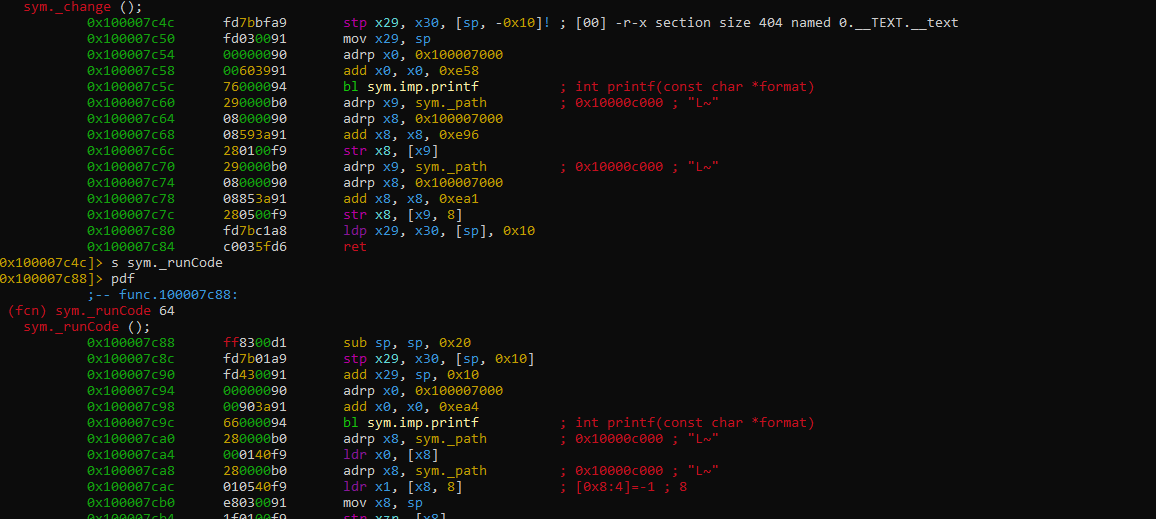
How to Reverse and Exploit iOS for BEGINNERS😈
👇My 3 part series👇
Part 1: How to Reverse & Patch iOS Apps
https://t.co/moBalBBWrI
Part 2: Exploiting iOS binaries: ARM64 ROP Chains
https://t.co/rHYYRidI8g
Part 3: Heap Overflows on ARM64: Spraying, UAF
https://t.co/5X6ls5OPC2