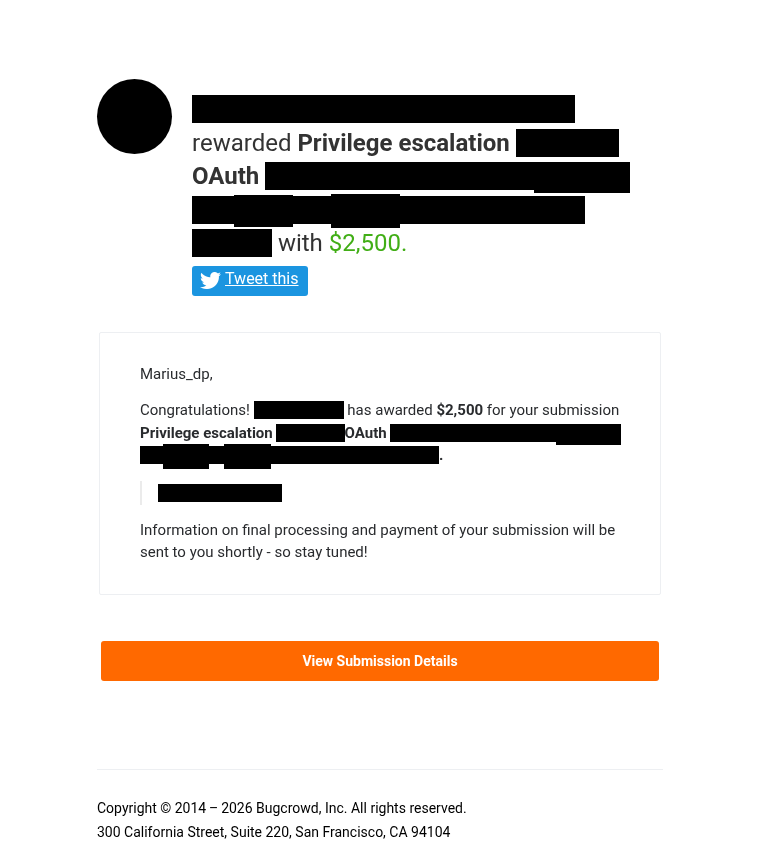
free account to billing admin, all from a public oauth client id
the back office client needed no secret. logged in through it with my own free creds and the token came back with back office scopes. could rewrite their prod pricing and it stuck. check which client ids skip the secret
JS function param whitespace seperator
Bypass XSS WAF protection using invisible separators before or after function name or between a JS function name and parameters
<img/src/
onerror=alert&#xFEFF;(1337)>
#XSS
First report on YesWeHack — officially Accepted! 🔥🟢
CVSS 9.3 (Critical) | +1 credit.
A great start on a new platform. The hunt continues!
#BugBounty#YesWeHack#CyberSecurity#InfoSec
To everyone who helped me, thank you. To everyone who ignored me, thank you too. You all played a part in pushing me further than I thought possible.
I haven't forgotten. And I'm just getting started.
#BugBounty#HackerOne#YesWeHack#Bugcrowd
Interesting development! 👀
The report was initially closed as Informative due to the HackerOne Signal Score requirement. However, it has now been triaged, and the team confirmed they are preparing a fix.
Keep hunting! 🔥 @Hacker0x01#BugBounty#HackerOne
If you have a JSON login page, test blind-SQL injection directly in the username and/or password fields like below.
Payload injected in username input field: 👇
username' ; waitfor delay '0:0:8' --
Happy hunting. ❤️
#bugbountytips#bugbountytip#bugbounty 🔥
If you have a JSON login page, test blind-SQL injection directly in the username and/or password fields like below.
Payload injected in username input field: 👇
username' ; waitfor delay '0:0:8' --
Happy hunting. ❤️
Credit: @__nav1n_#bugbountytips#bugbountytip#bugbounty 🔥