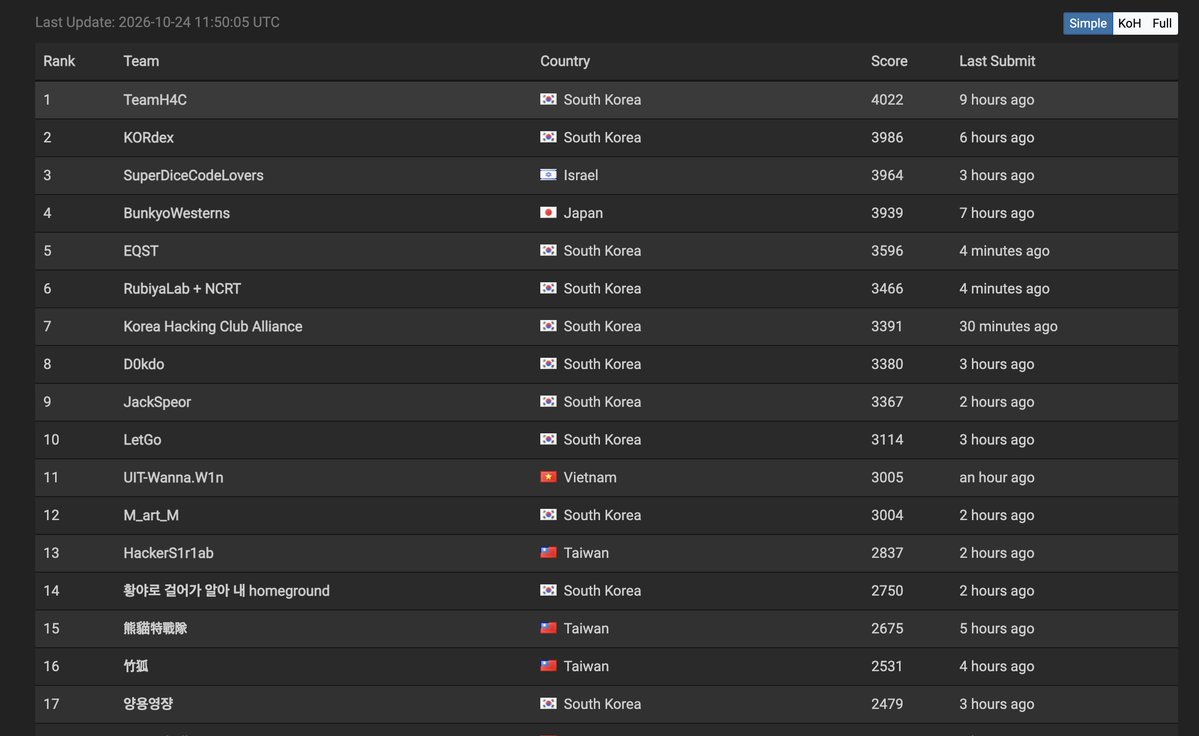
CTF has finally become a contest between Korean meat proxies just to see which team has the bigger wallet and can burn more tokens with their pay2win strats
🔴 Araştırmacı @4osp3l, Microsoft Azure Application Gateway v2 üzerinde ilginç bir 403 Forbidden bypass yöntemi buldu.
403 Forbidden veren bir URL, URL'nin sonuna "?x=.js" ekleyince (veya query string içinde .js geçen herhangi bir şey) kısıtlama bypass oluyor ve sayfaya erişilebiliyor.
@bruhbruh99u Honestly, I don’t really mind either way. What I enjoy most is the process of finding vulnerabilities. Whether it’s just a “thank you” or $5,000 doesn’t really make much of a difference to me XD
🥳 Found an RCE in Wallpaper Engine v2.8.42
Successfully achieved arbitrary code execution through workshop item.
Reported to the dev team. Writeup & PoC will be published once the patch is fully rolled out.
#CyberSecurity#WallpaperEngine#Oday#RCE
@Dre4M_LT Honestly, I don’t even know where to begin explaining this to you, and I can’t really disclose the details yet.
I assume you’re thinking of an exploit involving application wallpapers, but that’s actually not the case here.
@1GetNoHoes It’s something different. The wallpaper type itself isn’t really relevant to this vulnerability. It’s not limited to application wallpapers.
🥳 Found an RCE in Wallpaper Engine v2.8.42
Successfully achieved arbitrary code execution through workshop item.
Reported to the dev team. Writeup & PoC will be published once the patch is fully rolled out.
#CyberSecurity#WallpaperEngine#Oday#RCE



")()
#bugbountytips #bugbountytip https://t.co/lBiidTYfZ9](https://pbs.twimg.com/media/HTjJ7n2WwAAq0oj.jpg)





