The Vibration Architect. Don’t take advice from me. I'm not a licensed anything. Everything I say here is purely my personal opinion. Do your own due diligence.
ATTN:
For those entering the boards
You are about to enter an area of free speech, the likes of which you are probably unaccustomed to. With the exception of illegality, anything goes. There is no safe space. Feelings will be hurt. Get used to it. We won’t coddle you.
++ Canada, It's a Trap! ++
Ursula #vonderLeyen wants to lure Canada into an associate EU membership.
Will Mark Carney do right and tell von der Leyen to bugger off? If he won't, then the Canadian people will have to fix it, and maybe a new freedom convoy would then be in order.
BREAKING: 🇯🇵 Over ¥25.85 TRILLION ($165B) wiped out from Japanese stocks as the NIKKEI crashes -2.2% after inflation came in above the BOJ's 2% target.
The sequence was never random.
Some were watching the numbers.
Others were watching the signals.
But the ones who understood the architecture stopped asking when.
The final phase won’t come with an announcement.
It will simply become obvious why everything happened in this order.
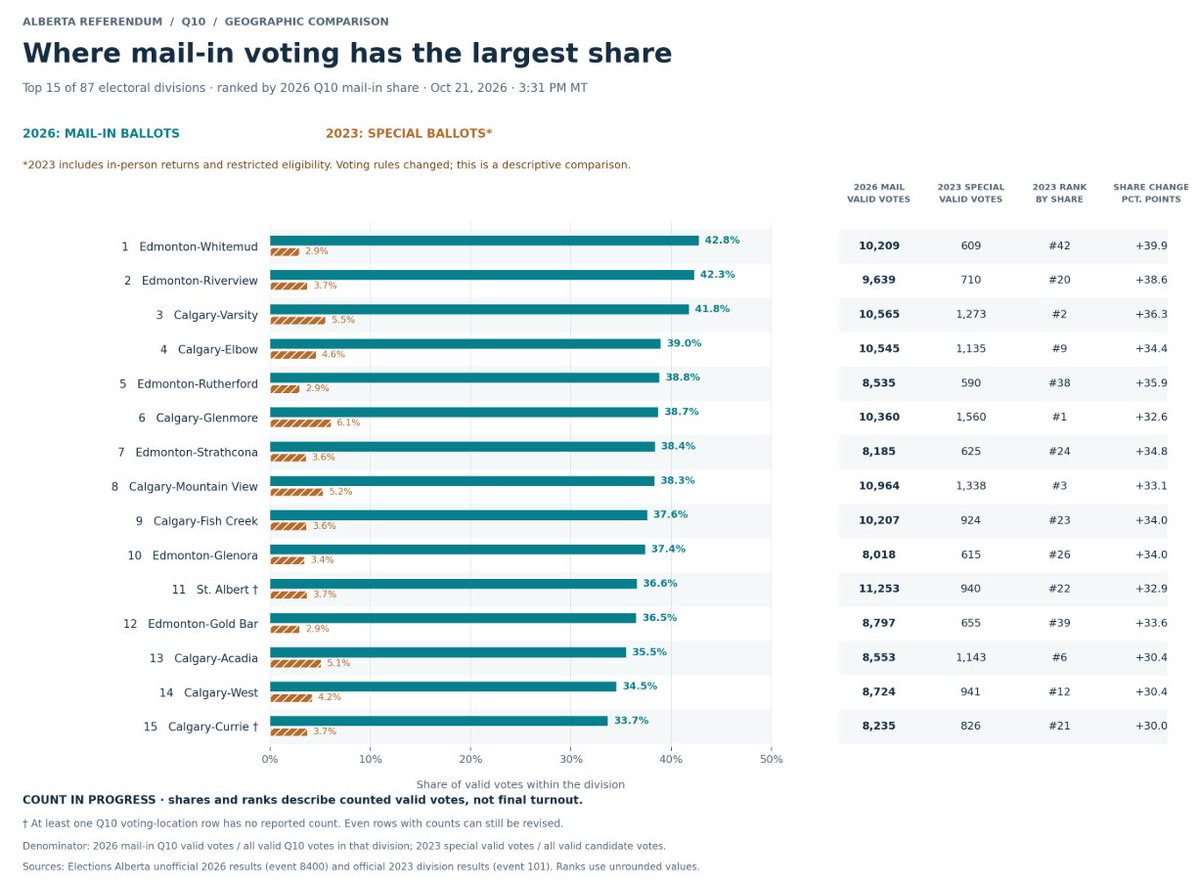
Probably nothing but I parsed out the top 15 electoral divisions that used mail-in-voting based on percentage and compared those same electoral divisions to their 2023 mail-ins and I have to say this is very concerning.
Why are these divisions mailing in 15x more ballots than they did in 2023? You would think with Covid no longer being a concern they would be more likely to vote any other way.
Edmonton-Whitemud was #42 out of #87 electoral divisions for mail in voting in 2023 but this year I guess almost half of the residents there felt they had to mail in their vote and now they are #1 for mail-in-voting.
Omar is going down and it’s going to happen soon. But there’s more to it that most aren’t seeing.
Once it’s proven she falsified documents and lied repeatedly about who she is and where she is from, then that will become a precedent. Once a precedent is set and then shown to the people, when it happens again it becomes instantly less shocking and more acceptable.
Now who else do we know that has lied about his heritage? Lied about who he is? Omar is the precursor to Renegade and I suspect many others that we haven’t even thought of.
Keep Watching. It’s about to get very good.
🚨The RCMP raid on Lion Electric is just the tip of the iceberg—the real machine behind it is far more sinister.
The Canada Infrastructure Bank is a banking cartel creation, wired straight into the WEF's "blended finance" scheme—and It's quietly siphoning BILLIONS from Canadian taxpayers.
And almost no one has a clue.
Holy shit.
FOURTEEN press outlets and the NY Slimes filed with the court seeking to get access to the search warrants in this case.
HEY NY SLIMES AND THE OTHER 14 NEWS OUTLETS!
If you were seeking to GENERATE SOME NEWS about the Ilhan Omar case, CONGRATULATIONS!
You just succeeded in DOING THAT.
The DOJ/US Attorney's Office in DC just **established on the record in it's filing about your seeking access to the search warrant info that OMAR HAS BEEN LIVING ALL THIS TIME IN THE US UNDER AN ILLEGAL ALIAS, and that she engaged in blatant immigration fraud.
NICE GOING, ASSHOLES.
Let's see your reporting on this.
Today I turn 88…I’ve seen some serious shit. The most serious of it all is love. I love my family, my friends, and my wonderful fans. The power of love remains.
AI Found Memory Flaws in the PHP Engine That Let an Attacker Take Over Servers Running Most of the Web
The PHP security team released emergency patches on October 21 for two critical vulnerabilities in the language’s core engine.
Both carry a CVSS v4.0 score of 9.2. Successful exploitation gives an unauthenticated remote attacker code execution as the web worker on any server running a vulnerable PHP version. PHP runs on roughly 70 percent of websites whose server-side language is known, according to W3Techs measurements that have held in that range for years.
WordPress, Drupal, Joomla, Magento, Laravel, and plain scripts are all exposed when the underlying interpreter is.
The issues are tracked as CVE-2026-109618 and CVE-2026-109619. They are not bugs in application code. They sit in the engine’s handling of request memory and fatal errors. Wiz Research reported the first of them in August after using its Atlas system together with Gemini 4 Argon and GPT-5.6 Sol.
The models helped locate the conditions, chain the memory effects, and adapt the resulting exploits across PHP versions, SAPIs, and heap layouts that a single researcher would otherwise have spent months mapping by hand.
A working unauthenticated proof of concept against current WordPress and Drupal containers was ready within days of the initial finding. The company later posted a technical write-up under the name PHP2Shell.
The core mechanism is the engine’s use of longjmp() to abort a request on out-of-memory. PHP treats memory exhaustion as fatal and jumps out of the current context rather than running normal cleanup that might itself allocate.
In several paths—multipart form parsing that expands headers or nested fields beyond the apparent post_max_size and memory_limit, session upload-progress handling, and certain error-backtrace or OPcache persistence steps—request-owned structures are allocated and then left partially initialized or still referenced from process-global state when the jump occurs.
The request heap is later freed, but the globals (BG(unserialize), EG(last_fatal_error_backtrace), session identifiers, and similar) continue to point at the now-invalid memory.
A later request processed by the same worker can read or write through those stale pointers before normal initialization replaces them. With a controlled heap layout the result is a use-after-free that yields arbitrary read or write and, in the demonstrated cases, full code execution.
One advisory describes the OOM path in detail: a multipart request can force allocation failure during startup or early parsing; longjmp() skips the matching reset; shutdown or the next request’s early diagnostics then operate on the corrupted state. The companion advisory covers the broader stale-global case, where fatal errors, non-fatal diagnostics during shutdown, or interrupted session operations leave request memory reachable across workers.
Both were confirmed to produce unauthenticated remote code execution under default limits on common configurations such as Apache mod_php with prefork. Memory disclosure of other requests’ data (credentials, tokens, keys) is also possible.
The flaws have been present since at least PHP 5.4; every version released in the last decade is affected by at least one of them.
Patches are available for the supported branches: 8.2.35, 8.3.36, 8.4.27, and 8.5.12.
Older branches receive no official fix. Estimates of exposed internet-facing hosts that still advertise a version range from roughly 1.3 million upward, with a substantial fraction on end-of-life releases that cannot be updated in place.
Some hosts have already disabled session.upload_progress as a temporary mitigation while waiting for the packages. Early scanning and exploitation attempts were reported on the morning of the release.
1 of 2
🚨⚠️Important Information: October 21 at 10:00 a.m. Eastern Time (11:00 p.m. Japan Time / 14:00 UTC)
Two critical vulnerabilities (CVSS v4.0 9.2) have been discovered in PHP, and emergency patches will be released.
These vulnerabilities may lead to remote code execution (RCE). If exploited, attackers could execute arbitrary commands on servers from outside or cause data leaks. The impact is widespread and may affect a large number of PHP-based sites, including CMS platforms such as WordPress as well as e-commerce and reservation sites.
After the patches are released, there is concern that attackers will analyze the details and launch automated attacks in a short time. Some security firms have warned of the possibility of large-scale attacks beginning within 15 minutes of the release.
Immediate self-protection measures:
•Change reused passwords
•Enable two-factor authentication (2FA) on major services
•Beware of phishing emails pretending to be “maintenance notices” or “password reset” requests
Server administrators are prioritizing the application of the patches. At the individual level, thoroughly strengthen password management and phishing countermeasures to prepare.