Had some really good conversations with the Cursor Ambassador for Ghana about tech, creativity, and actually shipping ideas.
This is what building in real time looks like.
https://t.co/VkMCFyfxjG
You know that moment when you realize you’re in the right room?
Yeah… this was one of those.
Builders everywhere, ideas flying, and that quiet focus of people actually working.
#cursor#tech
@lostsec_ Recon has been a huge win for me. You made it super simple, and for the last 3 weeks I’ve been pulling in ~$300/week just from recon. Your write-ups and videos helped me build my own method, and it’s working like magic.
Nice! The next is really understanding
1. What each vulnerability class is, what implementation causes it, what context it can be found …
2. How each works, this include how the vulnerability is introduced, how to detect a behavior that signals the presence of the issue, how to exploit it …
Then
Practice, practice and practice how to exploit the vulnerabilities in labs. Portswigger is a great platform to help you on this and it’s free
After that …
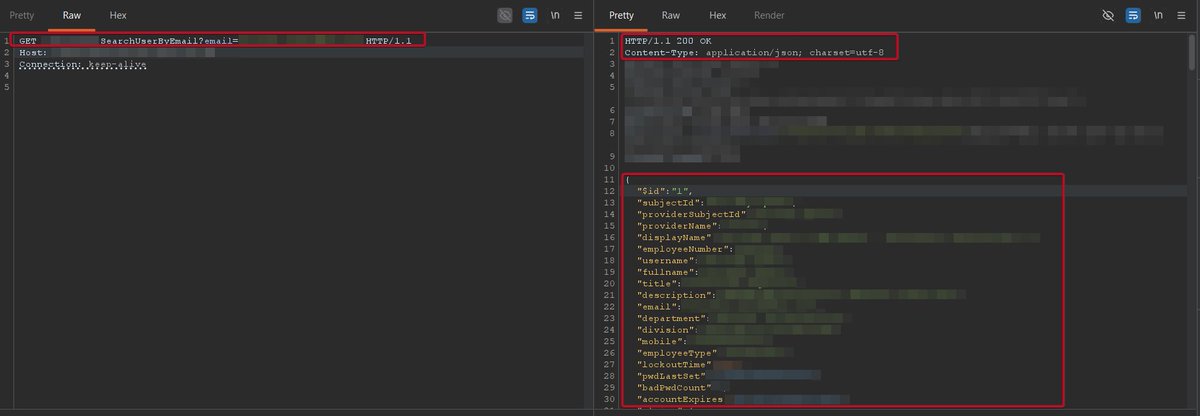
Digging through JS files, uncovering the secrets they hide. Found an admin email in index.js, spotted a ‘search user by email’ endpoint, passed the email … boom. Just treasures in plain sight 💎💎💎
Logical Bugs are often invisible to scanners
They live in the assumptions devs make
Want to find them? Think like the app shouldn’t work
Here are 6 strategies to uncover logic bugs (with examples):
#bugbounty#websec#cybersecurity