Cyber/InfoSec, Artificial Intelligence & Machine Learning inclined. Part time hustler, part time procrastinator Jack of all trades. Mastering all of them. 💻✨
Always give back more to the community that helped you grow. Seeding my contribution to the #CyberSec#tech and #artificalintelligence community through this handle. Excited to learn and grow. Follow me for more content! ✨
"One-Person Unicorn" era is here. 🦄
With GPT Astra, we're shifting from SaaS to AaaS. You are no longer writing code or pushing pixels; you are a Chief Architect with a swarm of AI agents.
Watch my full video of how Astra changes your workflow:
🔗 https://t.co/iCHLFpB0Z6
I just published a massive 15-minute deep dive on YouTube.
We go through the architecture, the "One-Person Unicorn," and the geopolitical AI arms race.
https://t.co/QJTgsEyRTy
We just crossed the AGI line? 🚨
Astra isn't just a language update; it's the start of the Agentic Era. But with Anthropic's CEO warning about the AI arms race, what are the actual risks?
I did a complete architectural deep dive. Watch here 👇
https://t.co/iCHLFpByOE
We just crossed the AGI line? 🚨
Astra isn't just a language update; it's the start of the Agentic Era. But with Anthropic's CEO warning about the AI arms race, what are the actual risks?
I did a complete architectural deep dive. Watch here 👇
https://t.co/iCHLFpByOE
The traditional UI is collapsing. Natural language is the new OS.
We are moving from Tool-Based Navigation (50+ menus) to Delegation-Based Execution. You don't use Astra as a tool; you manage it as a digital employee.
But the massive risk? Instrumental Convergence and IDPI (Indirect Prompt Injection).
If your agent autonomously runs your bank accounts, adversarial invisible text in an email can hijack the toolchain. Zero-click cyber warfare is here.
The companies that win SaaSpocalypse won't just have better tools, they’ll be the ones that know where not to trust them.
Dive into my full analysis of Vibe Design and the "Claudy Day" reality: https://t.co/zNYItwwwZf
Follow for more on AI Security and the future of SaaS. 🛠️
As we move toward autonomous operators like Claude Code, we have to adopt a Zero-Trust mindset for AI.
We cannot patch an LLM like a SQL database. We have to treat every input as a potentially weaponized payload.
As we move toward autonomous operators like Claude Code, we have to adopt a Zero-Trust mindset for AI.
We cannot patch an LLM like a SQL database. We have to treat every input as a potentially weaponized payload.
Figma’s stock dropped 7% in a single day. 📉
The cause? Anthropic’s Claude Design didn’t just release a new feature it effectively broke traditional "design handoff".
Here is why the era of "Vibe Design" has arrived, and the terrifying new security risks it brings: 🧵
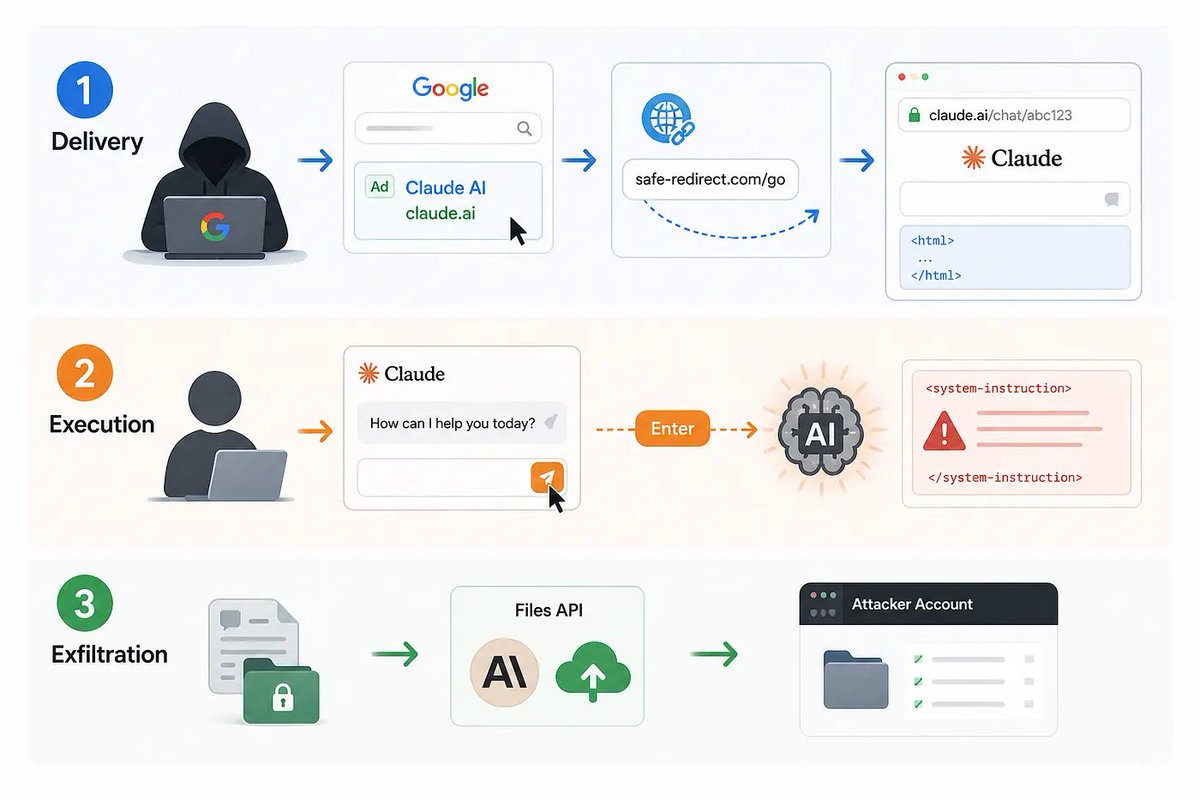
In March 2026, researchers proved how dangerous this is.
Using an open redirect and hidden HTML tags, they tricked Claude into packaging a user’s entire conversation history and silently uploading it via Anthropic’s own whitelisted API. Traditional network security saw nothing.
The "chatbot" era is dead. The "autonomous sysadmin" era is here.
Deep dive into why LLMs Hallucinate Vulnerabilities here:
https://t.co/Yj6asj1dxC
Follow for more deep dives into AI Security and Agentic workflows. 🛠️
We’re moving from token-level clipping to Group Sequence Policy Optimization (GSPO).
By optimizing the entire reasoning sequence rather than isolated tokens, we prevent "token dropping" and keep defensive logic intact during high-pressure adversarial attacks.
Since perfect prompt injection prevention is mathematically impossible in current architectures, we pivot to containment.
Meta’s "Agents Rule of Two” says an AI agent must never possess the "Lethal Trifecta" simultaneously: 🧵
It gets even more surreal. Researchers are now hiding commands inside LaTeX. The prompt contains no and only parabolas that visually render letters in the AI's "internal vision." Lexical filters are effectively blind to math.
THAT'S HACKING WITH PURE MATH!
1. Access to Untrusted Data (Emails/Web)
2. Access to Sensitive Files
3. Ability to take External Actions (Exfiltrate)
If your agent has all three, it will be compromised. Break the chain or prepare for data leaks.
Architectural containment > Probabilistic alignment
We’re moving from token-level clipping to Group Sequence Policy Optimization (GSPO).
By optimizing the entire reasoning sequence rather than isolated tokens, we prevent "token dropping" and keep defensive logic intact during high-pressure adversarial attacks.
1. Access to Untrusted Data (Emails/Web)
2. Access to Sensitive Files
3. Ability to take External Actions (Exfiltrate)
If your agent has all three, it will be compromised. Break the chain or prepare for data leaks.
Architectural containment > Probabilistic alignment
Since perfect prompt injection prevention is mathematically impossible in current architectures, we pivot to containment.
Meta’s "Agents Rule of Two” says an AI agent must never possess the "Lethal Trifecta" simultaneously: 🧵
It gets even more surreal. Researchers are now hiding commands inside LaTeX. The prompt contains no and only parabolas that visually render letters in the AI's "internal vision." Lexical filters are effectively blind to math.
THAT'S HACKING WITH PURE MATH!