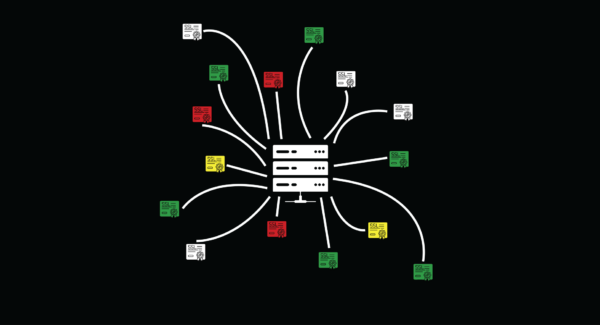
ESC15 is the latest of the ESC privilege escalation attack family. Follow along with Abricto Security to learn how to exploit this vulnerability here: https://t.co/iyPHIAsKLx
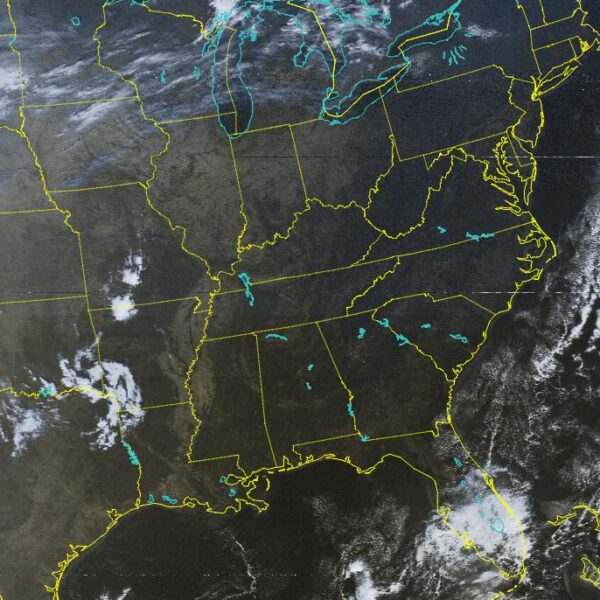
Learn how to capture live satellite images using an RTL-SDR! Discover the tools, and techniques to access live satellite data directly on your device. Check out this fun project here: https://t.co/e0GD6TcwsW
We're excited to share that David Edwards has been promoted to Senior Security Consultant! We look forward to seeing him thrive and grow in this new role. Congratulations, David! #AbrictoSecurity
We're thrilled to share that Kyle Meyer has been promoted to Manager of Consulting Services here at Abricto Security! We look forward to seeing him thrive and lead in his new role. Congratulations, Kyle! #AbrictoSecurity
In this latest blog post, Abricto Security's junior security consultant Christian breaks down a common web application vulnerability known as cross-site request forgery. Check out the blog here: https://t.co/f1kkb6NAXO
NTLM and Kerberos are the more commonly used user authentication protocol. Each has a different way to authenticate a user into a system. Both protocols have their own strengths and weaknesses. Abricto intern Takahiro gives us a walkthrough in this post. https://t.co/qRvhfm1sgg
If you're interested in getting into cybersecurity, try gamifying the experience and familiarize yourself with concepts and tools by joining CTFs! Abricto Security intern Melinda Chareunsip discusses your basic CTF options.
https://t.co/mlEXWajIJH
While there are over a dozen ESC vulnerabilities, the most common to encounter are ESC1 and ESC8. Join Abricto Security's Daniel Cornett as we do a deep dive using the Petit Potam vulnerability and Certipy. https://t.co/RHrmeh7O2L
Join us at BSides Augusta on October 4th at the Harrison Education Commons Building at Augusta University. Don’t miss the chance to meet the team and chat all things cyber. See you there! #BSidesAugusta#CyberSecurity#AbrictoSecurity
Abricto Security is proud to have our Security Consultant Team Lead Kyle Meyer (0xSterny) presenting at @GrrCON on September 26th, 2024. He will be presenting on the offensive security mindset of prompt injections with LLMs. Check out the bio here! https://t.co/QaCdFqONVL
Abricto took on Defcon with consultants David Edwards (Cab00s3) and Kyle Meyer (0xSterny). Thank you to all the volunteers and presenters for putting on such a great conference. Awesome to have a great venue under one roof at LVCC. Can't wait to be back next year! #Defcon
Are you aware of the most common vulnerabilities that affect SaaS platforms?
Check out our latest blog article where we dive into these issues and how to protect against them.
Click here to read 👉 https://t.co/7opJAirw32
Struggling to secure your SaaS app? 🛡️
From design to deployment, security is crucial. Learn how to:
✔️ Integrate security at every stage
✔️ Prioritize user privacy
✔️ Use cloud security features
Discover the blueprint for a secure SaaS platform.
https://t.co/vOaDzAJMM6
Ignoring security audits and employee training can lead to data breaches and security incidents.
Learn how to safeguard your platform with regular audits and continuous monitoring.
Read here 👉 https://t.co/7opJAirw32
Is your SaaS platform truly secure?
In our latest blog post, discover how to build a robust, layered defense strategy that continuously protects your app's data.
https://t.co/vOaDzAJMM6
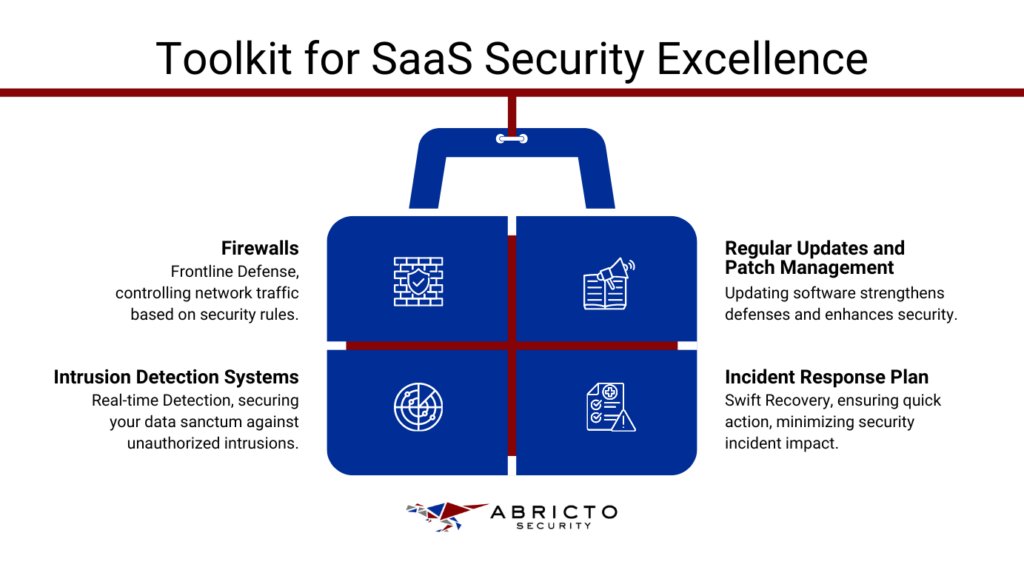
Effective SaaS security requires effective tools and best practices. Equip your SaaS platform with a strong security foundation and understand the importance of a solid incident response plan. Learn more in our latest post! https://t.co/vOaDzAJMM6
Is your SaaS platform secure?
✔️ Data Encryption
✔️ Access Control
✔️ Regular Audits
✔️ Threat Detection
Learn how these pillars protect sensitive info and ensure compliance.
Discover best practices for a robust security framework: https://t.co/vOaDzAJMM6
Excited to launch our AppSec as a Service! Product security is so much more than penetration testing. Our solution fills the security gaps. Learn more here: https://t.co/SpTWBWsHAs
An insecure direct object reference (IDOR) vulnerability enables a threat actor to access unauthorized information by manipulating a web application. If a web application lacks proper access controls, a threat actor could access sensitive information. - https://t.co/66lYTZD0DZ