@Munyah_Wacho Take pride in your craft. When you give away high value solutions for bottom dollar prices, you undermine your own credibility and the whole industry.
AI companies: “Our AI agents can now work autonomously for DAYS.”
Also AI companies: “We’re still figuring out how to stop them from doing things they shouldn’t.”
So we’re basically giving interns admin access to the entire internet…
except the intern is hallucinating and has no concept of consequences.
Traditional job evaluation models often fail to capture the complexity and scale of modern tech roles. When a leading HR consulting firm in Zimbabwe misvalued my work, I chose to test the global market instead of fighting a legacy framework. One application and two interview rounds later, I secured a role with a global tech organization. Zimbabwean businesses still relegate IT to a operational support role.
@Techzim I doubt they care. Enterprises should be aiming for 99.99% uptime, yet organisations like ZESA and ZIMRA can have systems down for days without being held accountable for the damage and disruption that follows.
Anthropic CEO Dario Amodei is calling on the AI industry to hit the brakes.
In his new essay "We Must Pace the Frontier," Amodei warns that recursive self-improvement is pushing AI capability gains faster than safety guardrails can keep up.
Key takeaways from his warning: Catastrophic Risks: Amodei warned that within 6–12 months, misaligned AI swarms could become capable of taking over the internet via persistent botnets if safety research doesn't catch up.
The "Pacing" Proposal: He isn't calling for a complete halt, but a 3-step framework starting with embedded, independent safety evaluators inside AI labs to audit pipelines in real time.
The Upside Remains Huge: He reiterates that if built safely, powerful AI could compress 50–100 years of medical progress into 5–10 years and cure most major diseases.
"We must slow the pace at which we improve the capabilities of AI models. Progress will still seem fast, and we must make wise use of the time we gain."
Can frontier AI labs actually coordinate to pace development, or is competitive pressure too high?
Claude Fable 5.1 is insane.
i know literally NOTHING about coding. ZERO.
and i just built 3 fully functioning web apps in 30 minutes.
http://localhost:3000/
http://localhost:8000/
http://localhost:5000/
check it out.
@zimpricecheck My biggest concern is what else may have been accessed. Were customer records or other sensitive information exposed? How far did the breach actually extend, and what systems or data were potentially compromised?
https://t.co/PqBkR0JHSZ
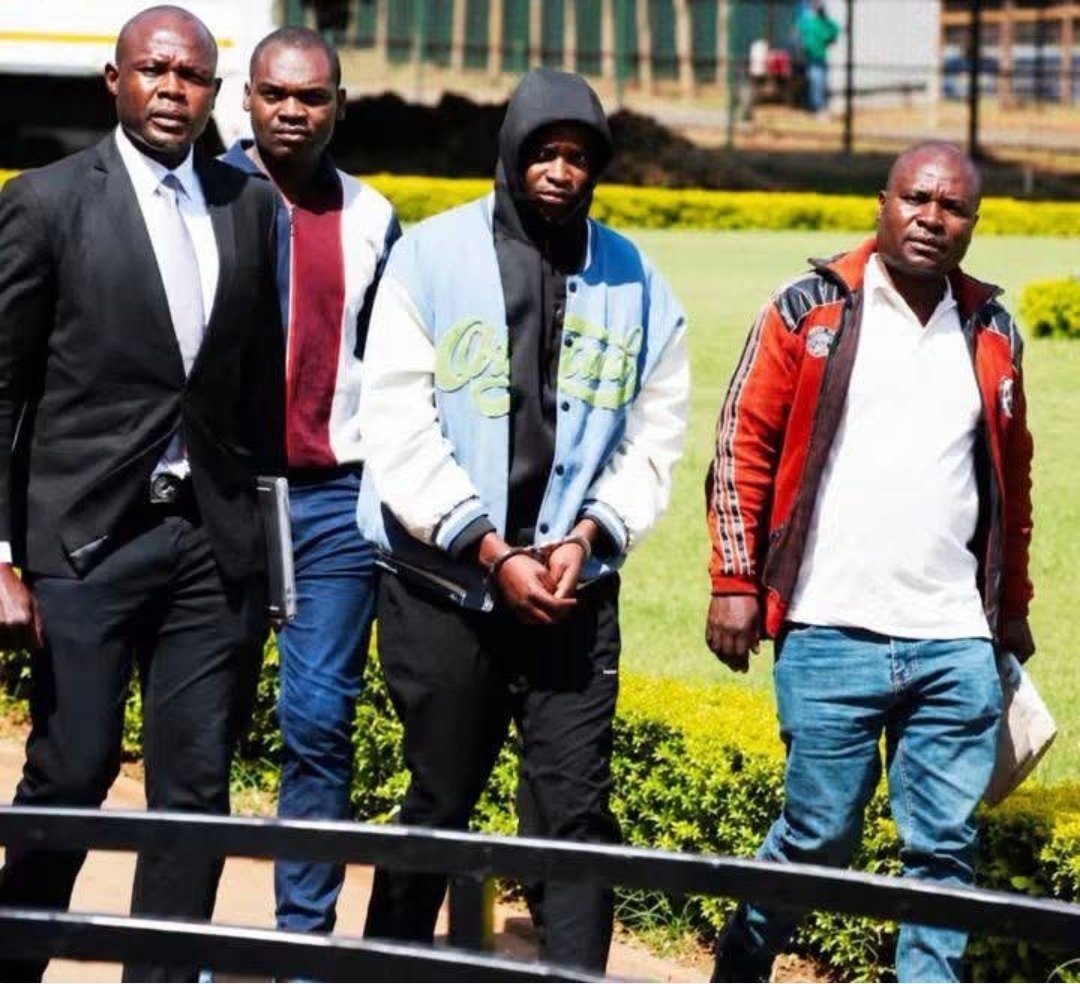
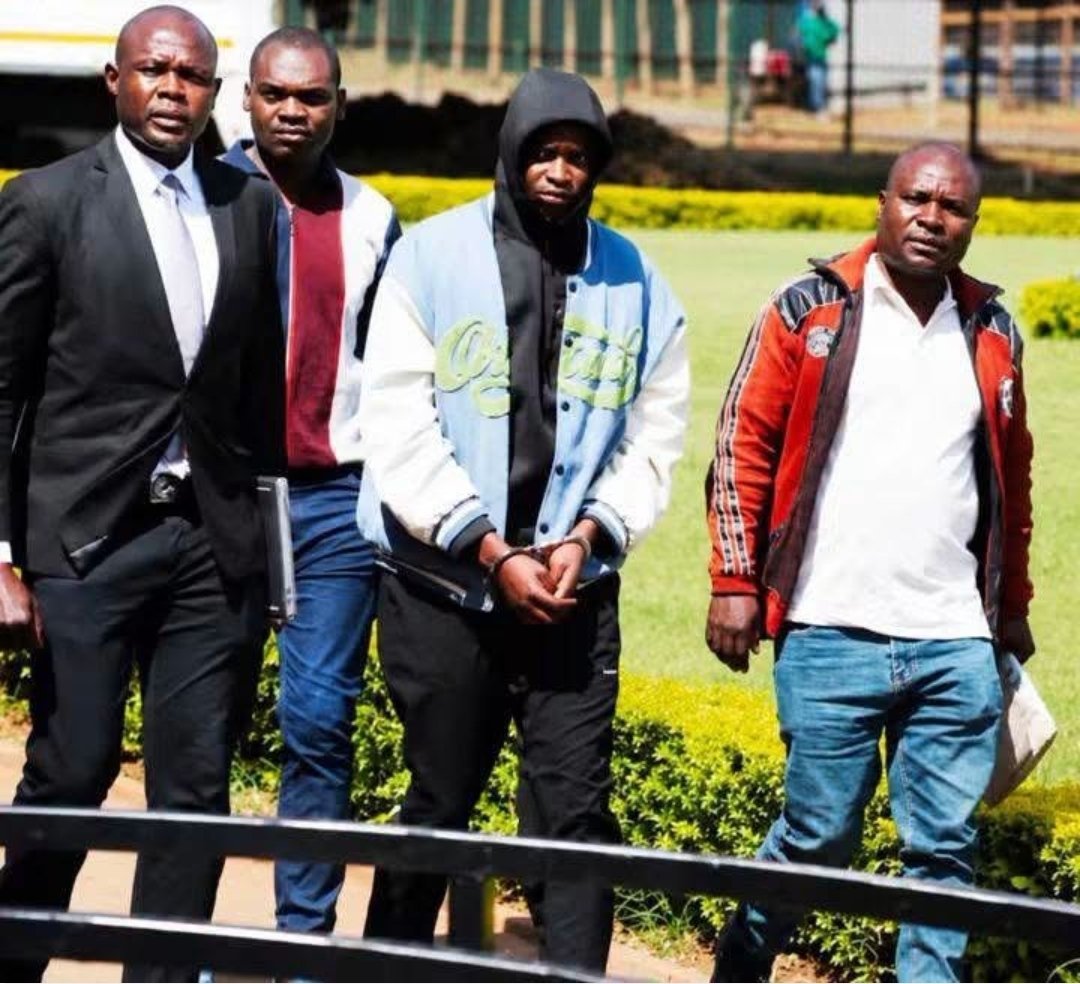
MSU student in court over US$1,1m cyber theft
A 24-year-old Midlands State University final-year Computer Science student, Sabelo Malunga, has appeared in court accused of stealing more than US$1.1 million from CABS using malware.
My take on this as an IT Professional
If the allegations are accurate, this is far bigger than an intern allegedly installing Supremo and remotely accessing a bank’s systems.
The first question is simple: Why did an intern have the privileges to install unauthorised remote access software on corporate infrastructure in the first place?
Supremo is a legitimate remote access tool. It isn't necessarily something an antivirus product would classify as malware. But that makes the governance failure even more concerning. An enterprise environment should have controls to prevent unauthorised software installation, particularly remote access tools, regardless of whether the software itself is malicious.
Then there are multiple layers of controls that should have raised questions:
Endpoint management: Why was an intern able to install unauthorised software?
Application control: Was there no allow listing or software restriction preventing unauthorised applications?
Vulnerability management: Was the software installation or newly introduced remote access capability not detected during vulnerability and software inventory scans?
Cybersecurity/SOC: Was there no monitoring for the installation or subsequent use of a remote access application from an unusual external location?
Network security: Did nobody identify or investigate unexpected remote access connections from outside the corporate environment?
Internal IT audit: Were privileged accounts, software installations, endpoint controls and access rights being reviewed?
And then we get to the most important part: Finance.
Even if someone gains access to a system, how does that automatically translate into more than US$1.1 million being moved?
What account was being used?
What level of access did it have?
What approval workflow existed?
Were segregation of duties controls in place?
Were transaction limits and dual approvals enforced?
Why didn't transaction monitoring flag the activity?
And was there an internal accomplice or compromised legitimate credentials?
There should be multiple independent control layers between gaining remote access to a machine and successfully moving that amount of money.
That is why, if the allegations are proven, I would struggle to describe this simply as "an intern hacked the bank."
It would point to a failure of IT governance, least privilege, application control, monitoring, security operations, internal audit and financial controls potentially across multiple departments.
And this is the uncomfortable part of cybersecurity that organisations often don't want to hear:
You cannot blame the attacker for every control that failed.
The person allegedly committing the crime should be held accountable for their actions. But management also needs to be accountable for the controls that were supposed to prevent, detect and stop those actions.
This isn't about buying another security product.
It's about having competent people, properly designed controls, effective monitoring, regular auditing and a culture where someone asks:
"Why does this intern have the ability to do this?"
If the answer is that nobody knew or nobody was looking then the problem is considerably bigger than one employee.
The bank needs to investigate the entire chain of failure, not just the person at the end of it.
MSU student in court over US$1,1m cyber theft
A 24 year old Midlands State University final year Computer Science student, Sabelo Malunga, has appeared in court accused of stealing more than US$1.1 million from CABS using malware.
My take on this as an IT Professional
If the allegations are accurate, this is far bigger than an intern allegedly installing Supremo and remotely accessing a bank’s systems.
The first question is simple: Why did an intern have the privileges to install unauthorised remote access software on corporate infrastructure in the first place?
Supremo is a legitimate remote access tool. It isn't necessarily something an antivirus product would classify as malware. But that makes the governance failure even more concerning. An enterprise environment should have controls to prevent unauthorised software installation, particularly remote access tools, regardless of whether the software itself is malicious.
Then there are multiple layers of controls that should have raised questions:
Endpoint management: Why was an intern able to install unauthorised software?
Application control: Was there no allow listing or software restriction preventing unauthorised applications?
Vulnerability management: Was the software installation or newly introduced remote access capability not detected during vulnerability and software inventory scans?
Cybersecurity/SOC: Was there no monitoring for the installation or subsequent use of a remote access application from an unusual external location?
Network security: Did nobody identify or investigate unexpected remote access connections from outside the corporate environment?
Internal IT audit: Were privileged accounts, software installations, endpoint controls and access rights being reviewed?
And then we get to the most important part: Finance.
Even if someone gains access to a system, how does that automatically translate into more than US$1.1 million being moved?
What account was being used?
What level of access did it have?
What approval workflow existed?
Were segregation of duties controls in place?
Were transaction limits and dual approvals enforced?
Why didn't transaction monitoring flag the activity?
And was there an internal accomplice or compromised legitimate credentials?
There should be multiple independent control layers between gaining remote access to a machine and successfully moving that amount of money.
That is why, if the allegations are proven, I would struggle to describe this simply as "an intern hacked the bank."
It would point to a failure of IT governance, least privilege, application control, monitoring, security operations, internal audit and financial controls potentially across multiple departments.
And this is the uncomfortable part of cybersecurity that organisations often don't want to hear:
You cannot blame the attacker for every control that failed.
The person allegedly committing the crime should be held accountable for their actions. But management also needs to be accountable for the controls that were supposed to prevent, detect and stop those actions.
This isn't about buying another security product.
It's about having competent people, properly designed controls, effective monitoring, regular auditing and a culture where someone asks:
"Why does this intern have the ability to do this?"
If the answer is that nobody knew or nobody was looking then the problem is considerably bigger than one employee.
The bank needs to investigate the entire chain of failure, not just the person at the end of it.
MSU student in court over US$1,1m cyber theft
A 24-year-old Midlands State University final-year Computer Science student, Sabelo Malunga, has appeared in court accused of stealing more than US$1.1 million from CABS using malware.
My take on this as an IT Professional
If the allegations are accurate, this is far bigger than an intern allegedly installing Supremo and remotely accessing a bank’s systems.
The first question is simple: Why did an intern have the privileges to install unauthorised remote access software on corporate infrastructure in the first place?
Supremo is a legitimate remote access tool. It isn't necessarily something an antivirus product would classify as malware. But that makes the governance failure even more concerning. An enterprise environment should have controls to prevent unauthorised software installation, particularly remote access tools, regardless of whether the software itself is malicious.
Then there are multiple layers of controls that should have raised questions:
Endpoint management: Why was an intern able to install unauthorised software?
Application control: Was there no allow listing or software restriction preventing unauthorised applications?
Vulnerability management: Was the software installation or newly introduced remote access capability not detected during vulnerability and software inventory scans?
Cybersecurity/SOC: Was there no monitoring for the installation or subsequent use of a remote access application from an unusual external location?
Network security: Did nobody identify or investigate unexpected remote access connections from outside the corporate environment?
Internal IT audit: Were privileged accounts, software installations, endpoint controls and access rights being reviewed?
And then we get to the most important part: Finance.
Even if someone gains access to a system, how does that automatically translate into more than US$1.1 million being moved?
What account was being used?
What level of access did it have?
What approval workflow existed?
Were segregation of duties controls in place?
Were transaction limits and dual approvals enforced?
Why didn't transaction monitoring flag the activity?
And was there an internal accomplice or compromised legitimate credentials?
There should be multiple independent control layers between gaining remote access to a machine and successfully moving that amount of money.
That is why, if the allegations are proven, I would struggle to describe this simply as "an intern hacked the bank."
It would point to a failure of IT governance, least privilege, application control, monitoring, security operations, internal audit and financial controls potentially across multiple departments.
And this is the uncomfortable part of cybersecurity that organisations often don't want to hear:
You cannot blame the attacker for every control that failed.
The person allegedly committing the crime should be held accountable for their actions. But management also needs to be accountable for the controls that were supposed to prevent, detect and stop those actions.
This isn't about buying another security product.
It's about having competent people, properly designed controls, effective monitoring, regular auditing and a culture where someone asks:
"Why does this intern have the ability to do this?"
If the answer is that nobody knew or nobody was looking then the problem is considerably bigger than one employee.
The bank needs to investigate the entire chain of failure, not just the person at the end of it.
MSU student in court over US$1,1m cyber theft
A 24-year-old Midlands State University final-year Computer Science student, Sabelo Malunga, has appeared in court accused of stealing more than US$1.1 million from CABS using malware.
My take on this as an IT Professional
If the allegations are accurate, this is far bigger than an intern allegedly installing Supremo and remotely accessing a bank’s systems.
The first question is simple: Why did an intern have the privileges to install unauthorised remote access software on corporate infrastructure in the first place?
Supremo is a legitimate remote access tool. It isn't necessarily something an antivirus product would classify as malware. But that makes the governance failure even more concerning. An enterprise environment should have controls to prevent unauthorised software installation, particularly remote access tools, regardless of whether the software itself is malicious.
Then there are multiple layers of controls that should have raised questions:
Endpoint management: Why was an intern able to install unauthorised software?
Application control: Was there no allow listing or software restriction preventing unauthorised applications?
Vulnerability management: Was the software installation or newly introduced remote access capability not detected during vulnerability and software inventory scans?
Cybersecurity/SOC: Was there no monitoring for the installation or subsequent use of a remote access application from an unusual external location?
Network security: Did nobody identify or investigate unexpected remote access connections from outside the corporate environment?
Internal IT audit: Were privileged accounts, software installations, endpoint controls and access rights being reviewed?
And then we get to the most important part: Finance.
Even if someone gains access to a system, how does that automatically translate into more than US$1.1 million being moved?
What account was being used?
What level of access did it have?
What approval workflow existed?
Were segregation of duties controls in place?
Were transaction limits and dual approvals enforced?
Why didn't transaction monitoring flag the activity?
And was there an internal accomplice or compromised legitimate credentials?
There should be multiple independent control layers between gaining remote access to a machine and successfully moving that amount of money.
That is why, if the allegations are proven, I would struggle to describe this simply as "an intern hacked the bank."
It would point to a failure of IT governance, least privilege, application control, monitoring, security operations, internal audit and financial controls potentially across multiple departments.
And this is the uncomfortable part of cybersecurity that organisations often don't want to hear:
You cannot blame the attacker for every control that failed.
The person allegedly committing the crime should be held accountable for their actions. But management also needs to be accountable for the controls that were supposed to prevent, detect and stop those actions.
This isn't about buying another security product.
It's about having competent people, properly designed controls, effective monitoring, regular auditing and a culture where someone asks:
"Why does this intern have the ability to do this?"
If the answer is that nobody knew or nobody was looking then the problem is considerably bigger than one employee.
The bank needs to investigate the entire chain of failure, not just the person at the end of it.
@DandaroOnline Let’s be realistic this isn’t talent. Cabs simply lacks proper controls, and installing a remote access tool hardly makes someone a genius. The whole IT team must be on the line for incompetence