"Alex Rivera", "Maya Chen", "Jonas Weber", "Priya Nair" are everywhere these days. Are these Claude's new watermarks?
Anyway, great way to spot fake companies and fake reviews: https://t.co/2pQcOw4NdK
@TadeasKmenta Strictly speaking, the GMS injection didn't bypass FRP. It bypassed SUW, which massively increases the attack surface against FRP. Countless ways to disable it from a fully booted Android device (e.g. my USB Nday chain, plus leaking the secret over ADB).
eMudhra key leaks impact Android's Factory Reset Protection (FRP), thanks to the generous GMS sign-in interface.
TL;DR: Inject mm.setContentFilters('{"user_setup_complete":1, "device_provisioned":1}'); on server JS responses with `mitmproxy --emudhra` and reboot, bypassing SUW. Then, flip system_server's mFrpActive with any N-day to leak the secret and wipe FRP.
Demo below. Full chain private for obvious reasons.
@RDKLInc@h1ghju1ce Indeed, MDM is trickier. Out of curiosity: Do your devices support OEM unlocking?
My chain was fully offline and tested on a Pixel 8a, which supports unlocking, so it should be possible to factory wipe and flash an MDM-free AOSP fork.
@hi_yoniyang Yes, that works too. My USB setup was needed because stage-2 Nday chain targeted USB drivers. But it's swappable with any Nday post reboot.
As for TalkBack, maybe it's optional, but I never managed to repro the GMS payload going directly into sign-in.
Recently @malltos92 gave great advice applicable to anyone doing novel research:
> DO NOT [...] USE ONLINE MODELS, LLMs will take what you have and amplify it to every code base, effectively making any novel ideas you had extinct. Do not give your knowledge away for free to these online models, monetize them offline.
holy shit.
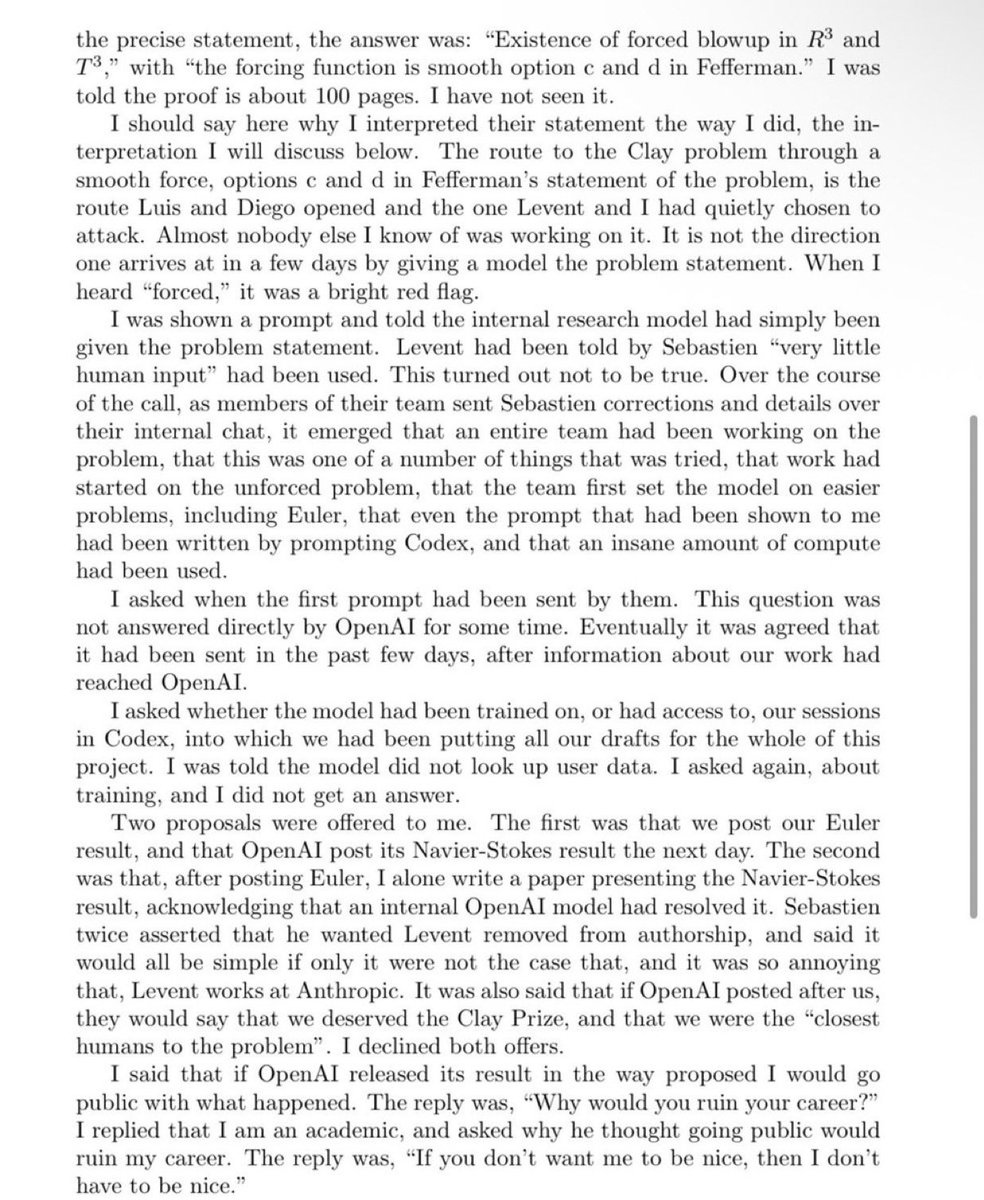
tristan buckmaster is saying openai has a forced navier–stokes blowup via the córdoba / martínez-zoroa program.
and that it may have used drafts from his and levent alpöge’s private codex sessions.
that’s the córdoba / martínez-zoroa route. almost nobody else was on it.
he also says the first prompt went out after information about his and levent alpöge’s work reached openai. that “very little human input” was not true. that a whole team had already been set on easier problems, including euler. that even the prompt they showed him was written by prompting codex.
then he asked:
did the model have their private codex sessions.
no answer on training.
if any of that holds, openai didn’t just scoop a math result. they may have done it off two researchers’ unpublished drafts, then tried to cut the coauthor because he works at anthropic.
a millennium-problem-adjacent result just became employee drama before an ipo.
i don’t even know which part is crazier.
this is one of the slimiest things i’ve seen in this industry.
@gf_256 Out of curiosity: Have you read Permutation City? Do you actually need to compute the end state to "make it real"?
Or does the "computational latent space" (for lack of a better word) exist even in the absence of a medium to compute it?
It looks like most 0day/bounty prices will drop to a slim premium on top of token costs, and cybersecurity will be proof-of-work (always has been?)
But for now, this seems like the best arbitrage opportunity in years.
Because Play Integrity is a different service than Hardware Attestation API. With the latter, you manage approved boot keys. With the former, Google does.
Yes, ideally developers should utilize the Hardware Attestation API, but EU DMA obligations cannot make Play Integrity disappear (the service itself is not the problem, but how it is run). All we can realistically do is demand fair access conditions to recognize additional boot keys.
Just filed an EU DMA complaint against Alphabet for gatekeeping against secure Android derivatives like @GrapheneOS via Play Integrity.
TL;DR: not certified ≠ not secure. Google lacks a FRAND certification process for non-OEMs that comply with objective security requirements.
@TimSweeneyEpic@GrapheneOS Yes, I have uploaded the DMA concerns and proposal below. Would be great to hear your thoughts on this. https://t.co/V7q62RAatr
I have additional material, but there's only so much that makes sense to post publicly.
Capstone.js, Keystone.js, Unicorn.js ports have been updated and published on NPM.
You can now assemble, disassemble and execute code of many new architectures in your web browser. Faster via WebAssembly, and using BigInt to support i64 interfaces.
https://t.co/QaAGWGixI7
@landaire Good point that's actually genius. Would be very interesting to have agents crawl vulns/patches, group and create queries for them. With a massive query DB, hit all OSS repos and have agents triage matches.
@landaire AIs still need tools to efficiently query data while saving on tokens. CodeQL provides this, right?
Just like AI can reverse assembly snippets, but on large projects is more effective paired with Ghidra/IDA to inspect xrefs, CFGs or reason over decompiled pseudocode.
It is, when easily available in manifests/DLLs, but static vendored dependencies in binaries with stripped symbols are often overlooked.
Gets worse as layers increase, e.g. app depending on libA -> libB -> libC. A vuln in libC requires up to 4 independent parties to fix, though those hellish scenarios occur usually in langs with easy dependency management.
Agreed with OP on vendoring. Langs with hard dep management incentivize vendoring, which in turn disincentivizes dep bloat, and reduces exposure to vulns.