my last tweet
new posts on #sigma https://t.co/dShHefHhBI and anything #infosec related which reflects my personal views will be published here https://t.co/ri0CjpMg0Q
story in the thread below
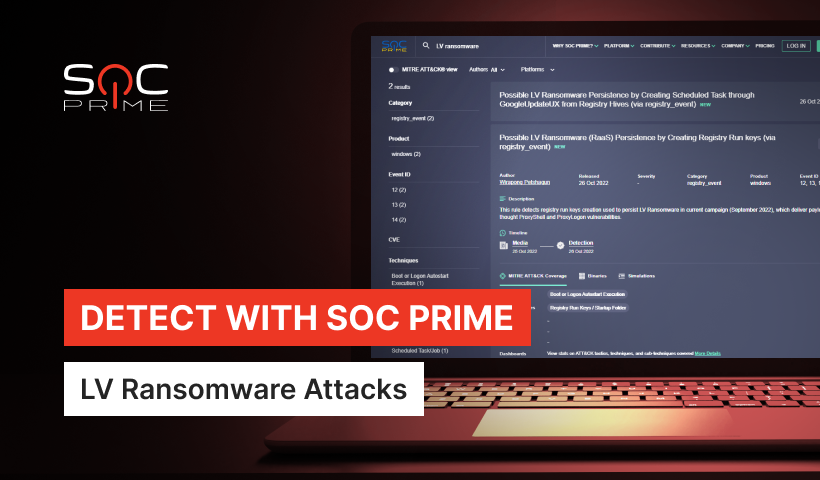
#Sigma rules to detect #LV#ransomware, an alleged #REvil successor actively targeting Europe & North America.
https://t.co/Kq6fcV1wuA
650+ rules to detect ransomware threats are right at hand! Get 30+ for free or reach all with On-Demand at https://t.co/KijuduKmwO #BlueTeam
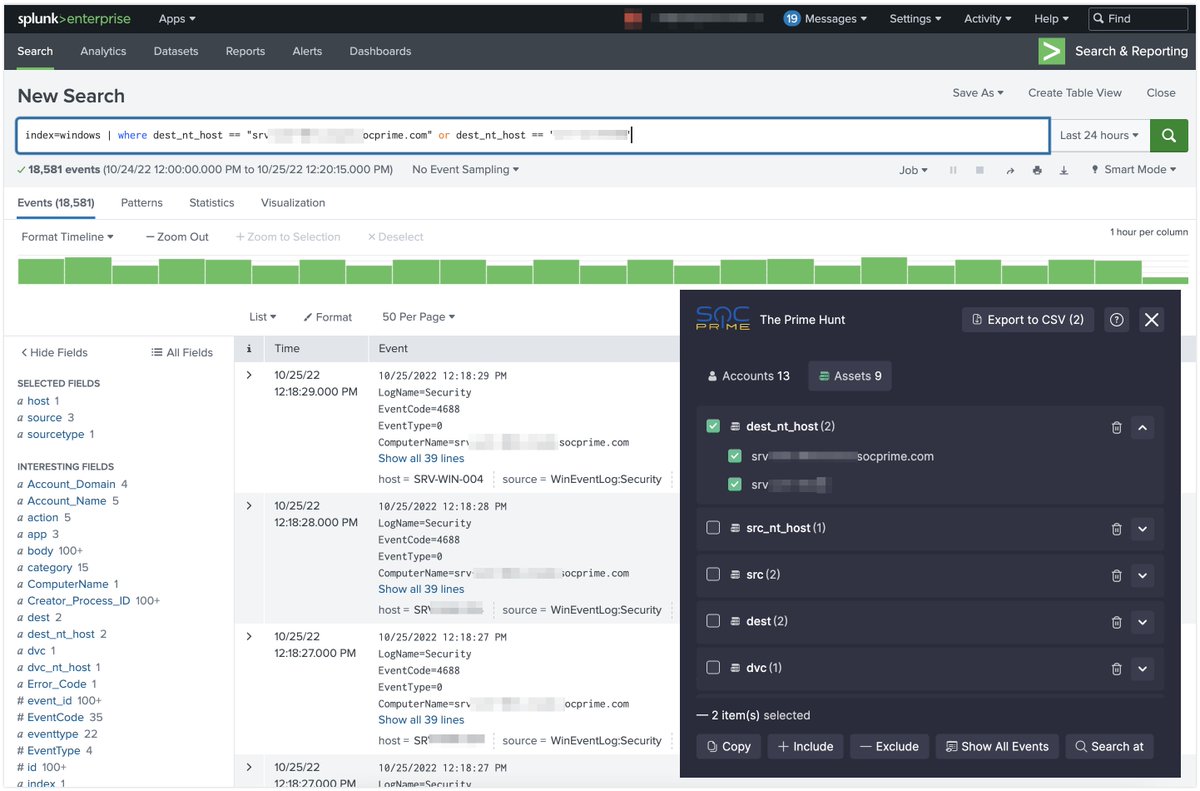
#ThePrimeHunt v 1.0.2 is out, despite blackouts and drone terror, massive thanks to our R&D team in #Ukraine. What's new?
https://t.co/lXZ93GmOXw
+ #Splunk is now supported!
+ EchoTrail integration for file rep context
+ https://t.co/dSGlOr4Uhd for context
improvements:
SOC Prime is attending IT-SA 2022 on October 25-27 in Nürnberg. Meet us and learn how to boost the effectiveness of your security operations with Collective Cyber Defense and Detection as Code.
Interested? Reach out to @TillsTweet for more details. @itsa_ITSecurity#itsaexpo
Do we plan to support more SIEM / EDR? Well, since it started with #sigma, the goal would be to support all sigmacs / sigma backends out there.
Ideas? Suggestions? Issues? PR? https://t.co/sXZ2dhd0jW
Today one of my dreams came to life. The Prime Hunt, one UI for platform agnostic threat hunting is out: https://t.co/sXZ2dgUR5O
An #opensource LGPL browser add-on that extends the success of #sigma as platform agnostic language for threat hunting to one UI. Waaaat? read on!
Immediate detection is essential as exploitation of public-facing Exchange servers is used by russian threat actors against Ukraine and allies.
Defence Intelligence of Ukraine: https://t.co/uVXAevuR7F
CERT-UA on Exchange Exploitation as Initial Access: https://t.co/SJCtUmeIvT
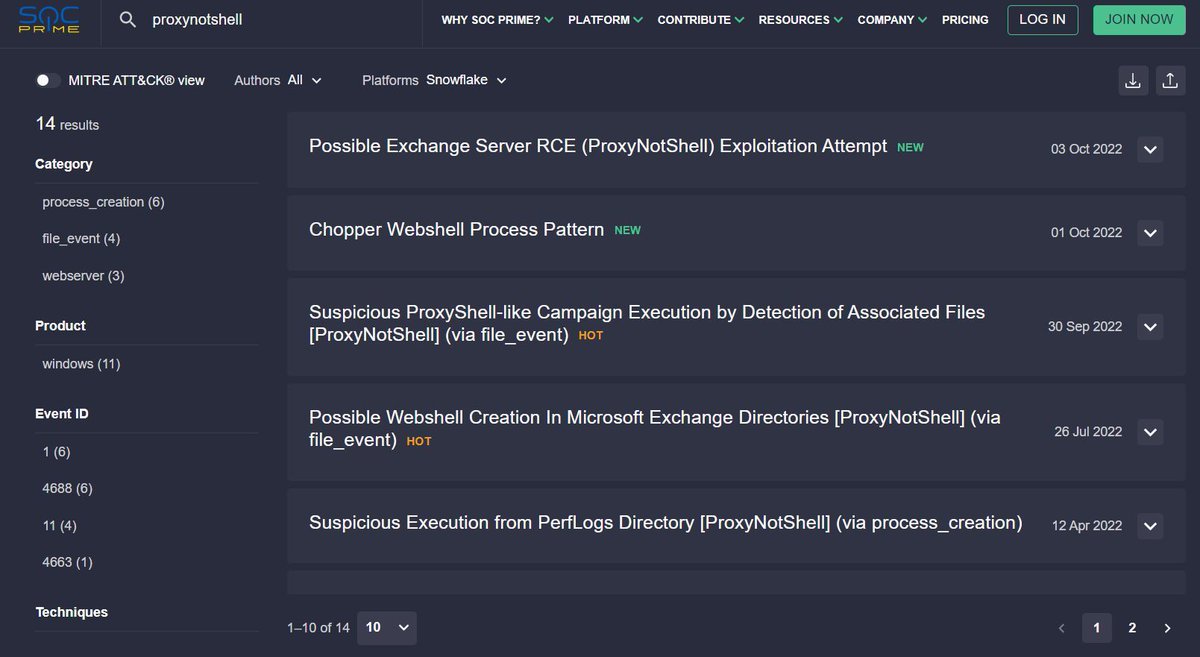
To defend Ukrainian organisations using IBM #QRadar, we are sharing pro bono 124 #Sigma rules on #ProxyNotShell and relevant vulnerabilities on Initial Access tactics as reported by #CERTUA division of @dsszzi
Full post
https://t.co/4ow4N6r5yH
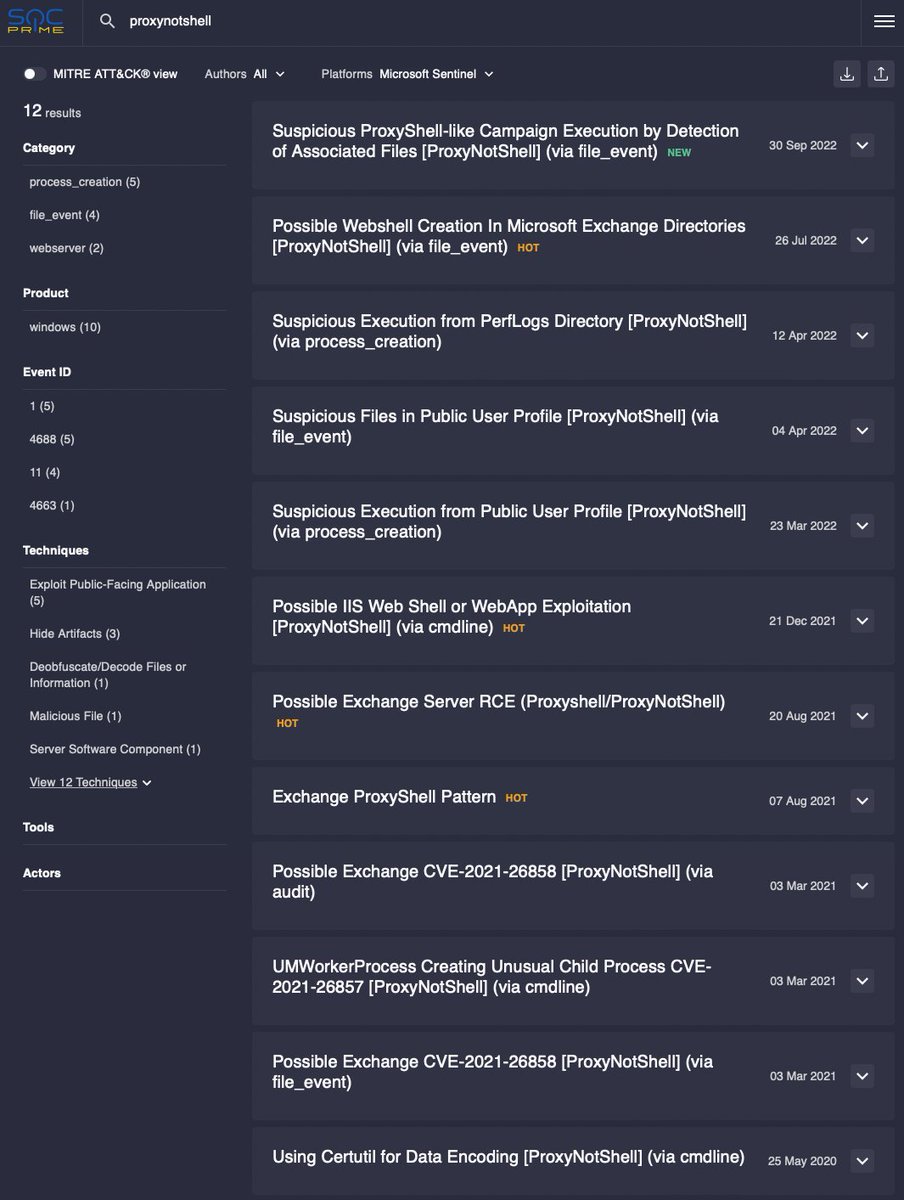
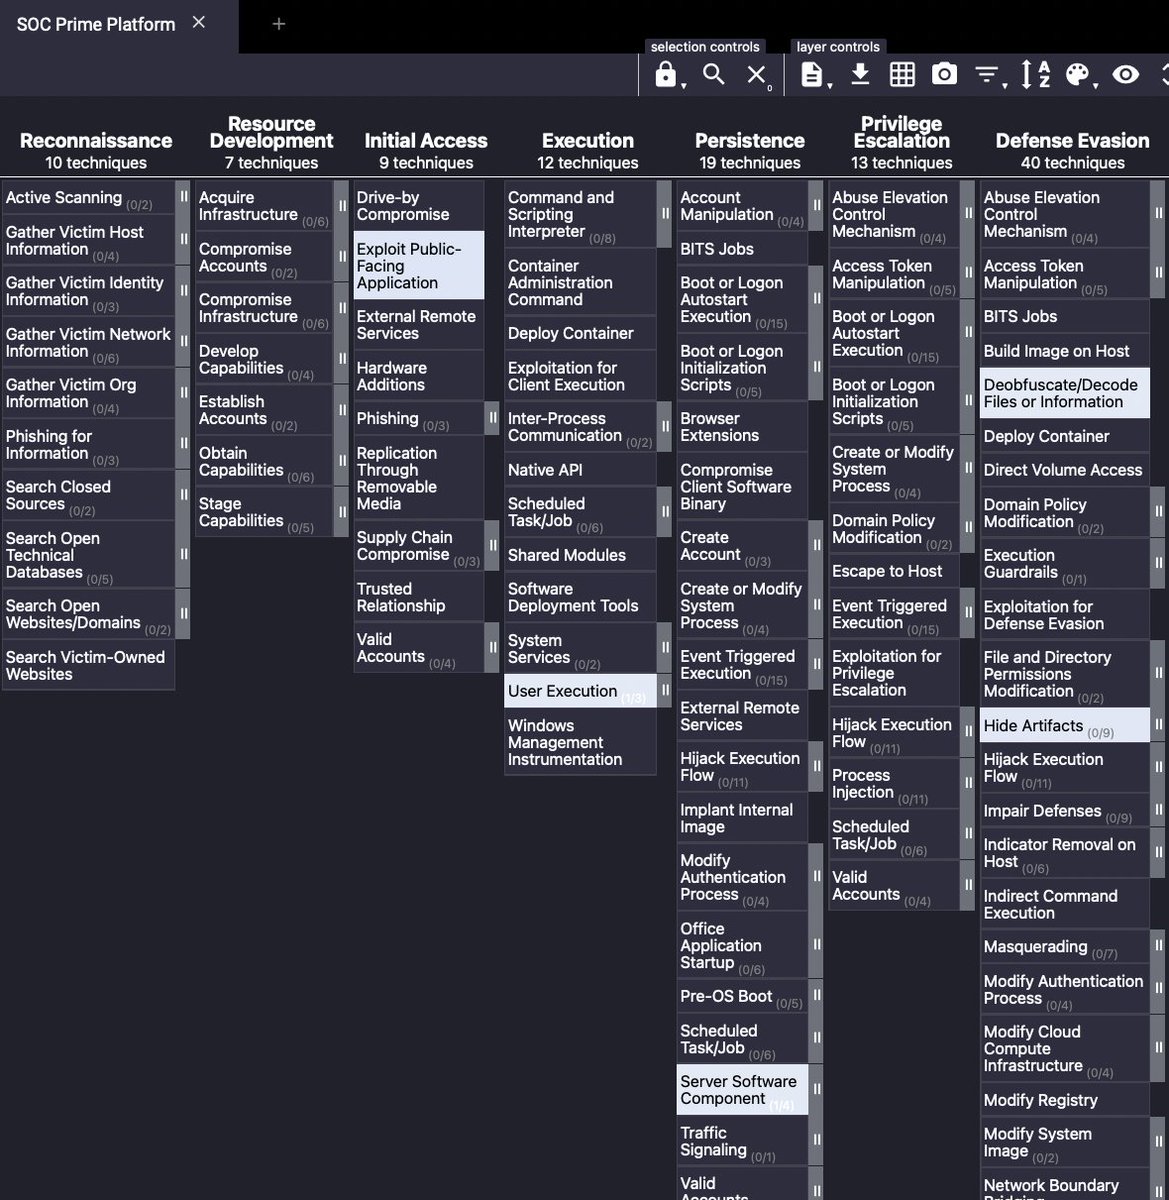
12 Sigma rules for CVE-2022-41040 & CVE-2022-41082 aka #ProxyNotShell for Microsoft Sentinel along with MITRE ATT&CK Mapping, strategic, tactical and technical recommendations including logging. Search here, no registration:
https://t.co/d4rQqc1DYK