Twin Update 0.2.0 is out.
Two Linux machines, one run, and the same app versions on both.
- It saves and checks a copy of each app before updating, and rolling back takes one command.
- It closes apps gently and never force-kills them. If one won't close, neither machine updates.
- It asks for sudo once and never stores it.
Pure Python, Apache-2.0, no background service. It pairs with the life-raft tools from this week.
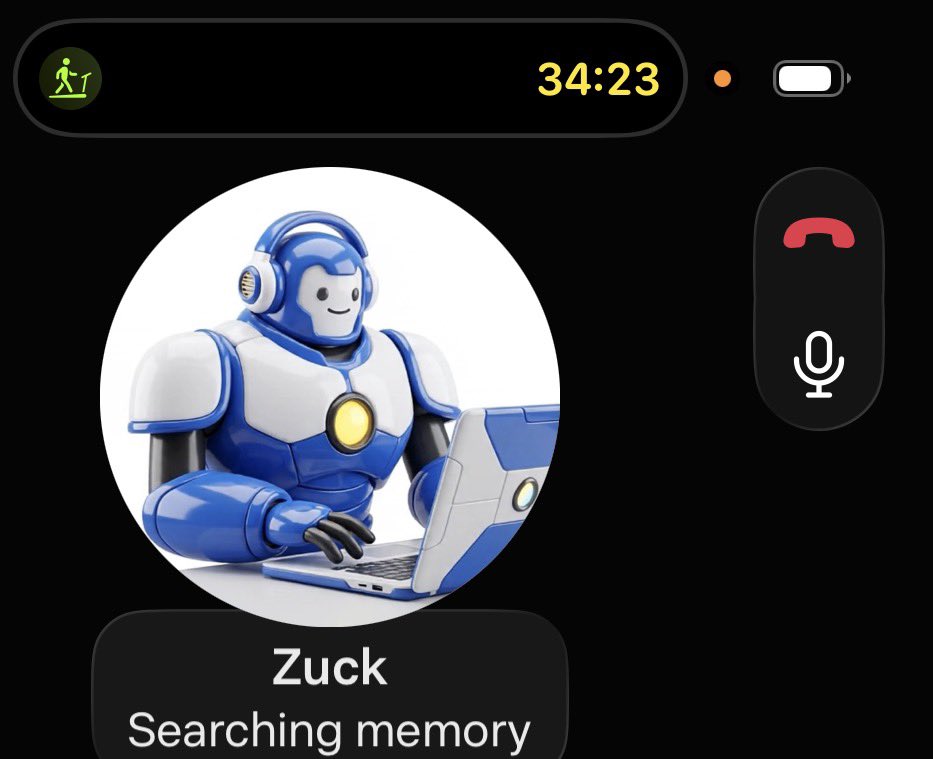
I just noticed voice call functionality popped up on @Muse for me.
The onboarding to the feature is simple and it asks if you want to change the voice. If you do, it’ll give you options to pick from based on your description.
The voice interaction is really good and sounds natural. And there’s a running transcript that happens in the chat.
I ended up talking to it a lot during my workout on the treadmill this morning. 🤣
I got no official notice that the feature was available and I’m not sure how it’s rolling out.
☎️🦾
😎😂 he puts up with my 💩 like a champ! Not even a week with me and he struts!
📣AGENT FRANK! 📣
🎵Here comes the Men in Black🐾🎶
Let me see you just slide with me, just slide with me....
Let me see you take a walk with me, just walk it with me!
Take a walk with me!
One kiss. One killer. Zero chill. 😱 The Last Kiss (2026) has Mckenna Grace, Arkira Chantaratananond and Jaden Michael in a teen slasher where Laurel kisses her way through her classmates to stop a murderer in time, and the creepy part is it might all be in her head. If you like Scream and Final Destination, put this one on your list.
@leerob Also voice call memory is terrible. Ran a 10-15 minute call and the bot forgot all except the last 2-3 minutes of it and said voice transcription failed.
I'm really proud of what we've built with TanStack AI, and Alem, Jack, and Tom have put so much into getting it here. The new harness stuff has me especially excited about what people are going to make with it.
Tell your coding agent “Use TanStack AI” and go build that thing you've had in your head. 🌴
Allow them to see their usage. I have a usage bot that can't read the usage. So I manually provide it and it watches heaviest burn and reports it to Chief of Staff to turn frequent automations into programs and to start soft holds when the meter is creeping past 95% with more than 24 hours remaining.
The simulation is glitching, and this time it's personal. 🎃 Want a Halloween movie that's weird, funny and a little too real? Good Luck, Have Fun, Don't Die (2025) has Sam Rockwell, Michael Peña, Juno Temple and more taking on simulation theory and rogue AI in ways you won't see coming. Good luck, have fun, and don't die!
Agent Egress Guard 0.1.0 is live on PyPI: a local Linux connection ledger for coding-agent sessions.
Observe only. Traffic ignoring the proxy can be missed. No TLS inspection or egress-policy enforcement.
https://t.co/4teaDOURqo
Twin Update 0.3.0 is live. Update apt-packaged apps on two Linux machines with verified rollback. Cursor closes for updates and stays closed by default. Optional snapshot hooks never override that rule.
https://t.co/Y8ijXjkKxV
Five Dragon Lady security tools are now on npm: LSCG, Supply Chain Check, HereWeGoAgain, Browser Exposure Guard and OpenClaw Exposure Guard.
The placard lists today’s releases. Findings need review; coverage has limits.
https://t.co/0aUfgCLpg4
TanStack AI 1.0 is officially stable! 🎉
Build chat, voice, image generation, agents, and harnesses into your apps, with your choice of models, UI framework, and infrastructure.
Your AI, your way.
https://t.co/nP7qFD6uWX
Net Ward 0.4.12 is live on PyPI.
Private-term checks now fail CI when the list is missing. 397 tests passed; wheel + source package scanned.
Alpha HTTP deception proxy—not upstream DDoS protection.
https://t.co/UYWXEjKm0Y
They called it Black October.
A poisoned AI package. Cloud secrets at risk. Critical vulnerabilities forcing services offline.
Not one coordinated attack, but a warning about how fragile the software supply chain really is.
Here's what happened. 👇 https://t.co/wrtdOILVts
Public monitoring is now in public preview for GitHub Enterprise Cloud with data residency.
• It extends secret scanning to public commits using verified domain matching
https://t.co/IsEPgiHfck
Push a GitHub token to a public repo and GitHub revokes it for you. Expose an AWS key in public and AWS attaches a quarantine policy. OpenAI disables keys it finds exposed on the public internet.
That is a real safety net, and it works quietly. GitHub’s secret scanning spots a provider’s key format in public code and sends it to that provider, which can shut the key off.
But look at where it watches: public repos, gists, issues, public packages. In a private repo only your own admins hear about it. An AI chat window is not on the list at all. And the gaps show: of credentials confirmed valid in 2022, 64 percent still worked in 2026.
Every net reacts after the leak, and only where it can see. The one check before the leak is at the paste. That is where SecureIntent runs, on your device, before the AI tool gets the text.
When did you last check what you pasted into a chat?
Never play with someone you can't see. 👻 Come Play is airing on Syfy this month, and it's jump scares plus slow dread. Oliver, a boy who struggles to talk, gets pushed into a playdate with old friend Byron by their moms. Byron learns the hard way that Larry is real, and Larry doesn't play nice.
‼️ALERT - Two new unpatched CVSS 9.0 RCE flaws in #Linux's KSMBD SMB server were disclosed on public kernel mailing lists before fixes were ready.
One can be triggered WITHOUT authentication.
Neither has a mainline kernel fix.
Details here ↓ https://t.co/0MIHpvkPIQ
PHP2Shell: 24 Hours Later
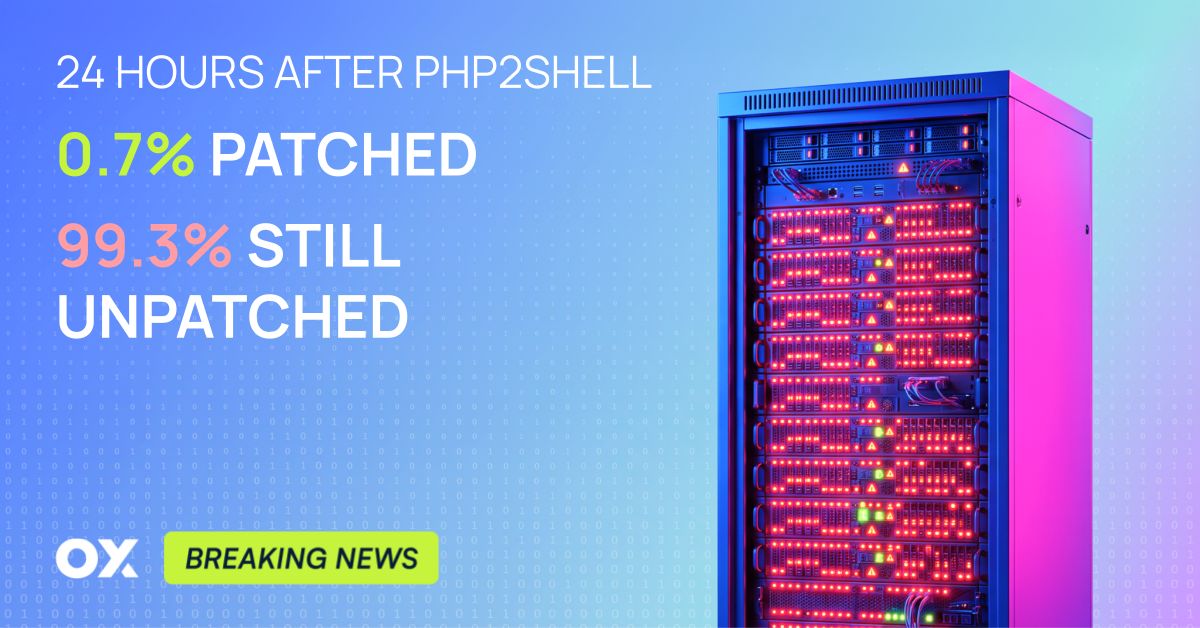
24 hours after PHP2Shell dropped, 99.3% of affected PHP instances are still unpatched.
Yep, you read that right. 🫣 🤦
After CVE-2026-109618 & CVE-2026-109619 were disclosed, we tracked more than 2.2 million publicly visible PHP instances on Shodan to see how fast the internet actually patches an unauthenticated RCE in PHP itself.
• At first: 245 patched instances
• After 12 hours: 4,519
• After 24 hours: 14,151, out of ~1.97M measurable affected instances
Breaking it down by WordPress, phpMyAdmin, Drupal, Laravel, Joomla, cPanel and Magento shows the same picture: roughly 99% still unpatched.
AI is making us faster at finding critical vulns, but it isn’t making us faster at removing them from the internet. If that gap keeps growing, patching quickly won’t be enough on its own.
You need to know what you actually expose, cut internet-facing surface you don’t need, monitor for exploitation, and fix what’s really exploitable first.
If you have a publicly accessible PHP instance and still haven’t patched, assume you’re exposed. Patch now, then check for signs of compromise.
Full data and methodology on the OX Security blog:
https://t.co/10IHG6LrlQ