Application allowlisting is the single most effective security control an organization can enforce on open devices. Windows comes with an application allowlisting feature that is included in every commercial Windows version. 1 and 1, sometimes, just equals 2, and that is ok.
Is WinGet actually enterprise-ready? 🤔
Our very own @byteben went DEEP on this one—breaking down what #WinGet gets right, where the gaps are, and how it compares to a curated enterprise catalog.
Fair warning: Ben brought receipts. 🧾
🔗 https://t.co/mzIsEBC9ak
#MSIntune #Intune
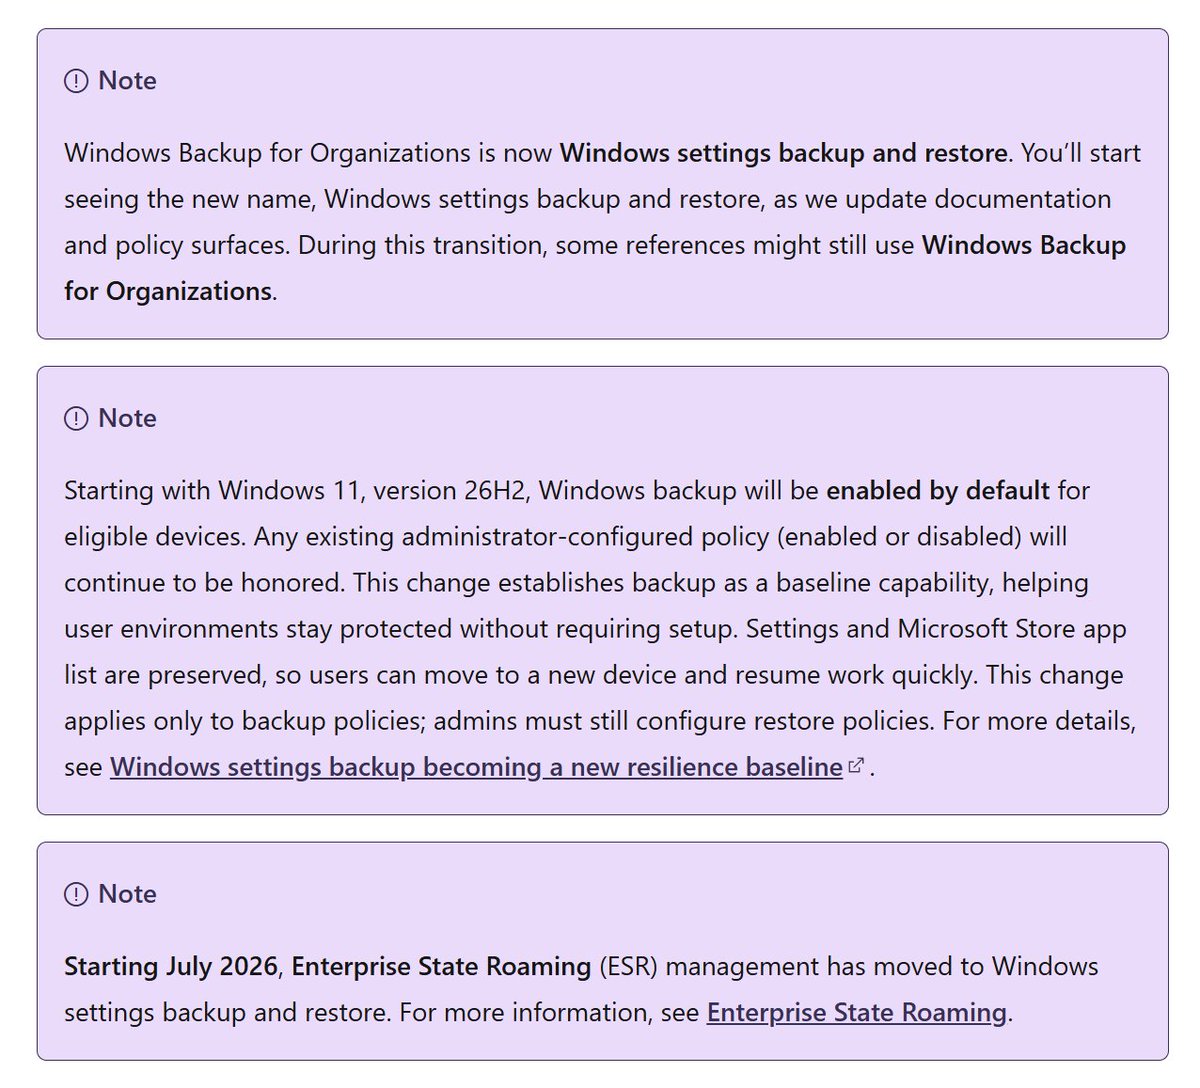
They always hide the good stuff in the notes :)
I've always liked Enterprise State Roaming, but many places never enabled it. Now the feature has been superseded by Windows settings backup and restore which will be enabled by default starting with the upcoming 26H2 release 🥳
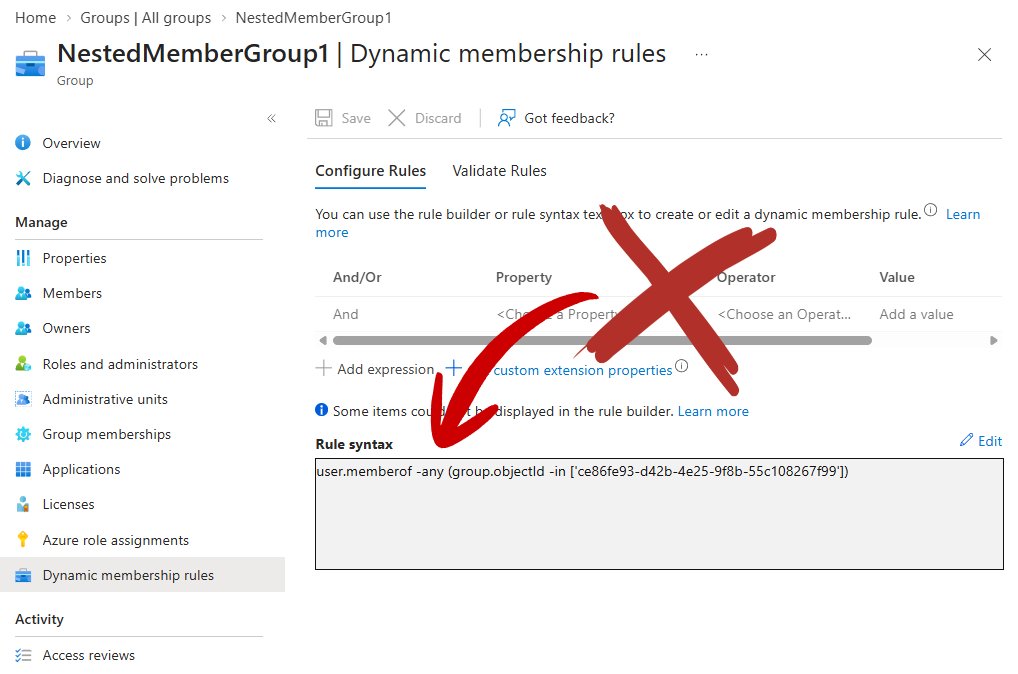
The 𝐌𝐞𝐦𝐛𝐞𝐫𝐎𝐟 𝐫𝐮𝐥𝐞 for dynamic groups in Microsoft Entra will very soon stop working! Read more here > https://t.co/zd7l8Qs8xd
However, this isn't just for groups. It will also impact anyone using the MemberOf rule operator in the following resources:
• Dynamic membership groups
• Dynamic administrative units (AUs)
• Entitlement management auto-assignment policies
• Platforms and services
• Microsoft Entra ID
• Microsoft Entra Groups
• Microsoft Entra Administrative Units
• Microsoft Entra Entitlement Management
For some resources, policies using MemberOf will first be quarantined from 27 October 2026 which will stop any processing. Then after November 3, 2026, any group memberships will stay in their last known state.
#Microsoft #Entra #News
@Senilex@NathanMcNulty@CyberCakeX@magicswordio We have no intend of trying to ram an entire security suite down your throat. We want you to be able to use an enforcement mechanism you're already licensed for. https://t.co/IDMmqbu4p7 helps you in deciding what you want to run at the app leve, not at file metadata level.
@CyberCakeX If you want better management of App Control policies, then I suggest you look at @magicswordio or @Appcontrolai
https://t.co/6UZuF4Zyd5
https://t.co/BjGsEck3dn
Or look at a different solution entirely, because App Control Wizard and Intune are not a good way to do this
#yaacdb Yet another Appcontrol Demonstrated benefit. "The ZIP file contains a Visual Basic Script (VBScript) that masquerades as a PDF document.", didn't think so, that's the end of the line of that attempt, long before any damage is done.
🚨 A malicious Notepad++ plugin is turning the legitimate editor into a malware loader.
CERT-UA links the campaign to Russia-aligned UAC-0099. It establishes persistence and deploys MATCHBOIL.V2 for follow-on malware.
Read more: https://t.co/fZHi21knWz
#yaacdb Yet another appcontrol demonstrated benefit. Loading an unknown dll, didn't think so. No one needs the privilege to run any code coming from anywhere.
Dark Elevator: Windows Install Service Local Privilege Escalation (CVE-2026-50343)
A pure-logic, 100% reliable path from a normal user to SYSTEM on Windows 11.
Full write-up: https://t.co/gFu0ZbhD6d
Tl;Dr Nightmare Eclipse brand new Legacy hive 0-day, reliably stopped by a comprehensive Application Control implementation. Don't get in the crosshairs between this security researcher and Microsoft's vulnerability disclosure handling. Implement Application Control for business (With https://t.co/PxCoHDShtA's assistance), now.
https://t.co/eZSIBTtK69
The most efficient strategy to get there is to build your trustlist by application instead of the typical web of rules to cover everything. https://t.co/IDMmqbu4p7 helps you get there with a vastly reduced worload. Schedule a demo or chat by filling in the account request form.
A proper Allowlisting implementation (analyzing exe, dll and scripts) stops pretty much every threat on Windows endpoints that uses code execution on the device and that is gold to your security posture. Every DfE threat report stopped.
So, you have your allowlisting under control and only allow what is needed? Awesome. Casey released Scan-LolbinPrimitives.ps1 as a reconnaissance tool to bypass your rules by identifying what you've allowed that is subject to 'proxy execution'.
YaACDB, Yet another Appcontrol Demonstrated Benefit or AAFTWA! Application allowlisting For The Win Again. Want a kickstart for your Appcontrol for business projects, https://t.co/kHMtKNjiXz
The AppControl team is present in Norway to promote application allowlisting. We continue to evangelize the need for application allowlisting. #wdac#acfb
This is a weekly reminder that users (nor agents) should hold the privilege to run unvetted code from anywhere. It's the single biggest mistake orgs have made and keep making against the principle of least privilege. The time to start controlling what code to allow is now! #acfb
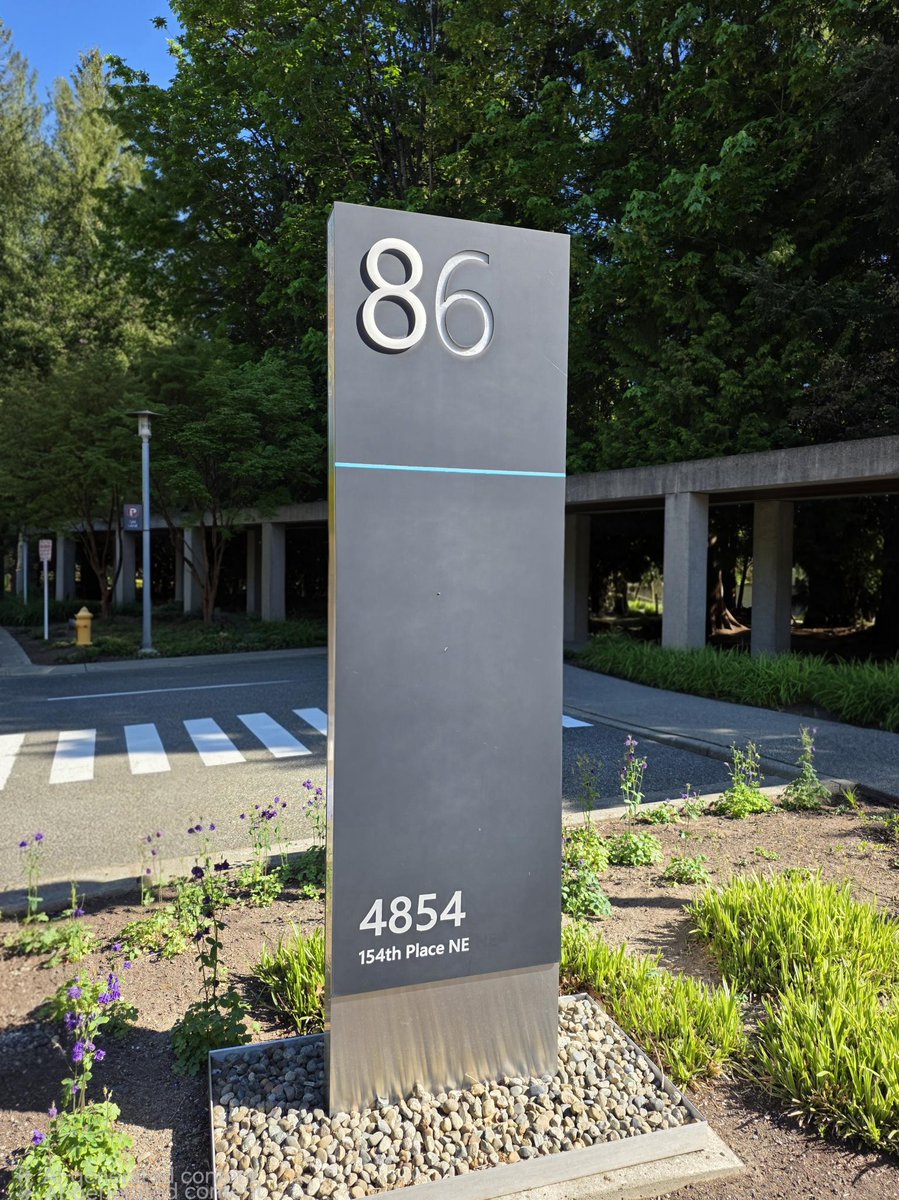
Two of https://t.co/IDMmqbu4p7 's members, @tomdegreef and @TheWMIGuy visited the Microsoft #acfb team on campus this week for the regular in person get-together. Had an interesting morning, learned stuff that will help us build an even better product and make AppControl easier.