TIPS ON HOW TO PROTECT YOUR SOCIAL MEDIA ACCOUNTS LIKE A PRO : use unique passwords, enable two-factor authentication and stay alert for phishing scams or security breach via spamming. #StaySafeOnline#Arden_toolz
Nightmare Eclipse, the person who has been dropping Windows zero-days, has finally decided to share his story. He's an ex-Microsoft employee, we had dinner together, and I've known him and his story for some time.
His real name is Abdelhamid Naceri. He's a very talented and intelligent individual, and he came across as someone who'd be a real professional to work with.
"If only I didn't pour my soul into that job with countless of stupid non sleep nights, i would have gotten over it..." - Naceri
He loved Microsoft.
I wouldn't say that what he did, releasing all those zero-days, was normal, but he felt he had no other option because of the injustice Microsoft did to him.
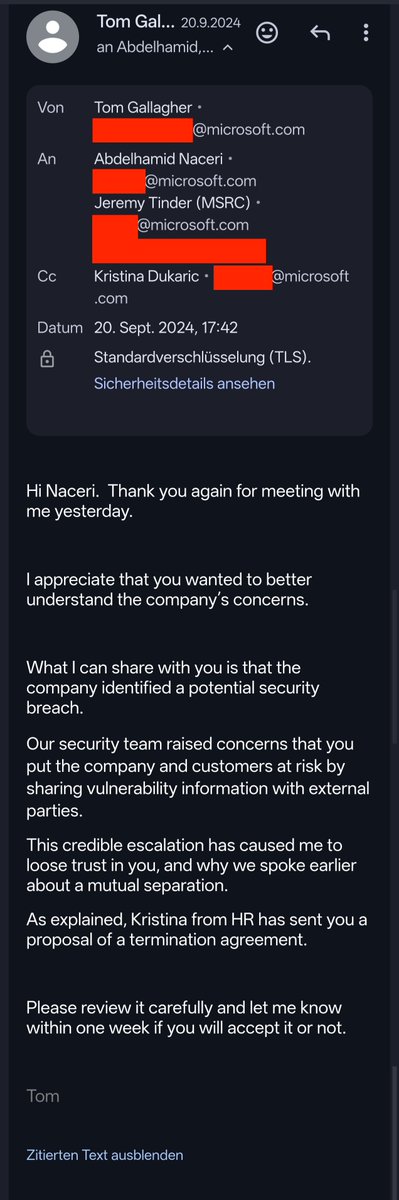
They fired him, and you can read the vague reason they gave in the email sent to him by the Vice President of Engineering at MSRC, below.
According to Abdel's account, VP Tom Gallagher met with him after the firing to tell him they were blacklisting him from Microsoft and writing him a bad reference so he'd never be able to get a job again.
Normally you'd think, well, big deal, just find another job, right? But Abdel doesn't have a European passport, and he was only a couple of months away from getting permanent EU residence.
So instead of granting him those couple of months, Microsoft fired him for a reason that, as far as we can tell, was never made clear, then fought him in court and offered him €55,000 plus a year's pay to drop the case.
All while Abdel was releasing zero-days.
Abdel continued suing Microsoft for unfair termination in Germany, a fight that has cost him over $200,000.
He says Microsoft refused to reveal any details about the security breach and went another direction.
If you are reading this, and you can offer him a LEGAL job, this is his e-mail: [email protected]
📡 Understanding Nmap Scan with Wireshark
🔥 Telegram: https://t.co/upuP8k7Ev3
When performing network reconnaissance with Nmap, Wireshark can capture and analyze the actual packets exchanged between the attacker and the target. This helps security professionals understand how different scan techniques behave at the packet level.
⚡ Scans analyzed in this guide:
🤝 TCP Connect Scan (-sT)
🕶️ SYN / Stealth Scan (-sS)
🏁 FIN Scan (-sF)
🕳️ NULL Scan (-sN)
🎄 XMAS Scan (-sX)
📦 UDP Scan (-sU)
🔍 By examining TCP flags, packet responses, and handshake behavior, analysts can determine whether a port is open, closed, or filtered and identify the scan type used during reconnaissance.
📖 Read the full guide:
https://t.co/pNNiiQAa1f
#CyberSecurity #Pentesting #Nmap #Wireshark #NetworkSecurity #InfoSec #HackingArticles 🚀
🚨 Hinge database allegedly offered for sale on a cybercrime forum, 34M+ unique user records claimed
⠀
Hinge, a dating application operated by Match Group, is allegedly affected by a data exposure after a threat actor advertised what they claim is the platform's complete database containing more than 34 million unique user records.
⠀
The advertised data includes:
⠀
• Full names
• Email addresses
• Phone numbers
• Dates of birth and ages
• Gender and pronouns
• Sexual orientation
• Cities, states and countries
• Ethnicity and religion
• Political preferences
• Drinking and smoking information
• Marijuana and drug-use preferences
• Children and family plans
• Dating intentions and relationship preferences
• Education and employment information
• Profile prompts and answers
• Account and verification status
• Subscription and billing metadata
• Match, like and profile activity information
⠀
The actor published a sample of the alleged database containing extensive account and profile fields and is offering the dataset for $350 in cryptocurrency.
⠀
The claims and the authenticity, source and scope of the allegedly exposed data have not been independently verified.
⠀
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. https://t.co/281Qjc6p2J
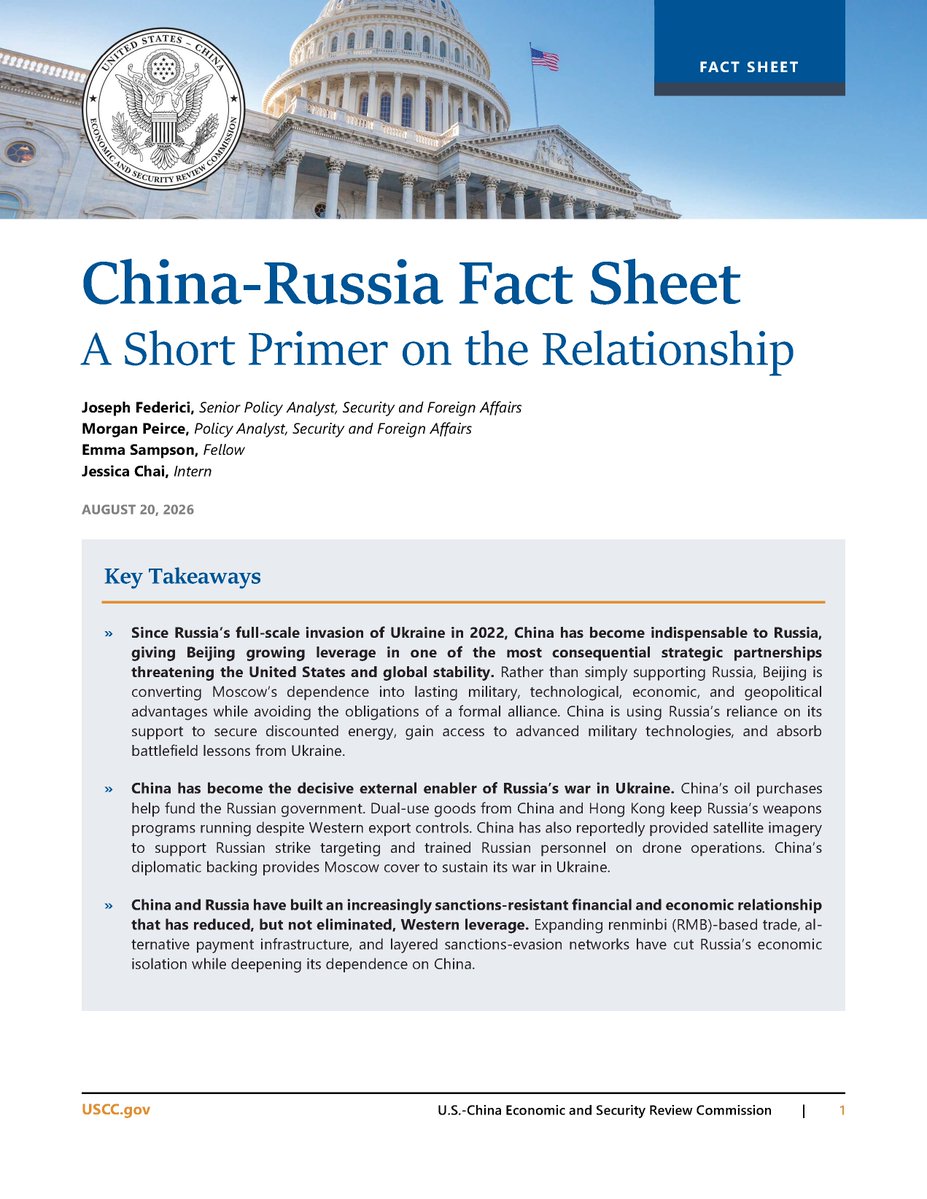
🚨New: China-Russia Fact Sheet: A Short Primer on the Relationship
This resource examines the increasingly consequential strategic partnership between Beijing and Moscow and its implications for U.S. national security and strategic competition.
More👇
🔻 Attackers are exploiting a GitLab flaw days after disclosure.
CVE-2026-19478 lets unauthenticated attackers modify or delete public projects and rewrite their data under certain conditions. watchTowr says it saw in-the-wild exploitation against its honeypots.
Running self-hosted GitLab? Patch now: https://t.co/WlHlqlHApV
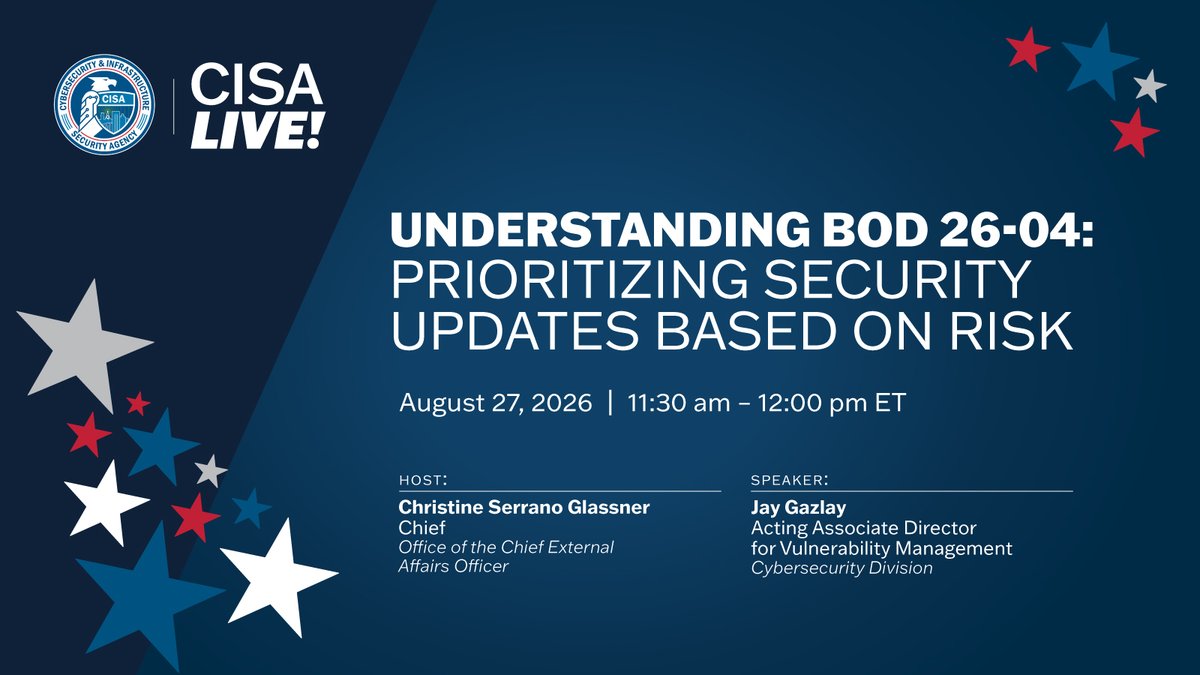
High‑risk vulnerabilities = 🚨 priority! Join us Aug 27, 11:30 AM ET for CISA Live! on BOD 26‑04 to learn how CISA is helping agencies boost resilience with smarter, risk‑based remediation.
https://t.co/sKWRScF89S