Most #security vendors struggle with this kind of attack due to the sender's good reputation and complex link chains. But not us!
🔗Recursive Unpacker + 📷 Object Detection Model: Extracted #malicious URLs at every step, stopping the #threat.
#PerceptionPoint's got you 📷💪
🚨📷 External Vendor ATO Alert!
We intercepted a sophisticated 4-step phishing attack from a compromised vendor account!
Details in the comments on how it worked and how we stopped it!
#ExternalVendorATO#CyberSecurity#EmailSecurity#Phishing
🔍PerceptionPoint blocked the attack at every step:
#VisualSimilarity Engine: detected impersonation in PDFs, websites, and login pages
#ML Content Model: identified the email content as part of a huge phishing campaign using RFQ/RFP with legit-looking hosting site links.
#step4
Final link leading to the #Phishing Login Page🛑:
The office forms link redirects you to another site, which hosts a fake Microsoft login page designed to steal your #credentials.
#step2
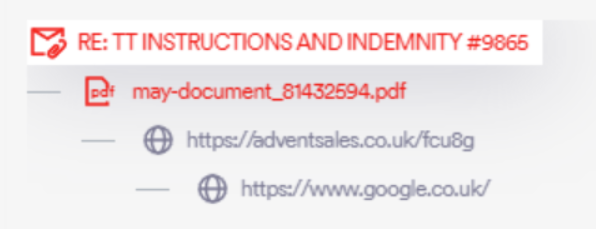
https://t.co/wCxmcxDUMk site link within the PDF 📄: the email includes a PDF attachment.
Inside, there’s a link to an office forms site.
Looks official, right? Wrong.
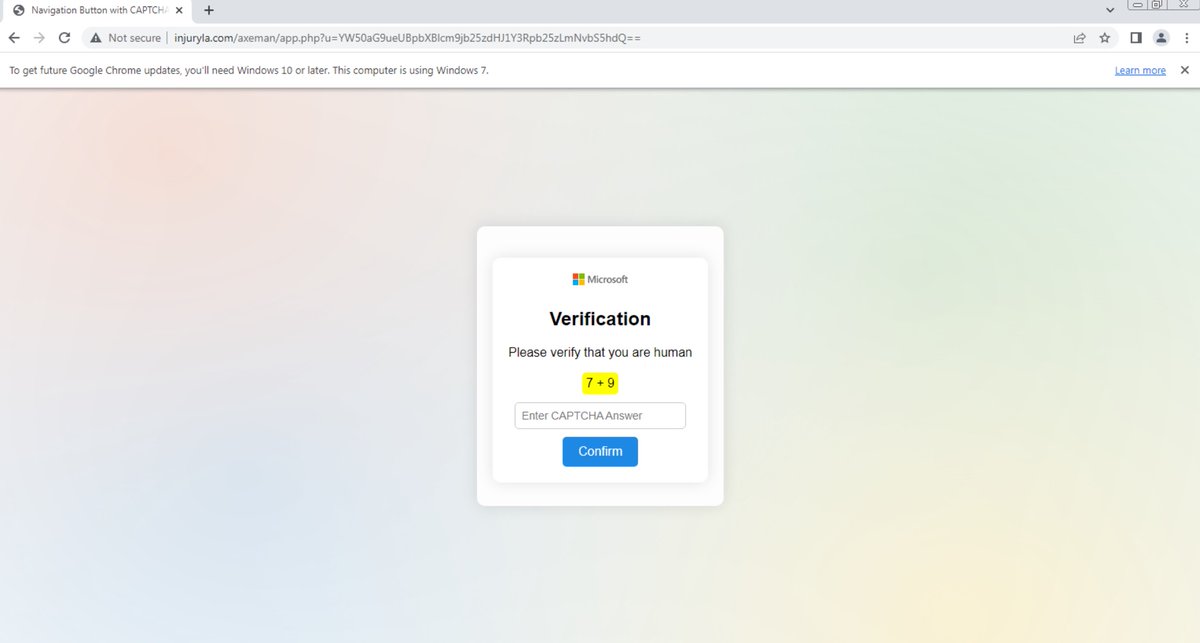
🚨 Attack Alert: Impersonating HR + Fake Microsoft Combined CAPTCHA to dodge security, aiming to steal credentials. Stay alert!! 🚨
An attacker attempted to deceive recipients by impersonating an HR system and sending a false updated timesheet. Details in the comments! 🛡️💪
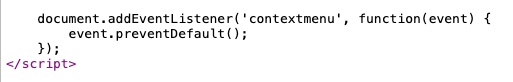
Blocking the context menu prevents users from inspecting or copying code, adding an extra layer of secrecy to conceal malicious activities on the CAPTCHA page.
To ensure success, the attacker disables right-click on the CAPTCHA page, blocking users from inspecting the HTML code for potential clues or security vulnerabilities.
This CAPTCHA mixes both text and math challenges, slipping past security checks, puzzling users, and making it tough for automated defenses to block attacks, allowing the malicious agenda to proceed.
🚫 The attacker poses as HR with a convincing domain to gain trust.
He supposedly emailed about an "updated payroll timesheet," urging quick action. The link led to a fake Microsoft math CAPTCHA.
Perception Point & @pax8 team up to combat evolving cyber threats. Our advanced solutions empower MSPs to mitigate risks in email, browsers, and apps. Learn more: https://t.co/0k6x3IaMAW
Hello everyone,
We are happy to share with you fresh #Darkgate IOCs.
eml > pdf > geofenced URL > jar > ps > zip > autoit3.exe & malicious a3x script
#IOCs:
- afarm[.]net
- adventsales[.]co[.]uk
#malware#threatintel#emailsecurity
3/4
Autoit3.exe (Not necessarily malicious as the script the it runs contains the malicious code) -
MD5: c56b5f0201a3b3de53e561fe76912bfd
SHA256: 237d1bca6e056df5bb16a1216a434634109478f882d3b1d58344c801d184f95d