We discovered CVE-2026-101767, an unauthenticated SQL injection in #Oracle E-Business Suite that chains to remote code execution. Fixed in Oracle's October CPU. Technical details to come later.
Indicators of Compromise:
🔹 Unauthenticated POST requests to /OA_HTML/AppsTCFServer that instantiate the Gantt data-server class (oracle.apps.jtf.gantt.server.GanttDataServer), followed by backend database activity.
🔹 SQL reconnaissance shortly after unauthenticated web requests (database version, current user, directory objects).
🔹 Unexpected files in $APPLPTMP and the oracle account spawning /bin/sh via the Concurrent Manager to run OS commands.
‼️ URGENT ‼️ Two CRITICAL, unpatched PHP flaws (CVSS 9.2 each) have triggered an emergency warning after alleged exploit details surfaced online.
Researchers report potential RCE.
CVE-2026-109618 and CVE-2026-109619.
Fixes scheduled for October 21, 14:00 UTC.
Details - https://t.co/jYegMlTtf2
NetNTLMv1 is dead. Long live NetNTLMv1. 🌈
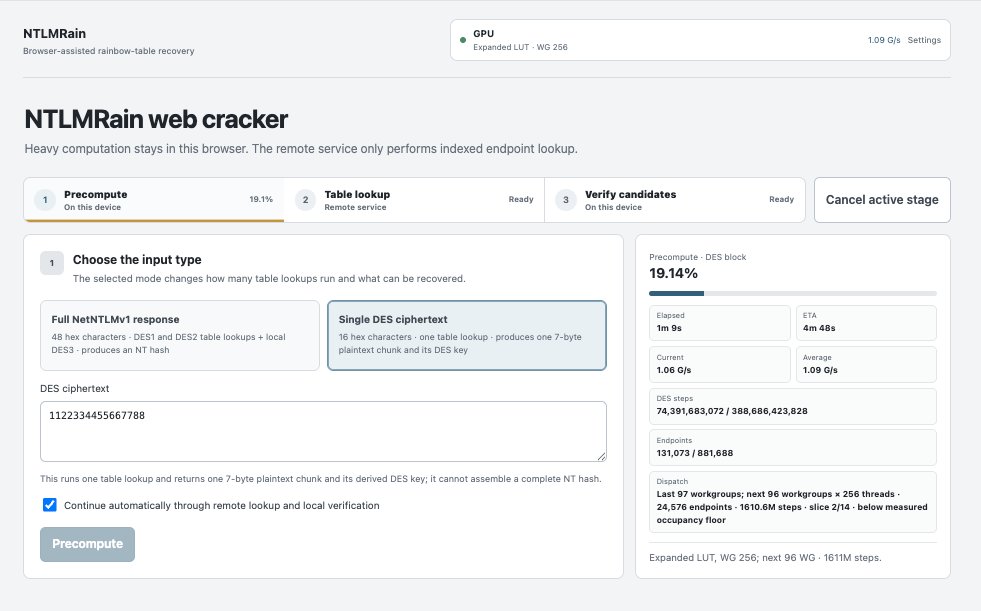
Today we're releasing NTLMRain: recovering NT hashes from NetNTLMv1 responses.
🌐 Browser-based cracking
⌨️ Cross-platform CLI with GPU/CPU support
💾 Searchable tables that fit on a 4 TB disk
Read the blog: https://t.co/fnNqGzJ9O0
I've seen a lot of Active Directory environments in the last 5+ years. These are some of the most dangerous issues I recommend reviewing and addressing in your environment.
Treat it like a check list.
If you have 0 of these, you're doing a great job. https://t.co/xOJN8qRe5X
Today we are disclosing the technical details of CVE-2026-9586, a SQLi-to-RCE in #Sangoma#Switchvox which we reported in April 2026.
On 30 Aug 2026, we received honeypot alerts of valid exploitation attempts across multiple internet sensors deployed in coordination with @DefusedCyber.
Check out the details and IoCs in our latest blog:
https://t.co/YhUIOZvEfl
IIS AppPool RCE is not the end of the story.
AppPool hits AD CS RPC → Windows promotes it to the machine account → Machine cert → TGT → S4U2Self admin. no Potato required.
https://t.co/3fgCjnYBs9
#ADSecurity#ExploitDev#InfoSec
New to BSides Canberra in 2026: Black Box Zero.
Can you unlock the final box? Solve ciphers, hack web apps and manipulate NFC tags in this three-stage physical challenge running Friday in the Locksport Village.
Details: https://t.co/GyLFbcZWAT
Check and patch your Wordpress instances and implement WAF rules in the interim if you cannot.
Yet another excellent bug dropped in the same week by the SLCyber team.
https://t.co/W7Pj5qtRUU
Our research team discovered a critical pre-authentication RCE inside ServiceNow by bypassing their scripting sandbox (CVE-2026-6875). You can read more here: https://t.co/JcHvB3V1rN
CVE-2026-0265, the PAN-OS auth bypass (when Cloud Auth Services are enabled) was fun to reproduce and load into the watchTowr Platform.
Our friends @ @HacktronAI are publishing their analysis this week, so we won’t be publishing. Looking forward to it 🚀
Our security research team discovered a pre-authentication arbitrary file read as root in cPanel (CVE-2026-29205) — a path traversal in cpdavd that we made exploitable by abusing Dovecot's + alias handling to create attacker-controlled directory names on disk.
We've updated cpanel2shell-scanner to cover both issues. Writeup and tool in replies.
👇
someone at ANTHROPIC just showed CLAUDE finding ZERO DAY vulnerabilities in a live conference demo
claude has found zero day in Ghost, 50,000 stars on github, never had a critical security vulnerability in its entire, history...
it found the blind SQL injection in 90 minutes, stole the admin api key, then did the exact, same thing to the linux kernel
🚨 Google told devs: API keys aren't secrets. Gemini changed that.
😱 We found ~3,000 public keys silently authenticating to Gemini - exposing private files, cached data & charging for LLM usage
💥Even Google's own keys were vulnerable.
🔗 https://t.co/UYRE9uCozc
If you're at BSides Ballarat this Saturday at 4:30pm, new to the Industry and looking for an understanding on the different types of roles in InfoSec, stop by and have a listen to our very own Lyal Collins, as he gives a quick overview of skills and career paths in IT Security.
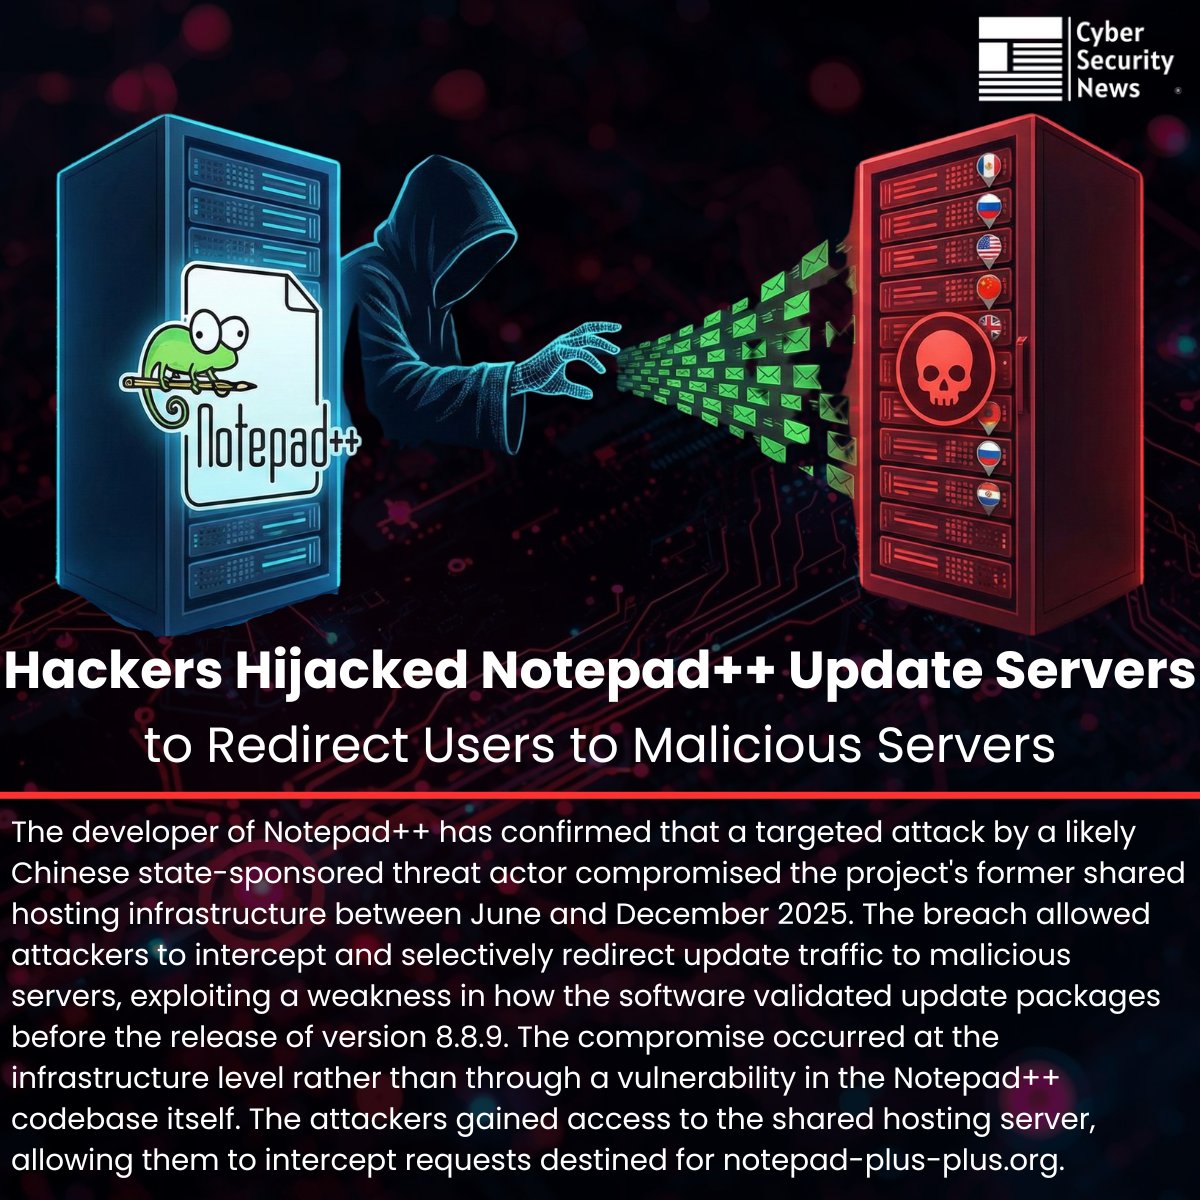
⚠️ Hackers Hijacked Notepad++ Update Servers to Redirect Users to Malicious Servers
Source: https://t.co/nVUozNndDu
The developer of Notepad++ has confirmed that a targeted attack by a likely Chinese state-sponsored threat actor compromised the project's former shared hosting infrastructure between June and December 2025.
The breach allowed attackers to intercept and selectively redirect update traffic to malicious servers, exploiting a weakness in how the software validated update packages before the release of version 8.8.9.
The compromise occurred at the infrastructure level rather than through a vulnerability in the Notepad++ codebase itself. The attackers gained access to the shared hosting server, allowing them to intercept requests destined for notepad-plus-plus[.]org.
#cybersecuritynews
Today we are disclosing the details of CVE-2025-64155, an unauth argument injection leading to root remote code execution affecting the Fortinet FortiSIEM.
Find the technical details, indicators of compromise, and proof-of-concept exploit in the blog.
https://t.co/b6kzNUYlJF
There is critical vulnerability in React Server Components disclosed as CVE-2025-55182 that impacts React 19 and frameworks that use it.
A fix has been published in React versions 19.0.1, 19.1.2, and 19.2.1. We recommend upgrading immediately.
https://t.co/kue7kd0XEX