Telegram shipped a "sandbox" for HTML widgets in messages. It's an in-process QuickJS (C) interpreter on a thread...
No fork, no isolatedProcess, no seccomp anywhere in the tree, so any QuickJS exploit is enough to gain full control with whatever privileges the Telegram client is running as without the need for any separate sandbox escape
The bug is a UaF in the interpreter, from standard JS:
```js
class D { [Symbol.dispose]() {} }
const d = new D();
let leak;
class C { static {
for (await using x of [d, d]) leak = () => x;
}}
// ... run anything ...
leak() // reads a freed frame
```
The fix for this particular vuln is still just in the master branch, and considering the number of vulnerabilities QuickJS has had in the past, this vuln will surely not be the last...
At DISC 2026? https://t.co/AE20tju8oD - Reach out if you'd like to chat about Dragos research and runZero product things! Great talks and an amazing community of defenders. I'd post photos/highlights, except its not that kind of conference, and you have to be here to see them.
Trying to scan for the https://t.co/JqAqPRbonZ authentication bypass? SSHamble v0.5.0 has you covered, with a helpful PR from Paul Asadoorian (@securityweekly)! Code at https://t.co/kVrGa1qwKb (with a bonus CoreOS check and Dockerfiles to validate both issues end-to-end)
We escaped AWS Firecracker. 🔥
We discovered a VM isolation vulnerability affecting versions 0.23.0–1.16.1 when restoring snapshots using the File memory backend with balloon or virtio-mem devices.
Fixed in 1.16.2 and 1.17.0+ (CVE-2026-122192)
Technical write-up:
https://t.co/hUU184cJyA
Good news! We've wrapped our initial "Lights Out" research into out-of-band management devices and BMCs. The final advisories are live and OOBscan now includes detections for all issues. The bad news: many of these issues still have no patch:
https://t.co/MIPYHjPxrP
hands down the best talk I’ve ever seen. the slides are public now.
- Calif got permission from @openai to discuss working with the (unreleased) “astra-cyber” model
- researchers are struggling to believe some of these exploits are real
- 0/1-click exploit development is possible in ~3 hours (with the right prompting, skills, and primitives)
- the world is changing faster than expected
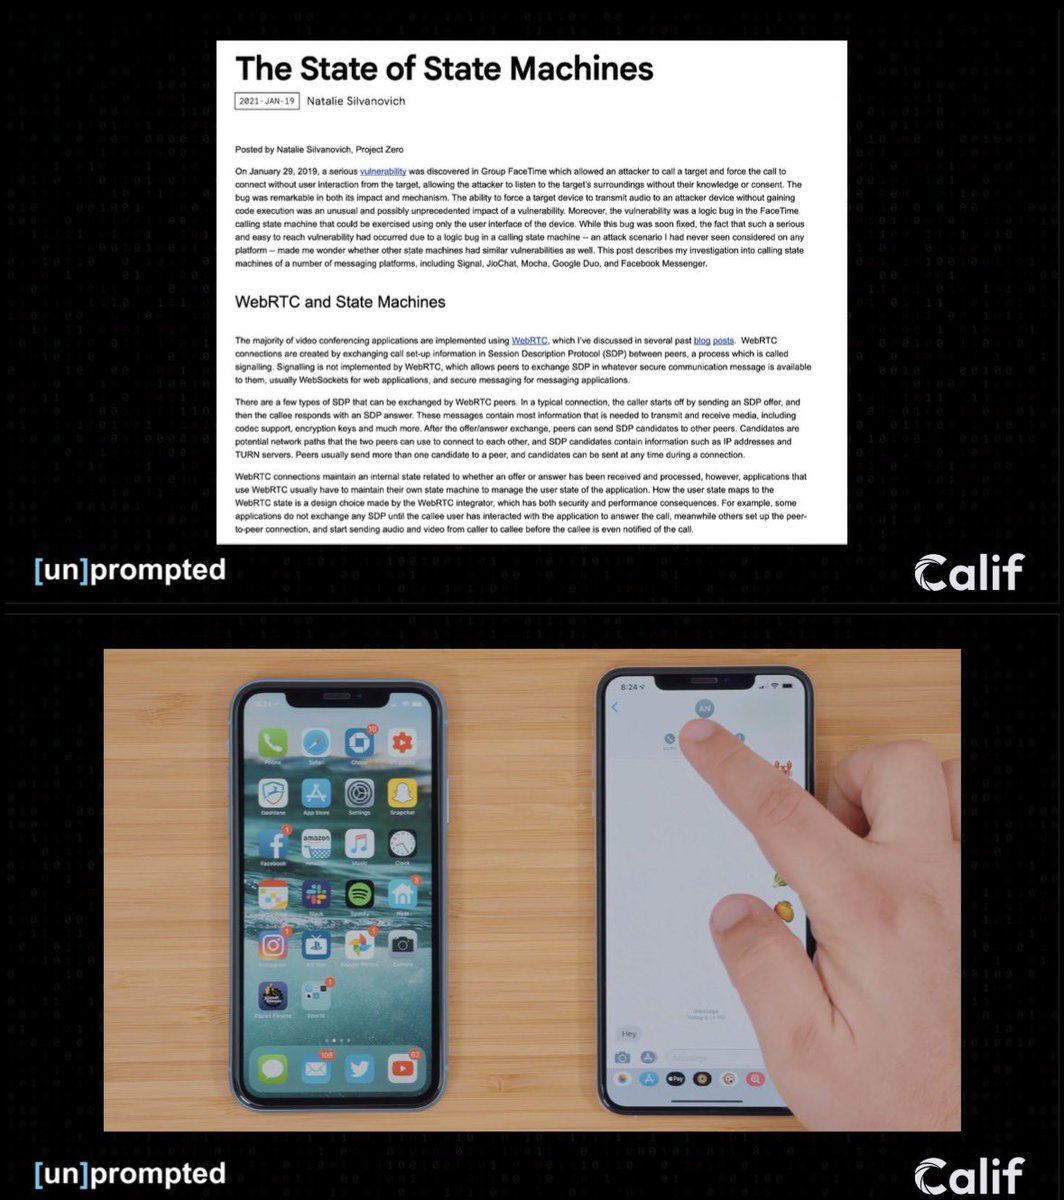
I also loved the shoutout to the 2019 group facetime bugs and @natashenka’s FT work. everyone who worked on that will remember it forever ❤️
thank you so much for the presentation! @pwnlambda@brucedang@calif_io
- They pulled credentials from inside their app's container and used them to request every secret on the platform: ours and every other customer's.
- They tried our cloud provider's metadata endpoint, the standard way to steal credentials for the host a container runs on.
- They asked the cluster what those stolen credentials were allowed to do.
- They went looking for our databases and caches by guessing their internal names.
- They port-scanned our whole internal network, all 65,536 addresses, twice.
- It was about 24 commands over 15 minutes, done on purpose and scripted. No app was ever run.
- Every attempt was blocked. Nothing was accessed.
Code-execution flaw in UEFI firmware affects most servers on planet Earth: https://t.co/JPF82ONwaj
Great work by Alex Matrosov (Anthropic) and Dan Holmes-Mitra (Google)!
Python's certifi package provides the trusted root CAs for a huge portion of the Python ecosystem. It's also a great example of how complex dependencies can get. Ultimately, these certs are sourced from Mozilla, but they go through 5 hops to get there:
https://t.co/BH77y7dqSU
For the next few months, we are looking at frequent discoveries of long-standing bugs - competent code auditing has gotten cheap and abundant. This carries a few consequences:
@halvarflake Also, once a vuln has been announced but not patched (eg. PHP RCE), everyone's got an electron-tunneling microscope to point at the codebase. The old ways of embargo and coordinated disclosure are more perilous.
In a world of AI slop blogs, presentations, images and write ups...
Calif is an excellent example of how to harness it correctly. Accuracy, Art, Asthetic all supporting excellent AI assisted research. 👏