Coinspect is now a Ledger security audit partner for Ledger wallet apps!
As one of Ledger's approved audit partners, we bring our crypto and embedded security expertise to help developers find and fix vulnerabilities before release.
Building a Ledger app? Let's talk.
Formal verification doesn't replace adversarial testing.
seL4 17.0.0 fixed critical crashes in verified configurations. The proofs weren't broken. The CPU model left registers out of scope.
We see the same pattern in sandbox research: strong cores, but security gaps at the boundaries.
1/ AI is finding bugs faster than we can patch them, we hear "formally verify everything" more and more. So let’s look at the most verified kernel in existence, seL4, and what its latest release (Oct 30) fixed. 🧵
BlockThreat - Week 45, 2026
📈 $53.2M stolen across 13 incidents. Only four touched smart contracts and they cost $1.4M
🔑 Signing and payment rails are the target now:
- Mercado Bitcoin ($48.6M) - Signed withdrawals
- Web3Authn ($1.82M) - Key derivation
1/ AI is finding bugs faster than we can patch them, we hear "formally verify everything" more and more. So let’s look at the most verified kernel in existence, seL4, and what its latest release (Oct 30) fixed. 🧵
🚨 Massive GitHub Actions CI Secret Stealer
4,800+ compromised accounts attempted to push malicious workflows to 61k+ repos. Payload dumps all CI secrets, memory, OIDC & commit secrets, then instantly deletes run logs.
Search your repos for:
• PR: "docs: dependency audit notes"
• Branch: wfx-docs or chore/
• Commits: "ci: refresh build cache" or "chore: add ci helper"
• Actions tab: Skipped/missing run numbers
If hit, assume total compromise. Rotate ALL secrets and cloud roles immediately.
Time to level up mobile wallet security.
With worse_query exposing application files, many wallets are proudly reminding users that their seeds are encrypted. But encryption with a password-derived key is the bare minimum, not a security achievement.
Research shows that users tend to choose weak passwords, particularly on mobile devices.
Once an attacker obtains an encrypted seed file, they can attempt to crack the password offline. Weak key derivation makes this even easier, as we've seen with stolen password manager vaults.
Both iOS and Android offer stronger protections, including hardware-backed key storage. Wallets should use these mechanisms.
At Coinspect, through our Wallet Security Ranking and WSF work, we want to help raise security standards across the ecosystem.
Welcome to Hotel Calif. We're in lockdown mode. You can check in, but you can never leave. Broccoli is served around the clock.
The Brotli bug apparently affected iOS and macOS too. Apple released version 27.2.1 yesterday, fixing this bug among other security issues.
This is an important security update. If you haven't updated yet, now's a good time. The demos show what we were able to do with it.
A dApp frontend can serve malicious code to one user while everyone else sees the real site.
dappFence helps developers prevent this using cryptographic integrity checks.
No extension. Works on mobile. Free & open source.
Alpha. We need developer feedback to shape it!
https://t.co/CatLnBu4zu
This is why hardware wallets exist.
Using a iOS 0day sandbox escape to steal software wallets through widely distributed malicious apps was historically expensive. The value of each wallet is unknown, and distributing the exploit risks exposing it.
A public, unpatched sandbox escape changes that equation.
1/ worse_query: unpatched iOS file system sandbox escape with a public PoC on GitHub.
Malicious app can silently get access to other app private files. No jailbreak.
The exploit looks sadly familiar. Remember all those Unix LPEs involving symlinks in /tmp?
Another supply-chain attack: compromised bee-js and Swarm Desktop releases steal wallet keys and install persistent backdoors.
The npm package had valid provenance. The official release workflow published malicious code without branch review or tests.
Provenance proves origin, not safety.
BlockThreat - Week 44, 2026
North Korea just hit @Binance for $6.36B, the largest heist in history. They now stole more this year than all past years combined.
Many people have a shallow understanding of what Rust actually guarantees. The borrow checker is great for ensuring memory safety *within an application*, the guarantees for multi-process interaction (and even interaction with shared libraries etc.) aren't the same thing.
Important work by Report URI.
Malicious JavaScript is a growing underestimated threat: it can steal passwords, credit cards, bypass strong MFA, and drain wallets.
Sometimes without anyone noticing for months.
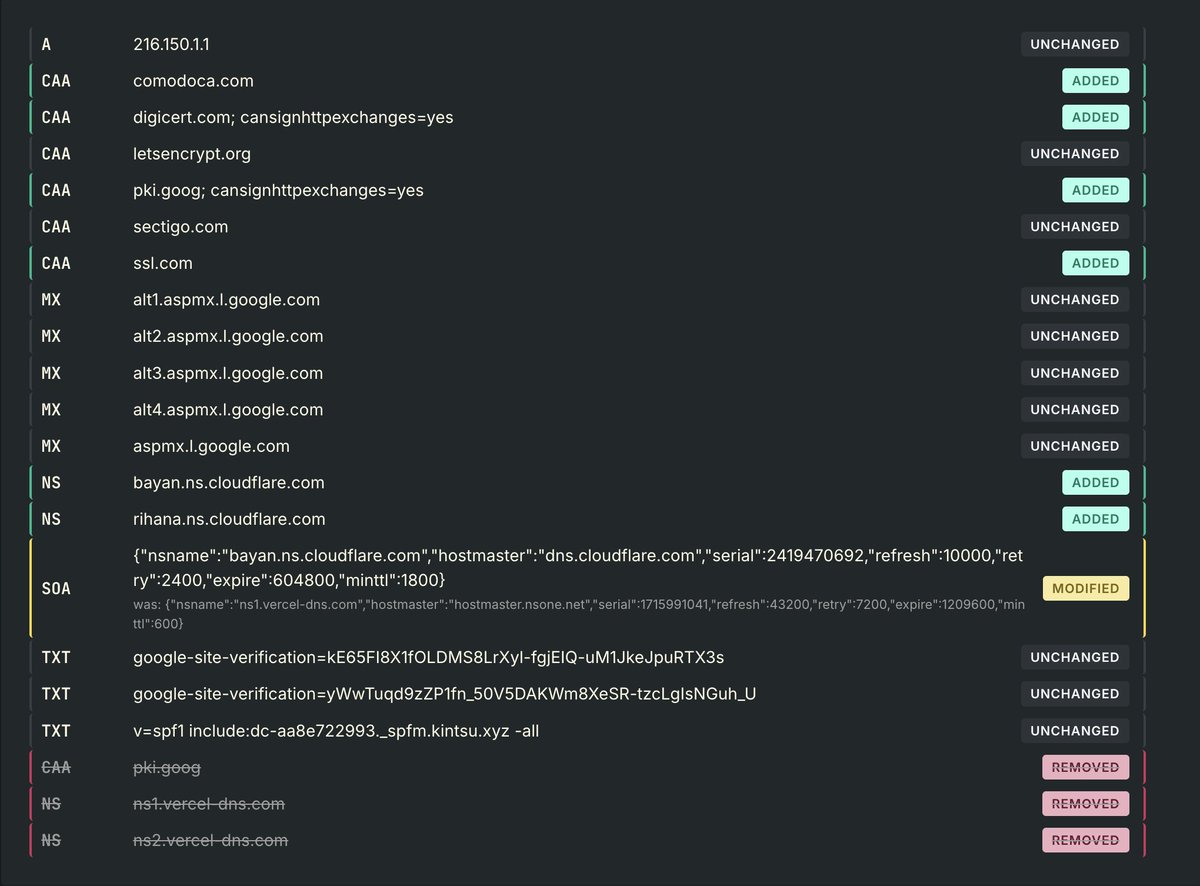
dApp frontend hijacking update:
✅ all 15 affected domains recovered.
But the attacker keeps:
13 DNS zones at Name com still point to 31.56.52.52
13 TLS certificates remain valid until January 29, 2027.
1 server online
What happened and how we confirmed it: 🧵
Two details explain the 13 certificates:
perena[.]org: its staged zone pointed to parking, not the attacker.
dooar[.]com: DNSSEC prevented the attacker from obtaining an ACME certificate.
CAA didn' t help Origami[.]finance, the attackers DNS zone simply omitted it.
We'll post about the wallet drainer payload next and how they used Irys (linked to attacker' s wallet) and what that reveals. Follow @coinspect !!
dappFence uses standard web technologies: Service Workers and signed integrity manifests.
No extensions required. Works on mobile browsers.
Users with a previously trusted manifest can remain protected 24h after a compromise.
Next: stronger protection through browser, wallet and extension support.
PQ security matters. But Web3 still ignores Bybit's hack fundamental lesson: blind trust in frontends.
Clear signing helps, yet DNS, third-party JS, and deployment pipelines remain critical attack surfaces as AI accelerates exploits.
dApps can improve frontend security now:
Frontend security cannot wait for the perfect signing UX.
Reduce trust in third-party JavaScript, monitor changes, and protect the code users interact with.
We are building dappFence, an open-source free tool to enforce security rules on web frontends:
https://t.co/5vFUm8J1VR