Not a bad Sunday.
Was hanging out in the @SyndicateGameHQ Discord, got talking with @nftimm, and he gifted me a 7-day Pass+.
> cracked one Rebirth+ pack
> pulled a LEGENDARY first try
> Trina Time, #184/195
I'm hooked! Glad I got into solana:syQqkspvb2PRr1meJ5pJDmhgxwc4hUou2TMjjrTmeta on the @backabledotbiz raise 🕴️
solana:DNhQZ1CE9qZ2FNrVhsCXwQJ2vZG8ufZkcYakTS5Jpump has lived 10 months in a space where most things don't survive 10 days.
My thesis is simple. AI has revolutionized the world of cybersecurity, and you can bet on this revolution with @zauthinc.
zauth has found vulnerabilities affecting millions of people in the web2 world, alongside hundreds of thousands of dollars in smart contracts exposed to drains.
zauth has hundreds of customers, enterprise contracts, and is building a real company; a startup spawned from a fair launch.
There is nothing like zauth. From the product to the team to the token.
I am not wrong. Just early.
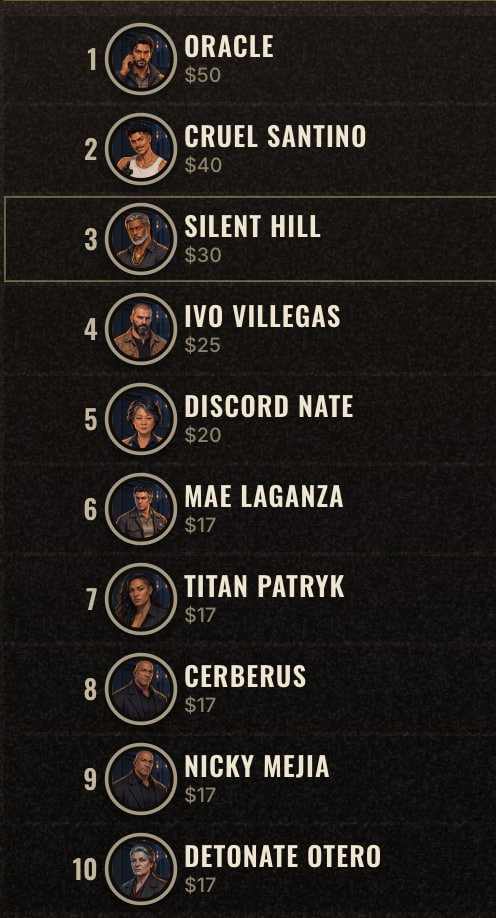
FRESH BLOOD LEADERBOARD IS LIVE AND COOKING.
These USD prizes are JUST for new players... no competing again long term grinders.
Just sign up, and win up to $50 this week just for playing @SyndicateGameHQ.
You know what to do https://t.co/rOlGi5VE9f
The world doesn’t need another meaningless token.
It’s time to own the game you play.
Introducing $GANG.
The Syndicate ICO launches on @backabledotbiz this Wednesday, October 7.
Proud to publish this one.
84 findings. 7 rounds. 5 days. 0 remain open.
https://t.co/VOe7shfc87
After a whitebox review of their npm packages and dashboard payment code, every vulnerability found has been remediated.
In three years the ability to find and exploit vulnerabilities went from a sophisticated few to everyone.
Offense got the upgrade, but defense did not.
This is why zauth exists. Agents that break into your systems the way the new attackers will, before they do.
We found a vulnerability in Dragonfly, a database downloaded over 25 million times. It affects every release up to and including the latest one.
Apps use it as their short term memory. Anything that needs to load instantly lives there instead of a slow database.
Dragonfly had three ways to take in data and only checked one of them properly. One malformed file through either of the other two could crash the server and wipe everything in memory, or trick it into leaking pieces of its private memory. The leak worked 19 out of 30 times.
Project Apex, our public security initiative, found it autonomously.
If you run Dragonfly, set a password until the patched release ships.
The zauth advisories section is live.
Every vulnerability we've found and disclosed, in one place.
Two are up now, with many more disclosures waiting on remediation.
https://t.co/cBISfRHjP1
zauth has been accepted into @AnthropicAI's Cyber Verification Program.
Our mission is to provide the best, accessible cybersecurity to the next generation of builders.
This is exactly what we'll do.
Vulnerabilities are in every crevice of the internet, from web3 to banking to healthcare. Pre-AI they were much harder to find, but this revolution gave attackers exponentially better tools.
Defense has improved at the same rate, but it has to be sought out. The standard Charles is describing is the right one.
zauth runs authorized-scope only, and we take disclosure very seriously.
We find on average 15 vulnerabilities, priced between $49 - $150 a scan.
Completely autonomous, no sales call or meeting. Protect your business today.
Cybersecurity is a 200 billion dollar industry that still runs on humans billing hours.
A pentest starts at four figures and takes weeks. ours costs pennies on the dollar and runs in minutes.
zauth is a tokenized cybersecurity company.
The incumbents are replaceable.
Caught a released-vs-master patch gap in ProFTPD's mod_sql.c (CVE-2026-42167, CVSS 8.1 High).
The fix existed in master but never got backported to the 1.3.9 release branch, so anyone running the official release was still exposed. We flagged it, and the maintainer confirmed and shipped the backport within a day.
First of many.
We are four days into Project Apex and we have already disclosed two critical vulnerabilities in software that many users and companies depend on.
--
The first is a SQL injection in a widely deployed file transfer server, running on roughly 160,000 machines currently exposed to the internet, and it requires no account or credentials of any kind to reach.
The fix already existed upstream, but had simply never been carried into the release branch that people download, so every administrator on the current stable version was exposed while the patch sat on a branch they had no reason to look at.
The maintainer is patching it now and we will publish the full proof of concept once that lands.
--
The second is a remote code execution vulnerability in a widely used open source platform with 70,000 downloads, reachable with no login, no password, and no action required from anyone at the target company.
It is reported and we are still waiting to hear back from the company.
We are holding both names until the fixes are in shipped releases and users have had a chance to update.
--
Both findings came out of Vector, our agentic pentesting engine we spent eight months building. Until four days ago it was private, run only on businesses that came to us directly. Now it is pointed at open source code across the internet
This is the tip of the iceberg.