@barcodevsf Not really about the game starting. A regular user shouldn’t be able to control which kernel driver the anti-cheat service loads. That’s the real problem.
1/7
After months of research, I found a logic flaw in EasyAntiCheat: a standard user can control which older signed EAC driver its SYSTEM service loads into the kernel.
Reported almost a year ago, rejected, and still reproducible.
Demo: 2022 and legacy 2017 drivers loaded and running.
7/7
This finding illustrates the distinction between verifying who signed a driver and verifying which driver a privileged service should load.
I’m sharing the implementation and reproduction details for other researchers to examine.
PoC: https://t.co/4Emvd0kwNO
6/7
Where this leads next is still an open research question. Exploring further impact requires a deeper understanding of how the older drivers initialize, interact with the current service, and which functionality remains accessible after loading.
@Salsa12__ Cool to know the password goes through CredProvDataModel's WinRT layer now. unsigned DLLs still load into logonui by design, windows being windows..
الحمدلله
أنجزت شهادة OSCE³ من @offsectraining
من أعلى وأصعب الشهادات في مجال الأمن الهجومي، تشمل:
OSWE – OSED – OSEP
رحلة طويلة مليئة بالتحديات التقنية والتفاصيل العميقة
فخور جدًا بهذا الإنجاز
#osce3
الكثير من الناس عنده مفهوم ان الملف الضار لازم يتم تشغيله (Executed) عشان يسبب الضرر الخاص فيه ,
اليوم بوريكم وبشرح كيف نقدر نستغل طريقة عمل الWindows وكيف نقدر نسرق الهاش (NTLMv2) الخاص باليوزر فقط عن طريق فتحه للمجلد او تحميل الملف بدون تشغيل اي برنامج خارجي .. مثل ماهو موضح في المقطع:
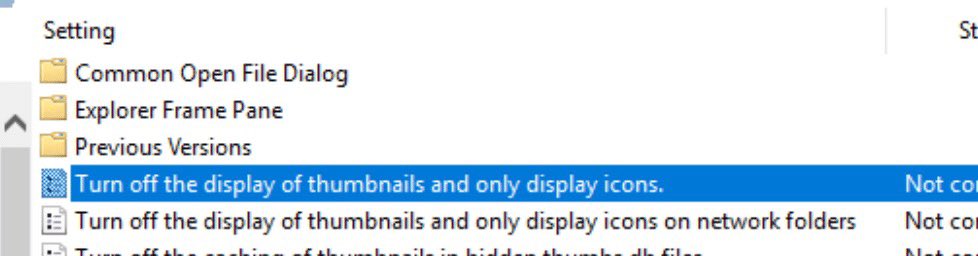
هنا سويت طريقة حلوه بأن الملف خليته في فلاش وخليت الايقونه الخاصه فيه هي صورة pdf كذبيه ، وسميت الملف
test.pdf.library-ms
ولكن مثل ماذكرت سابقاً ان explorer.exe راح يخفي الامتداد حتى لو كنا مفعلين اظهار جميع الامتدادات .. ف بكذا اول ما نفتح الفلاش راح تتم عملية المصادقه من explorer نفسه عشان يسحب الايقونه بدون اي عملية من المستخدم: