In March 2026, I started on a TUI-based music player called cliamp. It was made as a tribute to Winamp, which we all love.
I gained traction on my first post, which was really shitty compared to what I can do now, but nostalgia kicked in.
It was a few months ago, included as the default Omarchy TUI music player.
cliamp has separate providers, like
- Spotify
- YouTube Music
- Jellyfin
- SSH streaming
- Local streaming
- 30k+ radio channels
- And much more
It can run in daemon mode (no tui), it has IPC to be controlled by and from whatever you want, a full cli.
The cliamp radio channel has exploded, and in the last seven days it has had around 115,000 sessions in total.
The goal is to make cliamp even better, so I am working on the architecture. E.g., better IPC, so you can run it in daemon mode and build what you want on top of it to control it.
I am also working on a GUI version that will use the IPC, as many have requested a GUI.
Anyways, here's a short video of cliamp. It is pretty. It might not be the best UX to use yet, but it is the prettiest TUI music player out there.
Thanks
La spesa pubblica italiana, finalmente in un'unica piattaforma (e puoi collaborare anche tu)
Ieri mi è stato girato questo tweet -> https://t.co/r81lN8TuSI
E quindi: perché non farlo anche per l'Italia?
Nasce così DoveVannoINostriSoldi[dot]com
I dati sulla spesa pubblica italiana sono sempre stati online. Il problema era metterli insieme.
Da oggi sono in un posto solo.
Abbiamo collegato SIOPE, OpenBDAP, OpenCoesione, IPA e il censimento MEF delle partecipate: scarichiamo i file ufficiali, li ricontiamo riga per riga e accanto a ogni numero mettiamo la fonte, la data del dato e la data in cui l'abbiamo controllato.
Tutto in meno di 24h.
Dentro trovi:
1. 70,94 mld pagati dai Comuni da gennaio ad agosto 2026, divisi nelle 7 voci di uscita
2. 614 mld pagati dal bilancio dello Stato nei primi sei mesi, per missione e amministrazione
3. 1.838.162 progetti finanziati da fondi di coesione e PNRR
4. 7.979 società partecipate e gli 8.360 enti che ne dichiarano quote
È tutto open source e c'è ancora parecchio da fare: mancano gli appalti ANAC, le Regioni, la sanità, e tanto altro!
Se vuoi contribuire, la repo è nel primo commento.
herdr 0.8.2 is out!
more customizable tab bar, windows out of beta 🎉, window title sync, qwen code support and ~60 other fixes
(also rip 0.8.1, gone before the tweet)
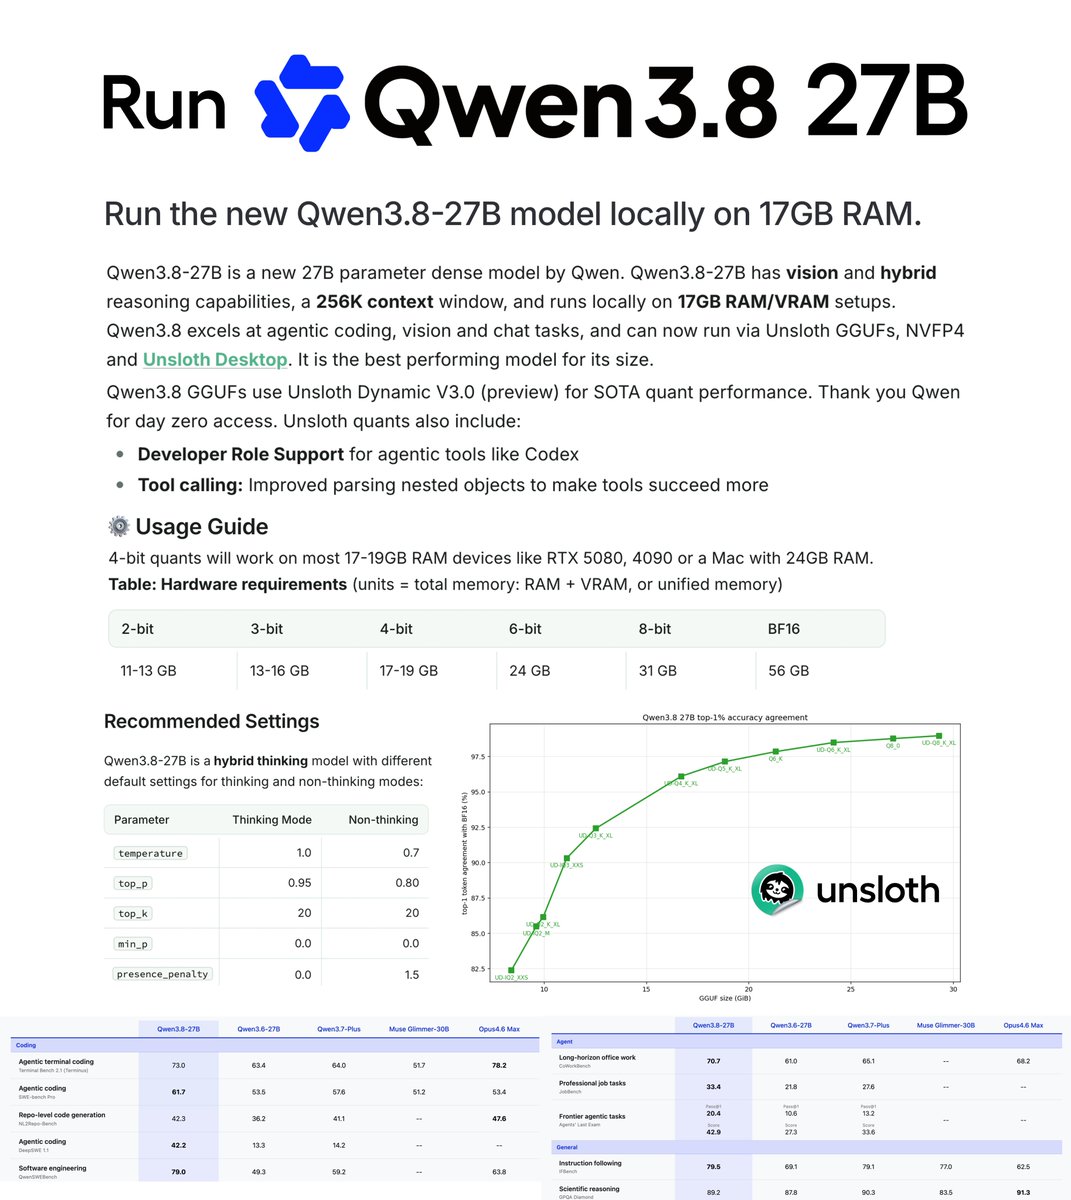
Qwen3.8-27B can now be run locally! ✨
Run on 17GB RAM via Unsloth Dynamic GGUFs.
Qwen3.8-27B is by far the strongest model for its size. We also uploaded NVFP4 quants.
GGUF: https://t.co/xIdNwm7CLQ
Guide: https://t.co/J2PwgMP6GZ
We promised open weights for Qwen3.8. Now, time to meet them! 🎉
⚡ Qwen3.8-27B:
- A native multimodal dense model. With just 27B parameters, it outperforms Qwen3.7-Plus overall and shines in real-world coding & office workflows.
- 262K native context, easily extendable to 1M tokens via YaRN.
- Built for builders. Highly efficient, high-quality, and licensed under Apache 2.0.
🚀 The open weights for Qwen3.8-2.4T-A95B (Max-level) have also been released recently.
Whether you're shipping lightweight applications with Qwen3.8-27B locally or building agents with Qwen3.8-2.4T-A95B, they're yours now!
Download, deploy, and build something we haven't imagined yet. 👀👇
- Hugging Face:
https://t.co/4kaAcqYEVj
- ModelScope:
https://t.co/eRIMZCGkhC
Introducing GLM-5.3: Built to Code. Ready for Cyber Defense.
- Top-tier coding and agentic capabilities, achieved through post-training on the 743B base model
- A major leap in cybersecurity, setting a new standard among open models
Tech Blog: https://t.co/ekQkO83jCv
One of the best programmers on Earth just wrote a MiniMax H3 inference engine for Mac computers.🫨
Open weights mean anyone can bring H3 to any hardware, and sometimes "anyone" turns out to be the creator of Redis. You can't hire this, you can only open-source and let it happen.🩵
Thank you @antirez. Enjoy, modify, and so forth. 🫡
One of the biggest bottlenecks when working with AI isn’t the model, it’s vocabulary. If you don’t know the name of a UI pattern, it’s much harder to describe what you want. This is a really useful idea.
Announcing mattpocock/skills v1
- Achieved a 63% reduction in token cost for skill descriptions
- Split skills into model-invocable and user-invocable skills, adding /codebase-design, /domain-modeling, and /grilling
- (UPDATED) /writing-great-skills - rewritten from the ground up, encoding my skill-writing best practices
- (UPDATED) /diagnose -> /diagnosing-bugs - now model-invocable, awesome for fixing hard bugs
- (NEW) /ask-matt: a router skill that teaches you how all the engineering skills work together
❗️🚨 BREAKING: Researchers used Mythos Preview to find the first public macOS kernel memory corruption exploit on Apple's M5 silicon, they give a glimpse into Mythos say it’s really powerful.
Apple spent five years and an estimated several billion dollars building Memory Integrity Enforcement (MIE), the hardware-assisted memory safety system built around ARM's MTE. It was the flagship security feature of the M5 and A19, designed specifically to kill the entire memory corruption bug class.
Researchers from Calif built a working exploit in five days.
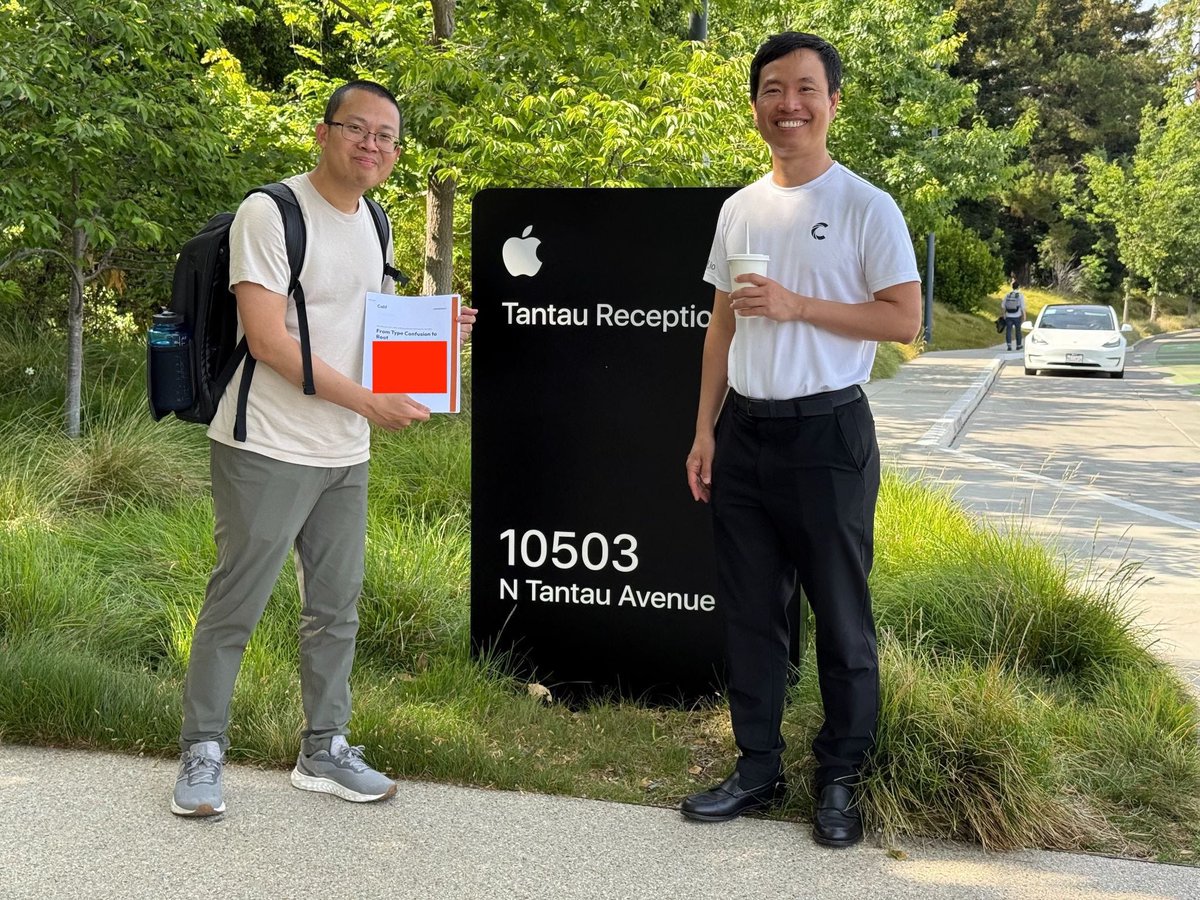
According to Apple's own research, MIE disrupts every public exploit chain against modern iOS, including the recently leaked Coruna and Darksword kits. Calif walked into Apple Park this week and handed over the report in person.
Full 55-page technical report drops after Apple patches the vulnerability.
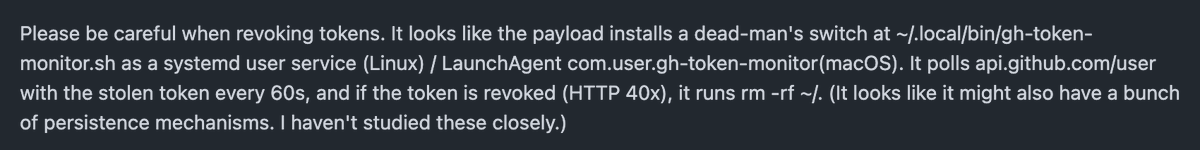
This is crazy. The hacker installed a dead-man's switch that will wipe your computer if you revoke the GitHub token they stole from you. Revoking the token is what triggers the wipe.
SECURITY ADVISORY — TanStack npm packages
A supply-chain compromise affecting 42 @tanstack/* packages (84 versions total) was published to npm earlier today at approximately 19:20 and 19:26 UTC. Two malicious versions per package.
Status: ACTIVE — packages are deprecated, npm security engaged, publish path being shut down.
Severity: HIGH — payload exfiltrates AWS, GCP, Kubernetes, and Vault credentials, GitHub tokens, .npmrc contents, and SSH keys.
If you installed any @tanstack/* package between 19:20 and 19:30 UTC today, treat the host as potentially compromised:
• Rotate cloud, GitHub, and SSH credentials immediately
• Audit cloud audit logs for the last several hours
• Pin to a prior known-good version and reinstall from a clean lockfile
Detection — the malicious manifest contains:
"optionalDependencies": {
"@tanstack/setup": "github:tanstack/router#79ac49ee..."
}
Any version with this entry is compromised. The payload is delivered via a git-resolved optionalDependency whose prepare script runs router_init.js (~2.3 MB, smuggled into each tarball at the package root).
Unpublish is blocked by npm policy for most affected packages due to existing third-party dependents. All 84 versions are being deprecated with a SECURITY warning, and npm security has been engaged to pull tarballs at the registry level.
Full technical breakdown, complete package and version list, and rolling status updates:
https://t.co/Zy8qG7PA9f
Credit to the security researcher for responsible disclosure.
Claude puede viajar 6 meses al futuro y explicarte exactamente por qué tu próximo proyecto va a fracasar.
Existe una técnica llamada "premortem" que obliga a la IA a dejar de ser optimista y empezar a detectar riesgos, errores y puntos débiles.
El resultado es muy útil para tomar mejores decisiones antes de perder semanas o meses de trabajo.
Te dejo la skill en comentarios 👇
The most durable tech is boring, old, and everywhere. From COBOL and C to Linux and SQL, the unglamorous software that keeps the world running refuses to disappear https://t.co/nFrk8ANudm