The DLMM review surfaced 17 findings: 6 Medium and 11 Low/Informational.
Meteora aligned swap estimates with execution and tightened pool-state controls, improving reliability for traders and LPs.
Read the full story 👇 https://t.co/1c17nbhm6S
With $32.1B traded in H1 2026, @MeteoraAG sits at the heart of Solana’s trading infrastructure.
Across 2026, our teams partnered together for 3 collaborative audits.
The focus: trading execution, staking controls and new AMM architecture.
The @aeroxyz Audit Engine engagement is complete!
Security researchers and AI auditors examined Aero's MetaDEX cross-chain and reward systems and Slipstream's concentrated-liquidity pools.
Our first flagship public engagement was a success. Let's look at the outcomes. ↓
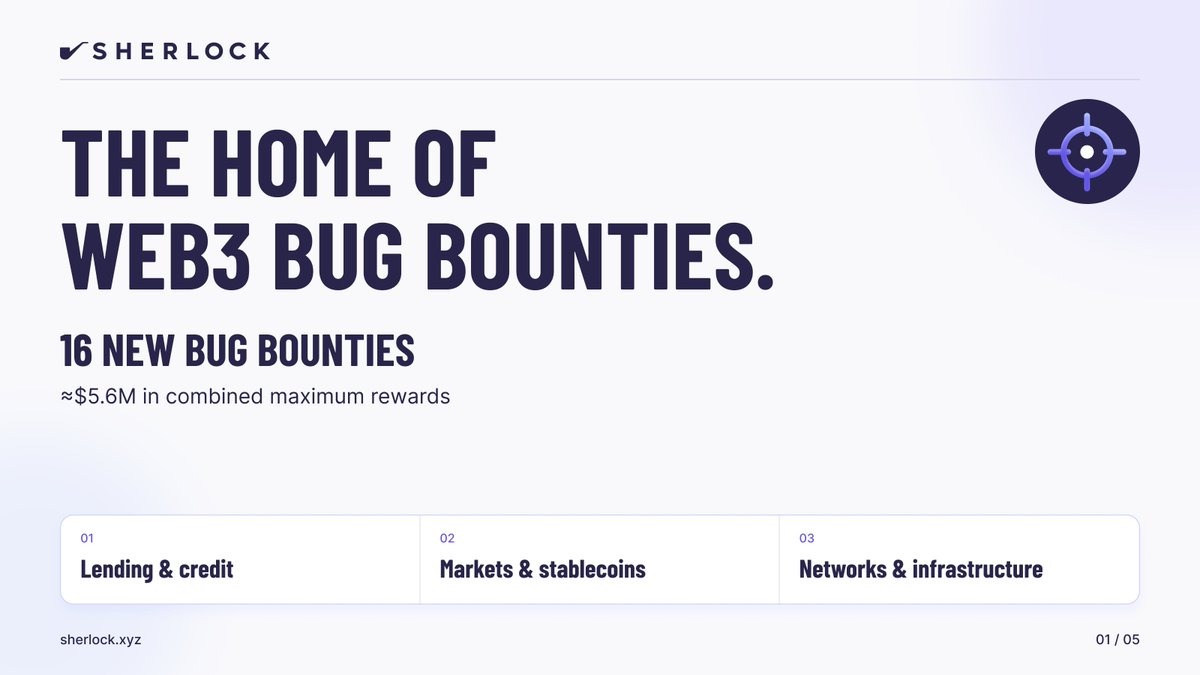
Leading teams are launching their bug bounty programs with Sherlock.
16 new programs. ≈$5.6M in combined maximum rewards.
With immediate triage + escalation from our in-house security team, we believe we’ve built the best bug bounty program in Web3.
Some recent launches ↓
We’ve had the privilege of securing @centrifuge through multiple generations of the protocol.
Proud to be back for V3.3 and to keep raising the bar together as they ship.
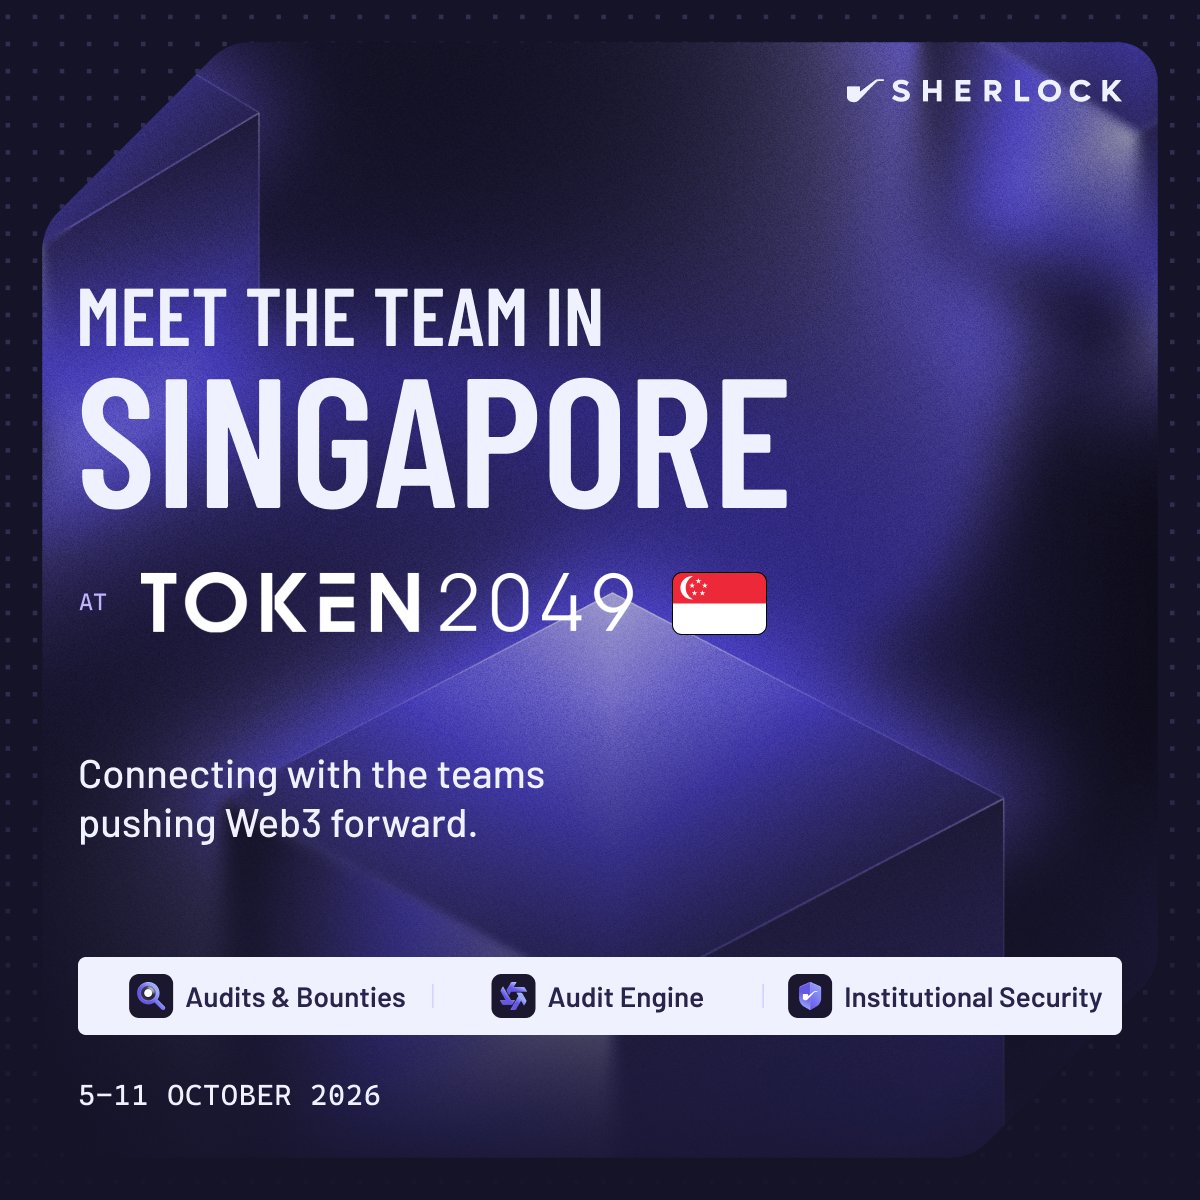
The Sherlock team is heading to TOKEN2049 Singapore. 🇸🇬
To our clients, partners, and teams pushing Web3 forward: let’s connect.
We’re talking audits, bug bounties, Audit Engine, and institutional security. Bring us what you’re working on.
Book time with our team:
https://t.co/pfURQT8ETw
New Sherlock Bug Bounty: @golemproject
Golem is building a global, DePIN marketplace for computational resources, connecting idle CPU, GPU and memory with the workloads that need them.
$10,000 USDC per valid Critical report.
Reward details below 👇
The next bull market is coming into view. Our partners never stopped building.
In 2026 we’ve worked with leading teams across stablecoins, payments, lending, trading, tokenization, Bitcoin infra & core infrastructure.
Sherlock was trusted to secure the code behind them.
In a recent post, @VitalikButerin argued AI could make formal verification practical at scale. Defining “secure” is the hard part.
Onchain, we ask what a proof covers, what sits outside its model, and whether it still applies after an upgrade.
We’ve been getting more questions from clients about formal verification, so we broke it down here. 👇
The @CRX_FX team completed an AI-only Sherlock Audit Engine run on their zkVM Risk Engine + FX Clearing Core.
CRXFX is bringing FX rate locks on-chain: 30+ corridors, custom contracts, and instant USDC settlement.
3 AI auditors: @v12sec / @zerocool_ai / @savantchat
51 submissions
21 accepted findings
1 High | 8 Medium | 3 Low | 9 Info
8 High and 55 Medium findings surfaced across the web app, offchain coordination, ZK library, and contracts. BaBe had no High or Medium findings.
All were resolved / formally acknowledged.
Babylon then hardened the library and returned for a dedicated review, where Sherlock verified the fixes and stress-tested it against malicious setup and malformed inputs.
https://t.co/crEu3R2I9W
Researchers from Sherlock and @blackthornxyz reviewed ZK proofs, cryptography, Bitcoin enforcement, Aave V4, and offchain services as one system.
Babylon treated security as protocol-wide, holding every layer to the same rules.
That depth matched the ambition of what Babylon is building.
ZK infrastructure depends on every system behind the proof.
@babylonlabs_io is defining the Bitcoin-ZK category by making native BTC usable in DeFi without ever leaving Bitcoin.
Sherlock and Blackthorn audited the full Trustless Bitcoin Vaults stack, followed by a dedicated hardening review.