Securing the agentic endpoint. Real-time visibility, governance and protection for the AI agents, MCP servers and skills on every machine in your organization.
Backslash has been named among Dun's 100 Best Startups to Work For in 2026! 🩷
The list is based on what employees say about their own workplace, which is why it means so much to us.
Thank you to our team, who earned this, and to Dun's 100 for a great event.
#Duns100
EDR, SASE and AI gateways leave AI risk on your endpoints uncovered.
One plugin, skill or MCP server can let an agent read sensitive data and run commands.
Join our CTO Yossi Pik and Up Defense's Roni Goldenberg for a Hebrew webinar, Nov 24, 11:00 IST: https://t.co/w1PqK4RtaG
“Attacks now happen at inference speed,” said @CrowdStrike’s George Kurtz at #FalConEurope, echoing what our CEO @ManShahar hears from customers: they want to move fast with AI, but ask what their agents are actually doing. Find us at Fal.Con Europe, booth #210.
🔴 LIVE WEBINAR TOMORROW. 79% of organizations reported little to no visibility into their agentic AI inventory, per Backslash customer data. @ranio1 and @JamesBerthoty of @latiotech go live on how security must adapt to agentic AI.
If your team is using Claude, are your AI agents outsmarting their endpoint cage?
We’re proud to be an Official Silver Sponsor of @CrowdStrike Fal.Con Europe 2026. Meet Shahar Man and Peter Wilcox in Barcelona, November 2–4, at booth #210.
#FalConEurope#AIAgentSecurity
Only 1 in 10 secrets we found in AI agent session histories was pasted by a user, and about 3 in 4 got there through the agent's own work.
A skill asking for .env was blocked, but one reading past sessions got the same keys.
Read the full blog → https://t.co/OLODIvTSWm
Our CEO Shahar Man was interviewed by @Calcalistech about how AI agents can put an organization at risk even without a malicious attack.
Read the full article: https://t.co/LGyTirh3h7
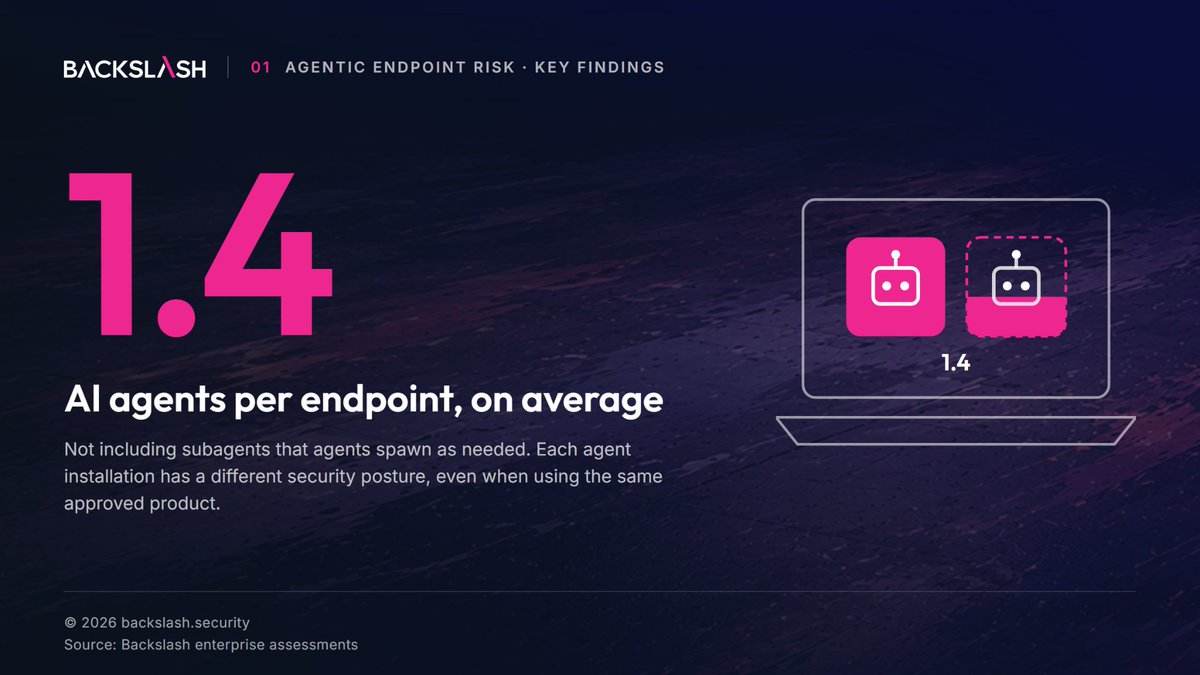
Employees run 1.4 AI agents per endpoint on average, not counting subagents.
Each installation has its own skills, MCP connections and permissions, so the same approved product can carry a different security posture on each endpoint.
Read the report: https://t.co/DiLcR0MboC
AI agents now run on employee laptops, and every vendor promises to secure the endpoint.
We compared 7 agentic endpoint security vendors and listed 4 tests to run on a live endpoint: discover, map, block, keep evidence.
#AgenticAIEndpointSecurity
https://t.co/awWJ7G0cWm
@AnthropicAI says as much themselves: "Auto mode reduces permission prompts but does not guarantee safety. Use it for tasks where you trust the general direction, not as a replacement for review on sensitive operations."
We tested it and found 3 gaps.
https://t.co/vFyx3In66Y
OpenAI quietly patched security flaws in Codex via release notes. Some never got a CVE, and older versions still run with them. Our CTO Yossi Pik was interviewed by @ISMG_News on why AI coding agent fixes skip the CVE process, and why it matters. https://t.co/5xwIteg2mF
Backslash named AI Security Endpoint Leader in the @latiotech 2026 AI Security Market Report.
Recognized for real-time protection and intent-based runtime analysis across Claude Code, Cursor, MCP & skills.
Thanks to our customers and team 🙏
https://t.co/UYS5051ywO
𝗧𝗵𝗲 𝗔𝗽𝗽𝗦𝗲𝗰 & 𝗥&𝗗 𝗣𝗹𝗮𝘆𝗯𝗼𝗼𝗸: 𝗛𝗼𝘄 𝘁𝗼 𝗔𝗹𝗶𝗴𝗻 𝗦𝗲𝗰𝘂𝗿𝗶𝘁𝘆 𝗮𝗻𝗱 𝗜𝗻𝗻𝗼𝘃𝗮𝘁𝗶𝗼𝗻
Bridge the gap between AppSec and R&D with clear steps to streamline workflows and foster collaboration.
👉 https://t.co/dPspgK3qGH
𝗙𝗿𝗲𝘀𝗵 𝗔𝗽𝗽𝗦𝗲𝗰 𝗶𝗱𝗲𝗮𝘀, 𝗮𝗻𝘆𝗼𝗻𝗲?
Our CEO’s, Shahar Man latest @TheHackersNews article explores how to revitalize application security practices for today’s challenges.
Dive in: https://t.co/vqVX3oh0V1
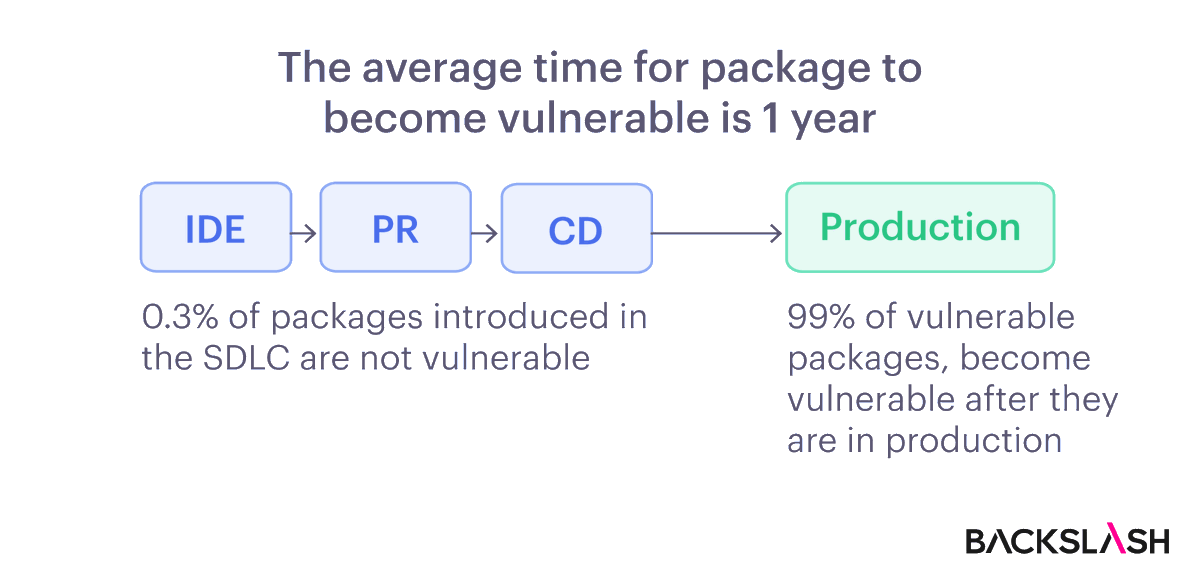
PR gates are great for verifying code changes, but let’s be real—they’re not a true defense mechanism. In our latest research, we conducted an extensive analysis of popular npm packages with over 1,000,000 yearly downloads.
📖 Check out our findings: https://t.co/WikLDTgClD
🤯 𝗢𝗻 𝗮𝘃𝗲𝗿𝗮𝗴𝗲, 𝗶𝘁 𝘁𝗮𝗸𝗲𝘀 𝗷𝘂𝘀𝘁 𝗼𝗻𝗲 𝘆𝗲𝗮𝗿 𝗳𝗼𝗿 𝗮 𝗽𝗮𝗰𝗸𝗮𝗴𝗲 𝘁𝗼 𝗯𝗲𝗰𝗼𝗺𝗲 𝘃𝘂𝗹𝗻𝗲𝗿𝗮𝗯𝗹𝗲.
While PR scanning is a crucial part of application security, it’s not enough. Read our full findings here: https://t.co/WikLDTg4w5
🤔 𝗜𝘀 𝗣𝗥 𝗦𝗰𝗮𝗻𝗻𝗶𝗻𝗴 𝗘𝗻𝗼𝘂𝗴𝗵?
New research from our team reveals a major security gap: PR gates often catch very little, and most OSS vulnerabilities are discovered long after code is merged.
Read the research: https://t.co/WikLDTg4w5
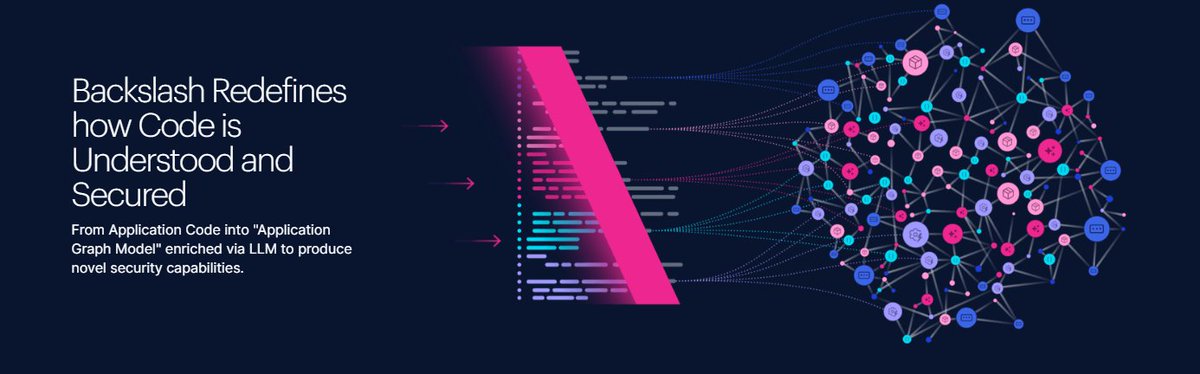
𝗚𝗼 𝗯𝗲𝘆𝗼𝗻𝗱 𝗯𝗮𝘀𝗶𝗰 𝗦𝗖𝗔 𝗮𝗻𝗱 𝗦𝗔𝗦𝗧!
With advanced reachability analysis, phantom package detection, and powerful remediation capabilities. See it in action: https://t.co/FJwfYNS5uE