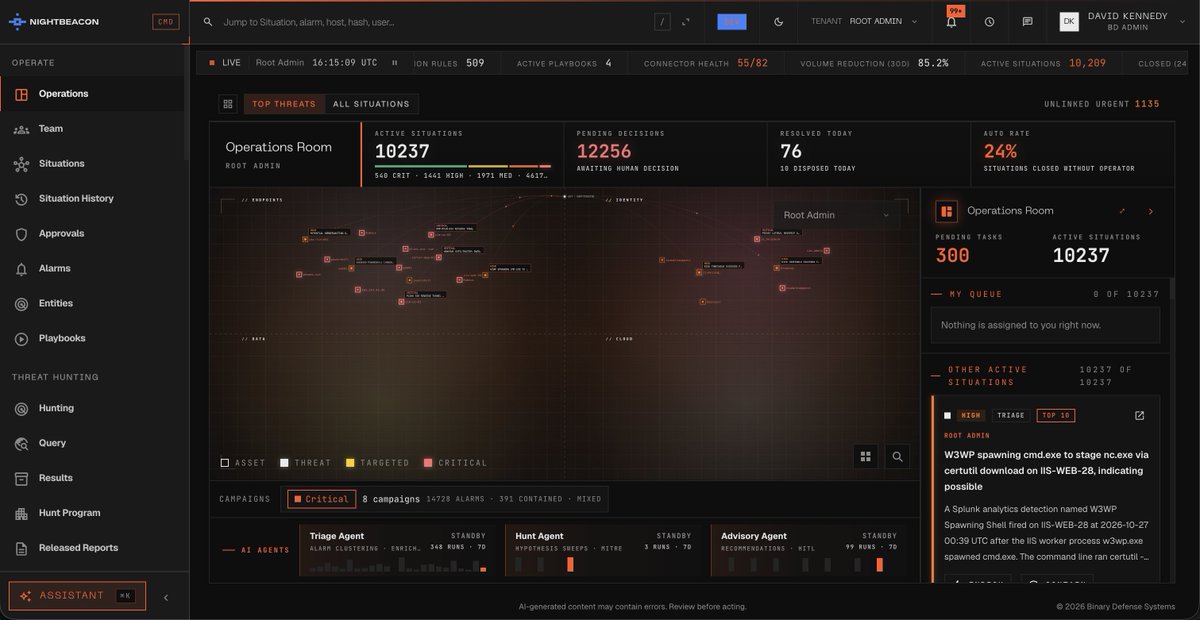
Want to drive NightBeacon CMD and see the power we've been building for over a year?
Gamified - run through an entire situation from start to finish, conduct threat hunts to identify compromised identities, see the power of what CMD really is.
Simply fill out information, get approved in minutes, and drive NightBeacon CMD.
https://t.co/kzinCpT9x7
#BinaryDefense
Alerts come in faster than analysts can review them. Real threats get lost in the noise.
For years, the answer has been a shorter queue worked faster. But what if you didn’t need the queue at all?
On December 8, Jason Vest (CTO) and Todd Kaltenborn (VP, Security Operations) will give a live look at how our SOC moved from reviewing individual alerts to working decision-ready Situations, and what that’s meant for our analysts.
You’ll learn:
- The difference between Situations and alerts, and why it matters
- How our SOC workbench, NightBeacon CMD, makes this approach possible
- Lessons you can apply to move your own SOC toward a zero-queue reality
Register now. Everyone who registers gets the recording.
https://t.co/fBPnQiH6ua
Friday at Queen City Conference, two of our leaders are speaking back-to-back. Block off 10:00 to 11:45.
10 AM, Regency A
@HackingDave's keynote, Throne of the Zero Trust Pharaoh. Bolting AI onto your existing stack isn’t going to cut it. Dave gets into what that means for defenders and how to actually use AI in your work today.
11 AM, Track 3 – Kilo Bytes
@Wh1t3Rabbit on The Changing Nature of SOC Analyst Work for the AI SOC Generation. Is AI taking work off your plate, or just shifting it somewhere else? Rafal covers how the mental load on analysts is changing, how SOC teams should reorganize, and how metrics need to change to keep up.
Two talks, one morning, and a clear look at where defense is going. See you Friday, Nov 13.
Cincinnati, see you this week.
We’re headed to Queen City Conference, November 13–15 at the Hyatt Regency Cincinnati, and our team will be there all three days.
Stop by table 2 to talk about how AI is changing the SOC, how to move faster without taking analysts out of the loop, or whatever your team is up against right now.
Bring your questions. Leave with a game plan.
Attackers don’t need to crack cryptography when they can social engineer your employees.
Thanks to Yaël Bizouati-Kennedy and @theindexsite for including our CTO Jason Vest in this look at the $6.3B Binance theft, and why crypto's biggest vulnerability is human.
Jason's point: the same playbook has now worked against both Bybit and Binance. That's not one company's problem. It's an industry still building the operational controls around the technology it created.
Full story: https://t.co/zoYOgnNttN
Think fast. Fight smart. Find us at BSides.
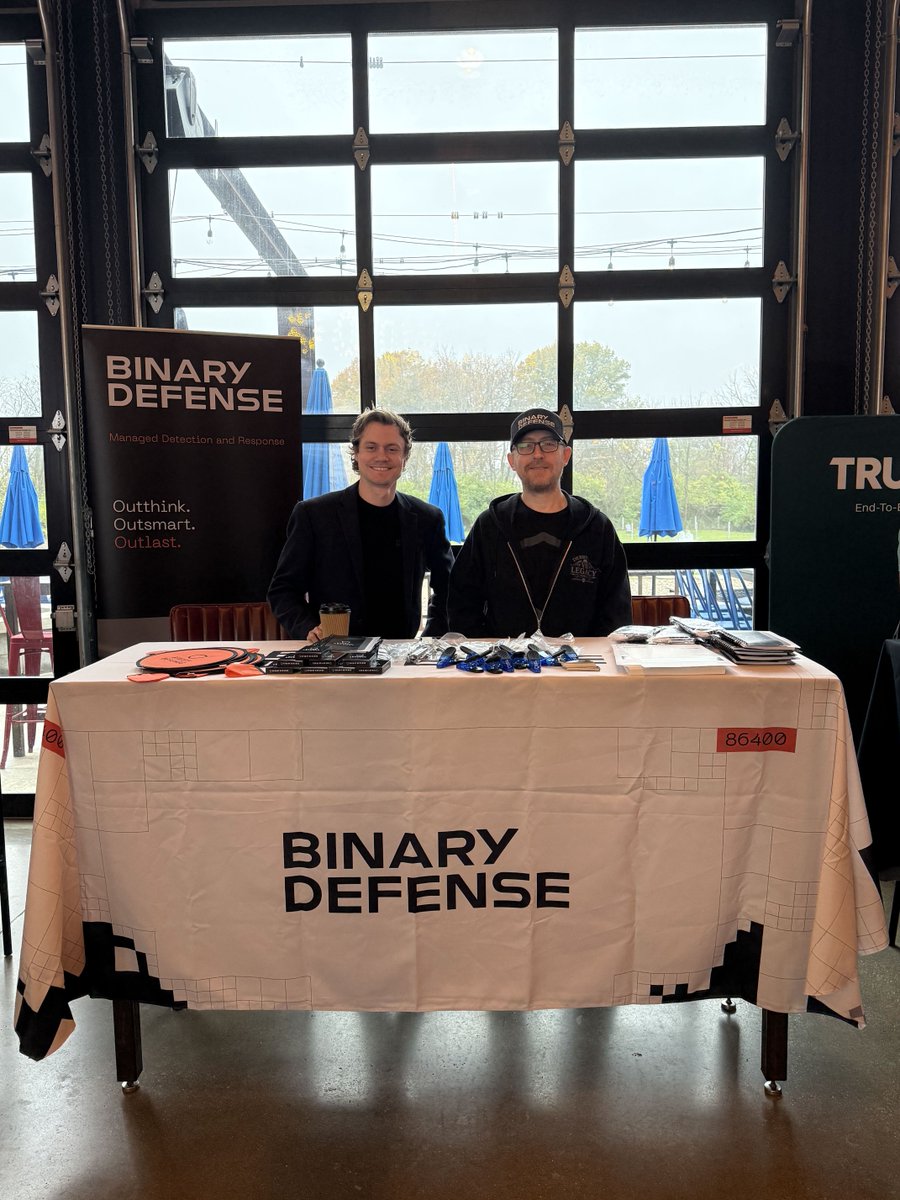
Today we’re at BSides Columbus at BrewDog in Canal Winchester.
Stop by and talk through what’s eating your team’s time: alert overload, too few hands, threats that don’t keep business hours. We’ll show you how NightBeacon MDR puts a human wingman in the fight, 24/7.
Not sure where to start? That’s what we’re here for. Our team will walk you through what fits your environment and what it takes to get there.
Good talks. Good people. Come say hi.
1,000 alarms. 1 situation. 1 human making the call.
NightBeacon CMD stitches the noise into the story. Your analysts stay in charge.
Full webinar: https://t.co/rbrW5zlIvc
Thousands of alerts a day. Up to 99% of them benign. And the queue still never shrinks.
For years, SOCs have tried to work the queue faster. We stopped working it.
Our analysts now work Situations, not alerts. NightBeacon CMD pulls every alarm and entity behind an event into one decision-ready Situation. NightBeacon does the analysis. Our analysts make the call.
On December 8 at 1 PM ET, Jason Vest (CTO) and Todd Kaltenborn (VP, Security Operations) will walk through how this changed our SOC, what our analysts think of it, and what you can take back to your own team.
Can’t make it live? Register anyway, and we’ll send you the recording.
Save your seat: https://t.co/r3tuFEe1sF
Heading to BSides Columbus next week? So are we.
The Binary Defense team will be on the floor November 6th, and we want to hear what’s keeping you up at night. Alert fatigue, stretched-thin teams, threats that show up at 2 a.m. on a holiday weekend. Bring the tough questions and we’ll bring straight answers.
Stop by to see how NightBeacon keeps a human-first defense working for you around the clock, so your team can focus on what matters most.
Columbus, let’s talk shop. See you there.
Good hats. Better conversation.
Thanks to everyone who joined Binary Defense and @PaloAltoNtwks at Haywire in Plano yesterday. We dug into how AI-speed attackers are reshaping the SOC, swapped real-world stories, and sent every guest home with a custom felt hat from @McKinneyHatCo. Thank you to their team for fitting every head in the room.
Defense is a team sport. Dallas showed up.
Every week NightBeacon gets a little sharper, on its own.
Latest model, auto-trained and auto-validated:
187 fewer false positives per 14.7K benign alerts (−16%)
83% detection at a 0.1% false-positive rate (was 75%)
Less noise for analysts. Zero manual model picks.
This was a one week statistical improvement from the prior weeks last model. Insane.
#BinaryDefense
Quest Diagnostics just disclosed a breach of the portal healthcare providers use to order lab tests and pull results. Patient records were likely accessed, and operations kept running.
That combination tells you something. Our CTO Jason Vest weighed in for HealthcareInfoSecurity: “That looks a lot more like data theft and extortion than traditional ransomware.”
Test results, insurance details and portal credentials keep their value long after the breach is contained. Jason explains why labs are in the crosshairs and what that means for defenders:
https://t.co/sCBGEKhIOt
Automating security decisions with AI won’t always give you the best containment scenario. AI should inform, but humans still need to make the critical decisions.
That’s exactly how NightBeacon CMD operates. It provides the evidence analysts need to make an informed decision. But the analyst still owns the decision.
See how NightBeacon CMD works: https://t.co/9NR6Gygzkt
A detection that never fires looks exactly like a well-tuned one. You wouldn't know the difference until it was too late.
We gave an AI detection engineer one rule: prove the detection works against real data, or explain why it can’t. In one run it found a rule that could never fire, tuned a noisy one with evidence, and called an empty environment “not covered” instead of faking it.
ARC Labs walks through the full run, including what it handed back to a human: https://t.co/euuzJUnY0k
Attackers are using AI to move faster. Defenders can too.
@HackingDave opened IANS New York on AI as a force multiplier. Not a replacement for analysts, but a way to do more with the team you have.
See it in action with our team on the IANS NYC floor today.
Attackers used to need 15 minutes to get a foothold, and hours or days to get everything they were after.
They can now do it all in a few minutes.
AI is changing the game for attackers. Defenders need to adapt.
Hear the full breakdown from our CEO David Kennedy, Chief Strategy Officer Rafal Los, and TrustedSec's Ryan Macfarlane and Carlos Perez on how defenders are adapting in the era of AI enabled attacks: https://t.co/HGhQIrxUwH
Most AI grades its own homework: reviewers see the model's answer, agree, and the agreement becomes training data.
In NightBeacon CMD, adjudicators commit their verdict before they ever see the model's.
Blind by design.
See it for yourself: https://t.co/9v3Pd3df62
Last weeks Citrix 0-Day laid an egg and your SIEM likely never saw it.
Attackers hid a payload in a NetScaler crash log and dropped a forked RAT. ARC Labs has the IOCs, KQL hunts and YARA rules in our breakdown below.
Read the full blog here: https://t.co/yUphkwscMq