🔴 IDOR Vulnerability
Discovered an IDOR vulnerability in the Forgot Password feature.
The issue is that the password reset token is not properly bound to the account email.
An attacker with a valid reset token could change the password of another user’s account due to improper token validation.
Example request structure:
{
"email": "[email protected]",
"newPassword": "NewPassword123!",
"token": "VALID_RESET_TOKEN"
}
#bugbountytip #hackerone #infosec #BugBounty #Hacking
🔎 CVE-2026-32130 — SCIM Auth Bypass
Found a path normalization issue where encoding U as %55 bypassed authentication.
GET /scim/v2/{org}/%55sers/{user_id} HTTP/2
/Users/... → 401
/%55sers/... → 200 OK
The endpoint returned the SCIM user object without authentication.
I found a vulnerability that allowed a low-privileged user to steal an administrator's Bearer token through a malicious shared connector, leading to administrator account compromise.
Full writeup:
https://t.co/Y2F98HkBoA
#bugbountytip#hackerone#infosec#BugBounty#Hacking
1. Bypassing invitation code restrictions: The code is intended for single-use and should expire immediately after the first user joins.
2. Lack of email-to-code binding: The invitation code is not linked to a specific email address, allowing it to be used by any unauthorized email.
I discovered a Race Condition vulnerability that allowed a single invitation code to be used across multiple accounts by accepting the invite from two accounts at the same time.
In addition, there was insufficient validation of the account’s email address, which made it easier to exploit the issue and bypass the intended invite-only logic🔓.
#BugBounty #bugbountytip #Hacking #InfoSec #CyberSecurity
🔴 IDOR Vulnerability
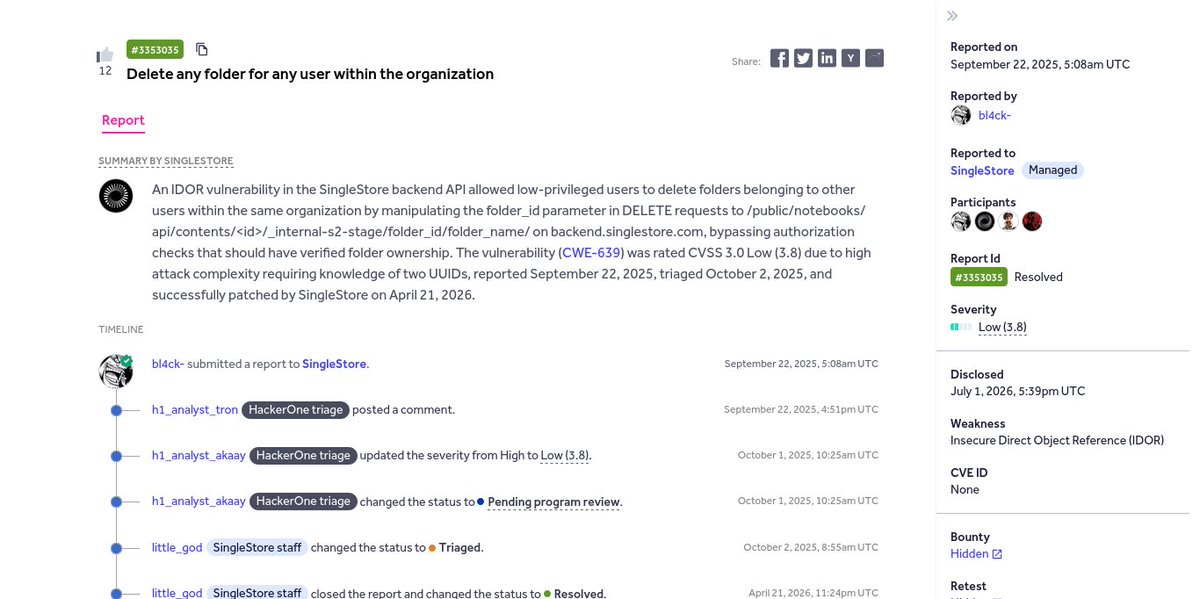
Missing validation of user's relationship with org_id.
The system relies only on memoryId without verifying organization ownership.
{
"org_id": "152ace33-d28f-4c21-bb8a-0130fe64bb24",
"memoryId": "9f3c2a41-7b8e-4d6a-a2f1-3e6c8d9b1a42"
}
Modify or delete other organizations' data by simply changing the memoryId.
#BugBounty #bugbountytips #Hacking #infosec