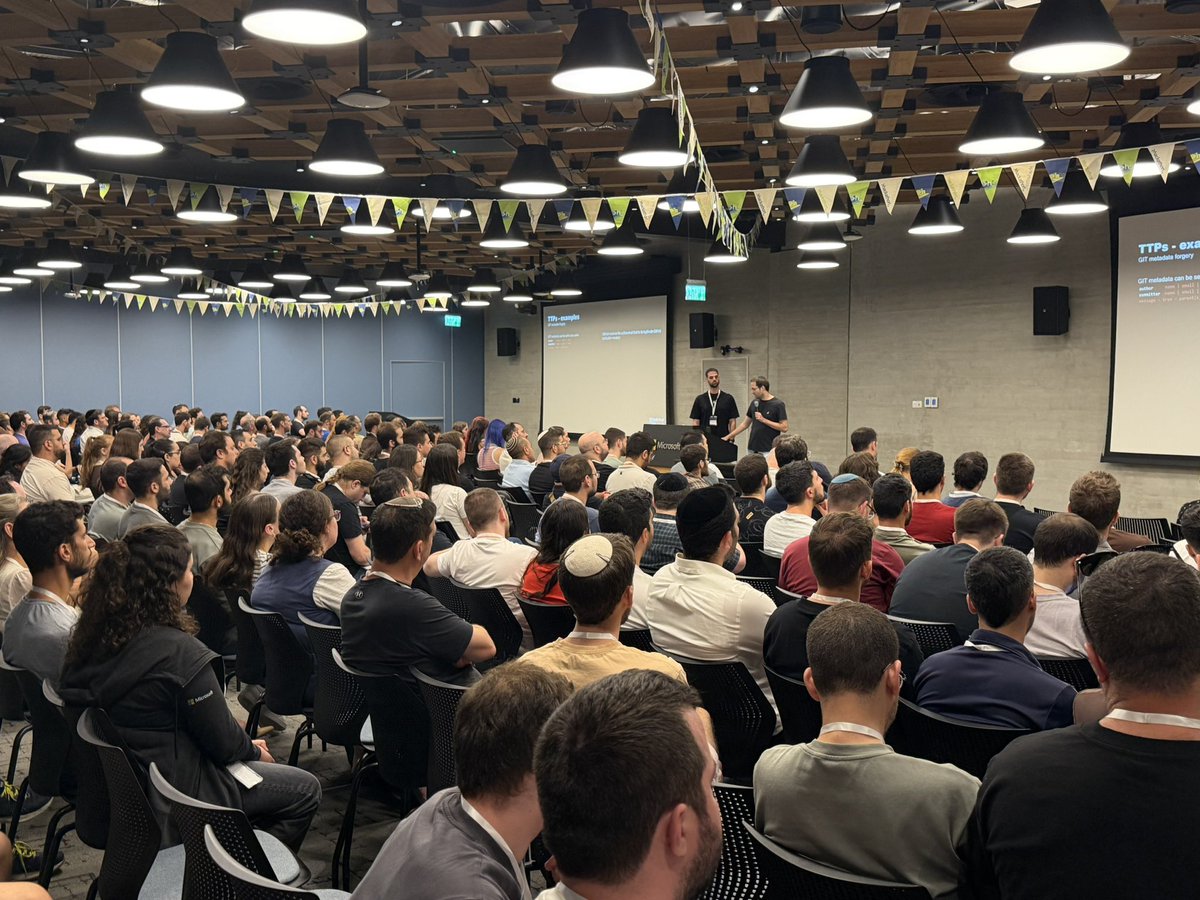
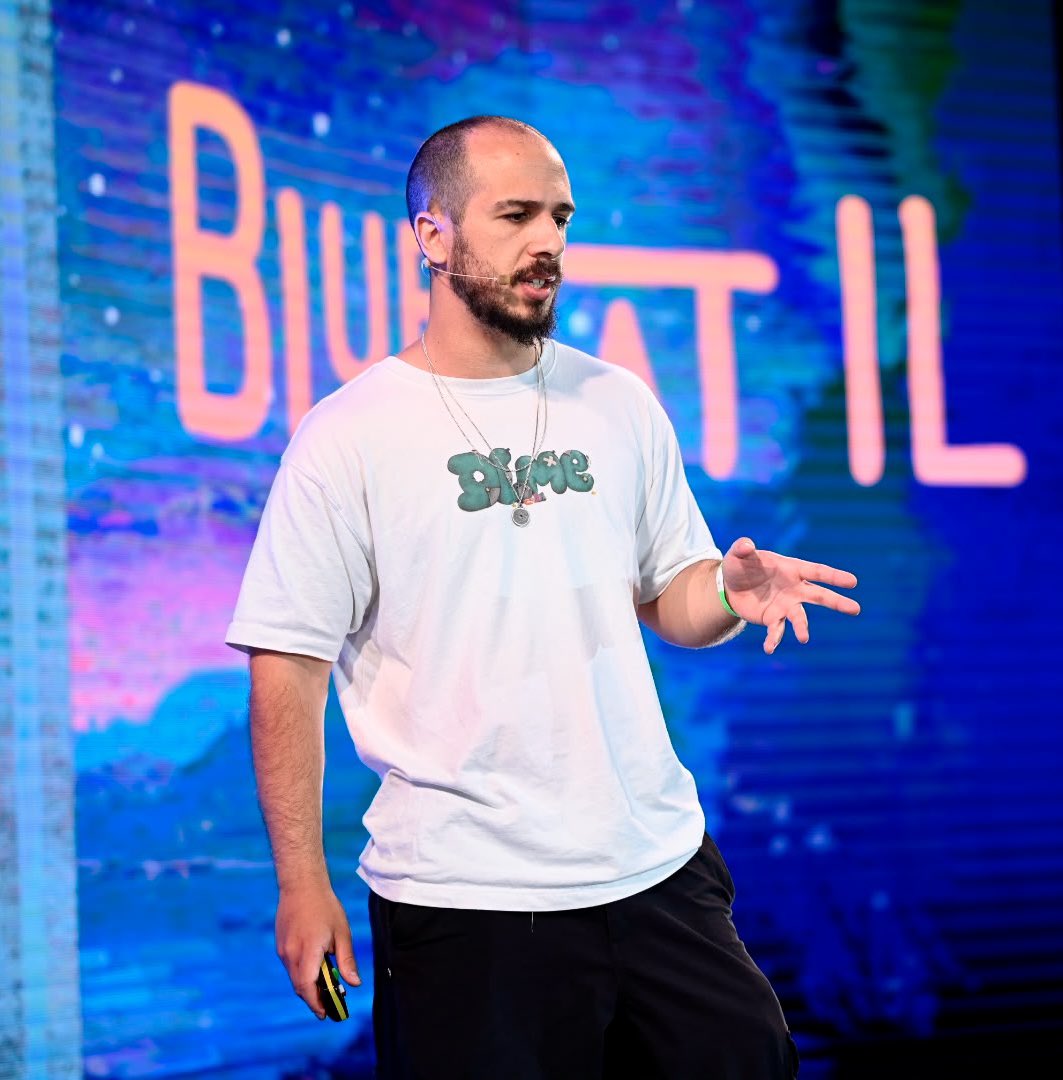
Shoutout to our amazing speakers at the BlueHat IL community meetup - and a huge thank you to the hundreds of you who joined us tonight. What a night! 💙
Grab your spot before they’re gone! Some of Israel’s top cybersecurity researchers are coming together for a special BlueHat IL community meetup - fresh from Black Hat and ready to share their latest research.
Register now: https://t.co/DhLnBiIBru
What happens in Vegas doesn't stay in Vegas!
Fresh off the Black Hat USA stage: Yossi Weizman, Mor Weinberger, Moriya Pedael & Simcha Kosman are joining us for a special BlueHat IL community meetup to share their latest research.
Register now: https://t.co/DhLnBiIBru
Cancel your weekend plans, grab an unreasonable amount of popcorn, and hit play. The BlueHat IL talks are now online and ready to watch! https://t.co/Wrw9DIeF1p
Yesterday you got RCE. Today you escape the sandbox.
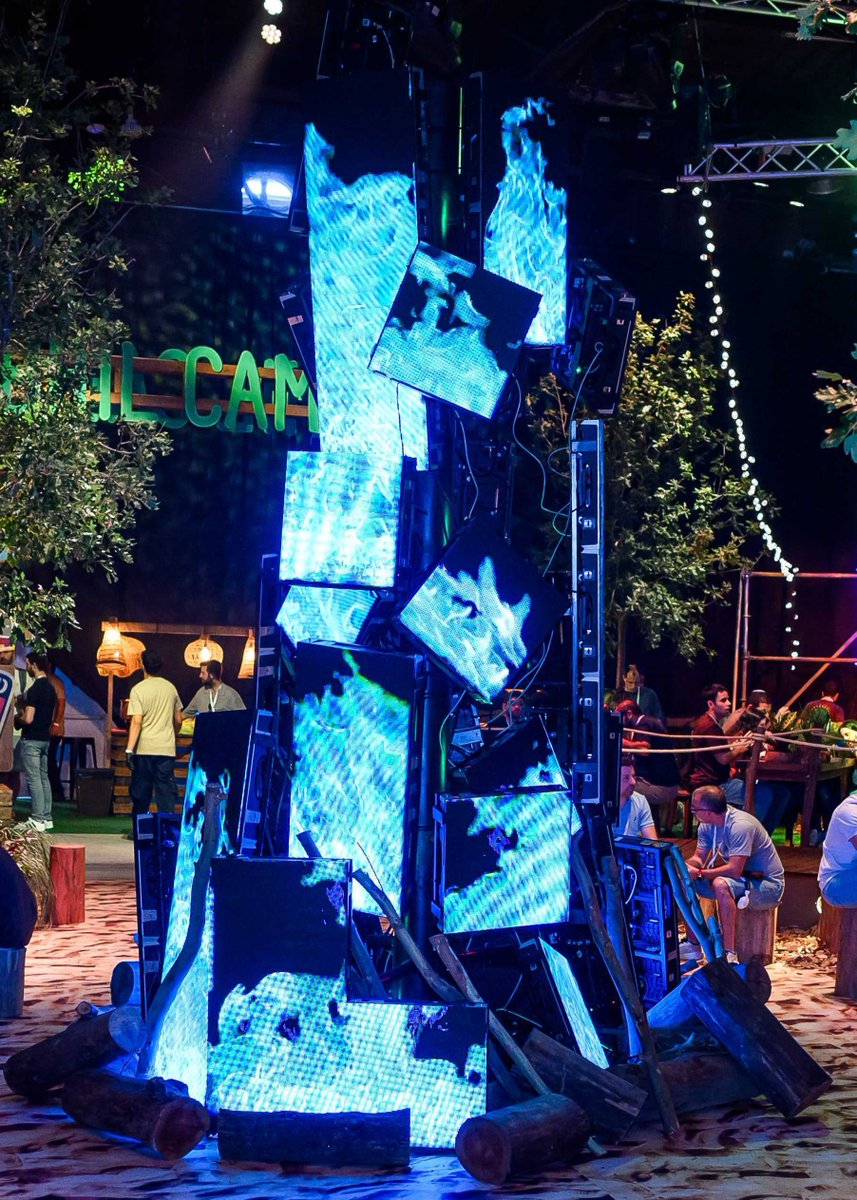
In Trial by Fire (Part 2), participants quickly discover that code execution isn’t enough. A Linux sandbox still stands between them and the real campfire controller.
We break down the sandbox architecture, the escape path, and how participants ultimately turn the flames blue.
Read the full technical walkthrough:
https://t.co/FgdlOeczw3
Yesterday we hacked AI agents. Today, we go back to the metal.
We just dropped Trial by Fire (Part 1) - the second write-up from our Microsoft BlueHat IL 2026 CTF challenges.
This part covers the initial foothold: how to chain vulnerabilities to achieve Remote Code Execution (RCE) in a restricted environment.
Read the full technical walkthrough here:
https://t.co/gEuwP8oYnJ
Part 2 is coming tomorrow.
We had the privilege of designing and building several CTF challenges for Microsoft BlueHat IL 2026.
Today, we’re dropping the first complete technical write-up: Hack the Moon - exploiting indirect prompt injection in a multi-agent AI system.
Over the next few days, we’ll expose our infrastructure challenges involving RCE and Linux sandbox escapes.
🔗 Full write-up in the first reply.
#BlueHatIL #AISecurity #LLM #CTF #CyberSecurity
From World War II to Starlink and beyond, @DanielBachmat took us through the secret war for the spectrum, closing out BlueHat IL 2026 with a fascinating look at one of the world’s most contested resources.
Sometimes the most interesting connections are the unexpected ones. @Oranav and @vbCrLf showed how PostgreSQL internals can play a role in exploiting AI orchestration zero-days.
Reminder to the BlueHat IL community: children are not allowed at the event.
We repeat: children are not allowed at the event.
Unless they’re this cute.