‼️ BREAKING ‼️ PHP warns of another UNPATCHED REC vulnerability just 2 days after releasing emergency patches for critical PHP2Shell flaws.
New "CVE-2026-115560" affects only unusual session configurations. PHP has issued urgent mitigation guidance.
Full details → https://t.co/YQV0MCJqAp
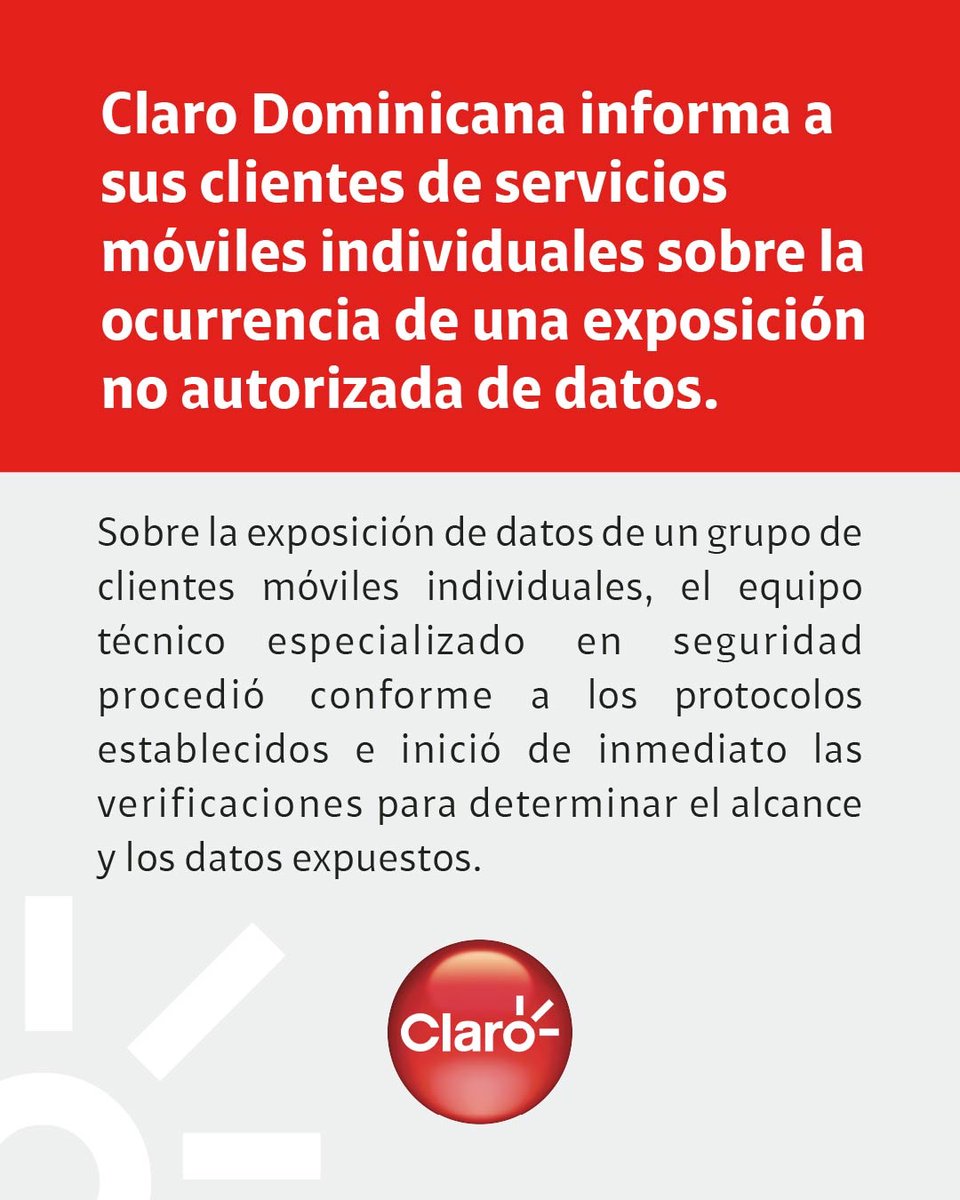
‼️🇩🇴 Claro Dominicana informs its individual mobile service customers of an unauthorized exposure of data.
The company says:
"Regarding the exposure of data belonging to a group of individual mobile customers, the specialized security team acted in accordance with established protocols and immediately began an investigation to determine the scope of the incident and the data that was exposed.
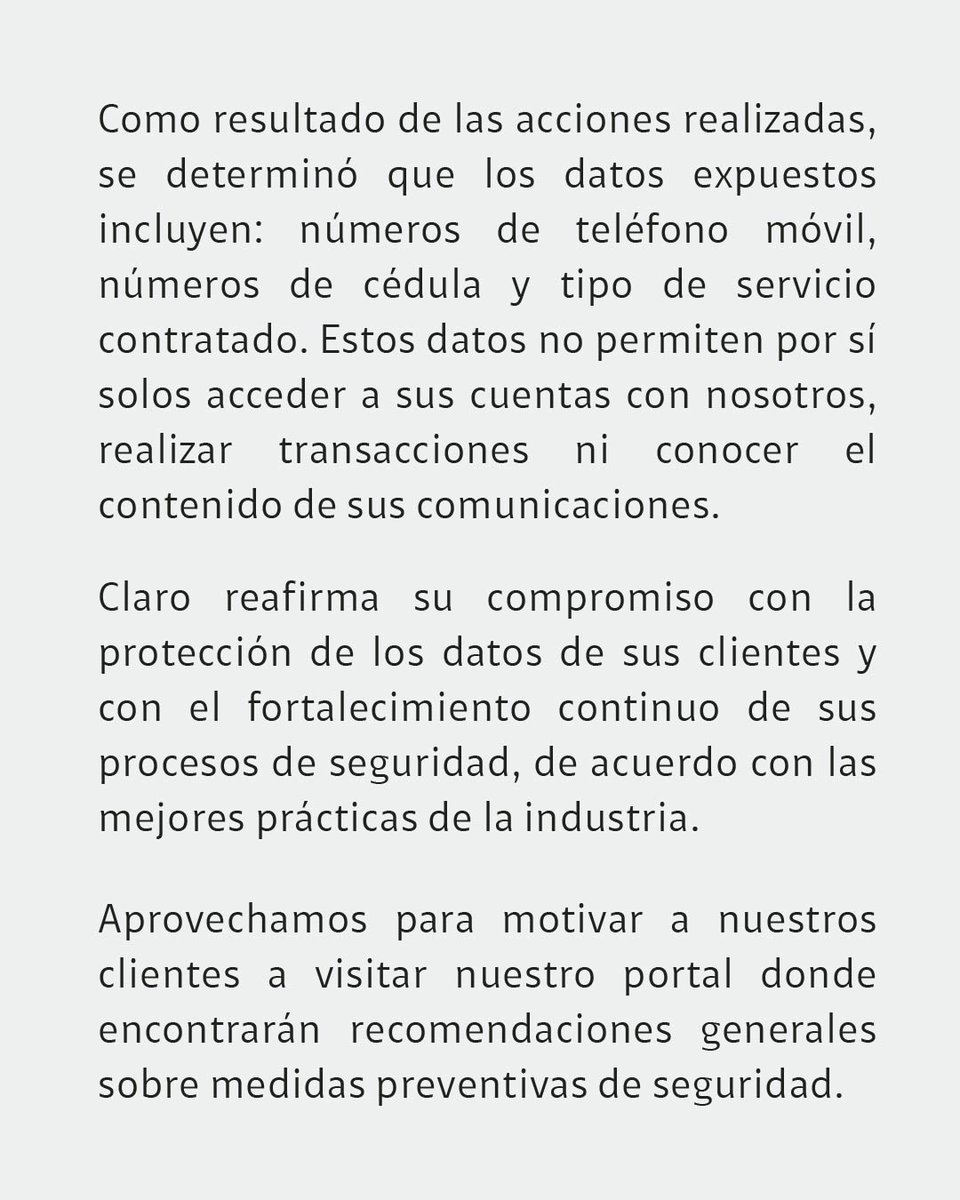
As a result of these actions, it was determined that the exposed data includes:
• Mobile phone numbers
• National ID numbers
• Type of service contracted
This information, by itself, does not allow access to customer accounts with Claro, enable transactions, or reveal the contents of customer communications.
Claro reaffirms its commitment to protecting customer data and to continuously strengthening its security processes in accordance with industry best practices.
We also encourage our customers to visit our portal, where they can find general recommendations on preventive security measures."