A CVSS 10.0 with 0% EPSS is not an emergency. That gap is the point of this account.
SecBoard reads 25+ sources and sorts by what's actually exploited — KEV, EPSS, ATT&CK. Where the data doesn't support a rating, it says so instead of inventing one.
https://t.co/02Uj0iWY3P
SecBoard Daily · 12 November 2026
Top story: Siemens Building Automation and Energy Products (CVE-2026-109618, actively exploited)
11 topics on exploited flaws
Full daily briefing on SecBoard – address in the image.
#ThreatIntel
CVE-2026-111560 (Barracuda Networks) has a CVSS of 7.2 and EPSS of 6%, yet it's in CISA KEV. This OS command injection vulnerability, exploitable by an authenticated admin, shows why confirmed exploitation always trumps scores.
#VulnManagement#CyberSecurity#InfoSec
522 vulnerabilities in CISA KEV are confirmed exploited. Windows leads with 73 KEV entries. ShinyHunters, Lazarus Group, and APT29 were frequently mentioned in the last two weeks. Our data pages provide more details.
#Windows#ThreatIntel#CyberSecurity
SecBoard Daily · 11 November 2026
Top story: Bluetooth, AirPlay Pairing Vulnerabilities Patched Across Apple Platforms (CVE-2026-113968, actively exploited)
11 topics on exploited flaws
Full daily briefing on SecBoard – address in the image.
#ThreatIntel#Apple
CVE-2026-20320 (Cisco BroadWorks) is a reminder that confirmed exploitation trumps scores. Despite a CVSS of 7.5 and EPSS <1%, it's in CISA KEV. Prioritize this XML parser info disclosure, not just high CVSS/EPSS.
#Cisco#VulnManagement#CyberSecurity
CVE-2026-124194 in Microsoft Outlook is a reminder that confirmed exploitation trumps scores. Despite a CVSS of 6.5 and EPSS of 2%, it's in CISA KEV. Prioritize based on real-world risk, not just metrics.
#Microsoft#VulnManagement#CyberSecurity
SecBoard Daily · 10 November 2026
Top story: Attackers Exploit AhsayCBS Flaws to Deploy Sandbox-Evading Python Backdoor (CVE-2026-105133, actively exploited)
6 newly listed as exploited
Full daily briefing on SecBoard – address in the image.
#ThreatIntel
Qilin ransomware (S1242) is active, targeting finance, telecom, and healthcare. Affiliates use phishing and social engineering (T1566, T1684) for initial access, sometimes deploying web shells (T1505.003). Monitor for these TTPs.
#Ransomware#ThreatIntel#CyberSecurity
CVE-2026-102895 in GPUStack (CVSS 9.8) is actively exploited, despite an EPSS below 1%. The vulnerability allows remote requests to impersonate the built-in administrator via a reverse proxy. Prioritize patching this critical issue.
#ThreatIntel#CyberSecurity#InfoSec
@TheHackersNews An attacker doesn't need to break the encryption if the app accepts them into the group. Who can join, and which earlier messages they can read, are security decisions too. Strong cryptography still depends on getting those checks right.
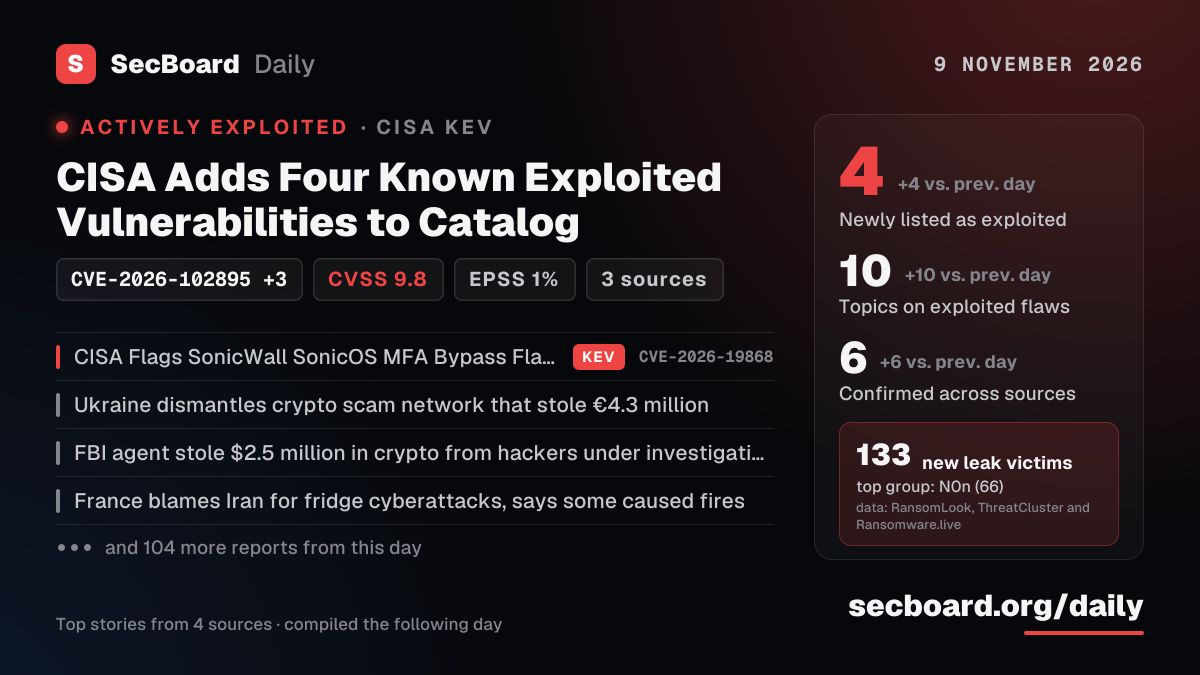
SecBoard Daily · 9 November 2026
Top story: CISA Adds Four Known Exploited Vulnerabilities to Catalog (CVE-2026-102895, actively exploited)
4 newly listed as exploited
Full daily briefing on SecBoard – address in the image.
#ThreatIntel
CVE-2026-123218 in IBM Aspera Faspex is a critical admin privilege escalation. Despite a low EPSS, its presence in CISA KEV confirms active exploitation. Prioritize patching this vulnerability.
#ThreatIntel#CyberSecurity#InfoSec
CVE-2026-123158 (CVSS 8.1, EPSS 1%) is in CISA KEV. This OpenSSH flaw on musl libc systems like Alpine Linux allows a password bypass with long strings. Confirmed exploitation means this low-scoring issue needs immediate attention.
#AuthBypass#VulnManagement#CyberSecurity
SecBoard Daily · 8 November 2026
Top story: Iris Ohyama data cloud breach exposes info of 7.7 million customers
12 reports collected · 24 new leak victims
Full daily briefing on SecBoard – address in the image.
#ThreatIntel
This week's KEV additions include criticals from Apache, Ivanti, Fortra, Microsoft, and Craft CMS. All are CVSS 10.0, EPSS >99%. Prioritize based on your asset inventory, as confirmed exploitation means they all need attention.
#Ivanti#ThreatIntel#CyberSecurity
SecBoard Daily · 7 November 2026
Top story: SonicWall warns of new SSL-VPN MFA bypass flaw exploited in attacks (CVE-2026-19868, actively exploited)
2 topics on exploited flaws
Full daily briefing on SecBoard – address in the image.
#ThreatIntel#SonicWall
APT29 (SVR) is active, targeting government, healthcare, and finance. They use phishing, social engineering, and AiTM. Monitor for T1566, T1684, T1557, and T1036. Patch CVE-2024-27834, CVE-2026-73570, and CVE-2025-43529.
#Phishing#ThreatIntel#CyberSecurity
CVE-2026-19868 in SonicWall SSLVPN is actively exploited, bypassing SAML and MFA. Despite a CVSS of 7.5 and EPSS <1%, CISA KEV listing means confirmed exploitation. Prioritize remediation over scores.
#SonicWall#VulnManagement#CyberSecurity
SecBoard Daily · 6 November 2026
Top story: CISA, federal partners flag exposed OT controllers as cyberattacks disrupt supermarket cooling systems across Europe
7 topics on exploited flaws
Full daily briefing on SecBoard – address in the image.
#ThreatIntel