Everyone swears their phone is secretly recording their voice.
You talk about buying hiking boots, and twenty minutes later Instagram serves you an ad for boots, even though your microphone permissions are turned completely off.
Most of the time, ad networks don't need audio anyway. They track you through shared IP addresses, location history, and cross-site browsing graphs.
At the physical hardware layer, the interesting question is whether your phone actually can listen with zero microphone permissions.
Turns out you don't need a microphone when your motion sensor is literally a mechanical ear etched into silicon.
1. The microscopic machine inside your phone
Inside your phone are MEMS (Micro-Electro-Mechanical Systems) accelerometers and gyroscopes.
These aren't just solid-state chips. They are tiny physical machines etched directly out of silicon.
An accelerometer has a microscopic silicon weight (a proof mass) suspended on silicon springs between electrical comb plates spaced barely 1.2 micrometers apart.
When your phone moves, that weight shifts and changes electrical capacitance. It is sensitive enough to measure sub-nanometer deflections.
2. The acoustic impedance catch (air vs solid)
Here is where the Hollywood spy movie stuff breaks down:
When you talk across an open room, airborne sound waves hit your phone's glass and aluminum frame and bounce right off. Air is thin, and your phone chassis is dense metal and glass. Because of that massive acoustic impedance mismatch, over 99% of airborne sound energy simply reflects away.
For a motion sensor to pick up speech, vibrations almost always have to travel through a solid medium:
- The phone's own speakers: The built-in earpiece and loudspeaker bolt directly to the chassis. During a call, the speaker physically vibrates the entire circuit board from the inside.
- A shared rigid surface: If your phone sits on the same wooden desk as a loud external speaker, sound conducts straight through the tabletop into the frame.
3. What researchers actually proved (Gyrophone & EarSpy)
Academic papers proved this side-channel is real, but with heavy asterisks:
- Stanford's Gyrophone (2014): Researchers showed smartphone gyroscopes can pick up acoustic vibrations between 80 Hz and 250 Hz (the pitch of human voices). But they didn't record someone talking across the room. They blasted audio at 75 dB from a speaker sitting on the same desk, testing a tiny 11-word vocabulary (just digits 0 to 9 and "oh"). Word recognition hit 65% for a single trained speaker, but dropped down to 26% across multiple speakers.
- EarSpy (2022): Tested accelerometer readings vibrating from the phone's ear speaker during active phone calls. Because modern ear speakers are louder and sit right beside the motion sensor, they could identify the caller's gender with 98% accuracy and guess spoken digits around 56% of the time.
Neither attack could transcribe an unconstrained conversation about buying shoes.
4. The quiet Android rate limit
Google saw this coming and quietly patched it in Android 12 by capping motion sensor polling to 200 Hz for third-party apps, requiring a special permission (HIGH_SAMPLING_RATE_SENSORS) to poll any faster.
By the Nyquist sampling theorem, a 200 Hz sampling rate cleanly captures frequencies up to 100 Hz. Adult male speech fundamentals start around 85 Hz, while female speech starts around 165 Hz, so a 200 Hz cap chops off the useful parts of speech.
The catch? HIGH_SAMPLING_RATE_SENSORS is a normal install-time permission. Android grants it automatically upon install with zero pop-up warnings. Plus, 200 Hz still aliases higher frequencies back into lower readings, and researchers already showed you can fuse offset readings from the accelerometer and gyroscope to effectively double the sampling rate without the permission.
5. Why your shopping app isn't doing this today
In the real world, physics makes this a nightmare for ad trackers.
The moment you walk, type, tap the screen, or shift the phone in your pocket, that silicon weight moves thousands of times harder than acoustic vibrations ever could. Your physical movement creates a massive noise floor that completely drowns out speech.
Ad companies don't need to burn battery processing raw vibration math when your location history, Bluetooth beacons, and credit card receipts already tell them what you want to buy. (we ain't that special mate)
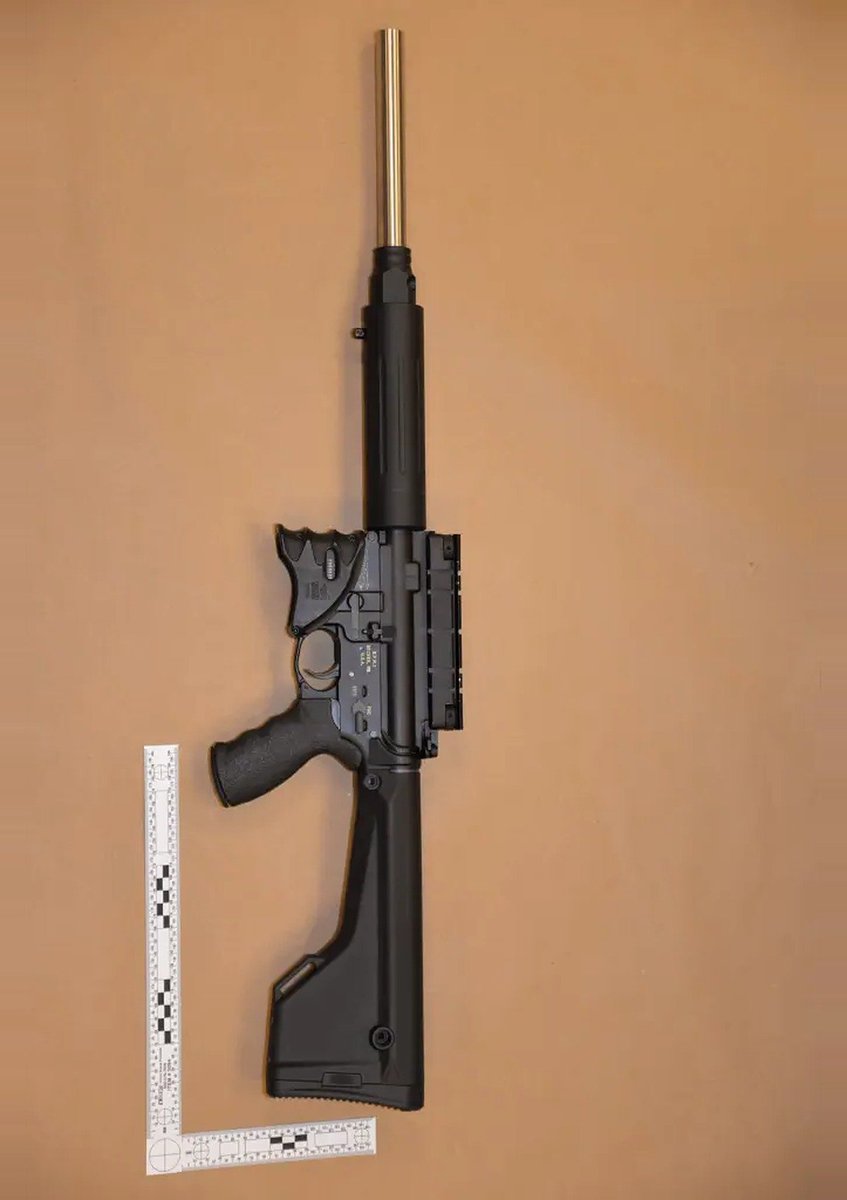
❗️ The FBI says Jonathan Kramer, 21, secretly ran a pro-ISIS SimpleX account that talked about attacks, then got hold of a rifle.
The account told its SimpleX group the app was "100% anonymous".
The FBI says it unmasked him anyway, using Reddit and Amazon records, a stakeout and a paid informant.
Agents seized his rifle and about 190 rounds from his Pennsylvania hotel room and bags on 12 September.
He hid behind the name "Hamza Al Rashid" on SimpleX, a messenger that needs no phone number or email.
Separately, Discord flagged "alternate" accounts that shared IP addresses or browser cookies with Kramer's known accounts.
One of them, last used from his home internet connection, sent users to a Discord profile showing a masked man in front of the ISIS flag.
Hamza Al Rashid had also called SimpleX "the most secure messenger available".
Weeks later, a Reddit account registered to Kramer's email wrote "simplex is where its at".
Hamza Al Rashid offered to chat at "7PM mecca time", noon in Pennsylvania, which the FBI says fits Kramer's night shifts.
Agents watched Kramer being driven to work at 9:41PM and home at 6:31AM.
The paid informant chatted with Hamza Al Rashid, who laid out a plan to blind a crowd with pepper grenades.
Amazon records show Kramer had bought pepper spray.
A federal grand jury indicted him on 6 October for receiving the rifle to commit terrorism for ISIS.
He has pleaded not guilty.
A 30 percent vitamin C solution dissolved in DMSO cleared 86 percent of basal cell skin cancer lesions within eight weeks in a clinical trial. In a randomized study published in Biomedicine & Pharmacotherapy, researchers tested a topical mix of high-concentration ascorbic acid and dimethyl sulfoxide, a solvent that helps substances penetrate deeply into the skin.
Applied twice daily for eight weeks, the combination produced complete clearance in 13 of 15 lesions (86.7 percent) among patients with low-risk basal cell carcinoma. This rate exceeded that of the standard topical treatment imiquimod, which cleared 8 of 14 lesions (57.1 percent). The vitamin C–DMSO formulation also caused fewer side effects and avoided the lasting skin hypopigmentation sometimes seen with conventional topical therapies.
Because basal cell carcinoma is the most common form of skin cancer worldwide, these early results suggest a possible low-cost, non-invasive option. Larger trials are still required before the approach can be adopted as standard care.
[Burke, B., & Bailie, J.-E. (2022). Randomized trial of topical ascorbic acid in DMSO versus imiquimod for the treatment of basal cell carcinoma. Biomedicine & Pharmacotherapy, 148, 112710. DOI: 10.1016/j.biopha.2022.112710]
WTF 🚨 The Telsa Roadster just defied gravity by hanging upside down, then LAUNCHING off a ramp did a 180 in the air and levitated to the ground...
What did we just watch 👀
Princess of UAE found slumped over during to cocaine binge on the streets of London, leaving her 3 year old to wander.
This is what happens when you whore your country to Israel and Epstein. Your women also turn into prostitutes.
Stay SAFU out there!
FWIW, I am not against hardware wallets, or self-custody. Different wallets/product for different use cases. All have different security implications and best practicies. YZiLabs invested in OneKey, SafePal (hardware wallets), TrustWallet (mobile), etc.
You use Proton VPN? Your IP could be leaked. GrapheneOS's new patch fixes that.
Even a mobile VPN can't stop leaking data on your Android it's an OS vulnerability that was recently fixed by the GrapheneOS team.
On stock Android, an app could bypass the VPN connection and request a packet (NAT-T keepalive) directly from your Wi-Fi connection, thus exposing your real ID.
No Android permission needs to be granted for the attacker to have access to your real IP and metadata. Nothing new TBH, for example, sensor data doesn't require a permission, which can lead to password input being intercepted and stolen
So even if you have the best VPN and setup possible, your identity still could be exposed. That's why hardware and OS matter.
Your great setup won't save you if the OS fails. GrapheneOS is the most secure you can get. Don't make compromises.
Get GOS.
This is insane…
An advanced Alzheimer’s patient just REGAINED her memory, speech, mobility, AND bladder control after a SINGLE dose of psilocybin.
There are NO Alzheimer’s drugs capable of doing anything CLOSE to this.
Switzerland wants every messaging app, VPN,
and email service over 5000 users to grab your government ID,
log your IP for six months, and decrypt your traffic on demand.
They're doing it by decree, skipping the vote.
The privacy capital, gone.
https://t.co/hZGk9ocFfg
Two Dutch teenagers with a metal detector dug up enough NATO weapons to arm a hundred men.
Nineteen crates of brand new pistols, explosives and sniper rifles, half a metre under a forest floor. Police called it wartime rubbish. The Prime Minister said he couldn't explain it for reasons of national security. It was Operation Gladio, NATO's secret army, funded by the CIA and British intelligence.
Windows keeps a thumbnail of every photo you've ever deleted.
It sits in a file called thumbcache_256.db, and forensic examiners pull it routinely. There are 15 more stores like it.
Here's how to find them and wipe them: