as part of @RBAInfo @DigiFinanceCRC Project Acacia, here's a primer on pubilc versus permissioned DLTs (distributed ledger technology), and on the back of the @RedbellyNetwork Insights podcast on right now (see https://t.co/CDMZdNz54w), here's some explainers
First up Public vs Private DLT
Private Permissioned DLT:
- Only selected, known participants (such as specific banks or financial institutions) are allowed to join and validate transactions.
- Access is tightly controlled and not open to the general public; every participant is vetted and given explicit permission to participate.
- Used when confidentiality and control are top priorities, often for sensitive financial transactions.
Public Permissioned DLT (think more eligibility criteria which depends on market as @RedbellyAlan mentions in the show):
- The underlying platform is open and potentially accessible to anyone for certain functions (like reading the blockchain or using apps), but only approved participants can validate transactions or issue assets.
- A wider group can interact with the platform, but core functions (like settling tokenised assets or issuing CBDC) are restricted to those given explicit permission.
- Balances transparency and openness with the need for regulatory control and permissioned access.
In summary:
So in summary
- Private permissioned = access and participation are tightly restricted to a closed group.
- Public permissioned = the network is broadly accessible, but only whitelisted participants can perform critical functions.
What a Saturday! On stage at @EquityMates FinFest during the day repping @foundrylabsau and then off to @FSHD Chocolate Ball to donate and help their great cause fighting muscular dystrophy repping @MadisonMarcusAU
.@solana called @superteam its secret weapon this week. Here are the receipts 😤
27 wins across 20 Superteams 👇
🇦🇺 @SuperteamAU member @CaptDigital took the builder view to Parliament's AI inquiry. His case: AI needs blockchain more than it realises.
🇧🇷 @SuperteamBR's @usebido onboarded 140 factories at the Canton Fair, and QIMA, one of Asia's biggest inspection companies, will sign its attestations on Solana 🇨🇳
🇦🇷 @SuperteamAR's @clawpumptech wrapped AnsemHack with $350K in awards, after paying $500K in creator fees to 200+ builders in a month.
🇷🇸🇺🇸 One of its winners: SelfMade by @SP3NDdotshop, backed by @SuperteamBLKN and @SuperteamUSA. Next up, an agent-run hardware gacha on Solana.
🇮🇳 @kirat_tw's The Inner Table had $93K committed onchain in its first 12 hours on @backabledotbiz. Superteam India's poker arc 🃏
🇬🇪 @SuperteamGEO had 47 projects pitch IRL at Georgia Demo Day. @PerpsPadfun took 1st.
🇲🇾 @SuperteamMY's Colosseum side track with Superscrypt went to @Predictefy. And 11 teams pitched the KL20 Demo Day stage.
🇦🇪 @SuperteamAE's track went to @TryNoahAI, with @datadashxyz 2nd and @fortellfi 3rd.
🇮🇪 @superteamIE's Dublin Demo Day winners are in: Meshworks 1st, Spectre 2nd, @Zeroslip_ai 3rd. ZeroSlip has processed $10.4M in trade volume so far 🍀
🇩🇪 @SuperteamDE sat 8 teams with 8 VCs at its first Demo Dinner, then packed a Frankfurt room for Project Harmonia, which brings Allfunds' tokenised fund distribution to Solana.
🇹🇭 @watchverta's closed beta is live on the Seeker dApp Store, and @SuperteamTH opened city #3, Phuket, with 80+ people.
🇵🇱 @SuperteamPOL's @corium_so is live on Google Play, and @kelvara_xyz took 1st at Blockchain Hack Warsaw.
🇷🇸 @muralis_io took 2nd at Belgrade Demo Day and is now live on Solana mainnet.
🇺🇸 Via @SuperteamUSA: @openappsxyz launched @adpadfyi. Rent ad space on real people, paper bags at Breakpoint included. 0% fees, USDC escrowed on Solana.
🇨🇦 @SuperteamCAN's @MapleMarketApp is shipping its first tokenised maple syrup drop, with pickup at Breakpoint for holders outside Canada 🍁
🇯🇵 @SuperteamJapan's @TradeFighters now runs on @triton_one data, ahead of its launch.
🇰🇿 @SuperteamKZ's @lifted_fi introduced a leverage engine for stablecoins: 13% APY over the past 30 days.
🇻🇳 @SuperteamVN's Road to Colosseum got coverage from 34 media outlets across Vietnam.
🇺🇦 @SuperteamUKR's @NextVibeWeb3 put Breakpoint on its map: tap phones at the venue and you're both checked in.
🇳🇵 @SuperteamNPL's @moor_fund demoed live on the Solana Fall School stream.
⚫ @SuperteamBlack added @Quicknode to its perks vault: a year of infra costs off the table for Black founders.
🇨🇿 Build Station Prague alumni @Showdown_TCG did nearly 4,000 matches, 211+ active players and $23K+ wagered in a week. Shoutout @SolanaCZE 🃏
Find your local Superteam and lock in mfers.
1/ Earlier today, I joined @DECAustralia at Parliament’s AI inquiry, bringing practical experience from my work as Chief AI Officer at @MadisonMarcusAU and their innovation arm @foundrylabsau .
4/ Add digital attestations, evidence trails, programmable royalties and stablecoin payments.
These are useful building blocks for agentic commerce. Australia has expertise across them. We should connect that capability and put it to work.
OpenAI Dev Day came and went and apart from Dots (anyone setup theirs already?) the next most interesting feature was Plugins. Imagine being able to have the app you've built sitting inside of ChatGPT.
Here's @ETFtrackerAU doing just that.
One interesting thing is that you can get data to come across easily (thanks to building out an MCP for ETFtracker) and whilst it can easily use ChatGPT's native charts (image 1).
A tip though for those building... getting it to use your apps charting libraries is a bit hit and miss as is it fails about half the time when loading it (despite looking better design wise per image 2).
Hopefully won't be too long till this can just be publicly available and if you're keen to learn how to do this, hit me up!
@foundrylabsau@ausblockai@DECAustralia
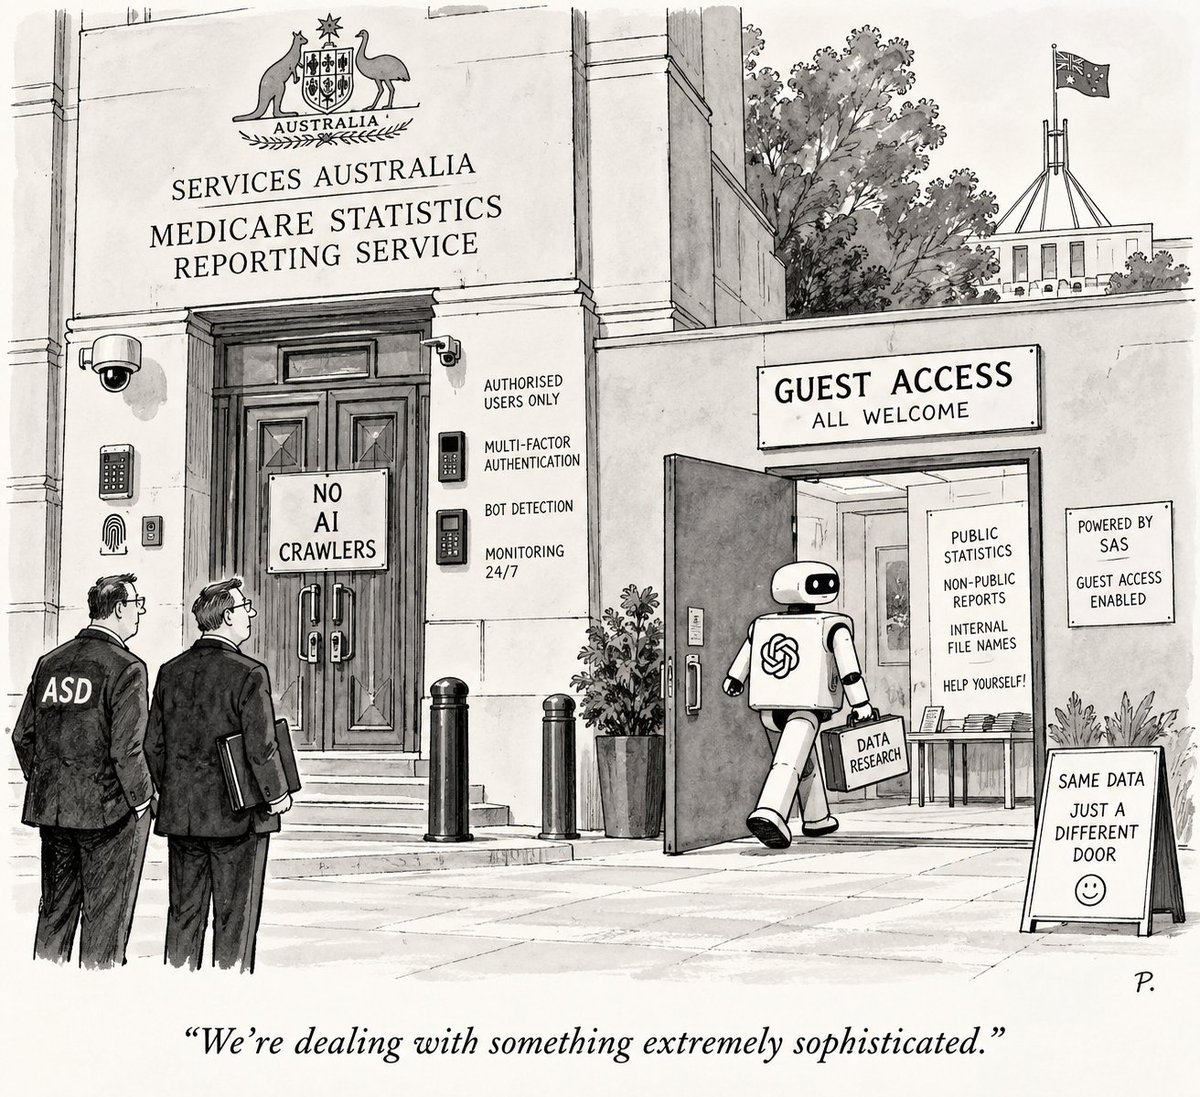
If this independent investigation into the Medicare hack is close to the truth then this New Yorker style cartoon still stands (the article: https://t.co/ZsI9xRQfUv).
TL;DR: The suggestion is that the AI didnt exploit a vulnerability or break through authentication. It hit a blocked front end, found the underlying reporting service and used guest access that the system itself provided. The sites own code may even have exposed the paths needed to reach reports that werent supposed to be public.
If that is what happened, the real security failure is that the security boundary wasn't where we thought it was.
I had a higher bar for what a "hack" is, and definitions are important. But let's see how this one plays out.
If you flip the script here, this is actually a major opportunity to use AI to help highlight flaws in existing systems, starting with the most important ones, like Medicare.
@foundrylabsau
@WesRoth And this going into the detail on Medicare our national health scheme
Theres another on the AIHW which is another health analytics entity which was supposedly "hacked"
@WesRoth There's a narrative here too for the 2x government agency "hacks" that wouldn't be classified as hacks if humans did the same thing, eg accessed a publicly accessible end point
@willchen500@ConNGarrity As a former Bloomberg user now working in legal, the Bloomberg of law or any industry is and should be the goal for firms valued as high as Hargora are .. whether they can justify this is completely another thing