⚡ Turbocharge your live streams with Caffeinated!⚡
☕ That's right, your favorite software can now be brewed to give yourself a competitive edge and set your streams apart from your peers! ☕
🥰 Your fans will LOVE the new you!🥰
https://t.co/ee8WlRCVRV
@Lina_Hoshino thanks for the knowledge on the hurdles and your efforts on the CEF upgrade 🫡
also cool to know that CEF now has a stable ABI(?)
and yeah, agreed.
@WillPayTheBill I do not have a crystal ball, but I would say it’s probably coming sooner than later.
This is only a problem if your widgets or alerts are vulnerable to XSS. If they aren’t (and you trust the maker of them) then this isn’t an issue.
@SYLViE_YTch It’d be an issue for anyone running official OBS or an unpatched version from your distro’s package manager. Definitely a massive issue for windows users since that’s the majority.
Looks like the Fedora package for OBS already has a fix in place for the code execution exploit.
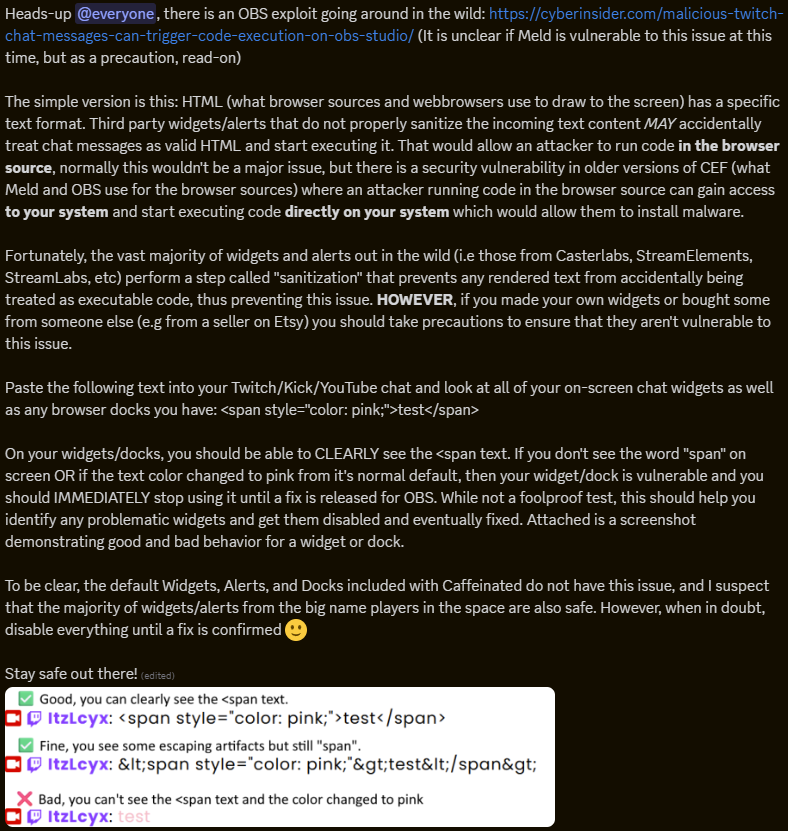
However, you should still scrutinize your widgets to ensure that they aren’t vulnerable to XSS exploits as they can still act maliciously (do the pink test)
https://t.co/avegEupAty
BTW, OBS in Fedora is not affected. Fedora has been shipping its OBS package with ~up to date CEF for a long time now.
Either way, this is only a risk if you use an unsafe or buggy chat widget. It doesn't mean everyone can get hacked through chat.
@SYLViE_YTch Interesting. I wonder if someone back ported the fix then? Specifically, CEF versions older than 128 are vulnerable. You might be able to check by opening a user agent website in a browser source to see what it reports.
@SYLViE_YTch And Twitch preemptively sanitizing everything means that every non-HTML interface would immediately start displaying garbage.
The correct solution is for people who make their own overlays to learn about XSS vulnerabilities and to fix them if their stuff is vulnerable.
@SYLViE_YTch If you’re talking about WebView2 (the windows framework that uses Edge under the hood), then no, OBS doesn’t use WV2. WV2 doesn’t support off-screen rendering and thus wouldn’t be able to be used as an overlay in the same way CEF can be.
@SYLViE_YTch The issue comes from an insecure version of CEF being shipped with OBS. They are working on an update to update CEF to patch this issue, however that wouldn’t solve the core problem of XSS vulnerabilities in poorly made widgets/overlays.
@Sevlore !
definitely contact the creator of that widget to get that fixed. XSS vulnerabilities are bad in general, it just happens that in the current version of OBS they’re much worse.