From research to FREE tools! 🔍
At #DFIRSummit, Ray DePalma shared his open-source AI DFIR Toolkit: 51 tools, 622 artifacts, 70 detection rules & 22 case studies.
🔗 Toolkit: https://t.co/oaJ284ObFX
Discover more free tools! Join us free Live Online: https://t.co/6TMWyImast
1️⃣ Complete the Ethical Hacker course on NetAcad: https://t.co/mr5sXVUDFp
2️⃣ Complete one of our quarterly #CapturetheFlag challenges on Cisco U.: https://t.co/z07K01Z9se
3️⃣ Receive your Cisco Certificate in Ethical Hacking!
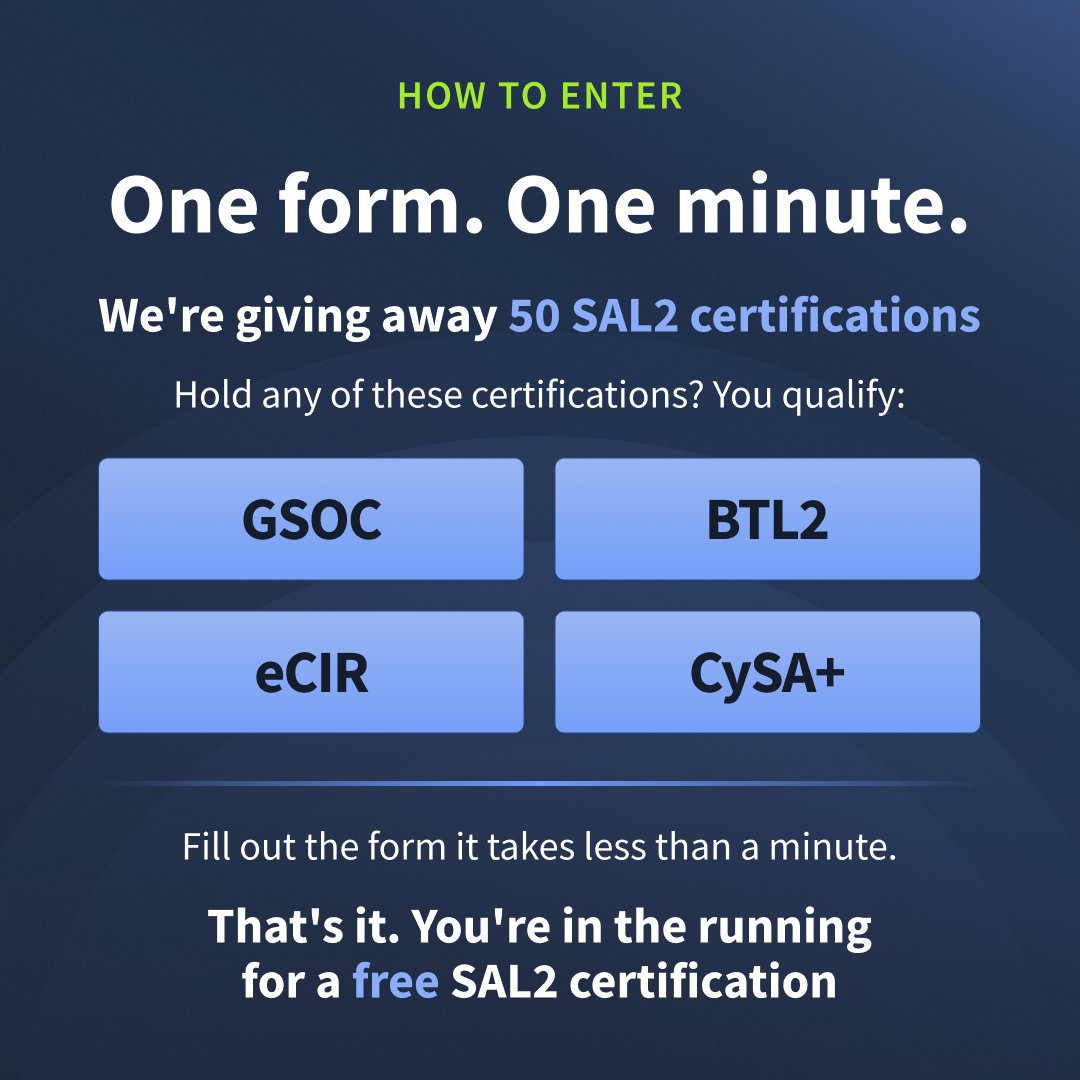
🚀 If you hold a GSOC, BTL2, eCIR, or CySA+, you already qualify. All it takes is one quick form, less than a minute to enter!
🚨 Free cert alert for defenders! We are giving away 50 FREE SAL2 certifications and you could be one of the winners🛡️
⏳ Only 3 days | 50 spots | Closes April 4th
👉 Enter now and secure your next cert for FREE! https://t.co/6qmBrbeguh
One community. One mission. 💜
The #WiCyS2026 community came together for our annual group photo, a powerful reminder of what it looks like when women, men, allies, and advocates unite to recruit, retain and advance women in cybersecurity.
Had a great time and learned to use hacker skills like OSINT and differential analysis, to gather information and to strategically job hunt like a hacker! Off to a complete overhaul of my resume and LinkedIn page!☝🏾
Thanks to Jason for a really amazing webinar @BanjoCrashland
Competition for cybersecurity jobs is fierce. Are you positioning yourself to stand out?
Join Jason Blanchard on March 10th, 2026, for this hands-on workshop and learn how to job hunt like a hacker.
Register now: https://t.co/BmFoLi2ph3
🚀 No experience? No problem.
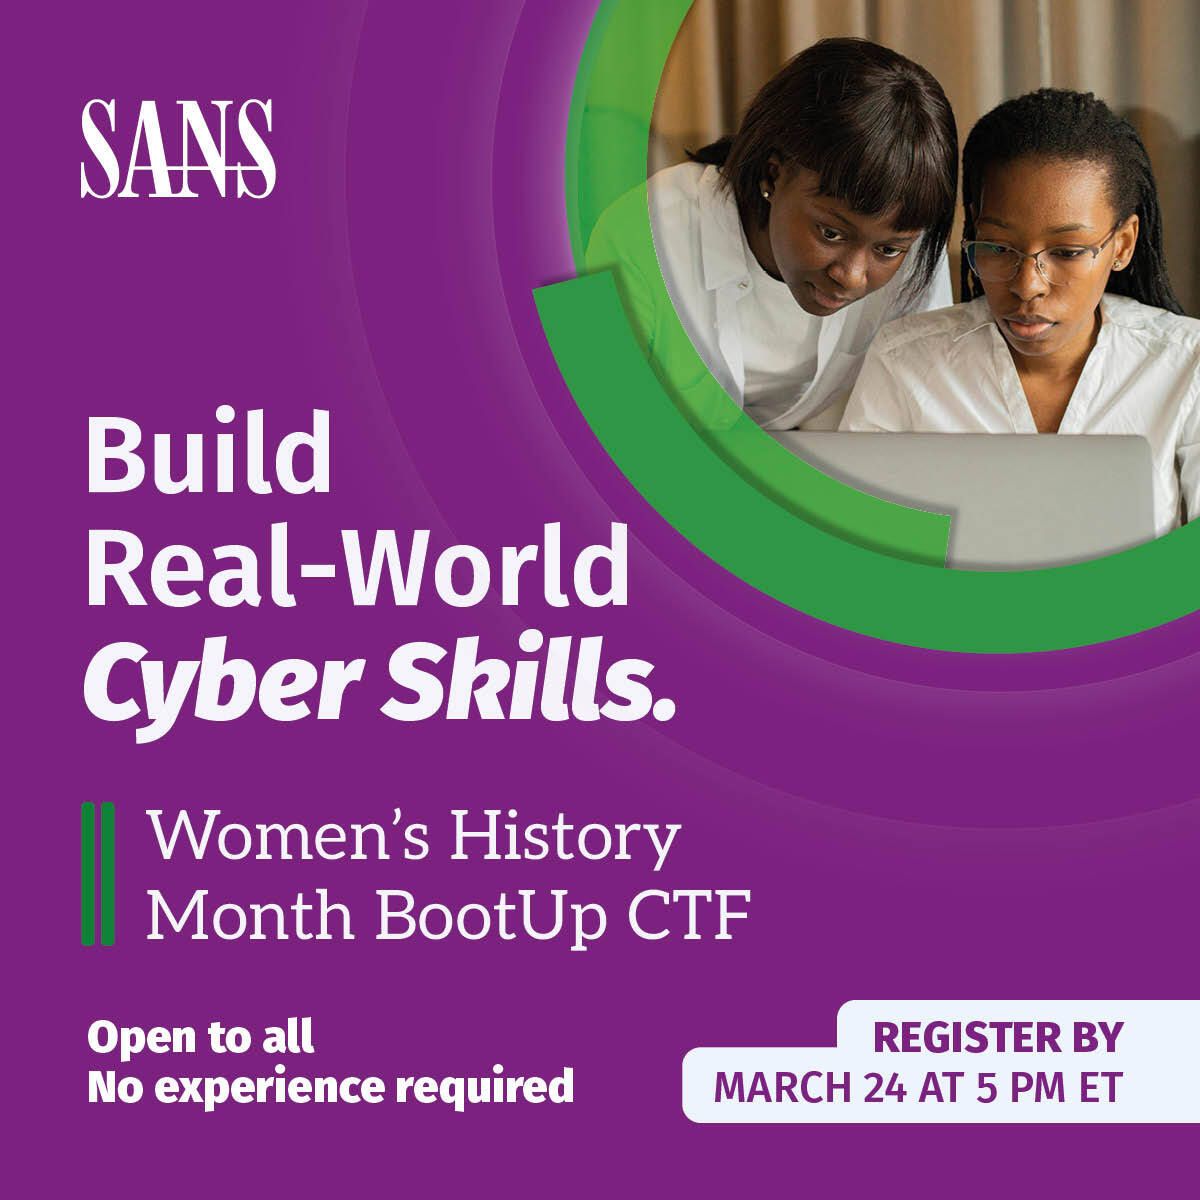
The SANS Women’s History Month BootUp CTF is open to all. Build real-world cyber skills in a free 72-hour global challenge.
🔗 Register by March 24, 5 PM ET: https://t.co/ADIaJZ35HX
🎮 Quit playing games…unless it’s for our latest DFIR Diva x @Detegoforensics giveaway!
Set in a vibrant, pixelated 8-bit cityscape inspired by classic arcade games, Detego Detective is the perfect quick break from your day. 🕹️
All you need to do to win some awesome Detego merch is reach the top 5 on the leaderboard. Detego Detective gives you the mental reset you need to stay focused at work, so get playing! 🕵️🔥
How to enter:
✅ Play the game at https://t.co/vQ1kF8N6GG
✅ Follow Detego Global on LinkedIn
Winners will be announced March 17th.
@NahamSec@sec_hub93028@hackinghub_io That’s great! I would love to grab one. Right now In Chat/DM it says that I can’t send a request to you bc I’m not verified. Is there another way to claim?
Excited to be chosen as a participant for the upcoming @WiCySorg x @SANSInstitute Cyber Quest Tournament!🎉 Ready to learn, apply some skills and capture some 🚩 !#WiCyS@lynn_dohm
📢 I partnered with @13CubedDFIR for another giveaway! 🎁
🏆 1 winner will receive a 13Cubed Investigator T-Shirt + the XPlat Bundle Complete which includes the following four courses:
- Investigating Windows Endpoints
- Investigating Windows Memory
- Investigating macOS Endpoints
- Investigating Linux Devices
Each course comes with a Certificate of Completion as well as Certification attempts.
👕 5 winners will receive 13Cubed Investigator T-Shirts
The T-shirts have the 13Cubed logo on the front and "Digital Forensics Investigator" on the back.
To Enter: Like, Comment, and Repost
On December 7th, entries from across three social media platforms will be combined and winners will be selected.
For more info check out:
XPlat Bundle Complete: https://t.co/3Sx1JWJ9x6
Certification Information: https://t.co/IVM2zdyp62
T-Shirts: https://t.co/021POuAXQL
#DFIR #DigitalForensics #IncidentResponse
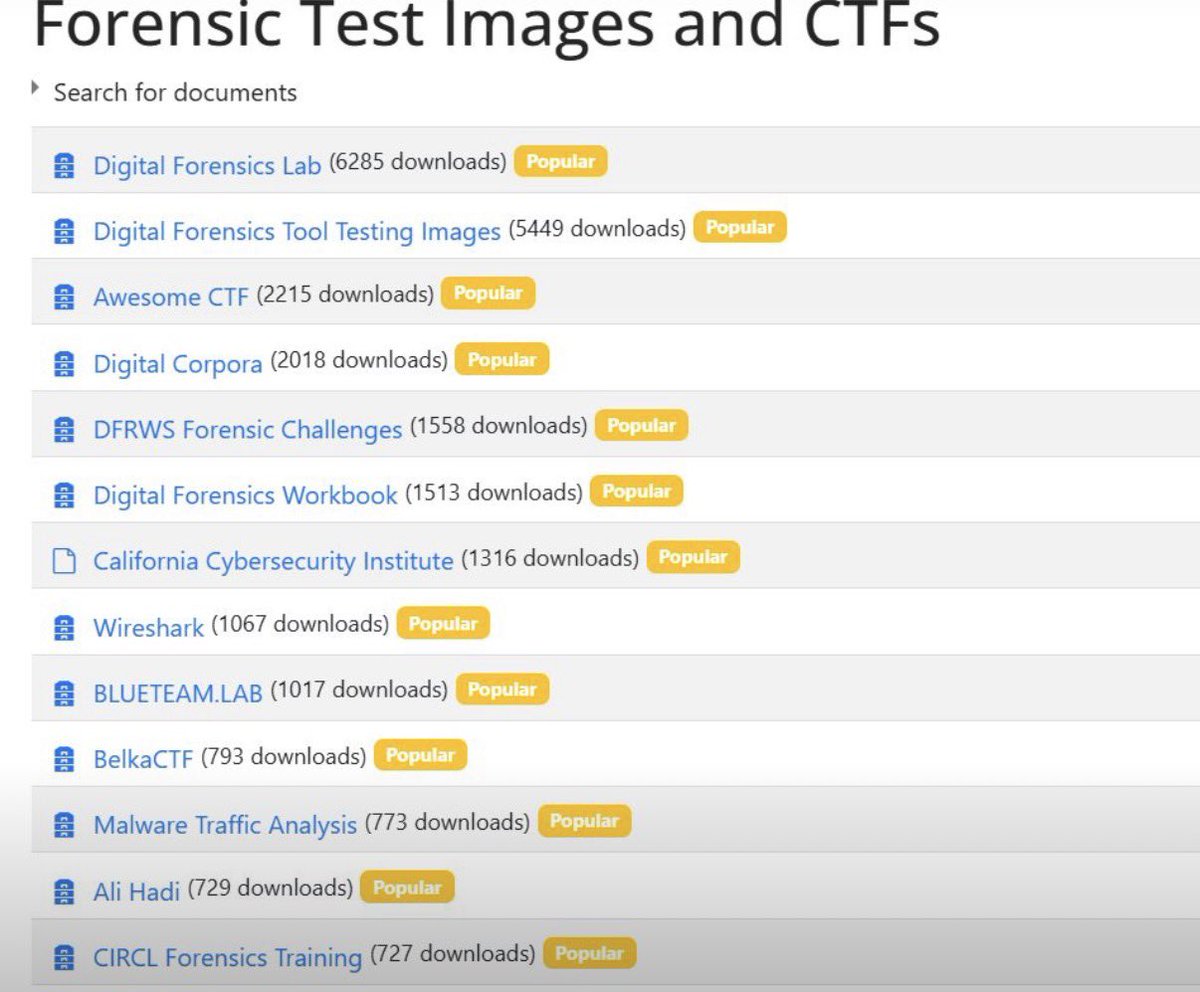
DFIR training hosts one of the most comprehensive curated collections of forensic practice materials bringing together high-quality datasets, lab images, and CTF challenges from trusted sources worldwide. The collection includes:
1. Full disk images for hands-on forensic analysis
2. Memory dumps for Volatility and memory forensics exercises
3. PCAP files for network investigation practice
4. Malware traffic and threat-hunting datasets
5. Real-world email corpora such as the Enron dataset
6. DFIR CTFs from DFRWS, DEFCON, CIRCL, BelkaCTF, MEMLabs, and others
7. NIST CFReDS and Digital Corpora reference sets
8. Tool-testing images for validating forensic workflows and methodologies.
If you're looking to sharpen your skills in digital forensics, incident response, or threat hunting, this collection is a goldmine.
The dataset provides the evidence your analysis uncovers the truth.
Link: https://t.co/5KGGUr6iEy
#retweet
🦃 🧡🤎Thanksgiving Giveaway🤎🧡🦃
I’m teaming up with @certtap to give away 1 CCNA Voucher!
Ways to enter:
• Like & Repost this
• Comment or tag a friend
Good Luck and Happy Thanksgiving 🙏🏽
If you haven't tuned in to a webcast recently, we have been including free mini-CTF's related to the topic and when you compete you can win free training from Antisyphon Training.
Learn more and signup here: https://t.co/is0ajbi3vz
Haven’t been on here in a minute, but I’ll try to track more of my progress here
End of the year goals:
☑️ GCIH
☑️ Create a DFIR project
☑️ Create a project using python
Wish me luck yall! 🤞🏾