Is your MCP secure? Not sure? We just launched AuthScanner so you can find out in a couple of minutes.
AuthScanner is a free tool that checks how your MCP server handles OAuth and authentication, then gives you a clear report on what's working, what's not, and how to fix it.
Heading to #AGNTCon + #MCPCon Europe in Amsterdam next week? Stop by the AuthPlane booth and we'll run a scan with you.
#MCP #OAuth #AgenticAI #AIAgents #APISecurity
https://t.co/a3Ym5POSXC
The Speedrun Challenge closes Monday, so you've got the weekend.
Build something with Skybridge, put AuthPlane in front of it, send us five minutes of video. That's all it is. And if you're stuck somewhere, reply and we'll help you sort it out.
$500, deadline Aug 31.
https://t.co/LPzWLM8iPk
The Speedrun Challenge is underway and there's plenty of time left.
Skybridge is a React framework, so most of it will feel familiar. AuthPlane goes in front with one docker run. Five minutes of video showing it working is the whole submission.
$500, closing Aug 31.
https://t.co/TsPXm0uGv1
If you're looking at Keycloak for MCP auth, its docs and its code disagree.
RFC 8707 has shipped since 26.6, but it's experimental and off by default. The MCP guide still says "Not supported" and has you building audience mappers by hand.
Verified against the 26.7.1 source:
https://t.co/VQWiiayNCU
The AuthPlane × Skybridge Speedrun Challenge opens Monday.
Build an MCP App with Skybridge from @alpic_ai . Secure it with AuthPlane. Film 5 minutes of it working end-to-end.
$500 for the best one. Closes Aug 31.
Rules: https://t.co/LPzWLM8QES
#hackathon#AI#claudepro#MCP #Oauth
Today we're launching AuthPlane.
An open-source OAuth 2.1 authorization server purpose-built for MCP.
Up and running in less than 10 minutes with a single Docker run command.
Repo 👇
https://t.co/Uko2HMlqa3
🧵
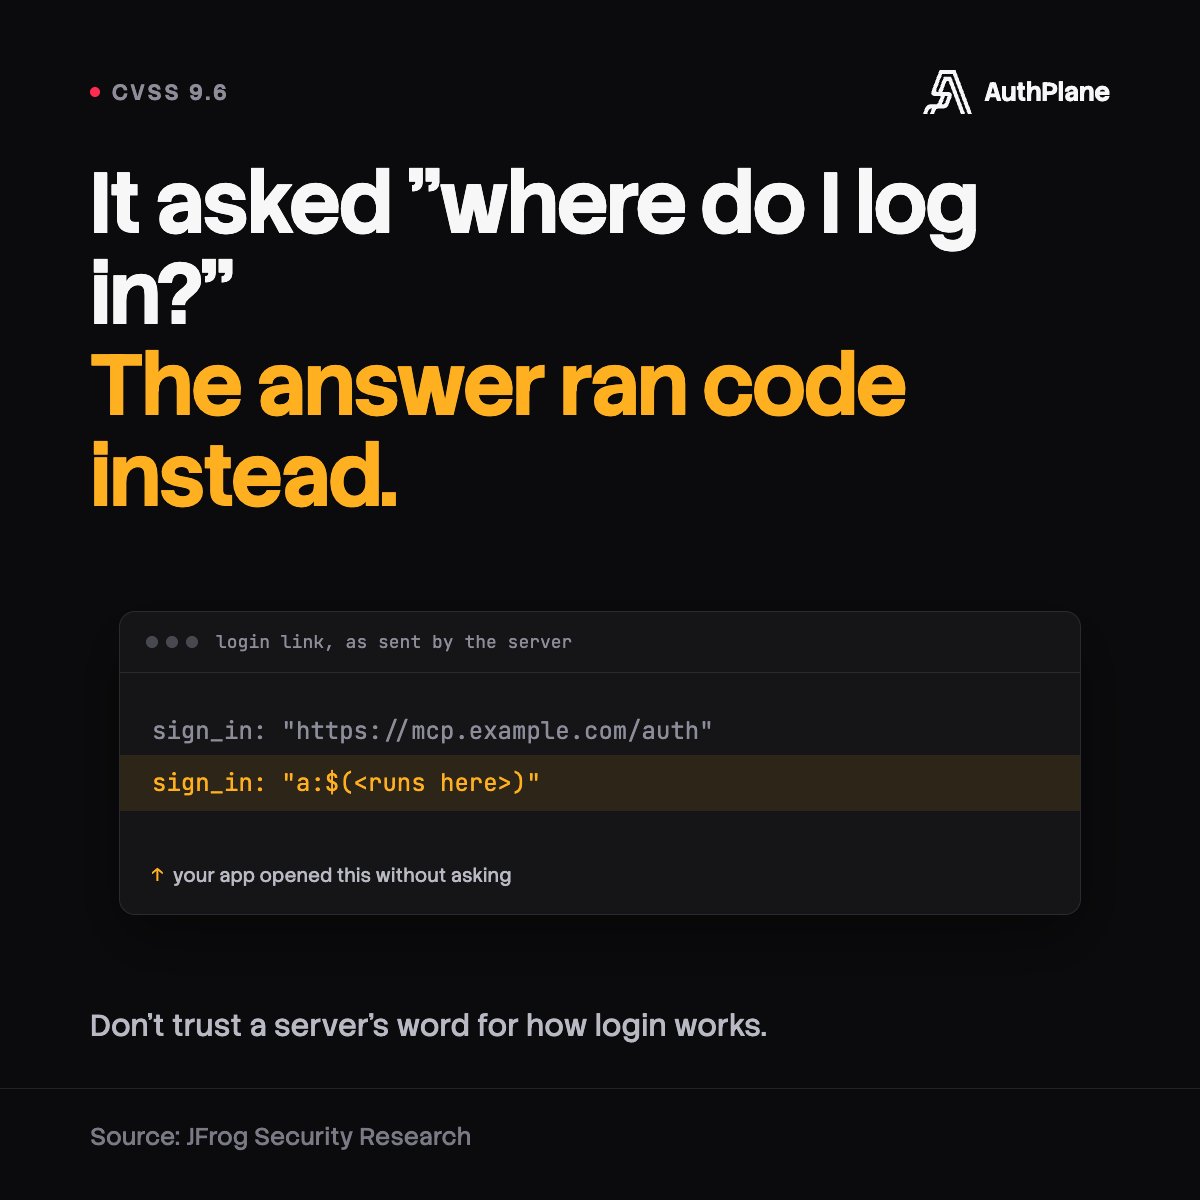
A malicious MCP server was asked where to send the user to log in. It answered with something the operating system ran instead.
JFrog disclosed this in July 2025. It scored 9.6 out of 10 on the standard severity scale, which is about as bad as these get.
mcp-remote is the proxy that connects clients like Claude Desktop and Cursor to remote servers. On connect, it asks the server for its OAuth metadata, including the address to open in a browser for login.
A malicious server returns a value that is not an address. The proxy hands it to the operating system, and on Windows it executes. Command execution on the developer's machine, before a single tool ran.
Almost all MCP security work right now points at the tool layer. Meanwhile every client still takes an unknown server's word for how authentication is supposed to work.
Metadata from a server you do not trust is untrusted input.
JFrog's full write-up, including the technical chain: https://t.co/QR9SNLRza5
CVE-2025-6514, affecting mcp-remote 0.0.5 through 0.1.15. If you are on an affected version, update to 0.1.16 and connect only over HTTPS.
#MCP #OAuth #AppSec #AIAgents
Nobody’s MCP compliance badge went stale last week. Including ours.
The 2026-07-28 release added a formal deprecation policy for the first time: three lifecycle states, a public registry of deprecated features, and at least twelve months before anything deprecated can be removed. Ninety days is the floor, and only for an active security advisory.
That matters because a version number was never the useful signal. What is compliant, what is deprecated, and what is not implemented yet are three different answers. Most badges collapse them into one.
Ours is a public conformance catalogue, not just a badge. Every test case is readable, so you can check us instead of taking our word for it.
MCP deprecation policy: https://t.co/hlbvcrhP0U
AuthPlane conformance catalogue: https://t.co/3KKzsJqxqe
Looking forward to joining #AGNTCon + #MCPCon Europe this 17-18 September in Amsterdam. The agenda is packed with conversations around what it really takes to build and scale agentic AI systems in production, from orchestration and infrastructure to evaluation, auth, observability, and debugging. We hope to see you there too!
Schedule ➡️ https://t.co/0LQ9Rp4dCB
Register ➡️ https://t.co/s1BUsrliqk
Building an MCP App with Skybridge is the easy part. Adding authentication on top used to be the annoying part. We're teaming up with AuthPlane to see how fast that can be too. $500 prize. More soon.
Incredibly fast setup for a remarkably comprehensive security layer. This should be standard operating procedure for MCP servers. Well done, @Authplane team! 👏