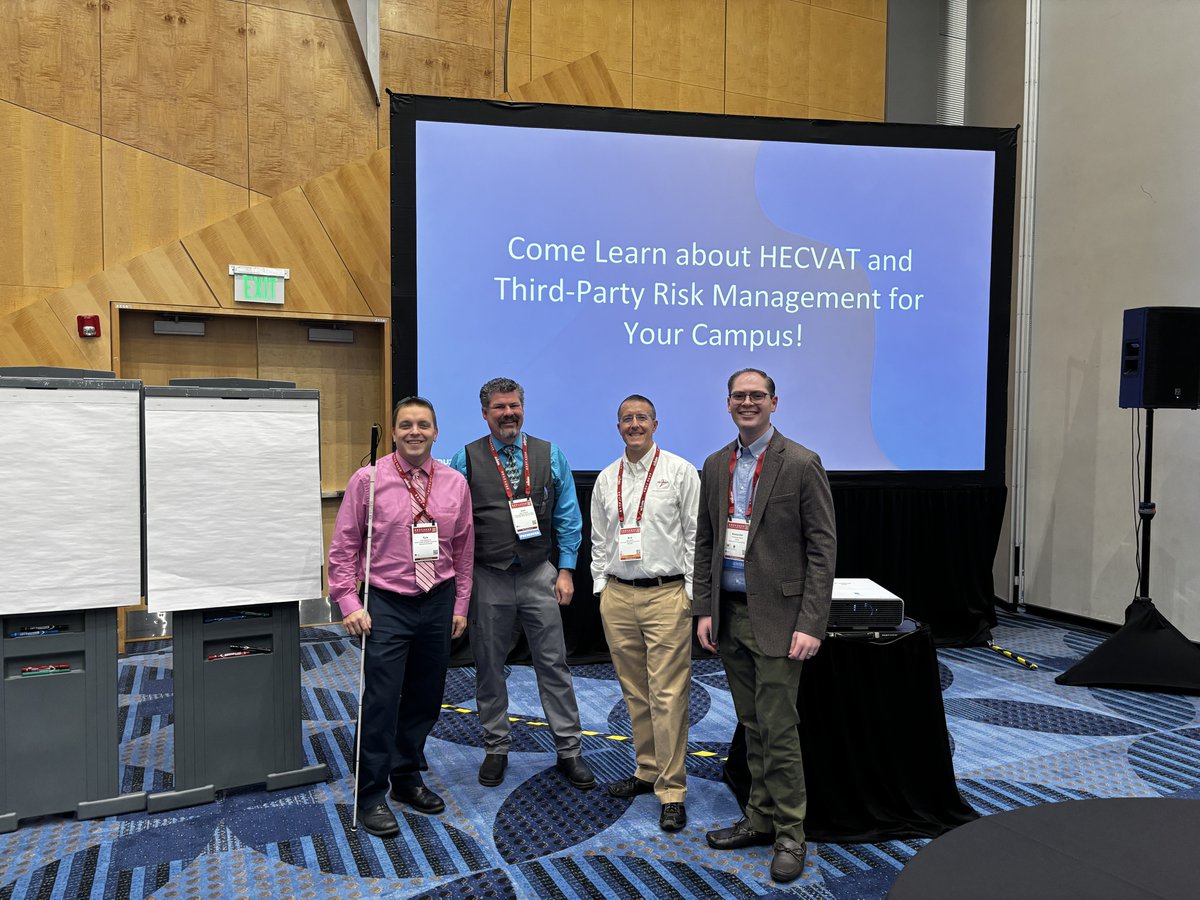
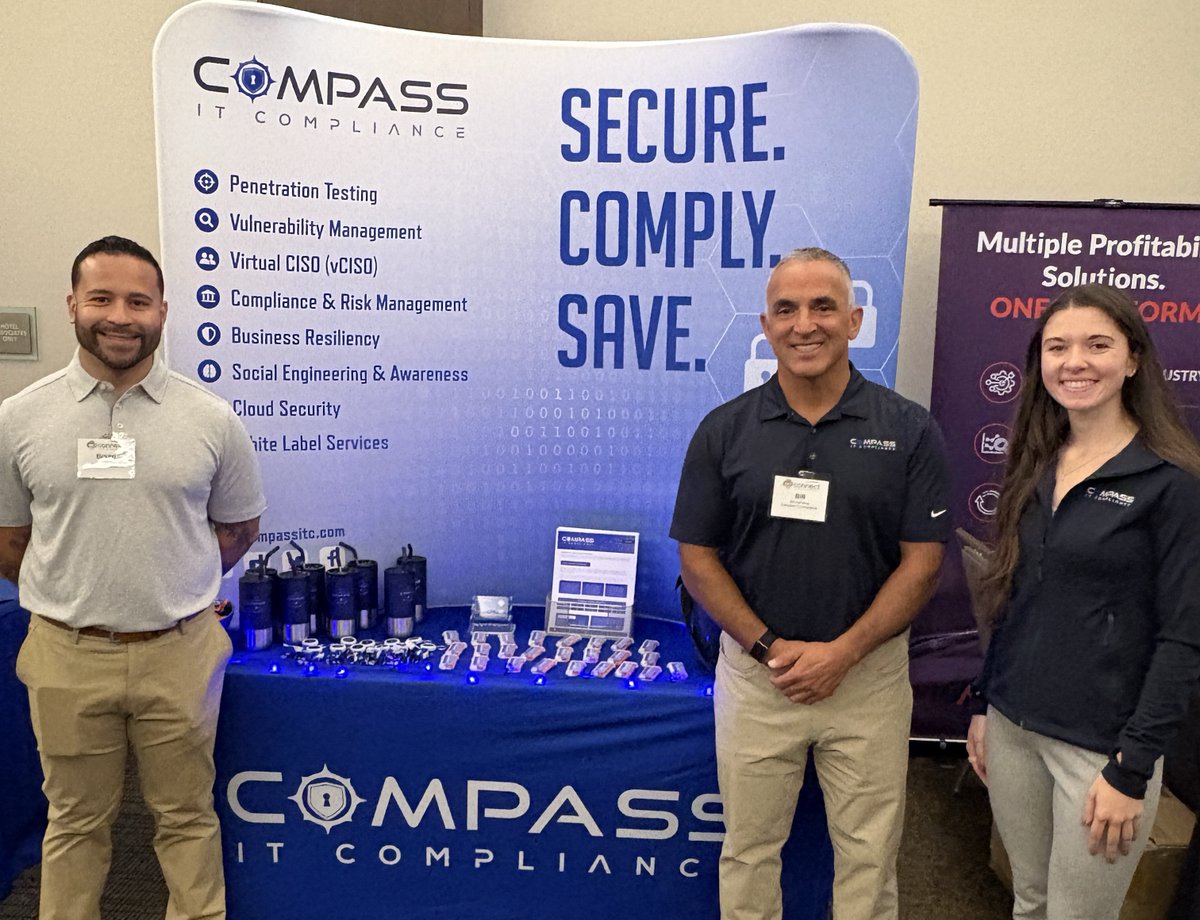
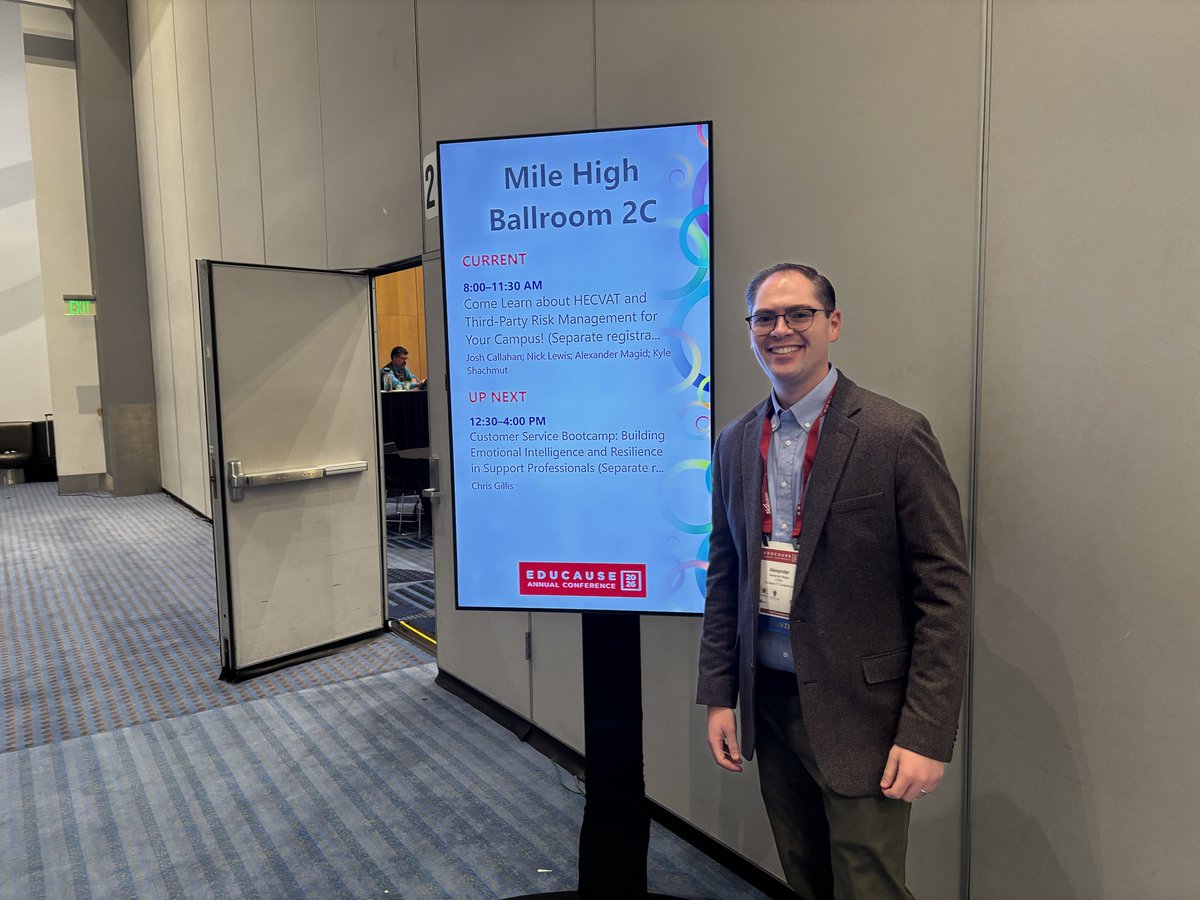
We had a great time at this year's EDUCAUSE Annual Conference in Denver. Thank you to everyone who stopped by to connect with us and joined Alex's session!
Regulators are building AI guidance for banks and credit unions. See what the CSBS AI Supervisory Framework asks about AI governance, inventory and vendor risk before your next exam.
https://t.co/fO7dxMW73o
The Compass IT Compliance team is exhibiting today at the MASSBUYS Expo at Gillette Stadium! As a longstanding Massachusetts statewide contract vendor, Compass is listed on state contract ITS78 for cybersecurity services.
https://t.co/VaGVeYyc2X
Compass IT Compliance is on the ground in Denver this week for the EDUCAUSE Annual Conference! Our team is excited to connect with higher ed technology leaders and dig into the #cybersecurity and #compliance challenges facing campuses today.
https://t.co/Osy1YZAmVm
Not every penetration test reduces ransomware risk the same way. Our latest blog explains what external, internal, and phishing assessments each reveal and how proper scoping keeps critical gaps from going untested.
https://t.co/Gm2G03gHOA
Cars aren't the only thing getting stolen at dealerships these days. Compass vCISO Robbie Harriman breaks down why dealers have become a favorite target for cybercriminals, and what you can actually do about it, in this recent webinar recording:
https://t.co/fvt2kNncEl
#Cybersecurity tools alone do not guarantee a paid insurance claim. At next week's Cloud Connect Summit, our own Derek Boczenowski, a 20-year compliance veteran, will detail why insurers are cracking down and the gaps that most often lead to denied claims.
https://t.co/64mGqh9qsc
We're on-site tomorrow at the Kansas City Technology Summit 2026, connecting with regional technology and #security leaders on today's top #cybersecurity and compliance challenges. Reach out if you'd like to connect with our team!
https://t.co/FcdK6vNfQN
Excited to hit the road for TechCon Unplugged 2026! This week we're heading to Chicago to connect with MSPs and industry leaders and swap real-world strategies for growing in today's IT landscape.
https://t.co/Z3bxAzovNl
We're excited to be exhibiting at the ISACA New England 50th Annual AGM this Thursday, September 10th at Gillette Stadium! Stop by our booth as we help celebrate this milestone anniversary alongside the New England #InfoSec community. See you there!
https://t.co/Qud9Lqwr5T
We're proud to be speaking at FirstLight's Cloud Connect Summit in Boston on September 24. Our Chief Architect, Derek Boczenowski, will be examining why insurers are denying more cyber claims and what organizations need in place to protect themselves.
https://t.co/1drQ6O45z2
CISA's new K-12 Cybersecurity Foundations Resource Package is a welcome step for a sector facing rising threats with limited staff and budget. Read our breakdown of the eight core objectives and where districts should start.
https://t.co/vBGFzeTxw3
Today, we took some time to celebrate our team at Compass HQ and enjoy an afternoon together outside of the usual workday. Between great food, some friendly competition, and plenty of laughs, it was a great way to spend the day with our team!
The best time to find a PCI DSS compliance gap is months before your assessment, not during it. Here's what a gap analysis typically turns up, and why it matters:
https://t.co/jeSY1BUFW9
SOC 2 audit quotes can vary widely, even for similar companies. Our latest post breaks down what actually drives audit cost so you can budget with confidence. Read more:
https://t.co/vlUDViNw12
Critical infrastructure faces threats beyond the network. Our latest blog shows how a physical security penetration test gained access to a water treatment facility's most sensitive equipment, and how to prevent it.
https://t.co/NtIbEURRlc
Great turnout at the Synergent Connect Conference this year! Thanks to everyone who stopped by our booth, attended our session, and joined the conversation on #cybersecurity and #compliance. We always come away energized by this amazing credit union community!
Scoping errors remain one of the costliest mistakes in PCI compliance, often long before a QSA ever reviews a control. Our latest post examines when an assessor is truly required, how merchant levels factor in, & what separates thorough due diligence ...
https://t.co/hGHHamAaqB
Excited for our team to be exhibiting & speaking at the Synergent Connect Conference next week, August 10-11 in Portland, Maine! We're looking forward to connecting with the credit union community & sharing our expertise in #cybersecurity & #compliance.
https://t.co/O3r7RcAy5M
The recent attacks on Minnesota's water utilities are a reminder of how exposed OT and ICS environments can be, even when nothing looks obviously wrong from the outside. Our latest post looks at what happened and what it means for organizatio...
https://t.co/4NKKgJjJmS