300 schools across Northern Ireland received emails threatening to blow up their buildings and kill students. Police assessed the threats as a hoax, with no explosive devices discovered at the time.
But how seriously should threats like these be taken? https://t.co/MYL2v2Pi6L
Tor is designed to protect your anonymity. Unfortunately, that doesn't mean your credentials are safe.
Attackers modified 342 Tor relays to enable SSH interception and password theft.
Read more about the attack: https://t.co/7P4KwyHRXY | #Cybersecurity#Tor#SSH
Have you taken our Physical Audit Certification Training course? Share your thoughts about your experience in the comments. 👇
There’s still time to join our November 21-22 PACT course–just enough time to roll out physical auditing as a service in 2027: https://t.co/0NVB5H28KG
Riots are spreading around (and even beyond) Europe. How would you advise your clients to protect themselves, their properties, and their livelihoods? Share your thoughts in the comments. 👇
Hear what Brian has to say about it: https://t.co/CEFseBCedU
Federal investigators suspect a cybersecurity executive helped ShinyHunters run its extortion infrastructure.
The FBI says the group collected $70M+ in 2026. Were ransomware negotiators involved?
Read more: https://t.co/G9wgyvqkBi
#Cybersecurity#Ransomware
A University of Wyoming researcher allegedly poisoned a coworker to steal his cancer research before returning to China.
Security footage reportedly caught her accessing his workspace after midnight.
Another disturbing insider threat case.
https://t.co/rktgKQchlE
Want to break into physical penetration testing? Start with audits.
They're a great way to gain experience and build a client base, while giving clients a faster, cheaper way to identify security flaws.
🎓 PACT Training | Nov 21–22
https://t.co/0NVB5H28KG
🚨 You can now get infected with spyware just by viewing an online ad. No clicks required.
Researchers uncovered "AdFection," a zero-click attack involving 75,000+ apps and 120,000+ websites.
Read now: https://t.co/1KTdGyJEnd | #CyberSecurity#Spyware
For $20–$40, you can buy a miniature listening device with an 18-hour battery, voice activation, and 16GB of storage.
But how useful are these devices during an actual physical penetration test?
Let's take a closer listen:
https://t.co/3vtKBQ56Xj
The EU spent €1.4 BILLION on a cyber early warning system.
But, not ONE member state has reported a "large-scale" incident since 2016.
WannaCry? Nope. CrowdStrike? Nope. Airport ransomware? Nope.
So what exactly is this system warning anyone about? https://t.co/tvZoCb9cuM
Three recent insider threat cases involving Berkeley, the University of Wyoming, and OpenAI highlight a serious problem with how organizations approach physical security.
Let's break down these three cases: https://t.co/v4hI2PnjBs
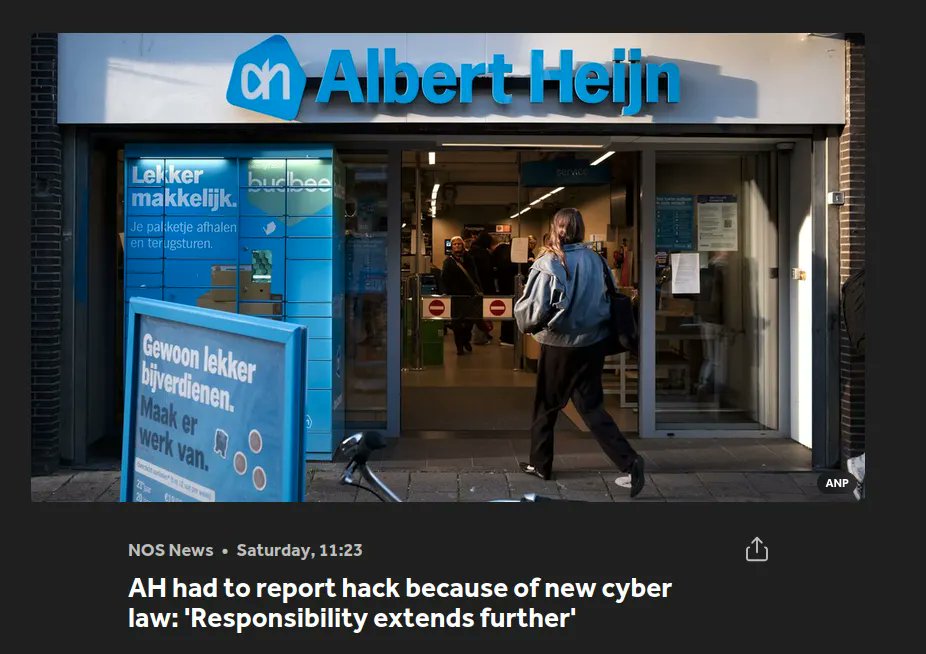
🚨 A cyber incident at Albert Heijn disrupted food deliveries and emptied shelves. Now the Dutch government is considering emergency food reserves.
Read the full story: https://t.co/IcydpY5QUB
Your next social engineering skill upgrade starts this weekend.
There’s still time to join us October 24–25 for our Elicitation Toolbox Training (ETT) course! Learn more and register: https://t.co/zluoStSdvw
#SocialEngineering#Elicitation#SecurityTraining#Pentesting
🔐 Your front door lock might look solid, but a few millimeters of exposed Eurocylinder can make it vulnerable to snapping.
Even worse, an attacker could potentially replace the lock without you noticing.
Do you know how secure your locks really are?
▶️ https://t.co/FbdsvlUfZO
Locks, cameras, action! 🎬 If your next physical penetration test had a soundtrack, this would be the opening track.
Because having security measures in place doesn't necessarily mean you're secure.
Listen: https://t.co/LGV1SIdP0o
An OpenAI engineer allegedly bugged an executive conference room, concealing the recording device with... toilet paper. 🧻
Would a wad of toilet paper behind your conference room TV raise suspicion?
Read now: https://t.co/7iUoAa73xx
Hackers reportedly raised refrigeration temperatures to 50°C across hundreds of French supermarkets, destroying food remotely.
As Europe connects more critical infrastructure to the Internet, are we creating more opportunities for attacks like this?
https://t.co/tck1ZobN6d
What if the insider threat is targeting YOU, not your organization?
A California engineer suffered repeated illnesses before a hidden camera caught her coworker contaminating her water: https://t.co/2GJHR0yG2f
Being trusted by an organization doesn't make someone trustworthy.
Could AI be making you more vulnerable to social engineering?
Getting frustrated with ChatGPT might seem harmless, but could those emotional habits carry over into real conversations, making you easier to manipulate?
▶️ https://t.co/8ZqCIsVSB8
Airports spend millions keeping threats OUT. But what if the threat is already in the cockpit?
A Flydubai co-pilot allegedly tried to seize control mid-flight, exposing a critical weakness in security: trusted insiders.
Read more: https://t.co/ZS66rNlDq6