#PHP2Shell (CVE-2026-109618, CVE-2026-109619, CVSS 9.2): RCE flaws in the #PHP core, no login needed. On default mod_php, one request is enough. Exploit attempts since Oct 17.
Patch to 8.5.12/8.4.27/8.3.36/8.2.35, then restart workers. https://t.co/B60DV7jk93
#CyberSecurity
CVE-2026-77524 (CVSS 9.9): Privilege escalation to cluster admin in KEDA.
KEDA doesn't validate Vault addresses in TriggerAuthentication. A tenant captures the operator's token and reads every Secret cluster-wide.
Patched in 2.21.0. Found by CyStack. https://t.co/We9R89cs6h
CVE-2026-91098, CVE-2026-91097: Two memory corruption flaws in HP HPLIP, the HP printer and scanner driver suite for Linux.
A heap overflow and an out-of-bounds write when parsing attacker-supplied data. No authentication, one user action, and the attacker has a path to code execution on the workstation or print server.
Patched in HPLIP 3.26.6. Found by a CyStack researcher. Details at https://t.co/jttYqwzWqR
#CyStack #CyberSecurity #Vulnerability #HP #HPLIP #Linux #EnterpriseSecurity #InfoSec
CVE-2026-84567, CVE-2026-86900: Two flaws in @Apple macOS file system drivers.
cd9660 mishandles memory when parsing ISO images, so an ordinary app can panic the kernel. exFAT trusts volume metadata, so a crafted USB drive or disk image triggers a kernel panic or leaks kernel memory.
All patched in macOS Golden Gate 27. Found by a CyStack researcher. Details at https://t.co/jttYqwzoBj
#CyStack #CyberSecurity #Vulnerability #Apple #macOS #EnterpriseSecurity #InfoSec
CVE-2026-94609: Privilege escalation to superuser in @AuthentikSec , the open-source SSO platform with 25.9k GitHub stars.
Superuser status is inherited through the group hierarchy, but the permission checks only looked at each group's own setting. A helpdesk account managing one group could promote itself to superuser.
Patched in 2026.2.7, 2026.5.7, 2026.8.2. Found by a CyStack researcher. Details at https://t.co/jttYqwzWqR
#CyStack #CyberSecurity #Vulnerability #authentik #SSO #IAM #EnterpriseSecurity #InfoSec
CVE-2026-85985: Authorization bypass in the CONNECT engine of @mariadb Server, the open-source database with 8.3k GitHub stars.
UDFs like json_file() and jfile_make() read and write files without checking the FILE privilege or secure_file_priv. A low-privileged SQL account reaches any file the MariaDB process can.
Patched in 10.6.28, 10.11.19, 11.4.13, 11.8.9, 12.3.3, 13.0.2. Found by a CyStack researcher. Details at https://t.co/jttYqwzWqR
#CyStack #CyberSecurity #Vulnerability #MariaDB #Database #EnterpriseSecurity #InfoSec
CVE-2026-84637: Thunderbird calendar invitations could launch executables on Windows.
A file URI attachment in a malicious invite bypasses Thunderbird's executable attachment protections and can show a misleading filename. The victim opens the invite, the attacker runs arbitrary programs.
Patched in v153.2. Found by a CyStack researcher. Details at https://t.co/jttYqwzWqR
#CyStack #CyberSecurity #Vulnerability #Mozilla #Thunderbird #InfoSec
The vulnerability exists in how the debugger caches a pointer to the Lua interpreter state and never refreshes it. SCRIPT FLUSH ASYNC recreates the engine and frees the old interpreter, so the next SCRIPT DEBUG command reads freed heap memory and crashes the server.
An attacker who reclaims that memory with a counterfeit interpreter state can take control of a function pointer, opening a path to code execution inside the database process.
CVE-2026-75889: Arbitrary file read in Grafana Alloy, the open-source telemetry agent from Grafana Labs that runs inside Kubernetes.
ServiceMonitor's bearerTokenFile field carries straight through into the scrape job. Point it at Alloy's own service account token, aim the scrape target at a server you control, and Alloy hands over its own credentials.
Patched in v1.19.0. Found by a CyStack researcher. Details at https://t.co/jttYqwzWqR
CVE-2026-76356: IP-spoofing auth bypass in the Automation Broker of Splunk SOAR, the SOAR platform used to automate incident response.
The broker trusts a client-supplied source IP header as proof of a local request. Spoof it, reach privileged functionality, no authentication needed, and execute arbitrary code on the host.
Patched in v8.6.0. Found by a CyStack researcher. Details at https://t.co/jttYqwzoBj
#CyStack #CyberSecurity #Vulnerability #Splunk #SOAR #RCE #EnterpriseSecurity #InfoSec
CVE-2026-61783: RBAC flaw in Wazuh Manager exposes cluster.key, the secret that authenticates inter-node cluster traffic.
The masking check only looks for a config-update RBAC rule, not whether it allows or denies the action. Attaching a deny rule is enough to get the raw key back from the config API.
Patched in v4.14.7 and v5.0.0-beta3. Found by a CyStack researcher. Details at https://t.co/jttYqwzWqR
#CyStack #CyberSecurity #CVE #CVE202661783 #Vulnerability #Wazuh #RBAC #EnterpriseSecurity #InfoSec
CVE-2026-8715: Arbitrary file read in HashiCorp's Vault Secrets Operator, the Kubernetes operator that syncs secrets from Vault.
The secretIDPath field never restricted which files it could point to. A namespaced tenant points it at a sensitive file on the operator pod, pairs it with a malicious VaultConnection, and exfiltrates the contents.
Patched in v1.5.0. Found by a CyStack researcher. Details at https://t.co/jttYqwzWqR
#CyStack #CyberSecurity #Vulnerability #HashiCorp #Vault #Kubernetes #EnterpriseSecurity #InfoSec
CVE-2026-59119: Privilege escalation flaw in Microsoft PowerShell, the command-line tool installed by default on most Windows systems.
Overly broad default permissions on an internal operation. An attacker with a local foothold, even at low privilege, exploits it to gain SYSTEM.
Patched in v7.4.19, v7.5.10, v7.6.5. Found by a CyStack researcher. Details at https://t.co/jttYqwzWqR
#CyStack #CyberSecurity #Vulnerability #Microsoft #PowerShell #PrivilegeEscalation #InfoSec
CyStack and NTQ Solution have launched Sentrix, a joint venture delivering full-lifecycle cybersecurity to global enterprises. Combining research and offensive security depth from CyStack and delivery and operations across 20+ countries from NTQ, Sentrix provides reliable and effective security solutions for clients worldwide.
Learn more at https://t.co/ElRqJdzcbt
#NTQ #CyStack #Sentrix #Cybersecurity #SOC #PenetrationTesting #DigitalTransformation
CVE-2026-58040: TLS session reuse in Node.js's HTTPS Agent can skip hostname verification.
An incomplete fix for CVE-2026-48934. Reuse a session across different identity policies and the certificate check for the new host gets bypassed.
Affects 22.x, 24.x, 26.x. Patched in v22.23.2, v24.18.1, v26.5.1. Found by a CyStack researcher. Details at https://t.co/jttYqwzWqR
3 vulnerabilities in RabbitMQ, the open-source message broker widely used in microservices architectures, finance, and e-commerce systems.
CVE-2026-67415: Atom exhaustion via the Shovel plugin, pushing the broker into prolonged DoS, requires a restart.
CVE-2026-67366: The Federation plugin skips vhost permission checks, allowing cross-tenant access.
CVE-2026-67408: Super Streams exhausts resources before the permission check, hanging the node or causing DoS.
Patches are available. Found by CyStack researchers. Details at https://t.co/jttYqwzWqR
#CyStack #CyberSecurity #Vulnerability #RabitMQ #InfoSec
CyStack has updated its analysis of CVE-2026-60747: a single packet drops a MySQL replica into a crash loop. A free-of-memory-not-on-the-heap bug (CWE-590) in MySQL replication's heartbeat decoder.
Details from Phuc Nguyen (pucagit) https://t.co/AvBU9sU3v0
#CyStack#MySQL#CVE
CVE-2026-40691: Heap overflow in Unbound, one of the most widely deployed open-source DNS resolvers with 4.7k GitHub stars.
Send one DNSCrypt query over TCP. Reply overflows the heap. Resolver crashes. Users behind it lose DNS.
Patched in v1.25.2. Found by a CyStack researcher. For more vulnerabilities, visit https://t.co/jttYqwzoBj
#CyStack #CyberSecurity #Vulnerability #Unbound #DNS #DNSCrypt #DoS #EnterpriseSecurity #InfoSec #CVE
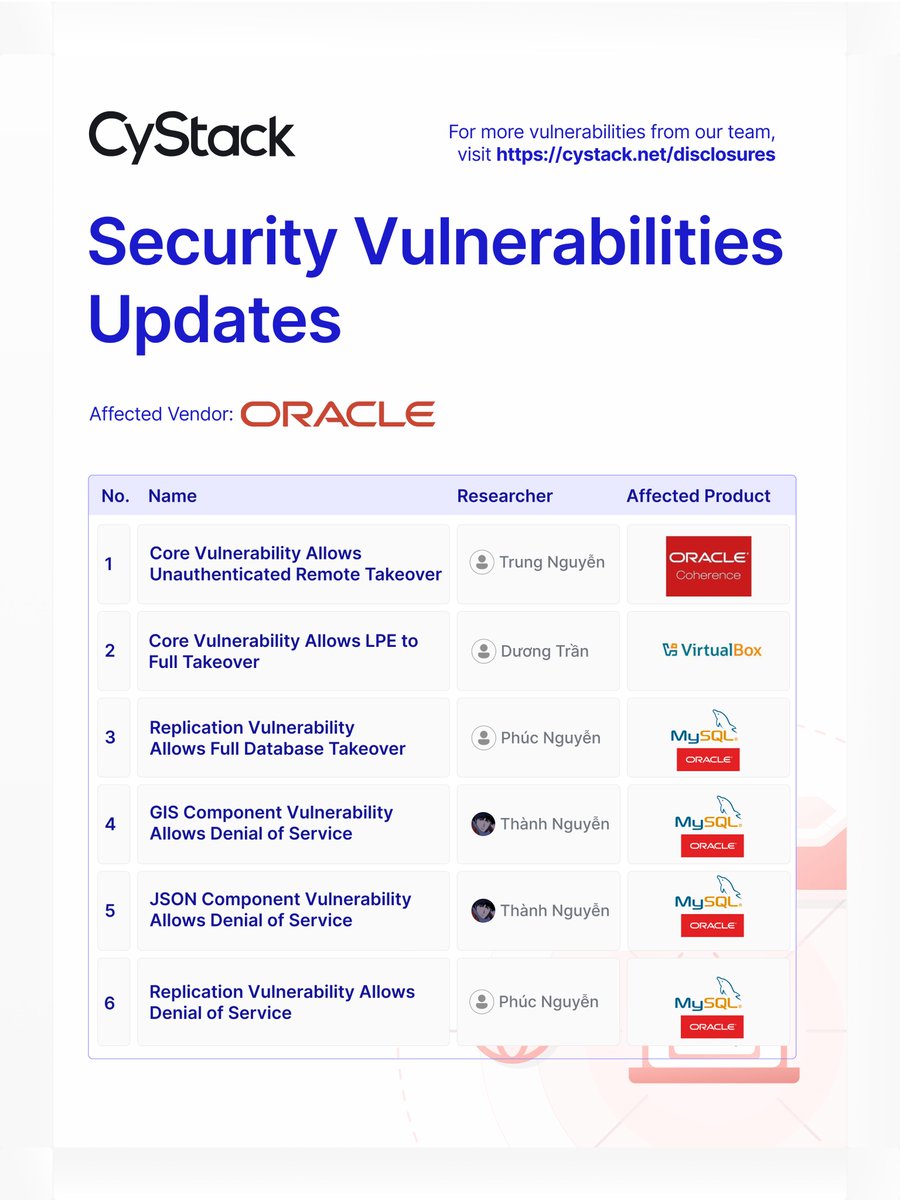
🚨 SECURITY ADVISORY
CyStack researchers responsibly disclosed 6 vulnerabilities across Oracle VM VirtualBox, Coherence & MySQL Server, all fixed in Oracle's July 2026 Critical Patch Update.
For more, visit https://t.co/We9R89cs6h
#CyStack#Oracle#CyberSecurity#InfoSec