Excited to disclose my research allowing RCE in Kubernetes
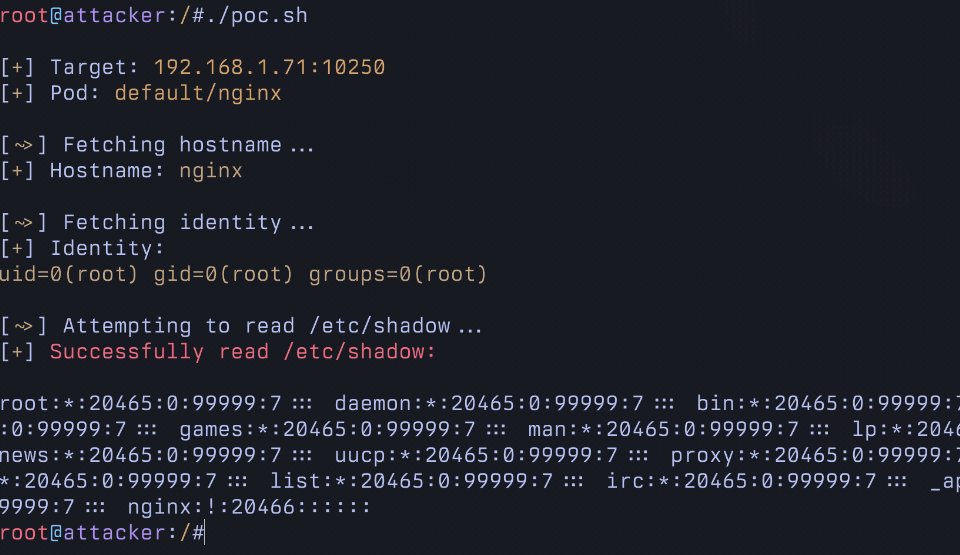
It allows running arbitrary commands in EVERY pod in a cluster using a commonly granted "read only" RBAC permission. This is not logged and and allows for trivial Pod breakout.
Unfortunately, this will NOT be patched.
Just finished the #EKSClusterGames by @Wiz_io! 🚀 An amazing journey through Amazon EKS configurations! Ready to test your skills? Join the challenge here: https://t.co/cb2DjT5dRk
https://t.co/T23vfGEUAN
Constellation is a Kubernetes engine that wraps your cluster into a single confidential context that is shielded from the underlying cloud infrastructure
Everything inside is always encrypted, including at runtime in memory
➤ https://t.co/kHaYYN9Yl8
In this article, learn how ReadOnlyRootFilesystem enhances container security by enforcing immutability, thwarting attacks, and ensuring consistent deployments
➜ https://t.co/HzJMilep8o
This article describes the challenges and solutions to connecting kubectl from your local computer to a private GKE cluster while impersonating a service account
➤ https://t.co/2bcLH58c0A
#WATCH | Prime Minister Narendra Modi met Team India in their dressing room after the ICC World Cup Finals at Narendra Modi Stadium in Ahmedabad, Gujarat on 19th November.
The PM spoke to the players and encouraged them for their performance throughout the tournament.
(Video: PMO)
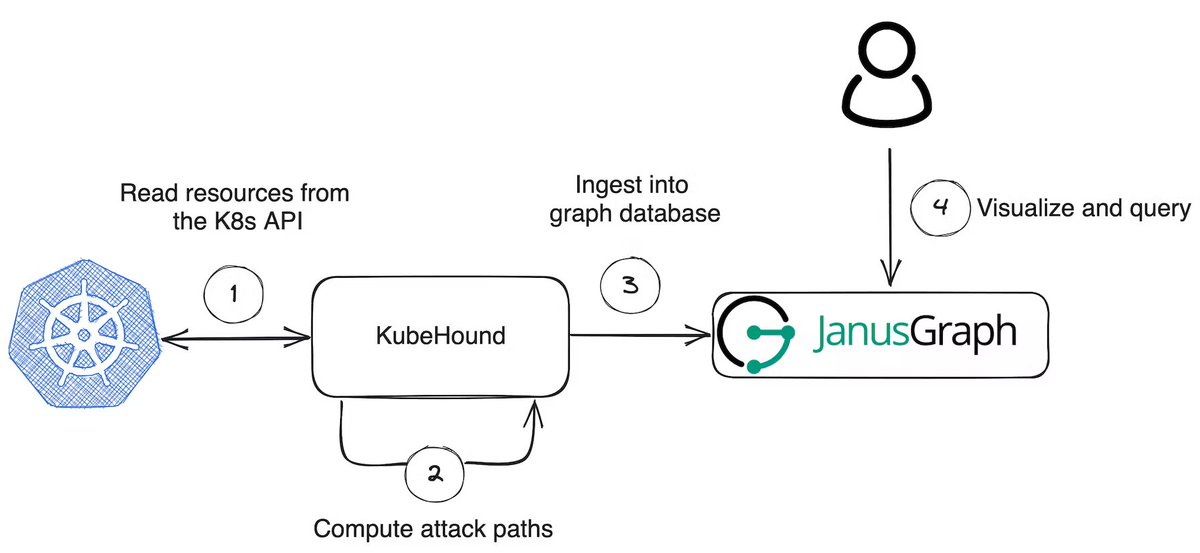
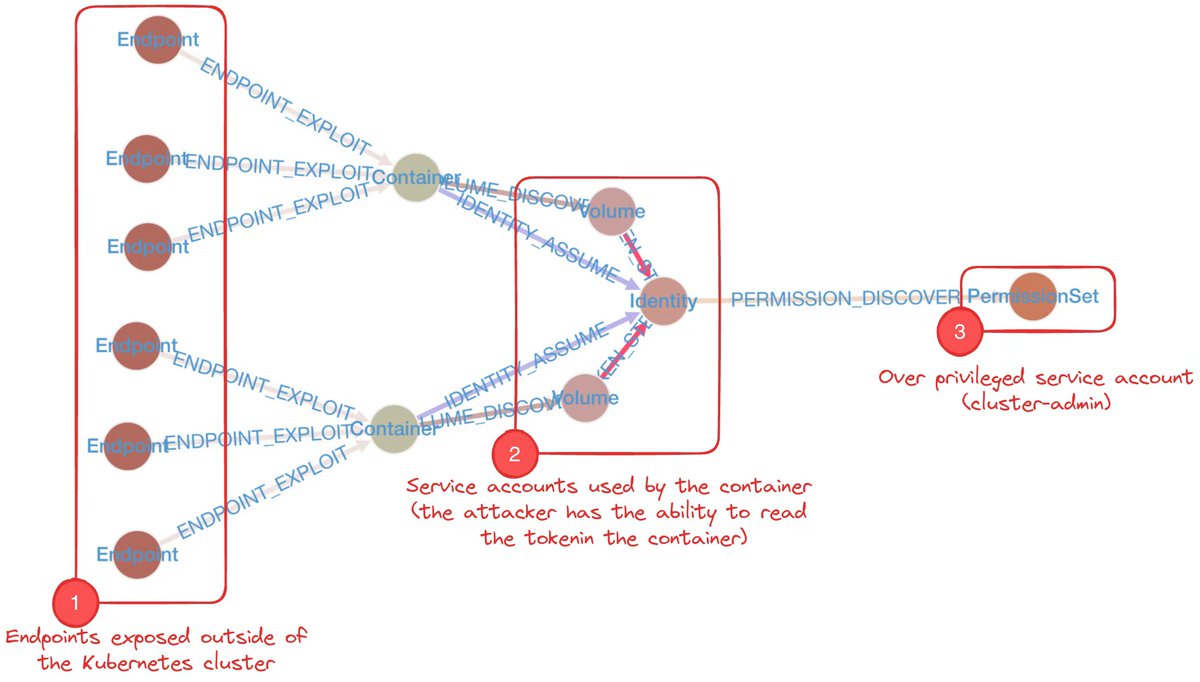
Datadog's security team has just released KubeHound, an open-source attack mapping tool for Kubernetes clusters
https://t.co/1NaHHIfznN
https://t.co/rwWQFHY4kT
Comes with 25 attack types, each one comes with step by step instructions of how to exploit it
Putting together some information in my blog as a starting point for Kubernetes security. Focus is around basics of cluster and its setup in local environment. https://t.co/ABlodWTClV