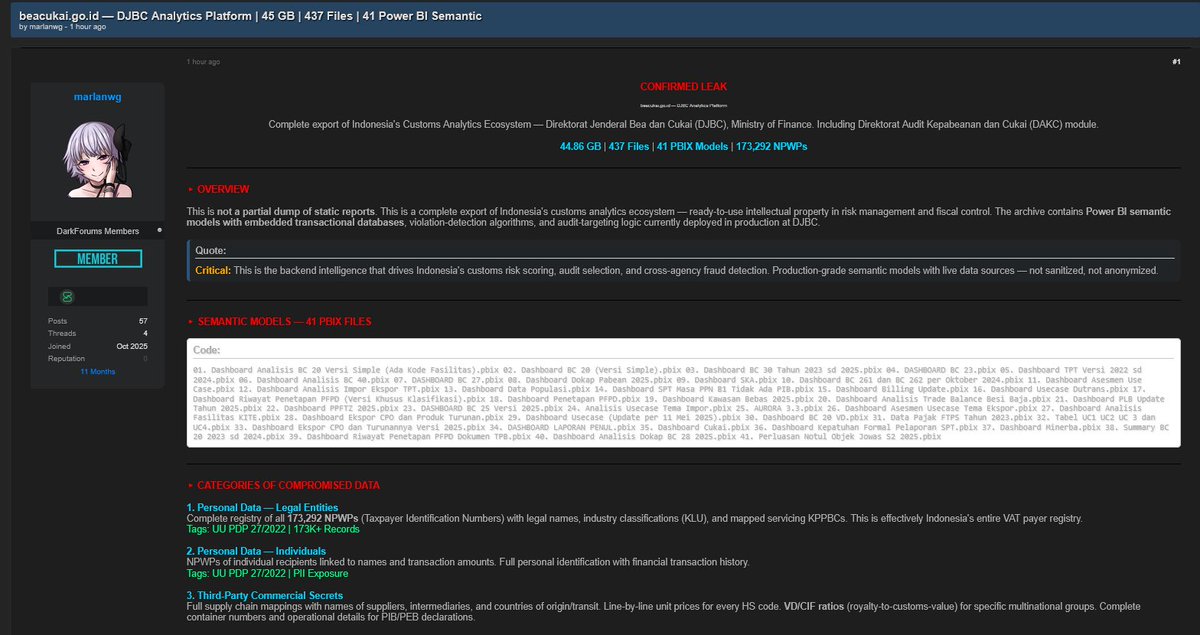
‼️🇮🇩 ALLEGED MAJOR DATA LEAK – INDONESIAN CUSTOMS (DJBC)
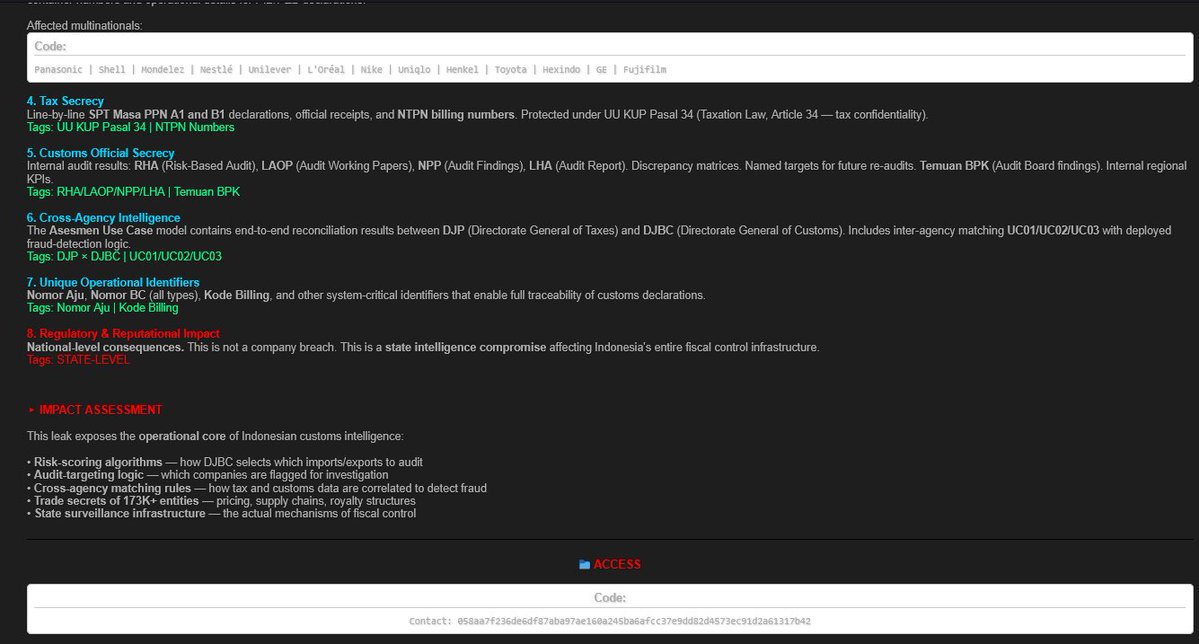
Threat actor marlanwg claims a 44.86 GB export of the Direktorat Jenderal Bea dan Cukai (DJBC) analytics ecosystem, including the Direktorat Audit Kepabeanan dan Cukai (DAKC) module.
📊 Claimed exposure:
• 437 files
• 41 Power BI (.PBIX) semantic models
• 173,292 NPWPs allegedly included
• Taxpayer/legal-entity information
• Individual taxpayer and transaction data
• Supplier, intermediary & country-of-origin mappings
• HS-code unit pricing and customs-value data
• Container numbers and PIB/PEB declaration details
• Tax declarations, receipts & NTPN billing numbers
• Customs audit records and findings
• Cross-agency DJP–DJBC reconciliation data
• Risk-scoring & audit-targeting logic
• Billing and customs operational identifiers
🖥️ The accompanying material also claims exposure of RHA/LAOP/NPP/LHA audit information, UC01/UC02/UC03 fraud-detection rules, Nomor Aju/Nomor BC and billing identifiers, alongside operational intelligence described as supporting customs risk scoring and audit selection.
⚠️ The claimed 44.86 GB leak, 437 files, 173,292 records, production use, authenticity and extent of access have not been independently verified. Sensitive taxpayer, financial and operational information is not reproduced.
#CyberSecurity #DataBreach #DataLeak #Indonesia #Customs #DJBC #ThreatIntelligence
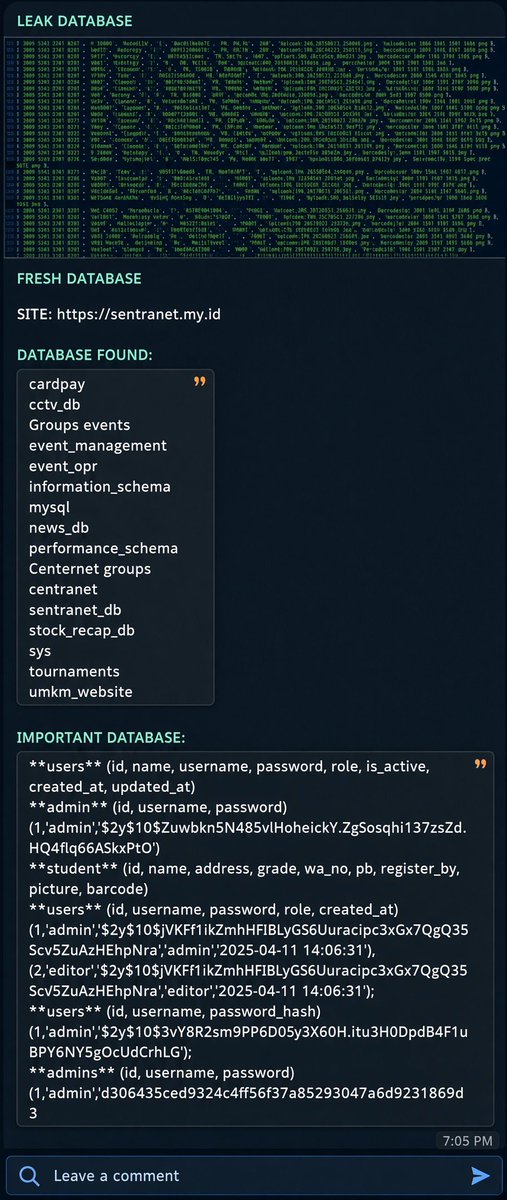
‼️🇮🇩 ALLEGED DATABASE LEAK – https://t.co/LCfW9yUsOw
A post claims a fresh database exposure involving https://t.co/2HrnRKtA10, with a 41.5 KB ZIP archive allegedly containing multiple databases.
📂 Claimed databases include:
• sentranet_db
• centranet
• cardpay
• cctv_db
• event_management / event_opr
• news_db
• stock_recap_db
• tournaments
• umkm_website
• Student and user-management databases
🔐 Claimed fields include: names, usernames, password hashes, roles, account timestamps, student addresses, phone/WhatsApp numbers and administrative records.
⚠️ The alleged breach, database contents, authenticity, affected systems and extent of exposure have not been independently verified. Password hashes, credentials and other sensitive data from the post are not reproduced.
#CyberSecurity #DataBreach #DataLeak #Indonesia #ThreatIntelligence #OSINT #DatabaseSecurity
‼️ALLEGED INITIAL ACCESS FOR SALE – ONE SOTHEBY’S INTERNATIONAL REALTY
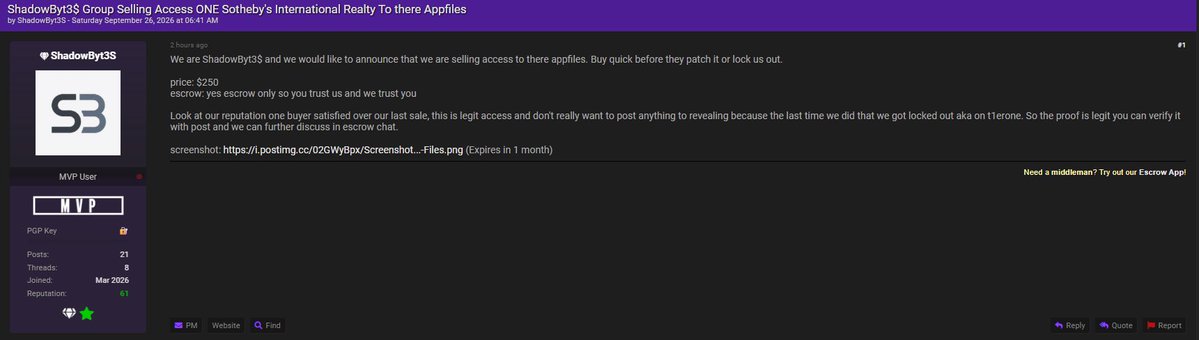
Threat actor ShadowByt3S claims to be selling access to AppFiles associated with ONE Sotheby’s International Realty.
💰 Asking price: $250
🔐 Claimed access: AppFiles environment
🤝 Escrow: Seller states escrow is required
📸 A screenshot is cited as alleged proof of access.
The seller claims the access is legitimate and warns that the target may patch the suspected weakness or revoke access.
⚠️ The claimed access, affected systems, vulnerability, seller attribution and validity of the proof have not been independently verified. No credentials or access-enabling information is reproduced.
#CyberSecurity #InitialAccess #DataBreach #ThreatIntelligence #RealEstate #Sothebys
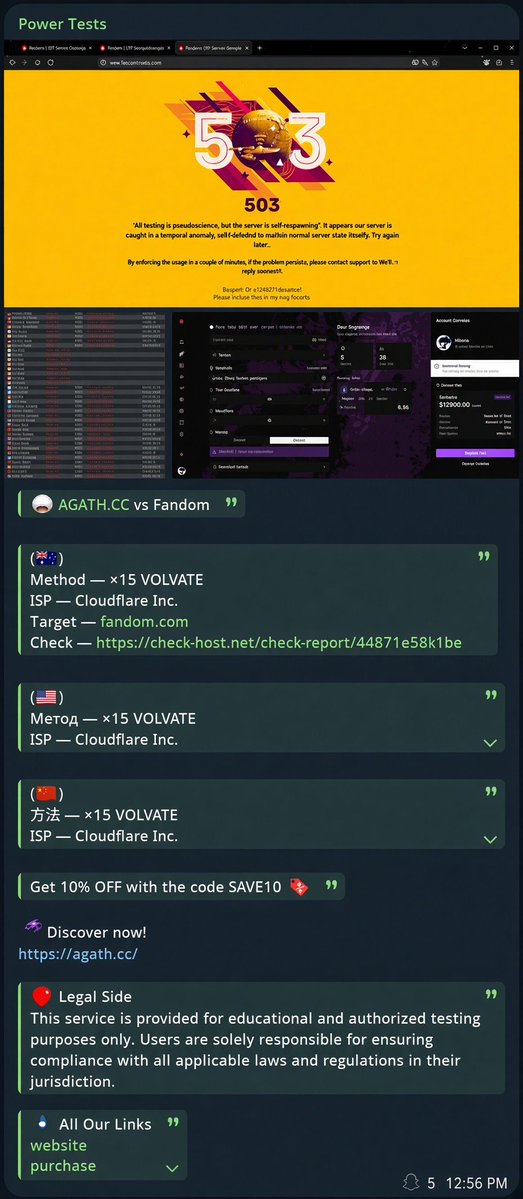
‼️ALLEGED DDoS-FOR-HIRE SERVICE – “https://t.co/zlCoIOVbO1”
An underground advertisement promotes a service allegedly offering stress-testing / traffic-generation services, with a sample targeting https://t.co/PeGPkP268o.
🔎 Advertised details:
• Target: https://t.co/JZcNtic77e
• Method: “x15 VOLVATE”
• ISP/CDN: Cloudflare Inc.
• Claimed check-host connectivity report
• Service advertised for $12,900
• Claims of “educational and authorized testing”
The post also advertises promotional discounts and a web storefront.
⚠️ The advertised capabilities, pricing, infrastructure and claims have not been independently verified. No operational instructions or attack-enabling details are reproduced.
#CyberSecurity #DDoS #ThreatIntelligence #CyberCrime #Fandom #Cloudflare #OSINT
‼️UNDERGROUND FORUM SHOP UPDATE – “GORZ ROSTAM”
An underground forum post advertises a “Forum Shop Rostam” with a bot-based storefront and support channel, reportedly updated September 26, 2026.
📂 Listed files:
• ae_full_update_2026_09_25.txt — 249.1 KB
• bh_full_update_2026_09_25.txt — 65.9 KB
• il_full_update_2026_09_25.txt — 156.8 KB
• qa_full_update_2026_09_25.txt — 51.1 KB
• sa_full_update_2026_09_25.txt — 675.8 KB
• us_full_update_2026_09_25.txt — 356.4 KB
The filenames appear to correspond to datasets associated with UAE, Bahrain, Israel, Qatar, Saudi Arabia and the United States.
⚠️ The contents, provenance, authenticity and legality of the advertised datasets have not been independently verified. The storefront is presented as underground-market activity; no sensitive data is reproduced.
#CyberSecurity #DarkWeb #DataLeak #ThreatIntelligence #OSINT #CyberCrime
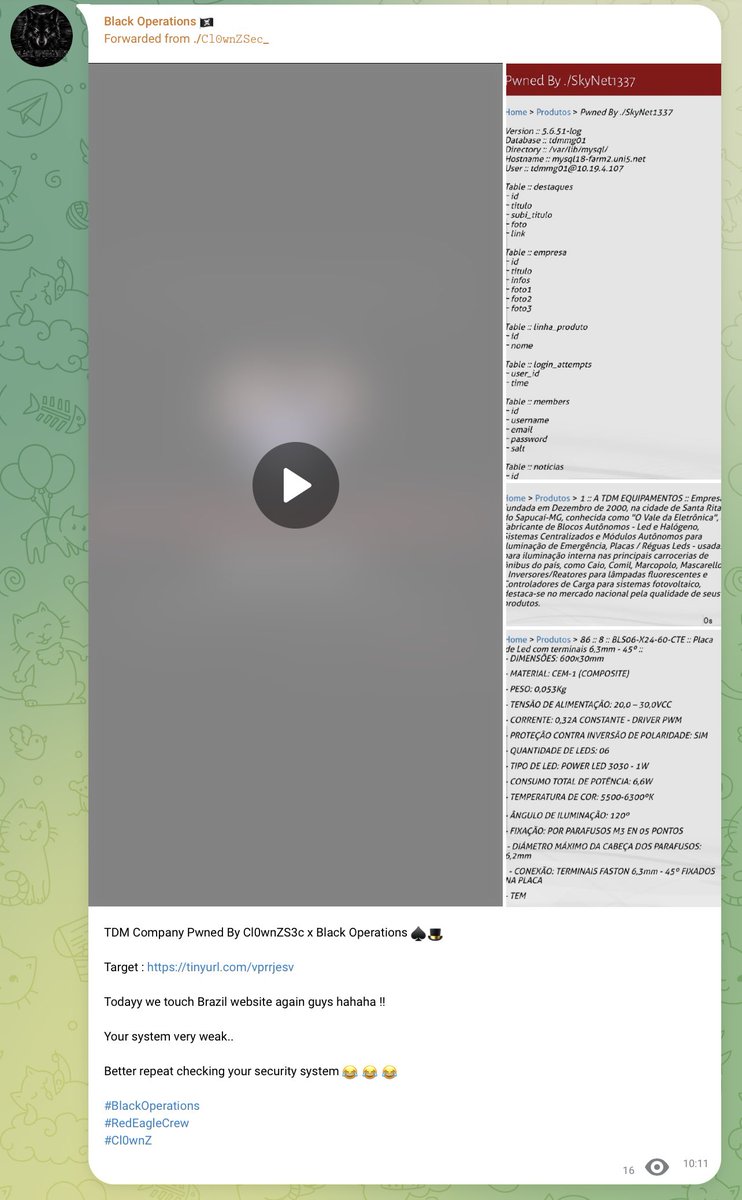
‼️🇧🇷 ALLEGED WEBSITE COMPROMISE – TDM EQUIPAMENTOS
A threat actor claiming affiliation with Black Operations / Cl0wnZSec alleges a compromise of TDM Equipamentos, a Brazilian manufacturer of emergency lighting and LED products.
🔎 Claimed exposure:
• MySQL database directory and configuration details
• Product, company and news tables
• Login-attempt records
• Member accounts containing usernames, emails & password-related fields
• Website product information
The post displays a “Pwned By” defacement message and claims the target’s security was weak.
⚠️ The compromise, database exposure, attribution and extent of unauthorized access have not been independently verified. Passwords, salts, credentials and infrastructure-sensitive details are not reproduced.
#CyberSecurity #WebsiteDefacement #DataBreach #Brazil #TDM #ThreatIntelligence #BlackOperations
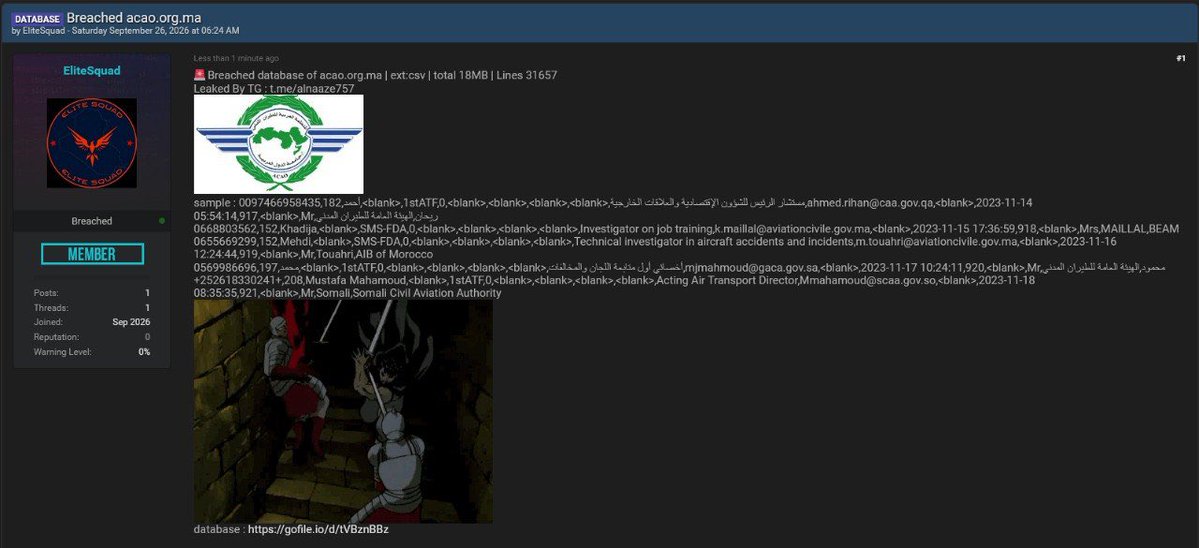
‼️🇲🇦 ALLEGED DATABASE LEAK – https://t.co/jpCcltbsGz
Threat actor EliteSquad claims to have breached https://t.co/QhkQpsgkLD, allegedly exposing a CSV database.
📊 Claimed dataset:
• 31,657 records/lines
• 18 MB CSV file
• Aviation-sector personnel information
• Names, job roles & organizational details
• Work email addresses & phone numbers
• Investigation/training-related information
• Records allegedly referencing aviation authorities in Morocco and other countries
The post includes samples containing aviation personnel and civil aviation authority records.
⚠️ The alleged breach, dataset authenticity, record count, provenance and scope of exposure have not been independently verified. Personal contact details are not reproduced.
#CyberSecurity #DataBreach #DataLeak #Morocco #Aviation #ThreatIntelligence #OSINT
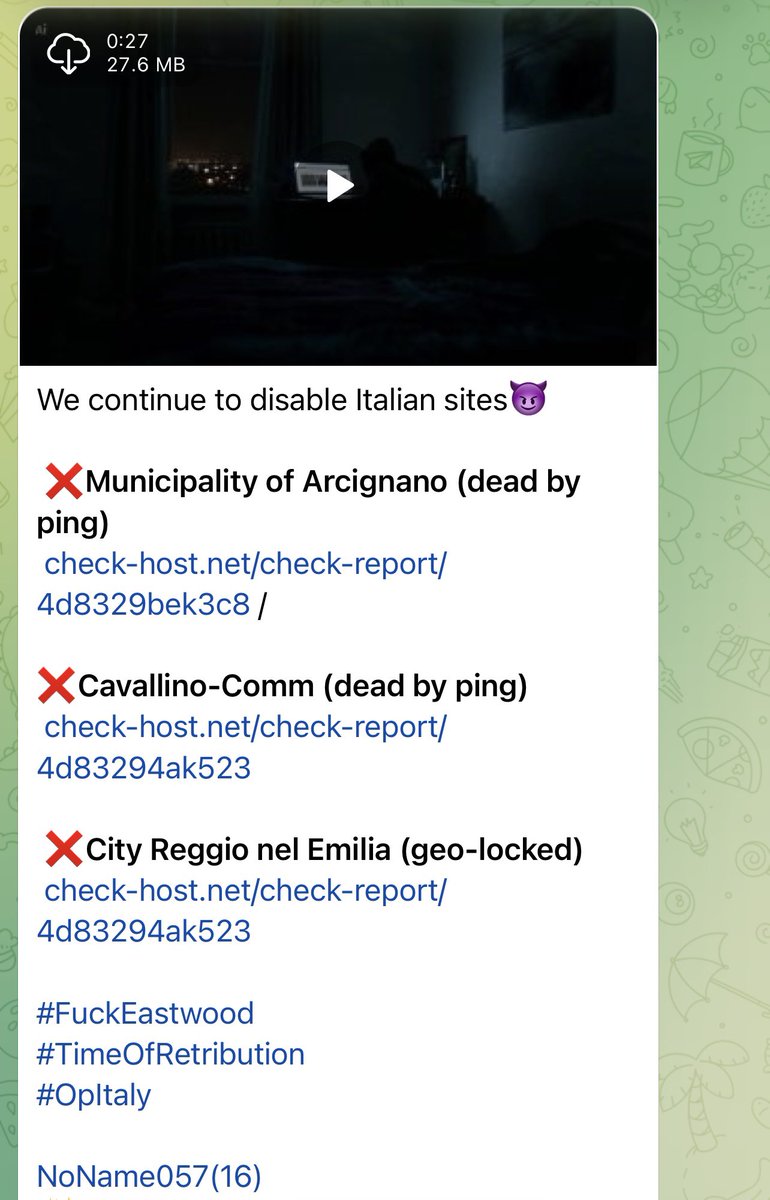
‼️🇮🇹 ALLEGED CYBERATTACKS – ITALIAN MUNICIPAL WEBSITES
The pro-Russian hacktivist group NoName057(16) claims to have targeted multiple Italian websites as part of an ongoing campaign.
🎯 Reported targets:
• Municipality of Arcugnano — reportedly unreachable by ping
• XCavallino-Comm — reportedly unreachable by ping
• City of Reggio nell’Emilia — reportedly geo-locked
⚠️ The reported targeting, attribution, impact and cause of the observed connectivity issues have not been independently verified. A failed ping or geo-block does not by itself confirm a successful cyberattack.
#CyberSecurity #CyberAttack #Italy #NoName05716 #Hacktivism #ThreatIntelligence
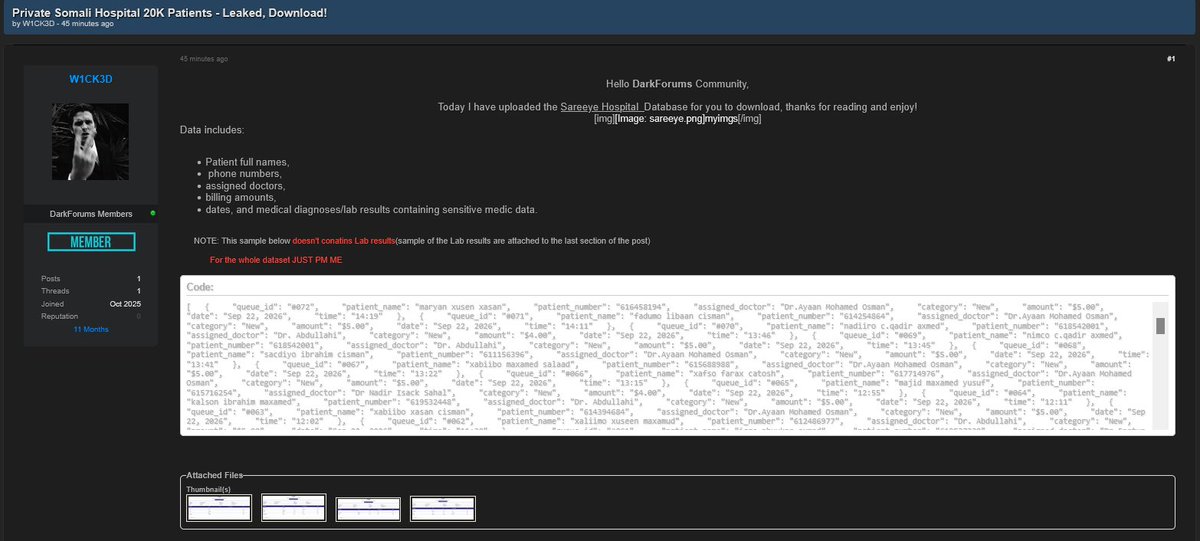
‼️🇸🇴 ALLEGED HEALTHCARE DATABASE LEAK – SAREEYE HOSPITAL
A threat actor W1CK3D claims to have leaked a database allegedly belonging to Sareeye Hospital, a private hospital in Somalia.
📊 Claimed data includes:
• Patient names & identification numbers
• Phone/contact information
• Assigned doctors
• Visit dates & queue details
• Billing/payment amounts
• Medical diagnoses and laboratory results
The actor claims the database contains information on approximately 20,000 patients and has reportedly shared sample records while offering the full dataset for download.
⚠️ The alleged breach, patient count, dataset authenticity and scope have not been independently verified. No medical records, patient identifiers or other sensitive health information are reproduced.
#CyberSecurity #DataBreach #DataLeak #Somalia #HealthcareSecurity #PatientData #ThreatIntelligence
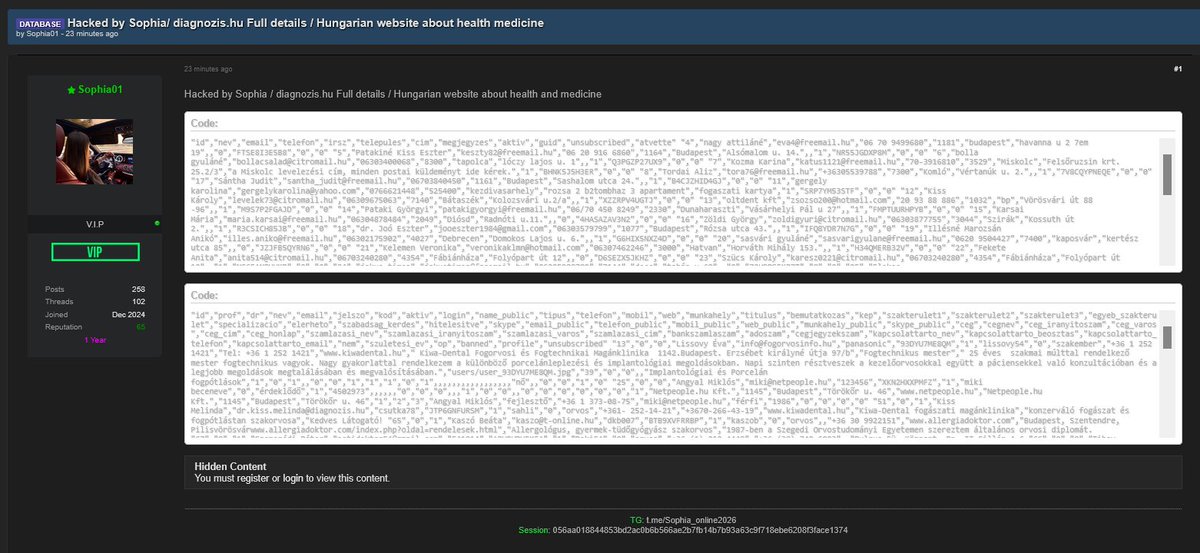
‼️🇭🇺 ALLEGED DATABASE LEAK – https://t.co/cdBYe5PAXL
A threat actor Sophia01 claims to have compromised https://t.co/xvjOGEMrEt, a Hungarian website focused on health and medical information.
📊 Claimed exposed data includes:
• User/profile records
• Names, email addresses & phone numbers
• Login/account information
• Professional profiles and medical specialties
• Workplace and business details
• Public/private contact information
• Tax and company registration fields
• Alleged password-related fields
The sample appears to contain information associated with healthcare professionals and organizations.
⚠️ The alleged compromise, dataset authenticity, scope and unauthorized access have not been independently verified. Medical-related personal data, credentials and other sensitive information from the sample are not reproduced.
#CyberSecurity #DataBreach #DataLeak #Hungary #Diagnozis #HealthcareSecurity #ThreatIntelligence
‼️🇫🇷 ALLEGED DATABASE LEAK – https://t.co/s1RWtkBkti
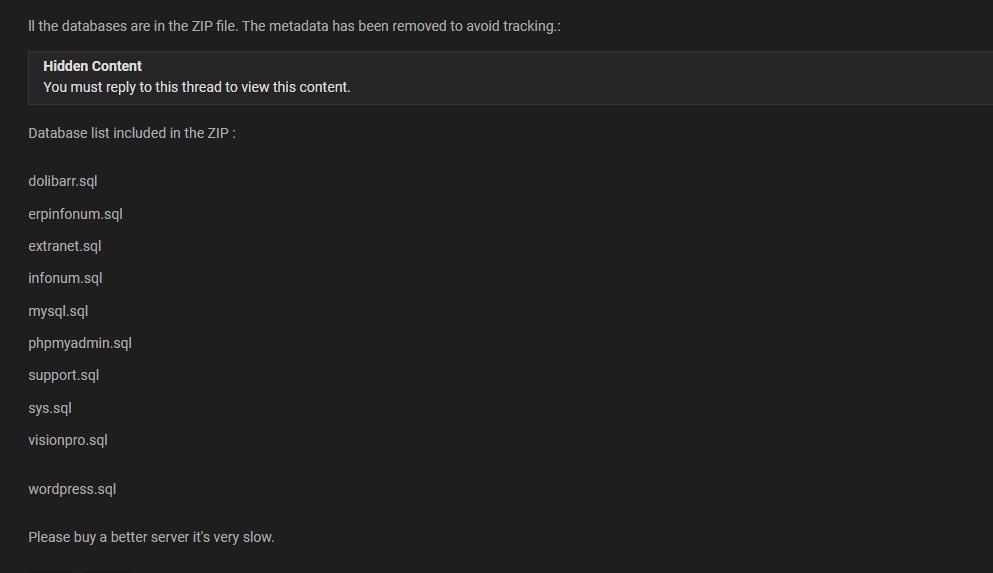
A threat actor imsolazymean claims to have leaked databases allegedly belonging to Aestria, described in the post as a French cybersecurity company.
📂 Claimed database files include:
• dolibarr.sql
• erpinfonum.sql
• extranet.sql
• infonum.sql
• mysql.sql
• phpmyadmin.sql
• support.sql
• sys.sql
• visionpro.sql
• wordpress.sql
The actor also claims exploitation of an LFI vulnerability, access to a web console and exposure of a WordPress login endpoint.
⚠️ The alleged compromise, vulnerability, database contents, and extent of access have not been independently verified. Credentials, account details and exploit instructions are not reproduced.
#CyberSecurity #DataLeak #DataBreach #France #Aestria #ThreatIntelligence
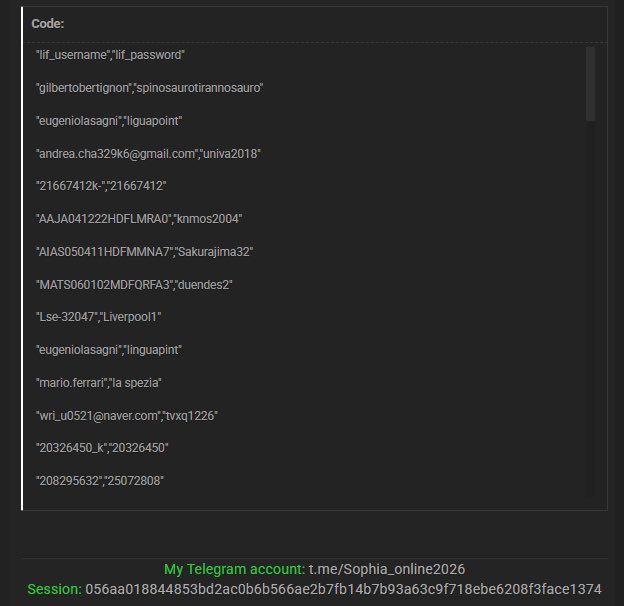
‼️🇪🇸 ALLEGED DATABASE FOR SALE – https://t.co/JZIrn6Xl7Z
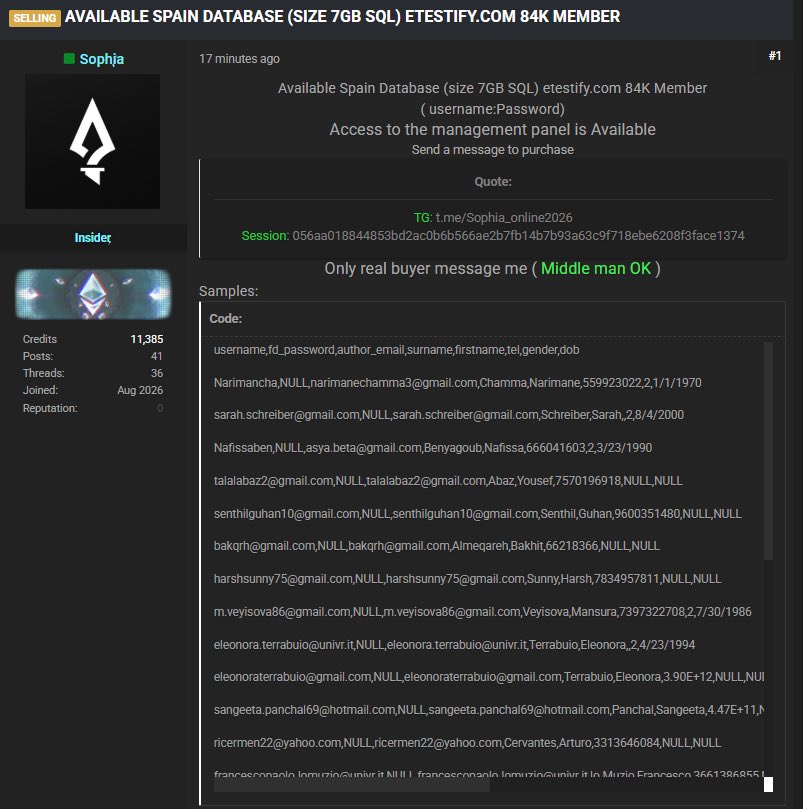
A threat actor Sophia claims to be selling an alleged 7 GB SQL database associated with https://t.co/UXDjnJZc9M, reportedly containing information on approximately 84,000 members.
📊 Claimed exposure:
• Usernames & passwords
• Email addresses
• Names and surnames
• Telephone numbers
• Gender & dates of birth
• Alleged management-panel access
The seller has posted sample records and claims the database is available for purchase.
⚠️ The alleged breach, dataset size, member count, credentials, and claimed management-panel access have not been independently verified. Actual passwords, personal data, session tokens and contact details are not reproduced.
#CyberSecurity #DataLeak #DataBreach #Spain #ETestify #ThreatIntelligence
‼️🇩🇴 ALLEGED DATABASE LEAK – ABX COURIER
A threat actor AlexG4Cvv2 claims to be selling a database allegedly linked to https://t.co/zlDJDViuvN, a Dominican Republic courier service.
📊 Claimed dataset:
• 263,828 lines / 263,603 data records
• 20 tables / 169 columns
• Customer names, IDs, RNCs, emails & phone numbers
• Addresses, account balances & passwords
• Payment and transaction records
• Invoices, credit/debt records & supplier data
• Payment tokens and user-token records
• Banking/account information
• Payment gateway and API configuration data
The post advertises the dataset for $500 USD and includes samples allegedly containing customer, financial, invoice and payment-system information.
⚠️ The alleged breach, dataset size, authenticity, and extent of access have not been independently verified. Credentials, tokens, and sensitive financial information are not reproduced.
#CyberSecurity #DataBreach #DataLeak #DominicanRepublic #ABXCourier #ThreatIntelligence
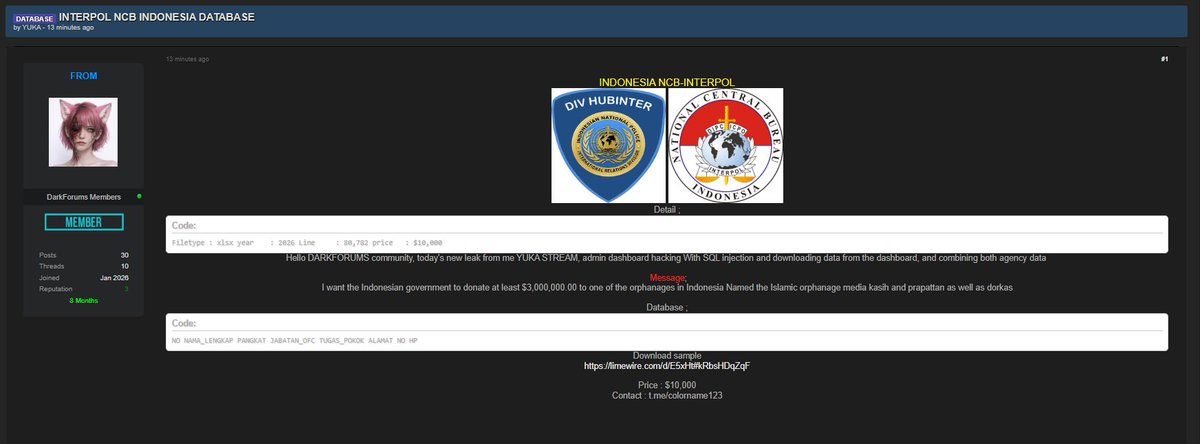
‼️🇮🇩 ALLEGED DATABASE LEAK – INTERPOL NCB INDONESIA
A threat actor YUKA claims to have compromised the Indonesia NCB-INTERPOL / Hubinter infrastructure and allegedly obtained agency personnel data through SQL injection.
📊 Claimed dataset: ~80,782 records
• Full names
• Ranks
• Official positions
• Duties/responsibilities
• Addresses
• Phone numbers
The actor claims access to an administrative dashboard and alleges that data from two agencies was combined. The database is reportedly being offered for $10,000.
⚠️ The alleged compromise, attack method, record count, dataset authenticity, and extent of access have not been independently verified. Sensitive personal information is not reproduced.
#CyberSecurity #DataBreach #DataLeak #Indonesia #INTERPOL #ThreatIntelligence #OSINT
‼️ALLEGED DATABASE BREACH – ONEKEY
A threat actor claims a breach of OneKey Hardware Wallet / Prime app user signup data, allegedly obtained through a misconfigured Supabase Row-Level Security (RLS) configuration.
📊 Claimed dataset: ~39,000 rows
• Email addresses
• Privy IDs
• Supabase user IDs
• Account creation timestamps
The actor claims the exposure involved the privy_user table and says proof of submission to OneKey was obtained, with further proof allegedly available privately.
⚠️ The breach, dataset size, vulnerability, and extent of exposure have not been independently verified. No sensitive credentials or private user data are reproduced here.
#CyberSecurity #DataBreach #DataLeak #OneKey #CryptoSecurity #ThreatIntelligence #Supabase
‼️🇫🇷 ALLEGED DATA BREACH – https://t.co/VlRkJ6UU25
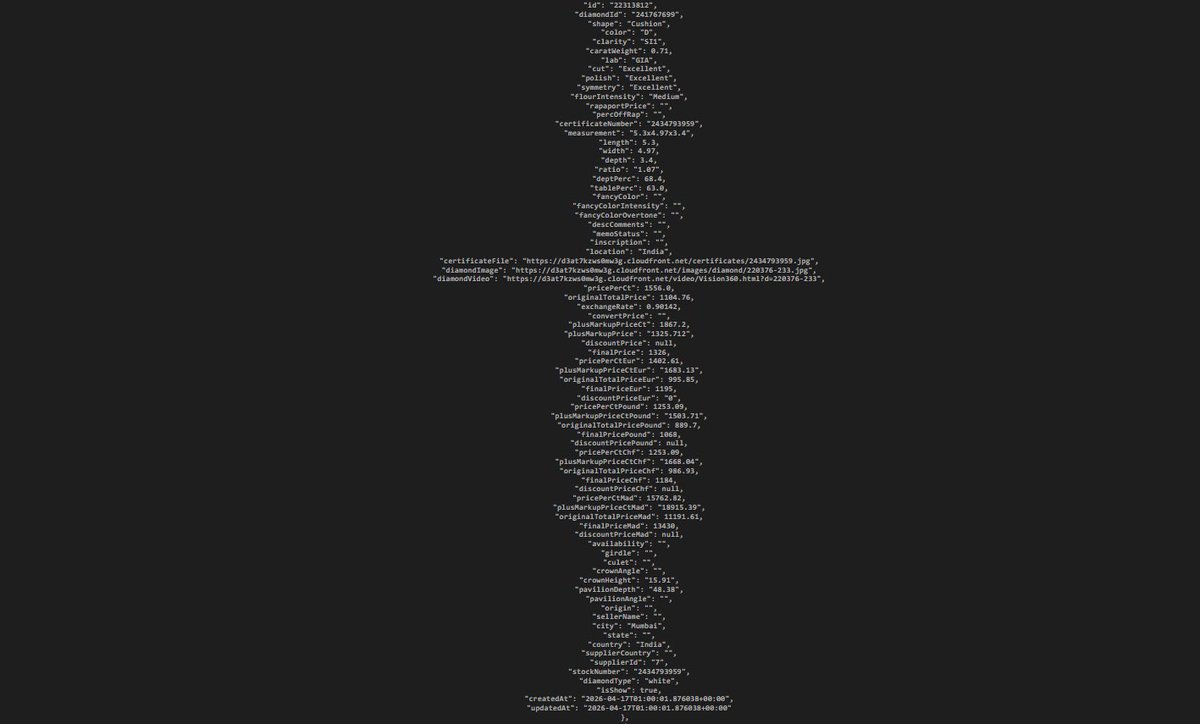
Threat actor CoDzz claims to have compromised Celinni, alleging exposure of customer, diamond, and internal business data.
📊 Claimed records:
• 243,871 customer references
• 32,914 GIA-related diamond records
• Customer names, emails, phone numbers & addresses
• Accounts, orders, invoices & identity documents
• GIA certificate/report numbers
• Supplier details and purchase orders
• Purchase/resale prices & profit margins
• Product, stock and order information
🔎 A sample allegedly contains detailed diamond inventory/pricing fields, including measurements, grading characteristics, GIA report identifiers, location, supplier/stock references and pricing in multiple currencies.
⚠️ The alleged breach, dataset size, authenticity, and extent of access have not been independently verified. Sensitive personal and financial information from the sample is not reproduced.
#CyberSecurity #DataBreach #DataLeak #France #Celinni #Diamonds #GIA #ThreatIntelligence
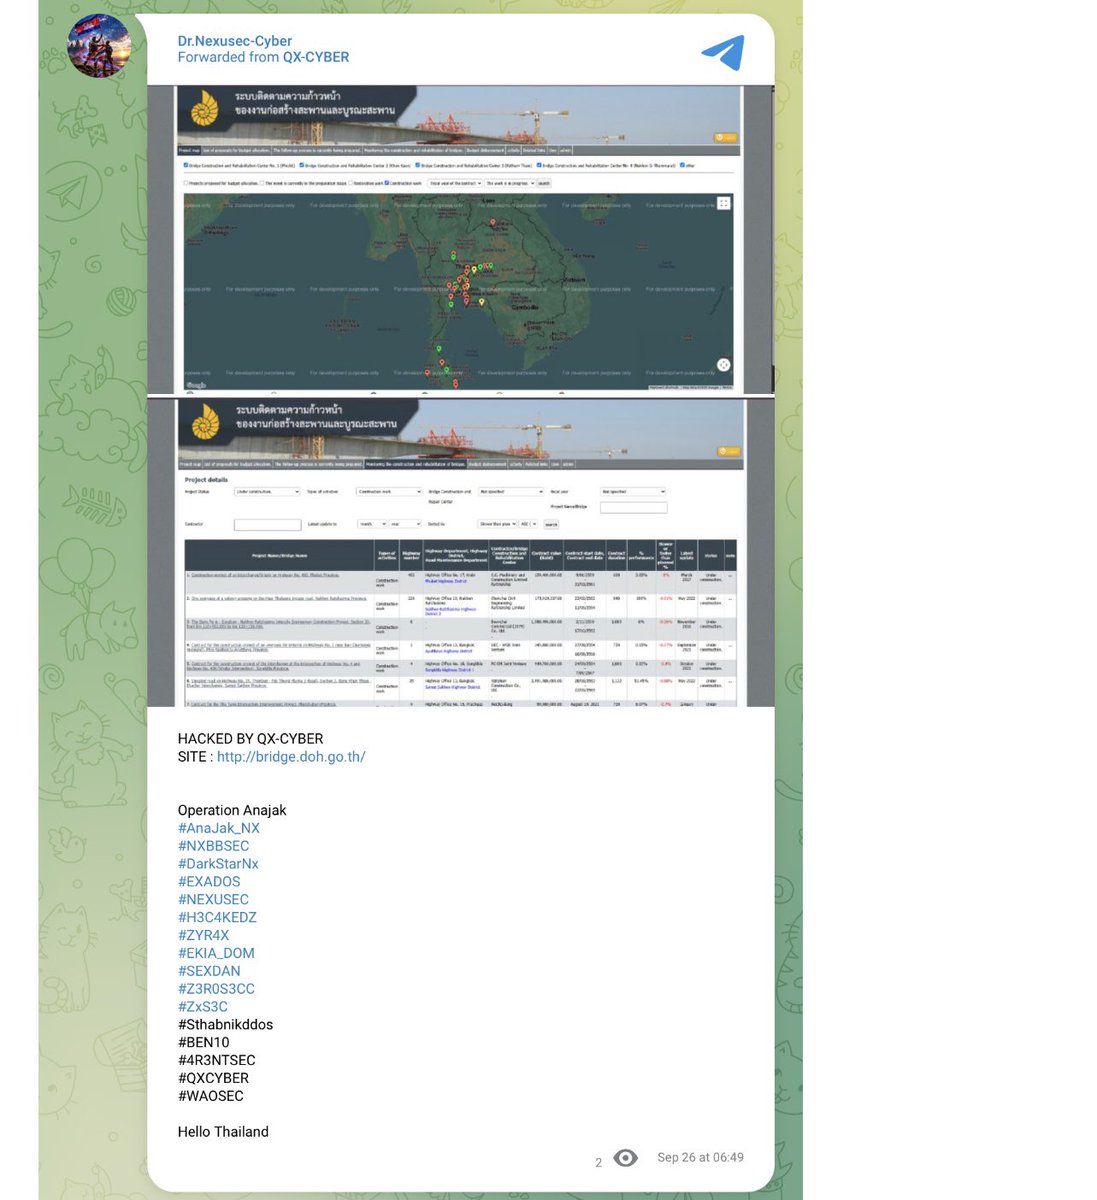
‼️🇹🇭 WEBSITE HACKED – THAILAND
Target: Department of Highways bridge construction & rehabilitation progress-tracking system
🌐 https://t.co/gEkyT7OiDz
A threat actor identified as QX-CYBER, with the post forwarded by Dr.Nexusec-Cyber, claims the site was compromised.
⚠️ The claimed compromise and extent of access have not been independently verified. The incident appears to concern website defacement rather than confirmed database exfiltration.
#CyberSecurity #Thailand #DepartmentOfHighways #QXCYBER #NXBBSEC #ThreatIntelligence
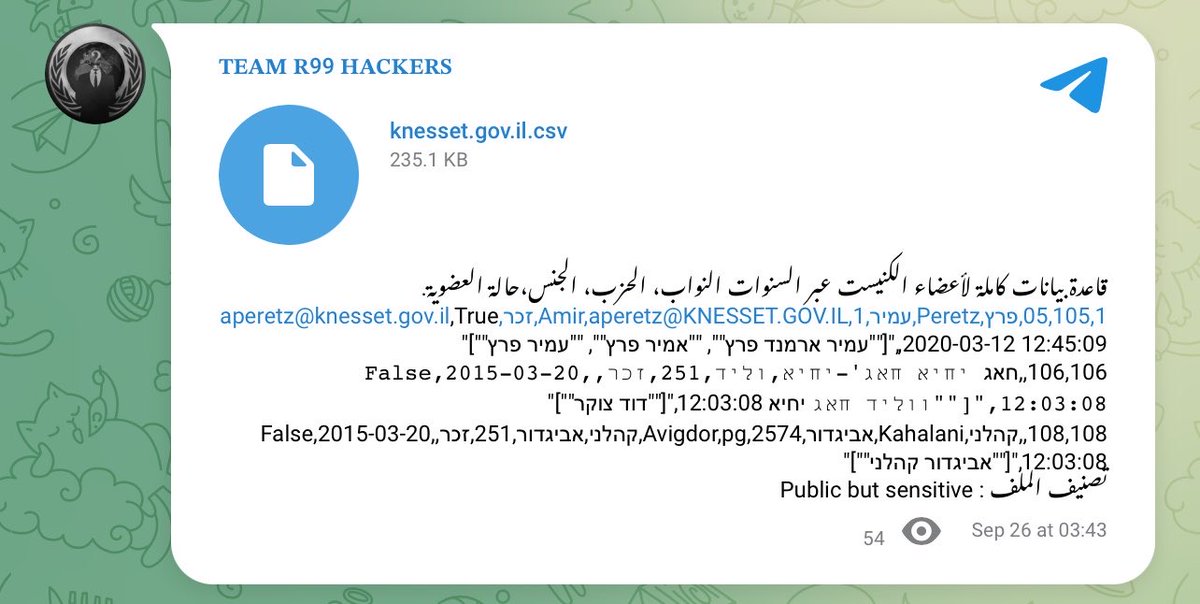
‼️🇮🇱 ALLEGED DATA DISCLOSURE – https://t.co/bSN380CSaY
Team R99 Hackers claims to have disclosed a 235.1 KB CSV database allegedly containing historical information on members of Israel’s Knesset.
📌 Claimed dataset:
• Members of the Knesset across multiple years
• Representatives’ names and party affiliations
• Gender and membership status
• Email addresses and account-related fields
• Membership/record timestamps
• Historical member records
📁 Filename: https://t.co/mnBUfmBhZk.csv
📦 Size: 235.1 KB
🏷️ Claimed classification: “Public but sensitive”
⚠️ The provenance, authenticity, and whether the dataset was obtained through unauthorized access have not been independently verified. The post appears to contain information that may overlap with publicly available parliamentary records.
#CyberSecurity #DataLeak #Israel #Knesset #DataBreach #ThreatIntelligence #CyberThreat
‼️🇮🇱 ALLEGED DATA LEAK – https://t.co/d41VRMf63h
A post attributed to Team R99 Hackers advertises a 597 MB CSV file named gov.il-وثائق.csv.
📌 Filename: gov.il-وثائق.csv
📌 File size: 597 MB
📌 Claim: Confidential/sensitive government documents or information
📌 Source: Team R99 Hackers
⚠️ The contents, authenticity, provenance, and scope of the alleged disclosure have not been independently verified.
#CyberSecurity #DataLeak #Israel #GovIL #DataBreach #ThreatIntelligence #CyberThreat