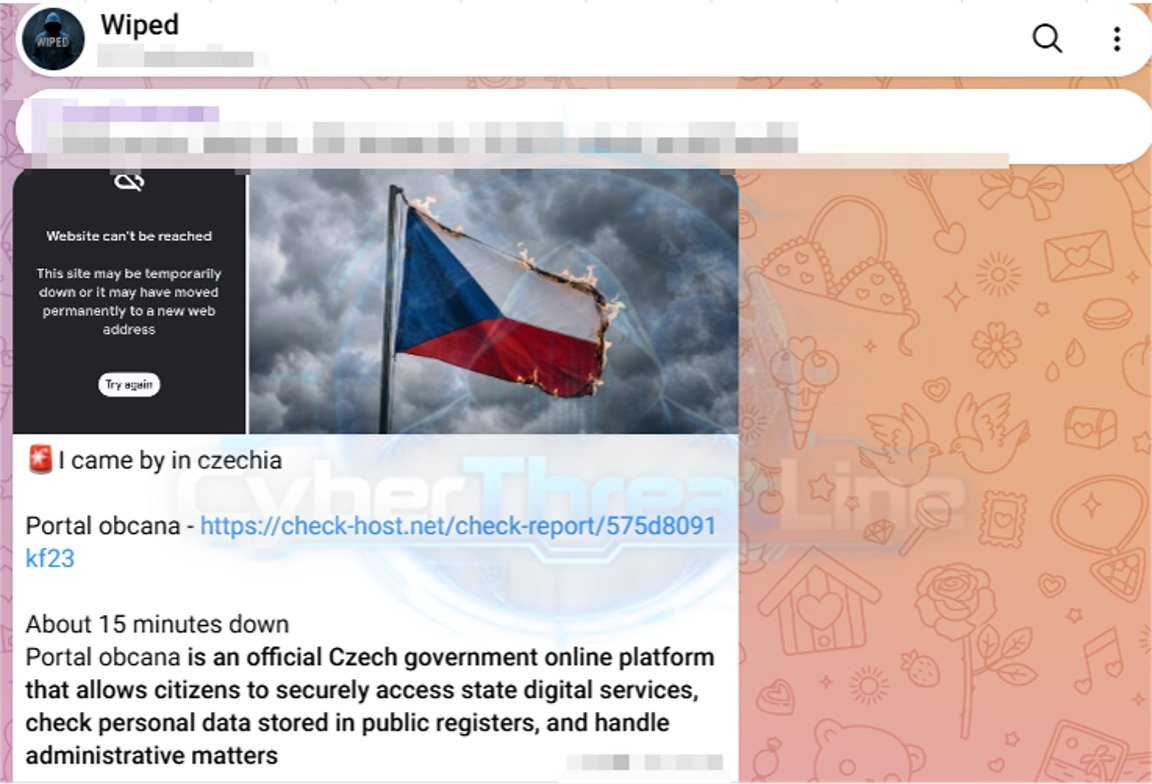
🚨 🇨🇿 Wiped Claims DDoS Attack Against Czech Government Portal
The hacktivist group Wiped published a Telegram post claiming a DDoS attack against Portal občana, an official Czech government digital services platform. The group shared a Check-Host report allegedly documenting service unavailability lasting approximately 15 minutes.
📢 Telegram Channel: Wiped
🏢 Affected Organization: Portal občana (Czech Government)
🏭 Sector: Government
📊 Reported Data: The group claims a DDoS attack caused temporary disruption of Portal občana, reportedly lasting around 15 minutes. A Check-Host connectivity report was provided as supporting evidence. No data theft or unauthorized access was reported.
⚠️ Status: Unverified — The group claims responsibility for a DDoS attack, but the reported attack, its attribution, and the extent of the service disruption have not been independently confirmed.
#CyberThreatLine #CzechRepublic #DDoS #Hacktivism #Government
🚨 🇲🇽 Hackero$ Claims Exposure of SIDECO Labor Conciliation Database
The Telegram publisher Hackero$ shared a database allegedly associated with SIDECO's 2026 labor conciliation records in the State of Mexico (EDOMEX). The publication includes a sample of database fields and references an accompanying SQLite database file, potentially exposing sensitive employment and personally identifiable information.
📢 Telegram Channel: Hackero$
🏢 Affected Organization: SIDECO (as identified in the publication)
🏭 Sector: Government / Labor Administration
📊 Reported Data: The advertised file, SIDECO.db, reportedly contains labor conciliation records with fields including names, CURP, age, nationality, gender, phone numbers, email addresses, social security information, employer details, case identifiers, reasons for conciliation, and agreed settlement amounts.
⚠️ Status: Unverified — The authenticity, origin, ownership, and potential exposure of the database have not been independently confirmed. The extent of the alleged data exposure remains unknown.
#CyberThreatLine #Mexico #DataLeak #PII #Government
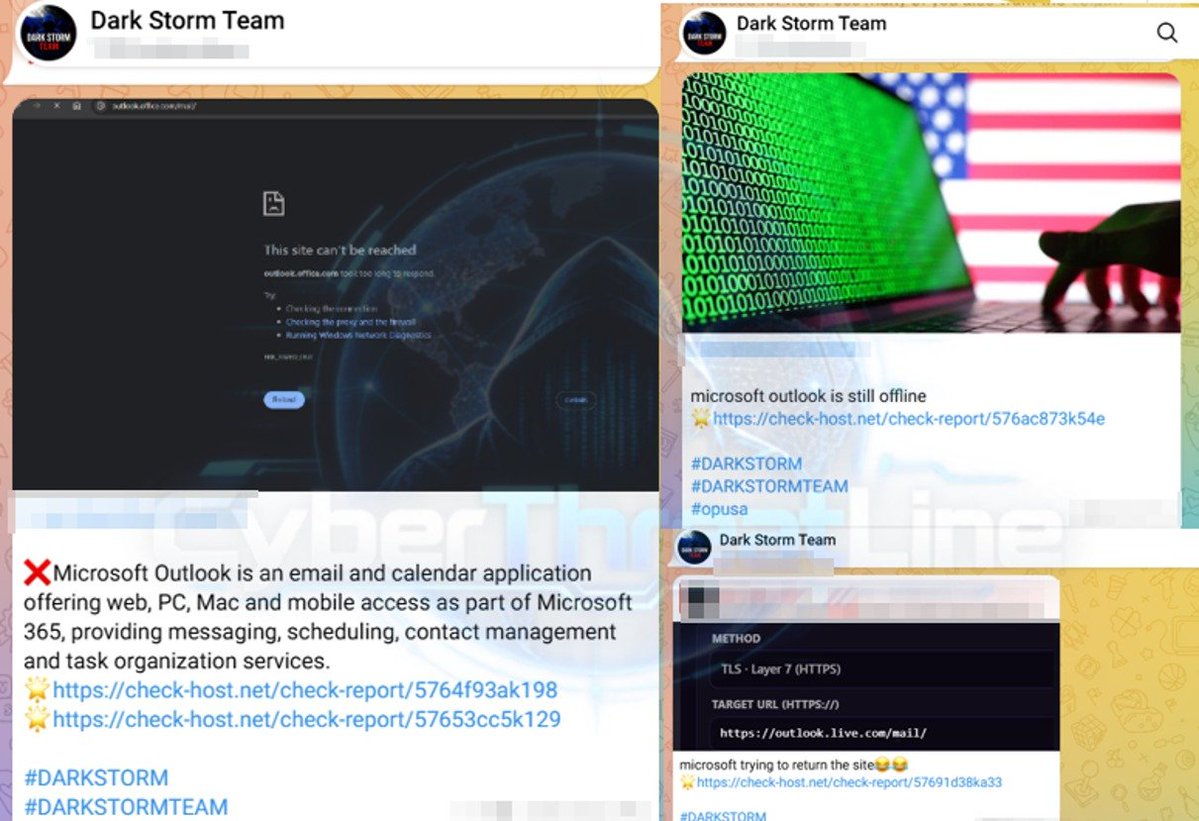
🚨 🇺🇸 Dark Storm Team Claims Microsoft Outlook Disruption
The pro-Russian hacktivist group Dark Storm Team published three Telegram posts highlighting Microsoft Outlook service disruptions, potentially suggesting involvement in the incident or attacks conducted alongside affiliated groups. The publications included Check-Host reports showing connectivity issues and comments indicating that Outlook remained unavailable while Microsoft was attempting to restore services.
📢 Telegram Channel: Dark Storm Team
🏢 Affected Organization: Microsoft
🏭 Sector: Technology
📊 Reported Data: Three separate publications referenced Microsoft Outlook availability and included Check-Host connectivity reports. Microsoft officially acknowledged service disruptions affecting Exchange Online and Microsoft 365, attributing the issues to infrastructure failures, server unavailability, and capacity-related problems.
⚠️ Status: Microsoft confirmed the service disruptions. However, no evidence has established that a cyberattack or DDoS operation conducted by Dark Storm Team or its collaborators caused the outages. The group's possible involvement remains unverified.
#CyberThreatLine #Microsoft #Outlook #Hacktivism #DDoS
🚨 🇲🇽 Mexico — Alleged Exposure of ISSSSPEA Employee Financial Records
The threat actor Olympus_group claims to have obtained approximately 13,000 bank statements from the Institute of Social Security and Services for Public Servants of the State of Aguascalientes (ISSSSPEA). The post alleges that the records contain sensitive employee information, including financial and personal identifiers.
📢 Telegram Channel: Olympus_group
🏢 Affected Organization: ISSSSPEA — Institute of Social Security and Services for Public Servants of the State of Aguascalientes
🏭 Sector: Government / Public Sector
📊 Reported Data: The publisher claims the 33 MB file, named ISSSSPEA.json, contains approximately 13,000 bank statements and exposes CURP and RFC identifiers, residential addresses, and salary information. The post does not provide independently verifiable evidence of the dataset's authenticity or the claimed record count.
⚠️ Status: Unverified Claim — The Telegram post alleges exposure of employee financial records. The scope of access, authenticity of the material, and any confirmed institutional response remain unverified.
#CyberThreatLine #Mexico #Aguascalientes #DataBreach #DataLeak
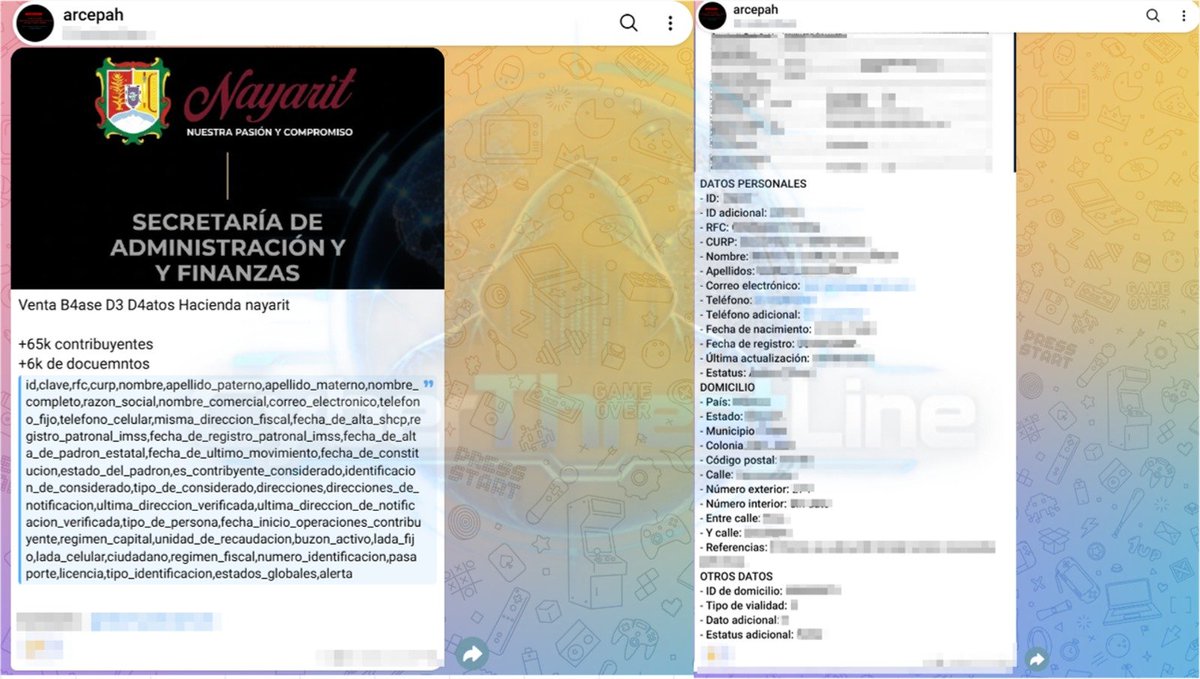
🚨 🇲🇽 Mexico — Alleged Sale of Nayarit Taxpayer Database Advertised on Telegram
A Telegram publisher is advertising a database allegedly associated with the Hacienda of Nayarit, Mexico, for sale. The post claims the dataset contains information on more than 65,000 taxpayers and over 6,000 documents. The authenticity, origin, and extent of the advertised material have not been independently verified.
📢 Telegram Channel: arcepah
🏢 Affected Organization: Hacienda of Nayarit
🏭 Sector: Government / Tax Administration
📊 Reported Data: The advertised dataset allegedly includes taxpayer identifiers and credentials, RFC and CURP numbers, names, business and corporate details, email addresses, landline and mobile phone numbers, tax and notification addresses, registration and incorporation dates, IMSS employer registration details, tax regimes, identification document numbers, passport and driver’s license information, taxpayer status, and account alerts. The publisher claims the material covers more than 65,000 taxpayers and 6,000 documents; these figures remain unverified.
⚠️ Status: Unverified Claim — The Telegram post advertises the database for sale. No independent confirmation of unauthorized access, data exposure, or the claimed record and document counts was provided.
#CyberThreatLine #Mexico #Nayarit #DataLeak #GovernmentSecurity
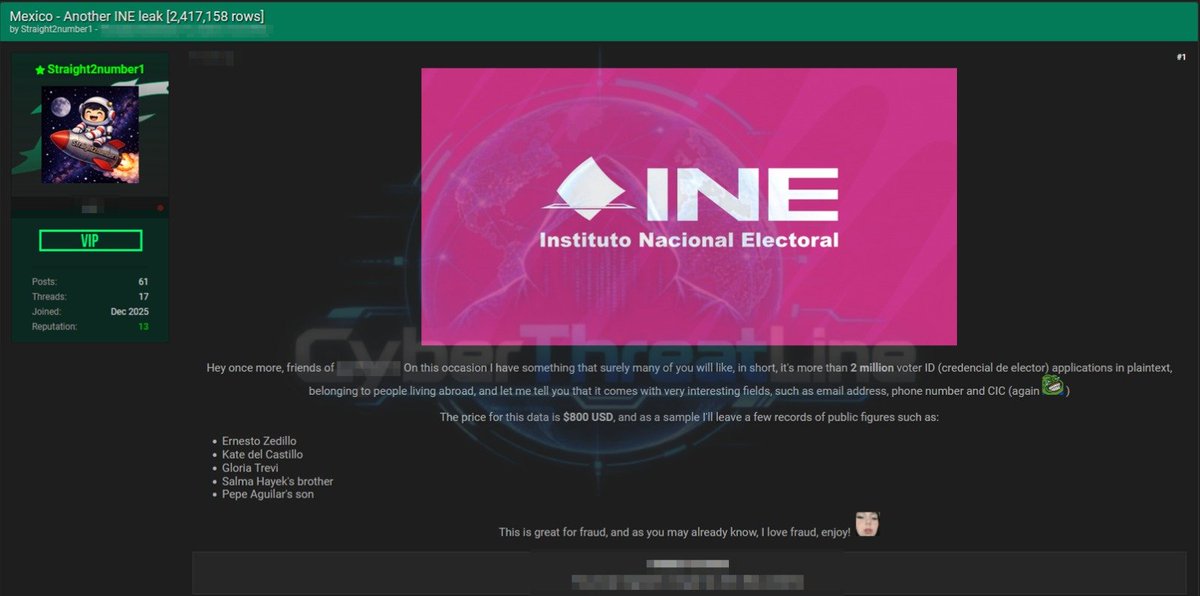
🚨 🇲🇽 Mexico — Threat Actor Reiterates Sale of 2.4 Million INE Voter Registration Records
A threat actor using the alias Straight2number1 is advertising the sale of a database allegedly containing more than 2.4 million voter identification applications belonging to Mexican citizens residing abroad. The seller explicitly promotes the information for potential fraudulent activities and requests $800 USD for the dataset.
👤 Threat Actor: Straight2number1
🏢 Affected Organization: National Electoral Institute (INE)
🏭 Sector: Government
🔎 Source: Dark Web Forum
📊 Reported Data: The advertised dataset allegedly contains 2,417,158 plaintext records, including voter registration application information, email addresses, phone numbers, and CIC identifiers. The seller references sample records associated with several public figures but does not provide independently verifiable evidence of the complete dataset in the supplied publication.
⚠️ Status: Unverified — the authenticity, origin, and scope of the advertised records, as well as their alleged association with INE systems, have not been independently confirmed.
#CyberThreatLine #INE #Mexico #DataLeak #IdentityTheft
🚨 🇲🇽 Mexico — Threat Actor Claims Access to Seguritech C5 Incident Monitoring Database
A threat actor using the alias Sc0rp10nn claims to have gained unauthorized access to Seguritech's internal monitoring infrastructure, allegedly exposing incident databases associated with multiple C5 security centers across Mexico. The actor also claims persistent access to the environment, raising concerns about the potential exposure and manipulation of sensitive public security information.
👤 Threat Actor: Sc0rp10nn
🏢 Affected Organization: Seguritech
🏭 Sector: Technology
🔎 Source: Dark Web Forum
📊 Reported Data: The allegedly accessed databases contain security incident reports, employee and law enforcement personnel information, full names, photographs, phone numbers, addresses, and incident coordinates. The actor claims access to real-time monitoring information, including patrol dispatch status and incident details. Additionally, the publication alleges the deployment of 32 backdoors connected to a command-and-control (C2) server, with full write permissions.
⚠️ Status: Unverified — the alleged unauthorized access, database exposure, deployment of backdoors, and claimed write privileges have not been independently confirmed.
#CyberThreatLine #Mexico #C5 #CriticalInfrastructure #CyberSecurity
🚨 🇲🇽 Mexico — Alleged Exposure of Internal Álvaro Obregón Borough Documents
A threat actor using the alias KzCx claims to have obtained a collection of internal documents related to the Álvaro Obregón Borough in Mexico City. The publication advertises an archive containing administrative, financial, and government-related records, including documents reportedly bearing signatures.
👤 Threat Actor: KzCx
🏢 Affected Organization: Álvaro Obregón Borough Government, Mexico City
🏭 Sector: Government
🔎 Source: Dark Web Forum
📊 Reported Data: The advertised archive, named 2026_Mex.zip, reportedly contains 68 files across 3 directories, with a stated size of approximately 234 MB (also described as 246 MB in the publication). Reported contents include internal administrative forms, signed documents, financial and budget reports, payment records, and grant and subsidy documentation.
⚠️ Status: Unverified — the authenticity, origin, and extent of the allegedly exposed government documents have not been independently confirmed.
#CyberThreatLine #DataLeak #Mexico #Government #CyberThreats
🚨 🇲🇽 Mexico City — Hacker Claims Sale of 5.8 Million Driver's License Records
A threat actor using the alias revolucionMX is advertising the sale of an allegedly compromised Mexico City driver's license database on a dark web forum. The seller claims the dataset contains 5.8 million license records and includes highly sensitive personal and biometric information.
👤 Threat Actor: revolucionMX
🏢 Affected Organization: Mexico City Ministry of Mobility (SEMOVI)
🏭 Sector: Government
🔎 Source: Dark Web Forum
📊 Reported Data: The advertised dataset allegedly contains 5.8 million records, including full names, CURP identifiers, dates of birth, contact details, residential addresses, blood types, license information, and administrative records. The seller also claims the database includes facial photographs, signatures, and fingerprints. Sample records and screenshots were published as supporting material. The database is reportedly offered for $3,000 USD or MXN 55,000.
⚠️ Status: Unverified — the authenticity, origin, and scope of the advertised database, as well as the alleged exposure of biometric information, have not been independently confirmed.
#CyberThreatLine #DataLeak #Mexico #SEMOVI #DataBreach
🚨 🇧🇴 Bolivia's Senate — Hacker Claims Personnel Database Breach
A threat actor operating under the alias konata_izumi_shell claims to have breached Bolivia's Senate and extracted a personnel database allegedly containing 2,652 records. The publication includes sample entries containing personal and contact information associated with individuals listed in the database. MortemTeam - KonataIzumiLeaks
👤 Threat Actor: konata_izumi_shell
📢 Telegram Channel: KonataIzumiLeaks
🏢 Affected Organization: Senate of Bolivia (Cámara de Senadores)
🏭 Sector: Government
🔎 Source: Dark Web Forum
��� Reported Data: The allegedly extracted database contains 2,652 records, with fields including names, national identification numbers, dates of birth, nationality, email addresses, phone numbers, residential addresses, and military service information. The publisher also shared sample records as evidence of the claimed dataset.
⚠️ Status: Unverified — the alleged unauthorized access, authenticity of the database, and reported scope of exposure have not been independently confirmed.
#CyberThreatLine #DataBreach #Bolivia #Government #DataLeak
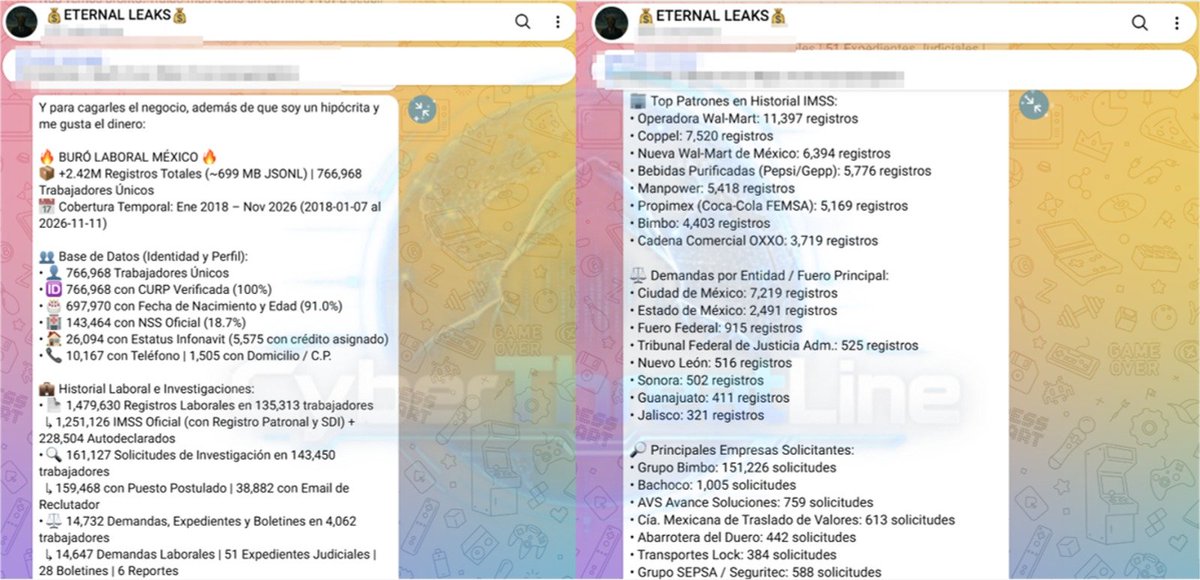
🚨 🇲🇽 Eternal Leaks Advertises Alleged Buró Laboral Database Containing 766K Worker Profiles
The Telegram channel Eternal Leaks is advertising for MXN 3,500 an alleged Mexican Buró Laboral database containing more than 2.42 million records associated with employment histories, recruitment investigations, and labor-related proceedings. The seller claims the dataset spans January 2018 to November 2026 and includes highly sensitive personal and employment information.
📢 Telegram Channel: Eternal Leaks
🏢 Affected Organizations: Multiple Mexican employers, including Grupo Bimbo, Walmart, Coppel, OXXO, Bachoco, and Coca-Cola FEMSA.
🏭 Sector: Human Resources & Employment Services
📊 Reported Data: The seller claims the database contains 766,968 unique workers, all reportedly associated with verified CURP records. Other advertised fields include dates of birth, NSS, Infonavit status, contact details, employment records, salary information, recruitment investigations, labor lawsuits, judicial files, and employee blacklisting records. The publication claims 1,479,630 employment records, 161,127 investigation requests, and 14,732 legal or blacklist-related records. Sample files and a separate infrastructure investigation document were also advertised.
⚠️ Status: Unverified — the database's authenticity, completeness, provenance, and alleged exposure of personal records have not been independently confirmed. All quantities and data categories reflect the seller's claims.
#CyberThreatLine #Mexico #DataLeak #PII #LaborData
🚨 🇲🇽 Eternal Leaks Advertises Alleged Buró Laboral Corporate Database in Mexico
The Telegram channel Eternal Leaks has published a CSV file titled “BURÓ LABORAL - BASE COMPLETA DE EMPRESAS,” allegedly containing information on companies that use and contribute records to Mexico’s Buró Laboral. The publication identifies organizations across multiple industries, raising potential concerns about the scope and circulation of corporate employment-related information.
📢 Telegram Channel: Eternal Leaks
🏢 Affected Organizations: Multiple companies operating in Mexico
🏭 Sector: Cross-Sector / Human Resources
📊 Reported Data: The advertised file, “empleados-empresas.csv,” is described as a complete corporate database. The accompanying publication highlights companies including Grupo Bimbo, Bachoco, Gruma, Grupo Posadas, Megacable, LG Electronics, Estafeta, Securitas, Afirme, Deloitte, PwC, and others. The post does not establish the exact number of records, available fields, or whether the listed companies' information has been independently validated.
⚠️ Status: Unverified — the dataset's authenticity, completeness, origin, and alleged association with Buró Laboral have not been independently confirmed. This publication concerns the corporate database, not the separate employee blacklist reportedly offered for sale.
#CyberThreatLine #Mexico #DataExposure #BuróLaboral #HumanResources
🚨 🇪🇸 NoName057(16) Claims Disruption of Spanish Bus Manufacturer UNVI Website
The pro-Russian hacktivist group NoName057(16) claims to have disrupted the public-facing website of UNVI (Unidad de Vehículos Industriales, S.A.), a Spanish manufacturer of buses and commercial passenger vehicles. The group frames the alleged incident as part of its ongoing operations targeting Spanish organizations under the #OpSpain campaign.
📢 Telegram Channel: NoName057(16)
🏢 Affected Organization: Unidad de Vehículos Industriales, S.A. (UNVI)
🏭 Sector: Manufacturing & Transportation
📊 Reported Data: The publication identifies UNVI's corporate website as the sole target and provides a Check-Host report as purported evidence of service unavailability. No database compromise, data theft, or exposure of personal information is reported.
⚠️ Status: Unverified — the alleged DDoS attack and resulting website disruption have not been independently confirmed.
#CyberThreatLine #Spain #NoName05716 #DDoS #OpSpain
🚨 🇪🇸 NoName057(16) Claims Disruption of Lamaignere and Correos Express Digital Services
The pro-Russian hacktivist group NoName057(16) claims to have disrupted multiple digital services belonging to Spanish logistics companies Lamaignere and Correos Express. The reported targets include customer portals, a review platform, and an authorization service, allegedly affecting digital services associated with freight transportation and parcel delivery.
📢 Telegram Channel: NoName057(16)
🏢 Affected Organizations: Lamaignere and Correos Express
🏭 Sector: Transportation & Logistics
📊 Reported Data: The group identifies three targeted services:
• Lamaignere customer portal.
• Lamaignere customer review portal.
• Correos Express authorization service.
Three Check-Host reports are provided as purported evidence of service disruptions. No data theft, database compromise, or personal information exposure is reported.
⚠️ Status: Unverified — the alleged DDoS attacks, service availability disruptions, and operational impact have not been independently confirmed.
#CyberThreatLine #Spain #NoName05716 #DDoS #Logistics
🚨 🌎 ShinyHunters Claims SSH and Root Access to 11 Organizations Across Multiple Countries
A threat actor identifying as ShinyHunters has advertised alleged SSH and root-level access to infrastructure belonging to 11 organizations across different sectors and countries. The listing includes hosting environments, web servers, development infrastructure, backup systems, and research cluster nodes, with access reportedly being offered for sale as a combined package.
👤 Threat Actor: ShinyHunters (self-claimed attribution)
🏢 Affected Organizations: TIPSA, Azul Handling, Psicotec, Qualitylike, Applinet, SSP Electronic, Nura, Custel, Conectar Remoto, Winiw, and Vietnam National University Hanoi.
🏭 Sector: Multiple Sectors — Transportation, Aviation Services, Technology, Education, Research, and Professional Services.
📊 Reported Data: The actor advertises SSH access across all 11 organizations, including claimed root shell access to multiple hosts belonging to Qualitylike, Applinet, and Vietnam National University Hanoi. The advertised infrastructure includes Plesk servers, MariaDB, Docker services, development repositories, backup systems, and research databases running MongoDB, Redis, and PostgreSQL. The combined access package is reportedly priced at approximately $1 million USD, with cryptocurrency payments accepted. No database samples or independent proof of access were provided.
⚠️ Status: Unverified — the claimed access privileges, infrastructure compromise, actor attribution, and authenticity of the advertised inventory have not been independently confirmed.
#CyberThreatLine #ShinyHunters #SSHAccess #RootAccess #CyberThreat
🚨 🇲🇽 Telegram Channel Advertises Alleged Mexican Driver's License Databases
The Telegram channel Leads and Leaks has published an advertisement promoting alleged databases containing Mexican driver's license information.
📢 Telegram Channel: Leads and Leaks
🏢 Affected Organization: Mexican driver's license database systems (specific institutions not identified)
🏭 Sector: Government
📊 Reported Data: The advertisement references alleged Mexican driver's license databases. No record counts, database samples, exposed data fields, file sizes, or information about the database's origin were provided.
⚠️ Status: Unverified — the existence, authenticity, origin, and potential unauthorized disclosure of the advertised databases have not been independently confirmed.
#CyberThreatLine #Mexico #DataLeak #Government #DataPrivacy
🚨 🇫🇷 LunarisSec Claims IDOR Vulnerability Exposes 15,171 Data Rows on SOS Oxygène Platform
The Algerian-associated group LunarisSec claims to have identified an Insecure Direct Object Reference (IDOR) vulnerability in the SOS Oxygène platform in France. According to the group's publication, the alleged access control weakness could allow unauthorized access to more than 15,171 rows of data.
📢 Telegram Channel: LunarisSec
🏢 Affected Organization: SOS Oxygène
🏭 Sector: Healthcare
📊 Reported Data: The group claims that the vulnerability exposed more than 15,171 data rows. No specific personal information categories, database samples, or additional technical details about the affected records were provided in the publication.
⚠️ Status: Unverified — the vulnerability, reported data exposure, accessibility of the records, and potential impact have not been independently confirmed.
#CyberThreatLine #France #LunarisSec #IDOR #DataExposure
🚨 🇲🇽 The Gentlemen Claims Access to PRINSEL-Related Data
The threat actor known as The Gentlemen has listed Productos Infantiles Selectos S.A. de C.V. (PRINSEL), a Mexican children's products company, in an apparent data compromise claim. The company operates in the children's footwear, clothing, and accessories market, with its headquarters in the State of Mexico.
👤 Threat Actor: The Gentlemen
🏢 Affected Organization: Productos Infantiles Selectos S.A. de C.V. (PRINSEL)
🏭 Sector: Retail & Manufacturing
📊 Reported Data: The supplied publication identifies the organization but provides no specific information about compromised files, exposed data categories, record counts, or exfiltration volume.
⚠️ Status: Unverified — the alleged compromise and authenticity of any potentially exposed information have not been independently confirmed.
#CyberThreatLine #PRINSEL #Mexico #DataBreach #Ransomware
🚨 🇲🇽 The Gentlemen Ransomware Group Lists Grupo San Cristóbal
The Gentlemen ransomware group has listed Grupo San Cristóbal, a Mexican business group, on its leak platform. The company operates across multiple business units, providing property management, accounting, construction, insurance, and legal services. The listing displays a countdown of approximately 235 hours before activation.
🎭 Ransomware Group: The Gentlemen
🏢 Affected Organization: Grupo San Cristóbal (https://t.co/XMfM5NJO9x).
🏭 Sector: Financial Services, Real Estate, and Construction
📊 Reported Data: The publication identifies the organization and provides a countdown of approximately 235 hours and 58 minutes. No specific stolen data categories, file samples, or exfiltration volume were provided in the supplied information.
⚠️ Status: Unverified — the alleged ransomware incident, potential data compromise, and any associated data theft have not been independently confirmed.
#Mexico #Ransomware #TheGentlemen #DataLeak #CyberThreatLine
🚨 🌎 Global — Widespread Service Disruptions Reported Across Major Technology Platforms
Multiple reports of service disruptions have been recorded worldwide on November 12, according to Downdetector. Users are reporting issues affecting Microsoft, Google, Cloudflare, and Amazon Web Services (AWS), alongside platforms including Zoom, with reported difficulties involving connectivity, authentication, email delivery, application access, cloud infrastructure, and service availability. No common cause linking the reported disruptions has been confirmed.
🏢 Affected Organizations: Microsoft, Google, Cloudflare, Amazon Web Services (AWS), Zoom
🏭 Sector: Technology
🔎 Source: Downdetector
📊 Reported Data: Reported disruptions affect Microsoft Outlook, Microsoft 365, Teams, Store, Copilot, Azure, Entra, OneDrive, Microsoft Account, Gmail, Google services, Cloudflare, AWS, and Zoom. The most frequently reported issues include application malfunctions, server connectivity, login failures, email delivery problems, DNS errors, cloud storage synchronization, and AI generation failures.
⚠️ Status: Ongoing Reports — Downdetector reflects increased user-reported incidents across multiple platforms. The full scope, underlying causes, and potential relationship between the disruptions remain unconfirmed.
#CyberThreatLine #ServiceDisruption #CloudOutage #Microsoft #Cloudflare