AI-generated attacks and zero-day threats do not wait for a rule to be written. Cyntros AI uses adaptive machine learning to help detect suspicious network activity without relying on signatures, static models, or any manual configuration.
https://t.co/NZQZ378BdL
Can you see the cybersecurity threats moving through your network?
Some attacks hide in lateral movement, command-and-control traffic, and unusual east-west activity.
Cyntros helps uncover suspicious network activity traditional tools may miss.
#Cybersecurity#NDR
Protecting endpoints is critical BUT it is not enough
Threats can move laterally, hide in unusual traffic patterns, and avoid leaving a clear endpoint footprint
Cyntros delivers next-gen NDR to help detect what endpoints CANNOT see: https://t.co/UEFbgWgpjL #NDR#MSSP#SOC
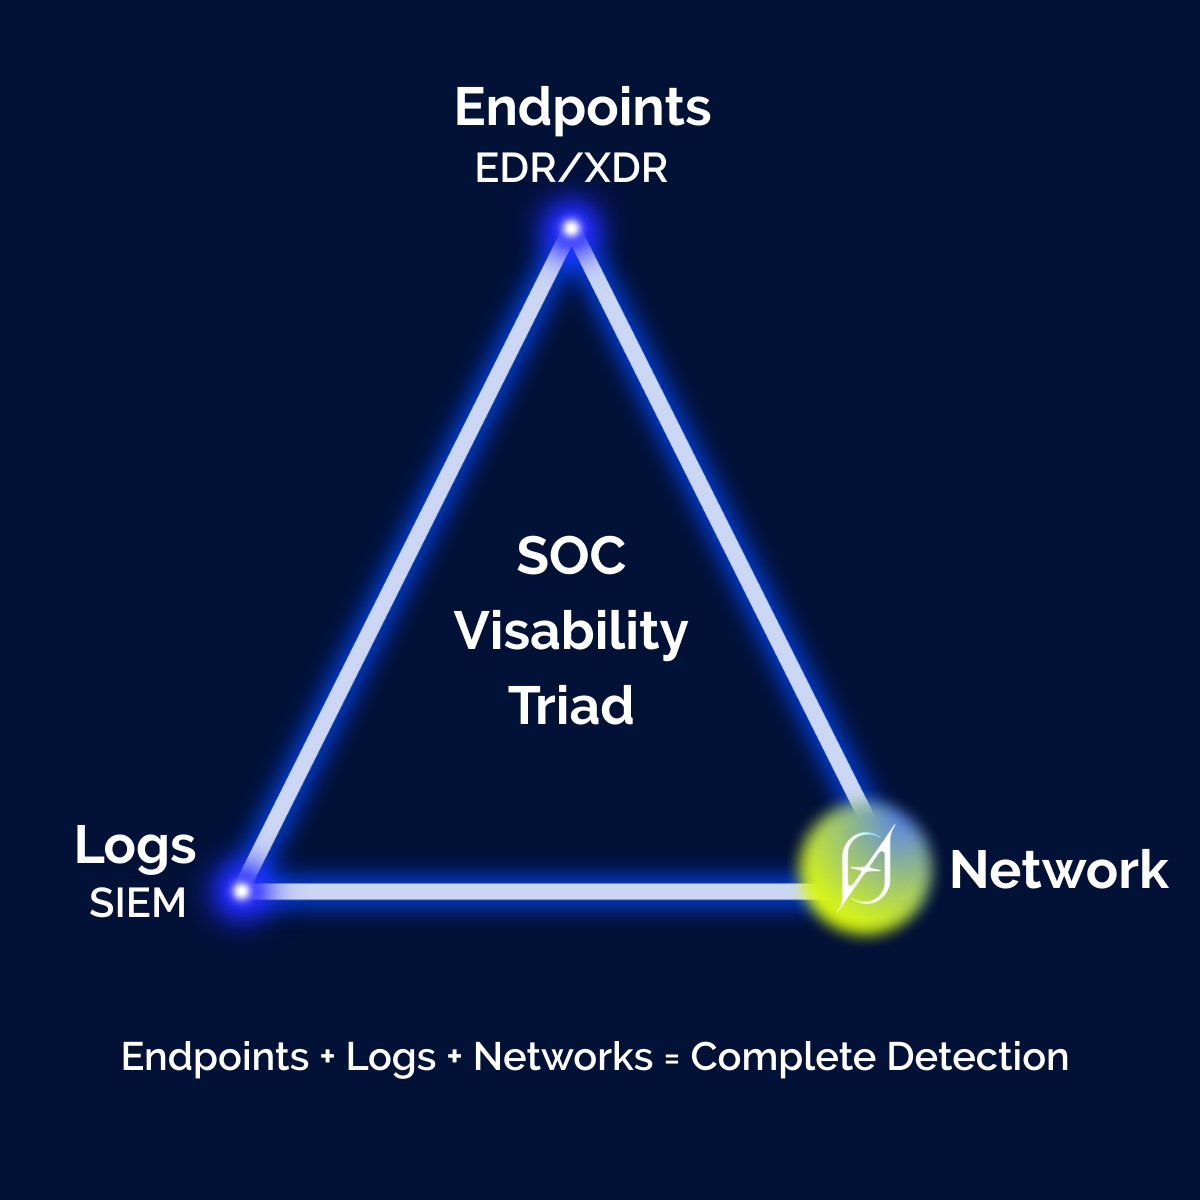
Security visibility comes from three places: endpoints, logs, and networks.
EDR and SIEM cover the first two. Cyntros provides the network visibility needed for complete detection.
https://t.co/XtrDxGQRYh
#cybersecurity#NDR#cyntros
Strong endpoint security doesn’t guarantee network visibility. Endpoints show part of the story, but lateral movement & abnormal connections appear on the network first. Cyntros learns normal behavior to detect abnormal activity as it moves. https://t.co/POHBWRTeYQ #Cybersecurity
Visibility alone is not security. Teams have plenty of alerts but lack clarity on what activity represents risk. Rules-based detection struggles in modern networks. Cyntros learns normal network behavior to detect what requires attention https://t.co/POHBWRTeYQ#Cybersecurity #NDR
Enterprise networks are dynamic but many security tools are still rules based. Static rules & signatures struggle in hybrid & cloud environments. Cyntros uses adaptive machine learning to detect malicious network activity in real time. https://t.co/POHBWRTeYQ
#Cybersecurity#NDR
Cyntros delivered one of the strongest CISA KEV results in the NDR market.
Independent @Miercom testing showed 97% effectiveness at detecting KEV-listed network exploits.
Rules-based and signature-driven tools miss what Cyntros sees.
No signatures.
No rigid rules.
Meet Cyntros - The next generation of #NDR.
Built on adaptive ML + behavioral analytics, it detects what others miss.
In independent testing, Cyntros caught 95% of threats missed by leading EDR & SIEMs. No signatures. No blind spots. Just control.
https://t.co/l45DPn0KVl
We’re excited to announce the launch of Cyntros, our next-generation Network Detection and Response platform. Independent testing by Miercom found Cyntros detected 95% of advanced threats missed by leading vendors — all without disrupting network operations.
Full release below