#DCISEAlert: PAN-OS RCE threatens firewall management systems
Patch affected systems or restrict management access to trusted IPs to reduce the risk of privileged compromise.
Check guidance: https://t.co/IOqwHryC46
Zimbra Expolit (CVE-2026-73570)
🛡 Update affected Zimbra servers to reduce the risk of command injection and data theft.e threat and mitigation guidance: https://t.co/d8IMPfqn3b…
Review your reporting procedures and ensure your team knows when and how to submit a mandatory incident report.
📩 Need guidance? Contact DCISE: [email protected]
#ZeroDayVulnerabilities
🎯 Threat: Successful exploitation of CVE-2026-88771 and CVE-2026-88772 lead to deployment of WHIPSHOT webshells and SLAPSHOT proxy tunnels for reconnaissance and credential theft.
🛡 Take Action: Response resources at https://t.co/mNLeoTbkcj…
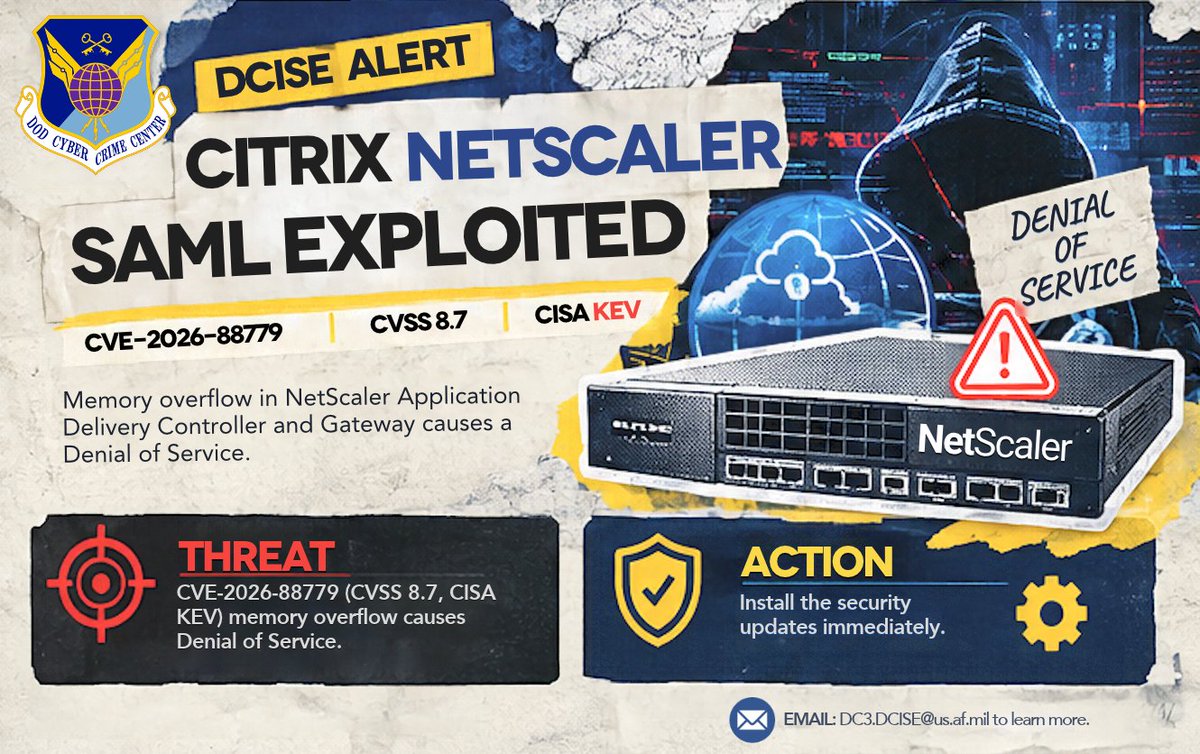
#Warning: Citrix NetScaler SAML Exploited
🎯 Threat: Exploitation of CVE-2026-88779 results in memory overflow leading to Denial of Service.
🛡 Take Action: Update relevant version https://t.co/XInFnde675
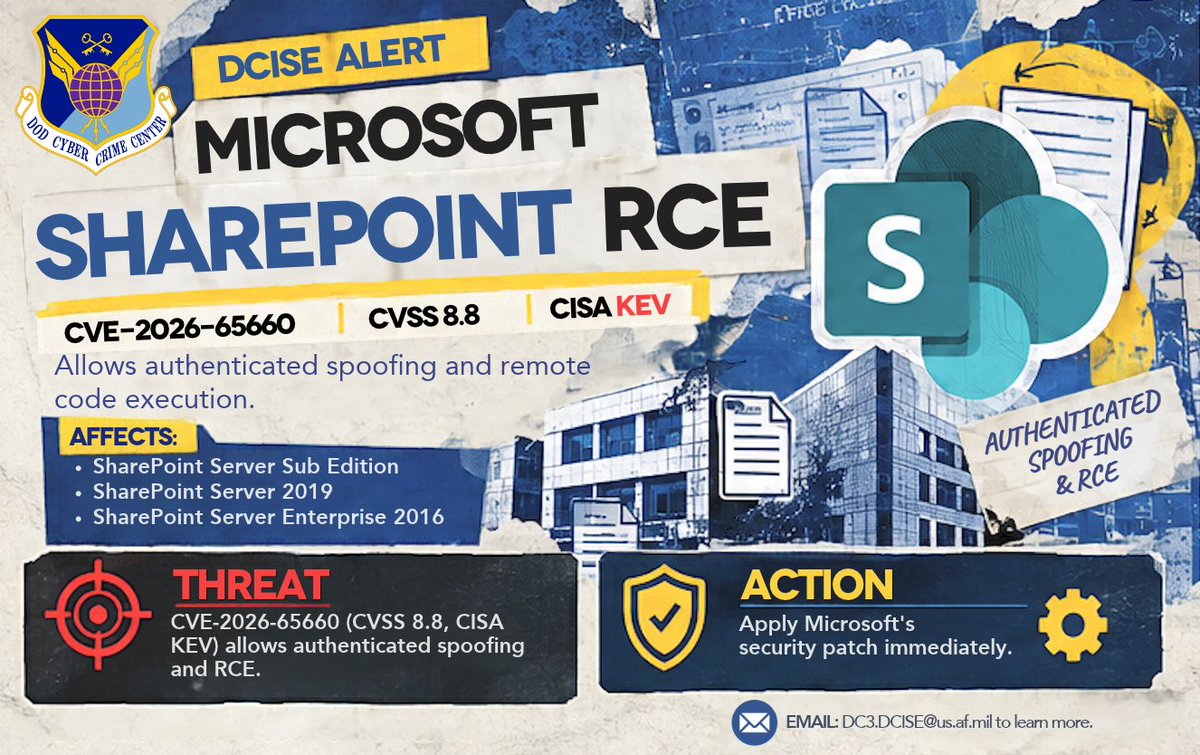
#Warning: Microsoft SharePoint RCE
🎯 Threat: CVE-2026-65660 allows improper code injection in Microsoft Office SharePoint allows an authorized attacker to execute code over a network.
🛡 Take Action: Patch immediately https://t.co/iLbalAIMre.
#Warning: Critical
MikroTik RouterOS Flaw
🎯 Threat: Successful exploitation of CVE-2026-84411 could allow an attacker to achieve remote code execution or cause a denial of service.
🛡 Take Action: Update RouterOS to 7.24+ immediately https://t.co/tyMtYmSZm2
#Warning: Microsoft Exchange Flaw
Threat: CVE-2026-96940 allows authenticated attackers to gain access to other users' mailboxes within the same organization and read email messages and attachments.
Take Action: Update security patches via https:// https://t.co/OJ0cCwOtoM)
Defending the DIB alone is a losing strategy.
Advanced adversaries exploit silos.
What hits your neighbor today could hit your network tomorrow.
Join the DIB Cybersecurity Program
Email [email protected] for more
Blind spots in your network visibility make you an easy target for APTs looking to breach the DIB.
Action: Enroll in ENSITE. Get a customized, near real-time network monitoring dashboard.
Email [email protected] to learn more.
CISA Adds Zyxel GS1900 Vulnerability to KEV
Threat: CVE-2026-7273, affecting Zyxel GS1900 Series Switches, is actively being exploited.
Action: Prioritize and apply mitigation guidance immediately to secure publicly exposed switches.
#DCISEWarning: VMware Center Targeted
by Chinese APTs
Threat: CVE-2026-59309 (Auth Bypass) & CVE-2026-59310 (RCE, CISA KEV) used to install reverse SSi backdoors.
Action: Patch immediately & check for
"vcenter_admin" or "zz-poc59310-syslog.log".