Cyber Intel 24/7. 🔔 Subscribe for sources and more. Welcome to the Dark Side.
Session ID: 051068fee6cdbbdaf0d7bff81e8e90b073abfd04d5bc574ce0dd93a7a41fc8a773
A data leak is a reminder to review your privacy setup. Proton VPN encrypts traffic between your device and its VPN servers and masks your IP from sites you visit. https://t.co/h6B05zgtdS #ad affiliate link
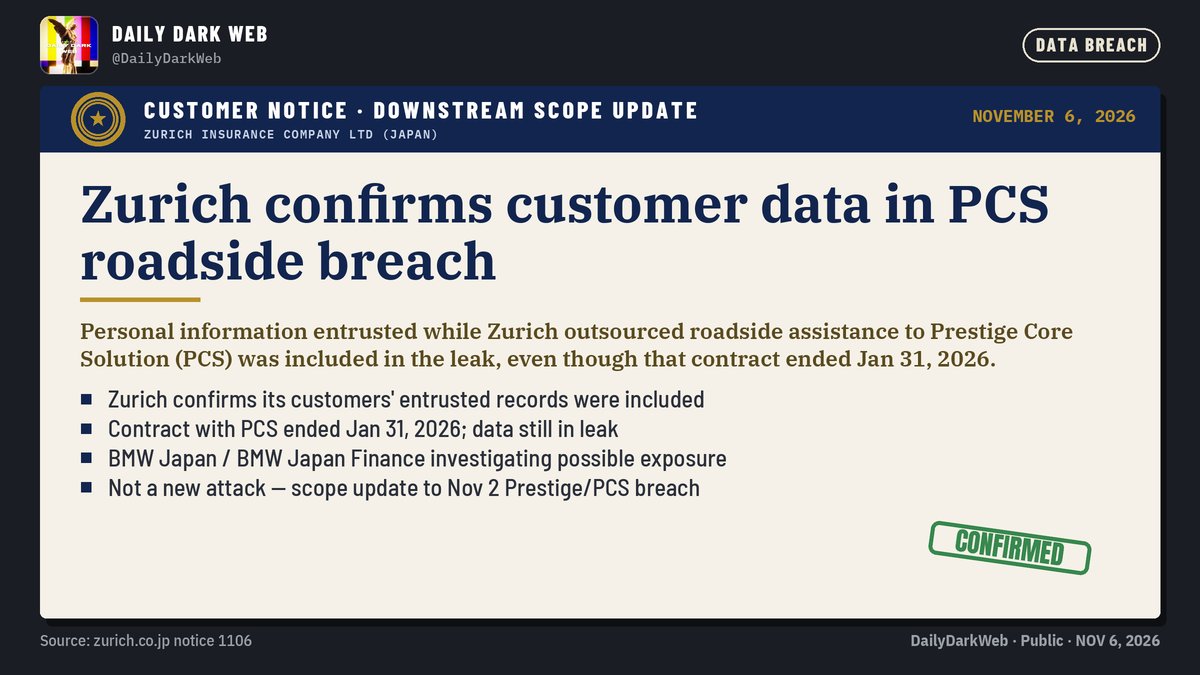
Zurich Japan says customer data leaked from former roadside-assistance provider PCS, despite its contract ending Jan 31, 2026. BMW Japan is investigating possible exposure. A new scope update to the previously disclosed breach.
⚠️ Analyst Note:
Zurich confirms data entrusted during its former roadside-assistance contract was included in the leak; it has not supplied an affected-customer count. BMW Japan and BMW Japan Finance are still investigating. Prestige's Nov 6 second report separately confirms three card-number records from reception records — not established as Zurich or BMW customers. The prior ~5.5M max includes duplicates and is not a new Nov 6 count. Do not treat this as a new attack.
https://t.co/5oSq6t6zg9
#DataBreach
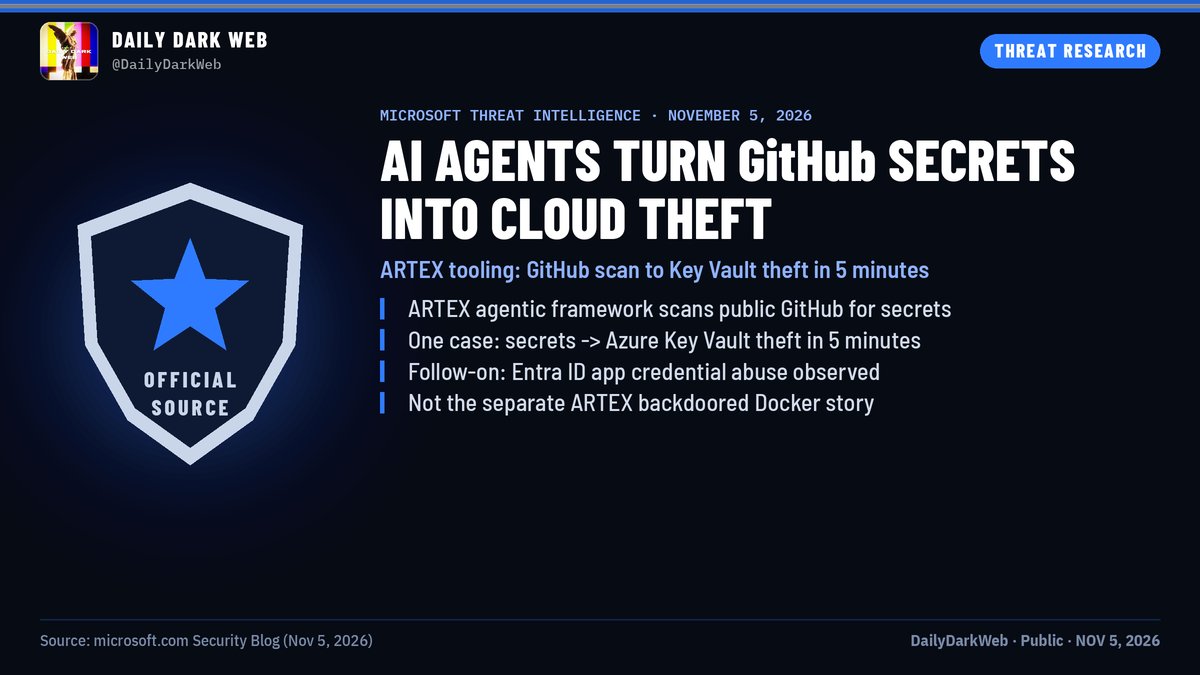
Microsoft: AI agents turn GitHub secrets into cloud theft
One observed ARTEX case went from secret searches to Azure Key Vault data theft in 5 minutes. Rotate leaked credentials and audit application sign-ins.
⚠️ Analyst Note:
These are reported real intrusions, not a lab demonstration. Microsoft supplies the ARTEX assessment and five-minute timing. Todyl independently observed overlapping infrastructure and credential abuse, but rates AI involvement low confidence and cannot establish model control. Microsoft describes API-request adjustments as consistent with adaptive troubleshooting; that interpretation is not independent proof of AI control. Distinct from the separate ARTEX backdoored Docker-image story already published.
https://t.co/xymnR66d15
#CyberSecurity
Former FBI agent Patrick Yaroch pleaded guilty Nov 5 to wire fraud and money laundering. DOJ says he stole $2.47m in crypto using wallet credentials tied to 35 FBI investigations.
⚠️ Analyst Note:
This is a new guilty plea and expanded theft scope, not a new arrest. Yaroch was arrested in July. The 35 figure refers to FBI investigations associated with credentials, not a victim count. Sentencing is scheduled for March 4, 2027; no sentence has been imposed in this plea announcement.
https://t.co/bo82lkTf8O
#Cybercrime
🇩🇪 🚨 BRAIN CIPHER RANSOMWARE CLAIMS ATTACK ON MUTARES
The Brain Cipher ransomware group has listed Mutares SE & Co. KGaA (mutares[.]com), the Munich-based private-equity holding company listed on the Frankfurt Stock Exchange (SDAX, ticker MUX), on its data-leak site.
The group claims to hold about 105 GB of "very interesting data." No file list, data categories or samples have been verified.
The claim has not been independently verified, and Mutares has not publicly confirmed an incident.
⚠️ Analyst Note:
Mutares is a listed special-situations investor with dozens of portfolio companies across automotive, energy, infrastructure/defense, goods and chemicals. A real compromise of the holding company could expose deal files, portfolio financials and personal data spanning many operating businesses. Brain Cipher uses LockBit Black–derived tooling and routinely posts mid-market victims. Until Mutares or a German authority confirms, treat this as an unverified threat-actor claim, NOT confirmation of a breach.
#DDW #DarkWeb #Germany #Mutares #BrainCipher #Ransomware #PrivateEquity #SDAX #DataLeak #ThreatIntelligence #CyberSecurity
Rohto says its breach exposed data on 2,797,545 customers. Stolen call recordings held card numbers and expiry dates for 9,715 people. Newly disclosed scope of a September incident.
⚠️ Analyst Note:
Rohto identifies names, addresses and telephone numbers in affected customer-management data; categories vary by person. The 9,715 figure concerns customers whose call recordings contained card numbers and expiry dates, not 2.8m exposed cards. Do not add the two counts. Rohto reports no known resulting fraud. The new development is quantified impact, not a new intrusion or newly identified cause.
https://t.co/CxknCSdLZ1
#DataBreach
🇺🇸 🚨 GEICO: 30.5M+ AUTO INSURANCE CUSTOMER RECORDS ALLEGEDLY OFFERED FOR SALE
A threat actor on an underground forum claims to be selling more than 30.5 million auto insurance customer records allegedly sourced from GEICO.
According to the listing:
• Claimed volume: 30,572,398 lines
• Asking price: $3,000 (described as negotiable; escrow accepted)
• Field categories claimed: name, address, city/state/ZIP, phone, vehicle year/make/model/body, VIN, gender, income
• Seller also posted state-level row counts across all 50 US states and DC
The claim has not been independently verified, and GEICO has not publicly confirmed any breach. No usable sample was independently reviewed.
⚠️ Analyst Note:
A claimed GEICO-linked dataset at this scale, with VIN and income alongside contact PII, would be high-value for insurance fraud, synthetic identity and targeted phishing if authentic. Low asking price vs volume and lack of a clear sample keep confidence limited — treat as an unverified marketplace claim, NOT confirmation of a GEICO breach.
Source: this is for subscribers only. Subscribe: https://t.co/O5fslMgfuw
#DDW #DarkWeb #GEICO #Insurance #DataLeak #PII #VIN #ThreatIntelligence #CyberSecurity
@austindixson_ Raise the phishing watch / monitoring now; keep the listing unverified until a clean sample and confirmed victim land. Don't wait to warn — don't treat the claim as confirmed either.
🇷🇺 🚨 https://t.co/B4wDIeeP4k — 3 MILLION RECORDS ALLEGEDLY OFFERED FOR SALE
A threat actor on an underground forum claims to be selling a 3 million-record database allegedly taken from Obed[.]ru (ООО «Обед.ру»), a Moscow-based corporate catering and office meal-delivery platform.
The actor claims the breach occurred on July 16, 2026, that the dump is in CSV, and that samples cover suppliers and clients. Advertised fields include names, phones, emails, company names, postal addresses, Russian tax identifiers, banking and transaction details, and order/accounting contact data. No price was stated. The claim is unverified.
⚠️ Analyst Note:
If authentic, supplier/client PII plus tax IDs and banking details would support phishing, BEC, invoice fraud, and payment-diversion scams against companies that work with Obed[.]ru. Samples raise plausibility but do not prove the data came from Obed[.]ru systems. Unverified threat-actor listing, NOT confirmation of a breach. Claimed breach date is July 16, 2026; this is a new Nov 6 listing of that older alleged event.
#DDW #DarkWeb #Russia #Obed #DataLeak #ThreatIntelligence #CyberSecurity
🇯🇵 NTT DOCOMO confirms customer-data leak
* Up to about 300,000 records affected
* Names, addresses, birth dates and phone numbers
Unauthorized access hit My docomo/Online Shop. Exact scope and cause remain under investigation.
⚠️ Analyst Note:
The figure is an approximate upper bound for records, not a verified count of unique people. Independent reporting cites the company disclosure rather than separate forensic confirmation. Do not conflate this with the separate 5G outage or the earlier plala incident.
https://t.co/3M65xKaPVt
#DataBreach #DDW
🇺🇸 🚨 SILENT RANSOM GROUP CLAIMS ATTACK ON US LAW FIRM TUCKER ELLIS
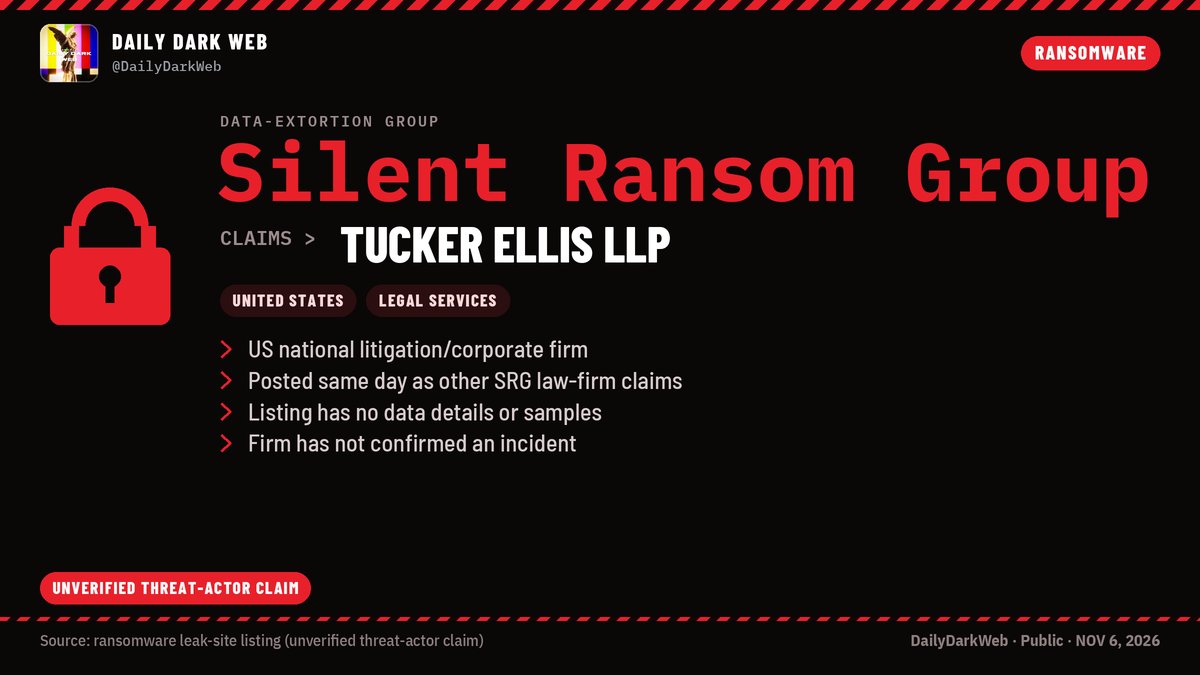
Silent Ransom Group (SRG, also tracked as Luna Moth / Chatty Spider) has listed Tucker Ellis LLP, a US law firm with a national practice across litigation, corporate and regulatory matters, as a new victim on its data-leak site.
The listing, discovered Nov 6, 2026, gives only a short firm bio and does not say what data was allegedly taken. No samples have been verified.
The claim has not been independently verified, and Tucker Ellis has not publicly confirmed an incident.
⚠️ Analyst Note:
SRG continues a concentrated campaign against US law firms. The FBI has warned that the group poses as internal IT support by phone or email, and sometimes in person, to gain remote access and quickly steal files for extortion without encryption. Law firms should verify any unexpected "IT support" contact. Treat this as an UNVERIFIED threat-actor claim, NOT confirmation of a breach.
#DDW #DarkWeb #Ransomware #SilentRansomGroup #LunaMoth #LawFirm #TuckerEllis #Legal #DataBreach #ThreatIntelligence #CyberSecurity
🇺🇸 🚨 SILENT RANSOM GROUP CLAIMS ATTACK ON ELITE US LAW FIRM WACHTELL LIPTON
Silent Ransom Group (SRG, also tracked as Luna Moth / Chatty Spider) has listed Wachtell, Lipton, Rosen & Katz, the New York–based elite M&A and corporate law firm, as a new victim on its data-leak site.
The listing, discovered Nov 6, 2026, gives only a short firm bio and does not say what data was allegedly taken. No samples have been verified.
The claim has not been independently verified, and Wachtell Lipton has not publicly confirmed an incident.
⚠️ Analyst Note:
Wachtell is one of the most prestigious US corporate law firms and holds highly sensitive M&A, board and litigation files for major clients, so a real compromise would create serious third-party and privilege risk. SRG has been listing US law firms in a sustained campaign; the FBI has warned that the group uses callback phishing and fake IT-support calls (and sometimes in-person visits) to steal data for extortion without encryption. Treat this as an UNVERIFIED threat-actor claim, NOT confirmation of a breach.
#DDW #DarkWeb #Ransomware #SilentRansomGroup #LunaMoth #LawFirm #WachtellLipton #Legal #DataBreach #ThreatIntelligence #CyberSecurity
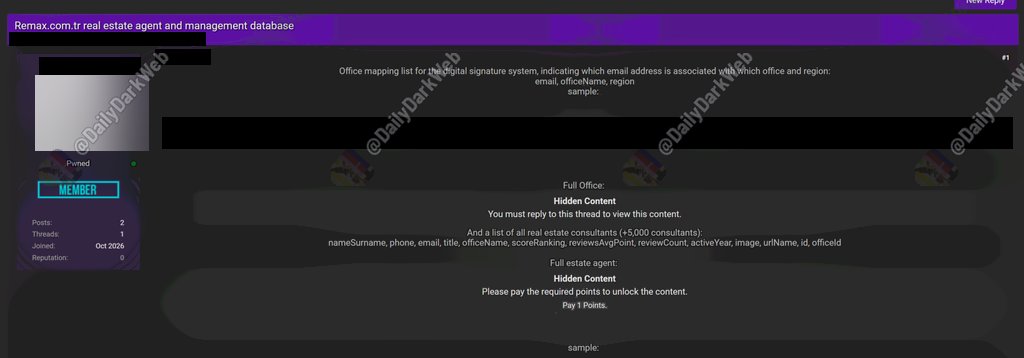
🇹🇷 🚨 TURKEY: THREAT ACTOR CLAIMS RE/MAX TURKEY AGENT AND OFFICE DATABASE
A threat actor on an underground forum claims to be offering a database tied to RE/MAX Turkey, the real estate franchise operating in Turkey and Northern Cyprus.
The listing allegedly includes:
* A list of 5,000+ real estate consultants with names, phone numbers, email addresses and titles
* Office names, rankings, review scores and years active
* An office mapping list from a digital signature system (email, office name, region)
The claim has not been independently verified.
⚠️ Analyst Note:
If genuine, a full directory of agents with direct phone numbers is ideal material for targeted phishing, fake listing scams and impersonation of RE/MAX offices toward buyers and sellers. The digital signature mapping suggests access to internal tooling. Agents should be wary of unexpected requests for credentials or payments. Unverified threat-actor claim, NOT confirmation of a breach.
Source: this is for subscribers only. Subscribe: https://t.co/O5fslMgfuw
#DDW #DarkWeb #Turkey #REMAX #RealEstate #DataLeak #Phishing #ThreatIntelligence
@ondrejsimaichl1 Thanks — that's an important addition from the official notice. ID document numbers and any bank fields raise the phishing risk a lot; treat unexpected Docomo SMS that already knows your details as suspicious and don't tap the links.
@EFadlon17449 Yes — leaked OAuth/session tokens often enable silent account takeover without password spray. Treat them like credentials: revoke/rotate immediately, force re-auth on affected IdPs, and watch social-login sessions for anomalies.
🇰🇷 🚨 2 MILLION KOREAN CONSUMER RECORDS WITH KAKAO/NAVER TOKEN FIELDS ALLEGEDLY FOR SALE
A threat actor on an underground forum claims to be selling a 2 million-record South Korean consumer database. A sample table was posted. No victim organization, breach date, file list, or price was given. The claim is unverified.
What the sample allegedly contains:
• Names and nicknames
• Email addresses and phone numbers
• kakao_token and naver_token fields
• Account-type labels
⚠️ Analyst Note:
If authentic, contact data plus Kakao/Naver-related token fields could support phishing, smishing, account enumeration, and account-takeover attempts against Korean consumers — especially if any token values are live session or auth material (not confirmed). No company or platform is named, which complicates victim notification. Unverified threat-actor listing, NOT confirmation of a breach at any named service.
#DDW #DarkWeb #SouthKorea #Kakao #Naver #DataLeak #ThreatIntelligence
⚠️ Barracuda ESG: researchers demonstrate a pre-auth root execution chain when the admin interface is reachable.
CVE-2026-116606 + CVE-2026-111560: restrict admin access and verify vendor patches. No in-the-wild exploitation confirmed.
⚠️ Analyst Note:
Barracuda corrected its authentication description on November 5 (Admin UI access required; no login needed). watchTowr reproduced the chain and published a command-execution proof of concept. Firmware-version guidance differs between sources; verify applicable patch IDs against current vendor instructions.
Source:
https://t.co/sfBkr8RCGA
#CyberSecurity
🇫🇷 🚨 AKIRA CLAIMS FRENCH FURNITURE HOUSE LIGNE ROSET
The Akira ransomware group has listed Ligne Roset, the French design furniture manufacturer known for collaborating with major designers since the 1970s, on its leak site.
The group claims it will publish about 150 GB of corporate data, allegedly including:
* Employee personal information (passports and driver's licences)
* Contracts, agreements and NDAs
* Financial and other confidential files
No samples have been verified. Ligne Roset has not publicly confirmed an incident.
The claim has not been independently verified.
⚠️ Analyst Note:
Akira remains one of the most active ransomware operations and often reaches firms through unpatched VPN appliances and stolen credentials. A manufacturer of this size holds employee identity documents, supplier contracts and financial records, so a real leak would create HR, legal and third-party risk. Until the company or a French authority confirms, treat this as an unverified threat-actor claim, NOT confirmation of a breach.
#DDW #DarkWeb #France #LigneRoset #Akira #Ransomware #Manufacturing #Furniture #DataBreach #ThreatIntelligence #CyberSecurity
U.S. prosecutors unsealed charges Nov 5 alleging AI impersonation of CEOs and lawyers helped steal $129m. E-signature NDAs and fake acquisition calls targeted finance staff. Verify payment requests through a separate, trusted channel.
⚠️ Analyst Note:
The indictment alleges the conduct and losses; charges are not convictions. Arrests occurred June–September 2026, not at the time of this announcement. Independent reporting confirms the charges, not the underlying losses.
https://t.co/nCcPnjglxy
#Cybercrime
@austindixson_ Raise awareness now if clients use https://t.co/5Hxn03aaxl (phishing watch + account monitoring), but keep the claim unverified until a clean sample and confirmed victim org land. Don’t wait for proof to warn; don’t treat the listing as confirmed either.
@ondrejsimaichl1 Solid checklist — bump Active Storage to the fixed releases for your line (8.1.4.1 / 8.0.5.2), and if you use disk storage rotate secret_key_base after upgrading. ImageMagick on a public upload path is the risky combo.
🚨 RUBY ON RAILS: CRITICAL ACTIVE STORAGE FLAW (CVSS 9.8) ALLOWS UNAUTHENTICATED FILE WRITE VIA IMAGE UPLOADS
Rails has disclosed a critical flaw in Active Storage. Apps that process uploads with ImageMagick may let an unauthenticated attacker write arbitrary files on the server with one crafted upload.
• Advisory: GHSA-f3w6-w445-fwh9 (no CVE yet), CVSS 9.8
• Attaching the file is enough; no variant, preview or analyze call is needed
• With the Disk service, attackers may also read any file the app can read, including secret_key_base and credentials
• Fixed in activestorage 8.1.4.1 and 8.0.5.2
⚠️ Analyst Note:
Rails does not say whether the flaw has been exploited. Upgrade now. If you store attachments with the Disk service, rotate secret_key_base, the master key and every credential the app can read.
https://t.co/hUQbvu3txx
#DDW #DarkWeb #RubyOnRails #AppSec #PatchNow