Let’s set the record straight: @lcfr_hax was the first to discover php2shell and develop a working exploit. See his August 5 tweet: https://t.co/I88EQFrUHa
His work convinced the PHP Foundation to invest in fixing this entire bug class. He then worked around the clock to review, test, and retest the patches.
If you’re into AI and CTFs then you might think this CTF that Netwrix is doing is cool. You can win a free pass to Blackhat! :)
https://t.co/Kj8etdF42J
Two critical vulnerabilities have been identified in PHP, a widely used programming language that powers websites and web applications. These vulnerabilities (CVE-2026-109618 and CVE-2026-109619) could allow malicious cyber actors to remotely execute code in PHP core, potentially compromising sensitive data and networks.
The FBI urges organizations to take the following steps now:
➡️ If an immediate update is not feasible it is recommended that organizations take the system offline until it can be fully mitigated.
➡️ Immediately update affected PHP installations following the guidance on https://t.co/rDrPSxB3zX. Inventory where PHP runs in your environment, prioritizing internet-facing systems and vendor products that bundle PHP.
➡️ Monitor web servers for suspicious activity, including PHP processes unexpectedly launching command shells or downloading files. Ensure appropriate process-monitoring capabilities are in place to help identify potential exploitation.
➡️ If you find signs of compromise, isolate affected systems, preserve your web server and PHP logs, and report it to your local FBI field office or https://t.co/iqgVZIbCru. Those reports help us identify the actors involved and warn other organizations before they become victims.
For the latest information, follow PHP’s announcement on https://t.co/rDrPSxB3zX, CERT-EU Security Advisory 2026-018, and CISA’s Known Exploited Vulnerabilities catalog.
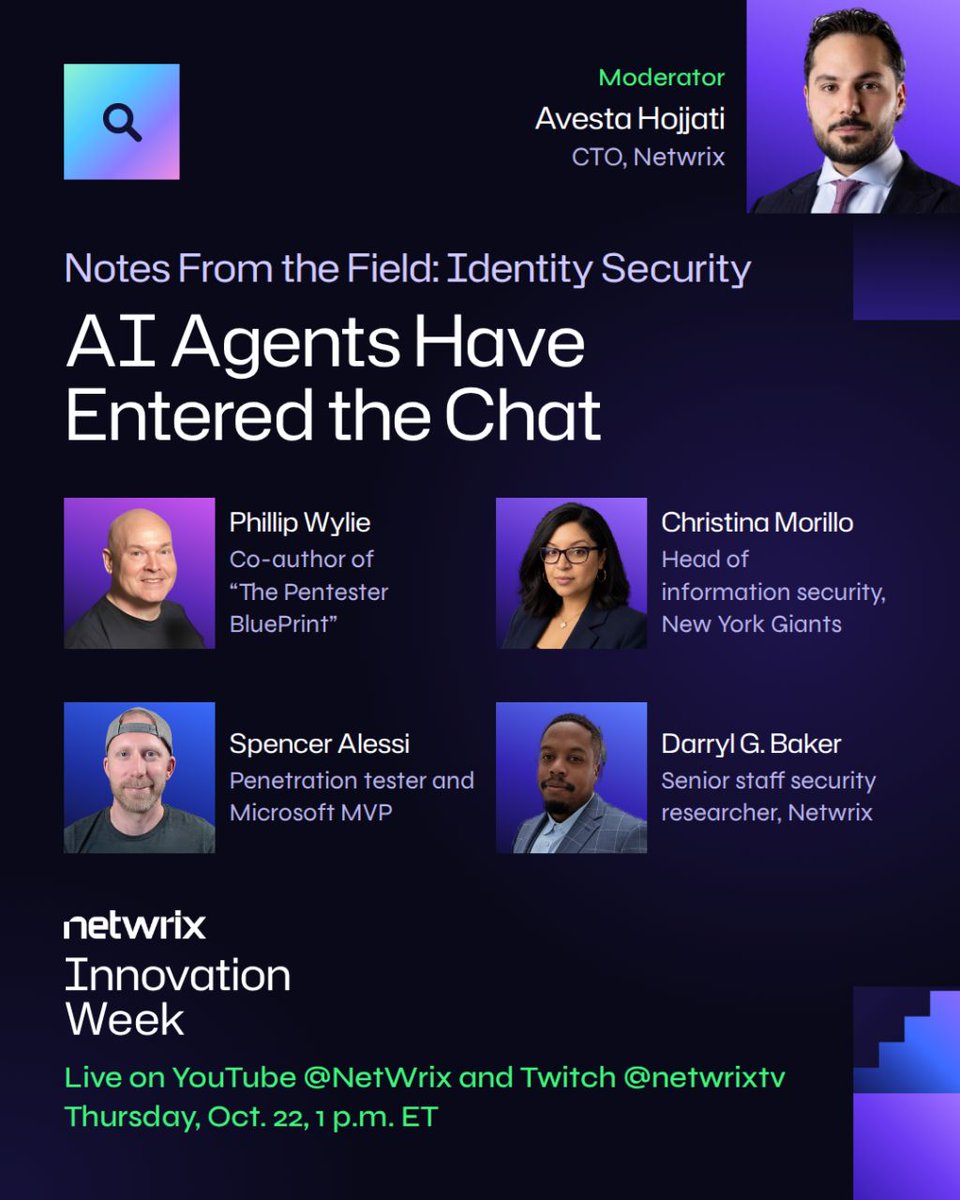
I got invited to speak alongside these other awesome people for a @Netwrix Innovation Week panel discussion on Identity Security in the age of AI.
Long live Active Directory! 💪😄
Thursday, Oct. 22, at 1 p.m. ET
Watch live here 👇
YouTube: https://t.co/bV3Kw29Aov
Twitch: https://t.co/YyUYChl1rb
🚨 ConnectWise has suspended Cloud Backup and disabled 7 app identities after attackers compromised Microsoft 365 tenants.
Backups and restores are unavailable. Previously issued access tokens may remain valid.
Read: https://t.co/bMnsZpqZNw