Software dev for a long time.
Now focus on security of code at @AikidoSecurity.
Sceptical about where programming is going, so keep OnlyFans as an option.
I expect supply-chain attacks via downloaded skills to be a game changer
Hundreds of agents (some with root access) will be controlled by an md file written by some script kiddie
That’s an absurdly powerful attack surface
Друзяшкі-програмісти, якщо ви ВСЕ ЩЕ думаєте «може мобілізуватися», то нам дуже потрібні люди.
«Ми» — це ті, хто розробляє, зокрема, «Дельту» і всю екосистему навколо неї.
Посилання на вакансії нижче.
(Це Київ, мобілізація на контракт; а з переводами, ну, як завжди...)
@zverok «I am thinking about publishing it as a separate post/document» - do it!
Since i discovered file based expect tests in ocaml, i can't stop using them
https://t.co/XUFzMzhfVV:
let () =
print_endline "Hello, world!"
test.expected:
Hello, world!
+ autopromotion is magic
The victim list is growing fast. Multiple companies now have compromised packages under their npm scopes from this Shai-Hulud attack.
@CharlieEriksen's tracking each one as it's confirmed 👇
Let's summarize supply chain attacks: "You can't execute random files you found on the internet."
Surprisingly, that's the same thing I was explaining to my older relatives 20 years ago.
@KsyundelMeyta Тобто є задачі, які може вирішити десятирічна дитина, а ви не можете. І ви робите це частиною своєї ідентичності? 🥲 Тертуліан на мінімалках
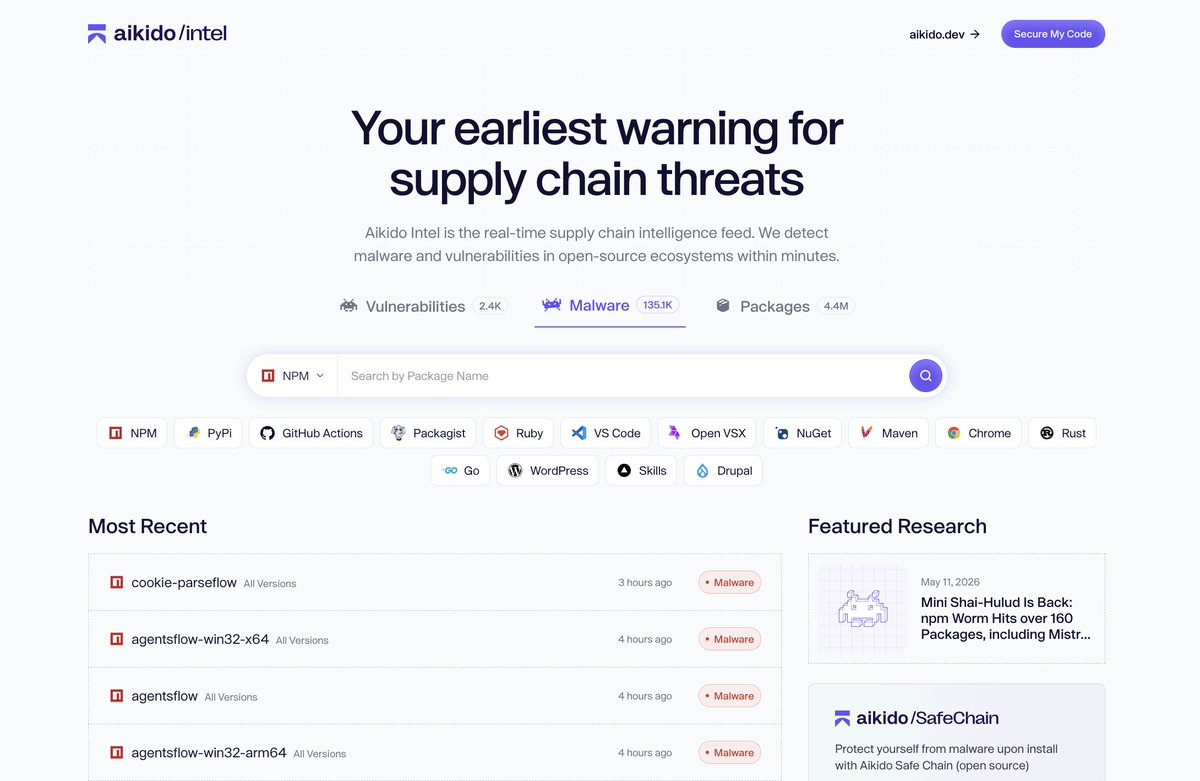
Aikido Intel is your earliest warning for supply chain threats.
Our engine detects malware and vulnerabilities in open-source ecosystems within minutes.
Built by our team of security researchers & AI engineers.
Bookmark it: https://t.co/utLseYtAra
Working in cybersecurity feels like a dream job from The Catcher in the Rye.
«What I have to do, I have to catch everybody if they start to go over the cliff - I mean if they're running and they don't look where they're going I have to come out from somewhere and catch them»
A significant part of AI’s coding speed comes from lowering quality standards. Writing bad code was always faster — we just didn’t consider it the right trade-off before.
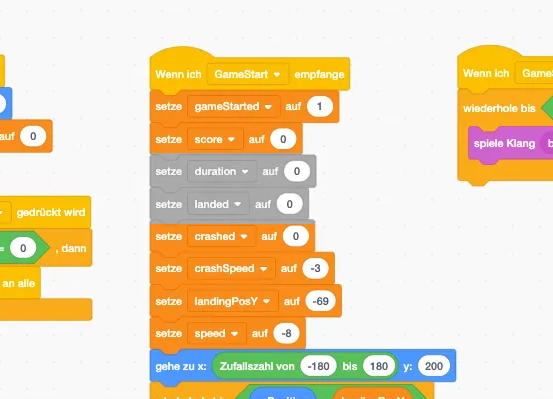
Scratch misses critical feature - the ability to comment out parts of code.
Running code with some parts commented out is one of my favourite debugging techniques.